
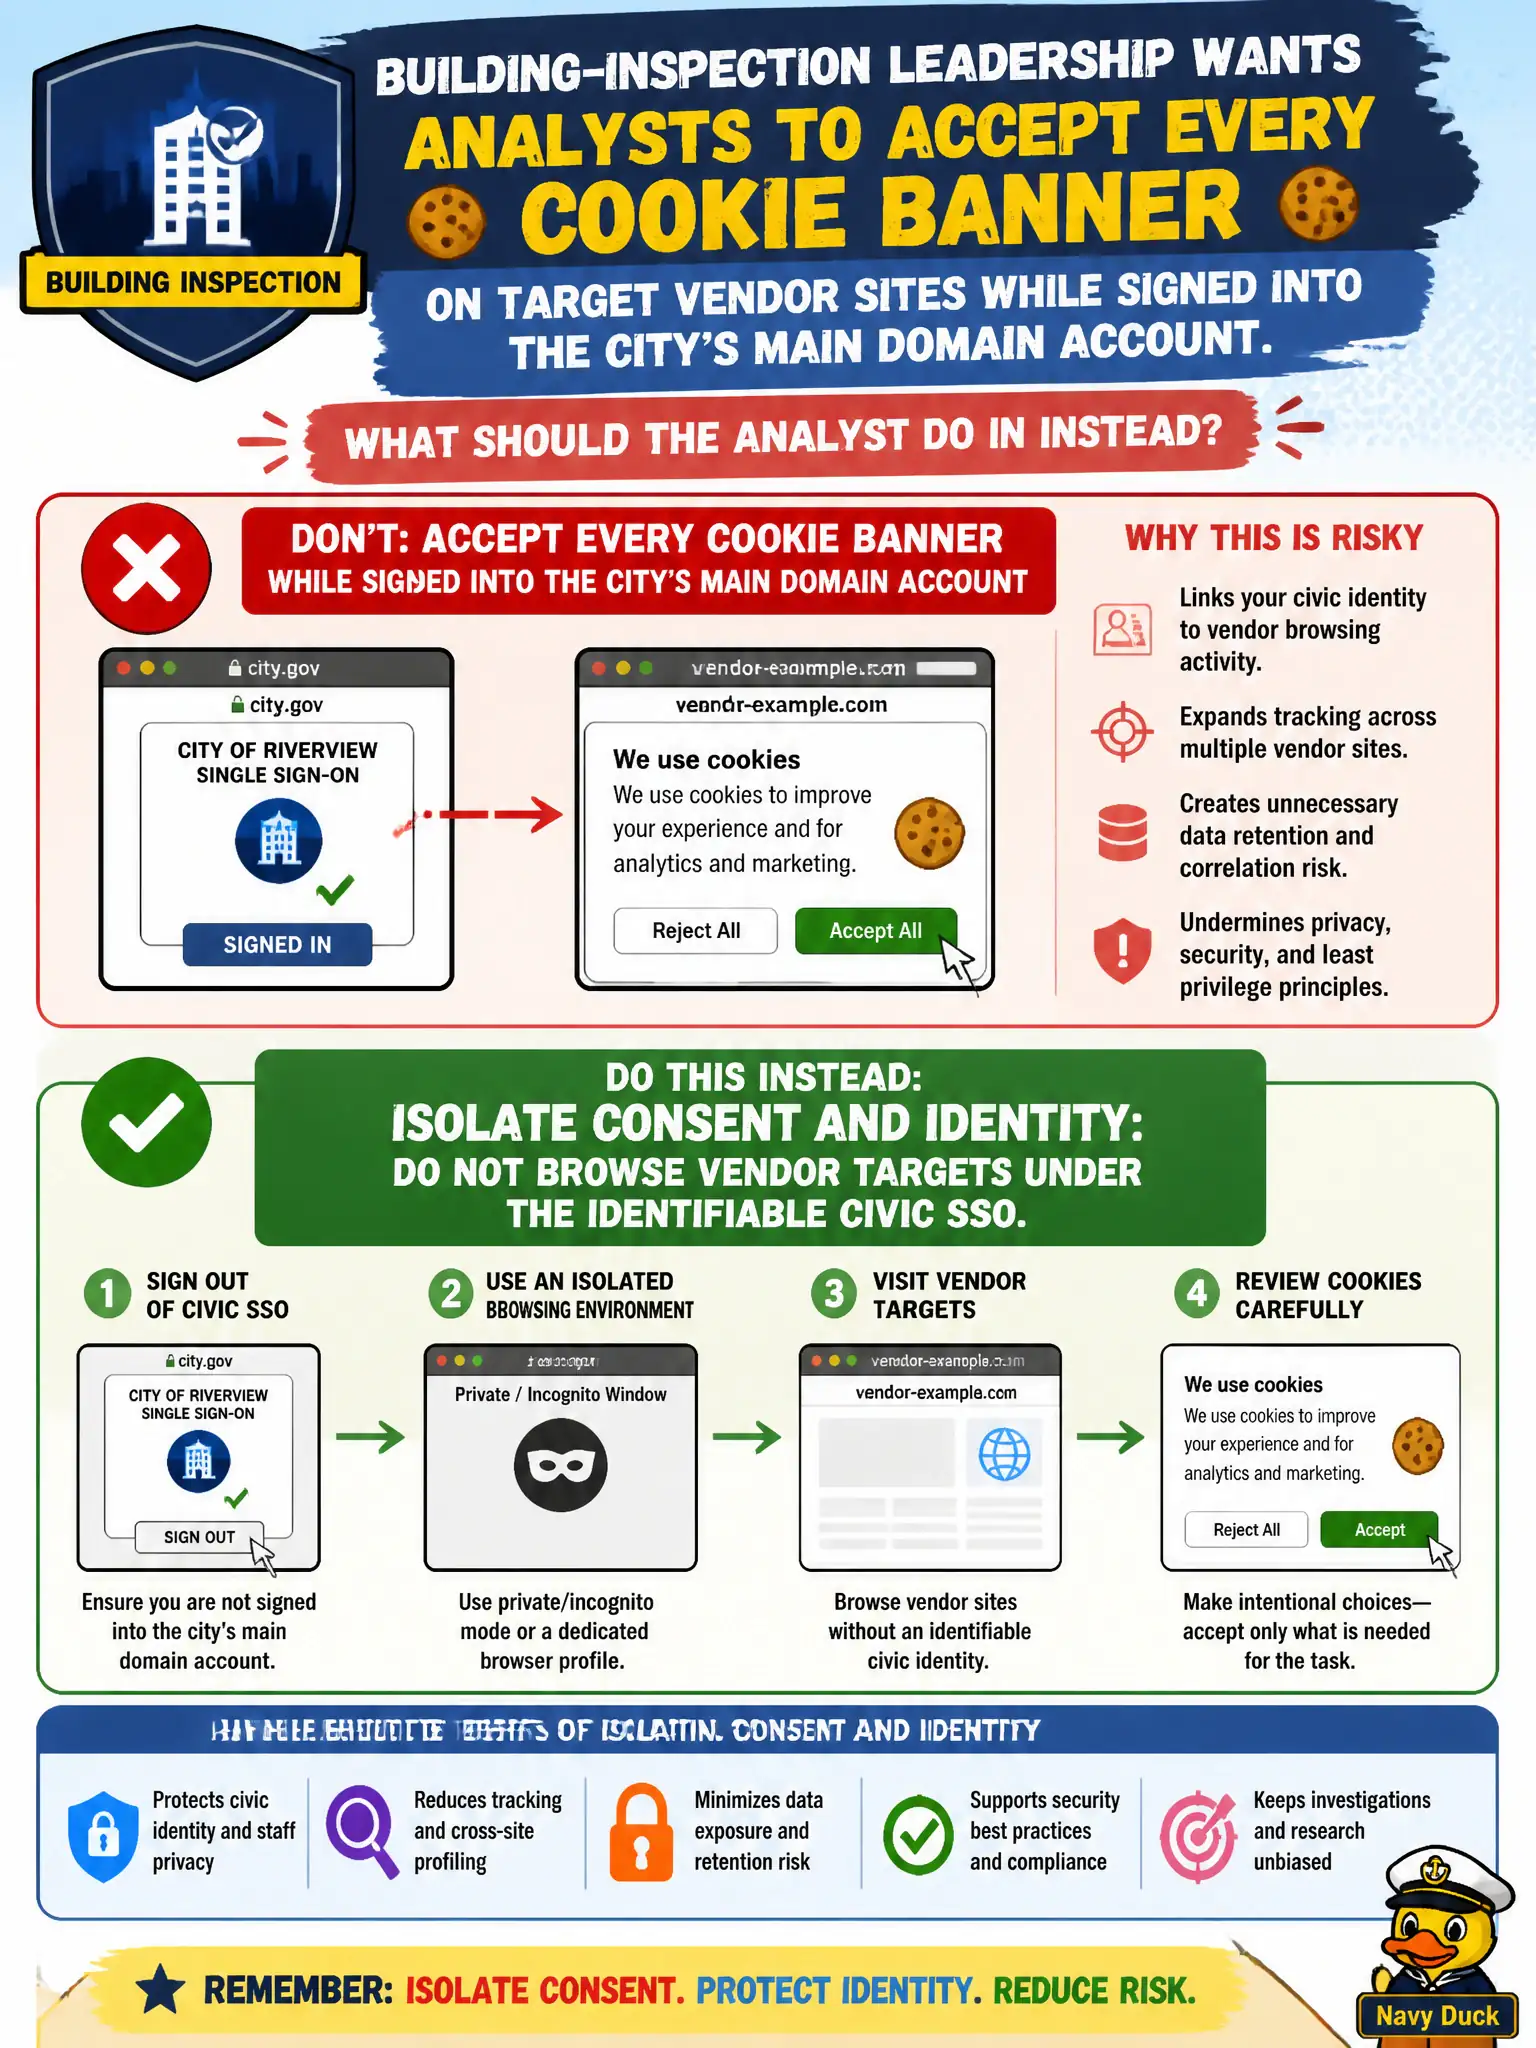
Building-inspection leadership wants analysts to accept every cookie banner on target vendor sites while signed into the city's main domain account. What should the analyst do instead?
Select an answer to reveal the explanation.
Short Explanation
Accepting every cookie while wearing the city's SSO badge is like touring a warehouse in a labeled city jacket and then filling out their guestbook. The vendor learns who is looking, and the tracking profile gets messy. Research identity and cookie consent belong in an isolated profile, not the main civic login.
Full Explanation
Analysts should isolate consent and identity: do not browse vendor targets under the identifiable civic SSO while accepting every cookie banner. Building-inspection leadership that wants staff to accept all cookies on vendor sites while signed into the city's main domain account links municipal identity to third-party tracking and blurs OPSEC. Clicking Accept All so vendor analytics can prove the city visited is the opposite of researcher control. Using the mayor's public mailbox login because it looks more official worsens identifiable exposure. Disabling the lab and collecting only from the production permitting workstation mixes operational credentials with research traffic. Exam caveat: some procurement visits may be intentionally attributable; those should be planned as official outreach, not casual OSINT under SSO. Operational check: open vendor research in an isolated research profile or lab browser without civic SSO cookies, and record whether any consent banners were accepted in that isolated context. Keep the civic purpose, method limits, and exhibit labels aligned so reviewers can see what was public-source work versus other authorities. Document residual uncertainty explicitly rather than implying completeness.