
Elections staff look up a campaign email in public breach-index tools and get no hits. What does that result mean?
Select an answer to reveal the explanation.
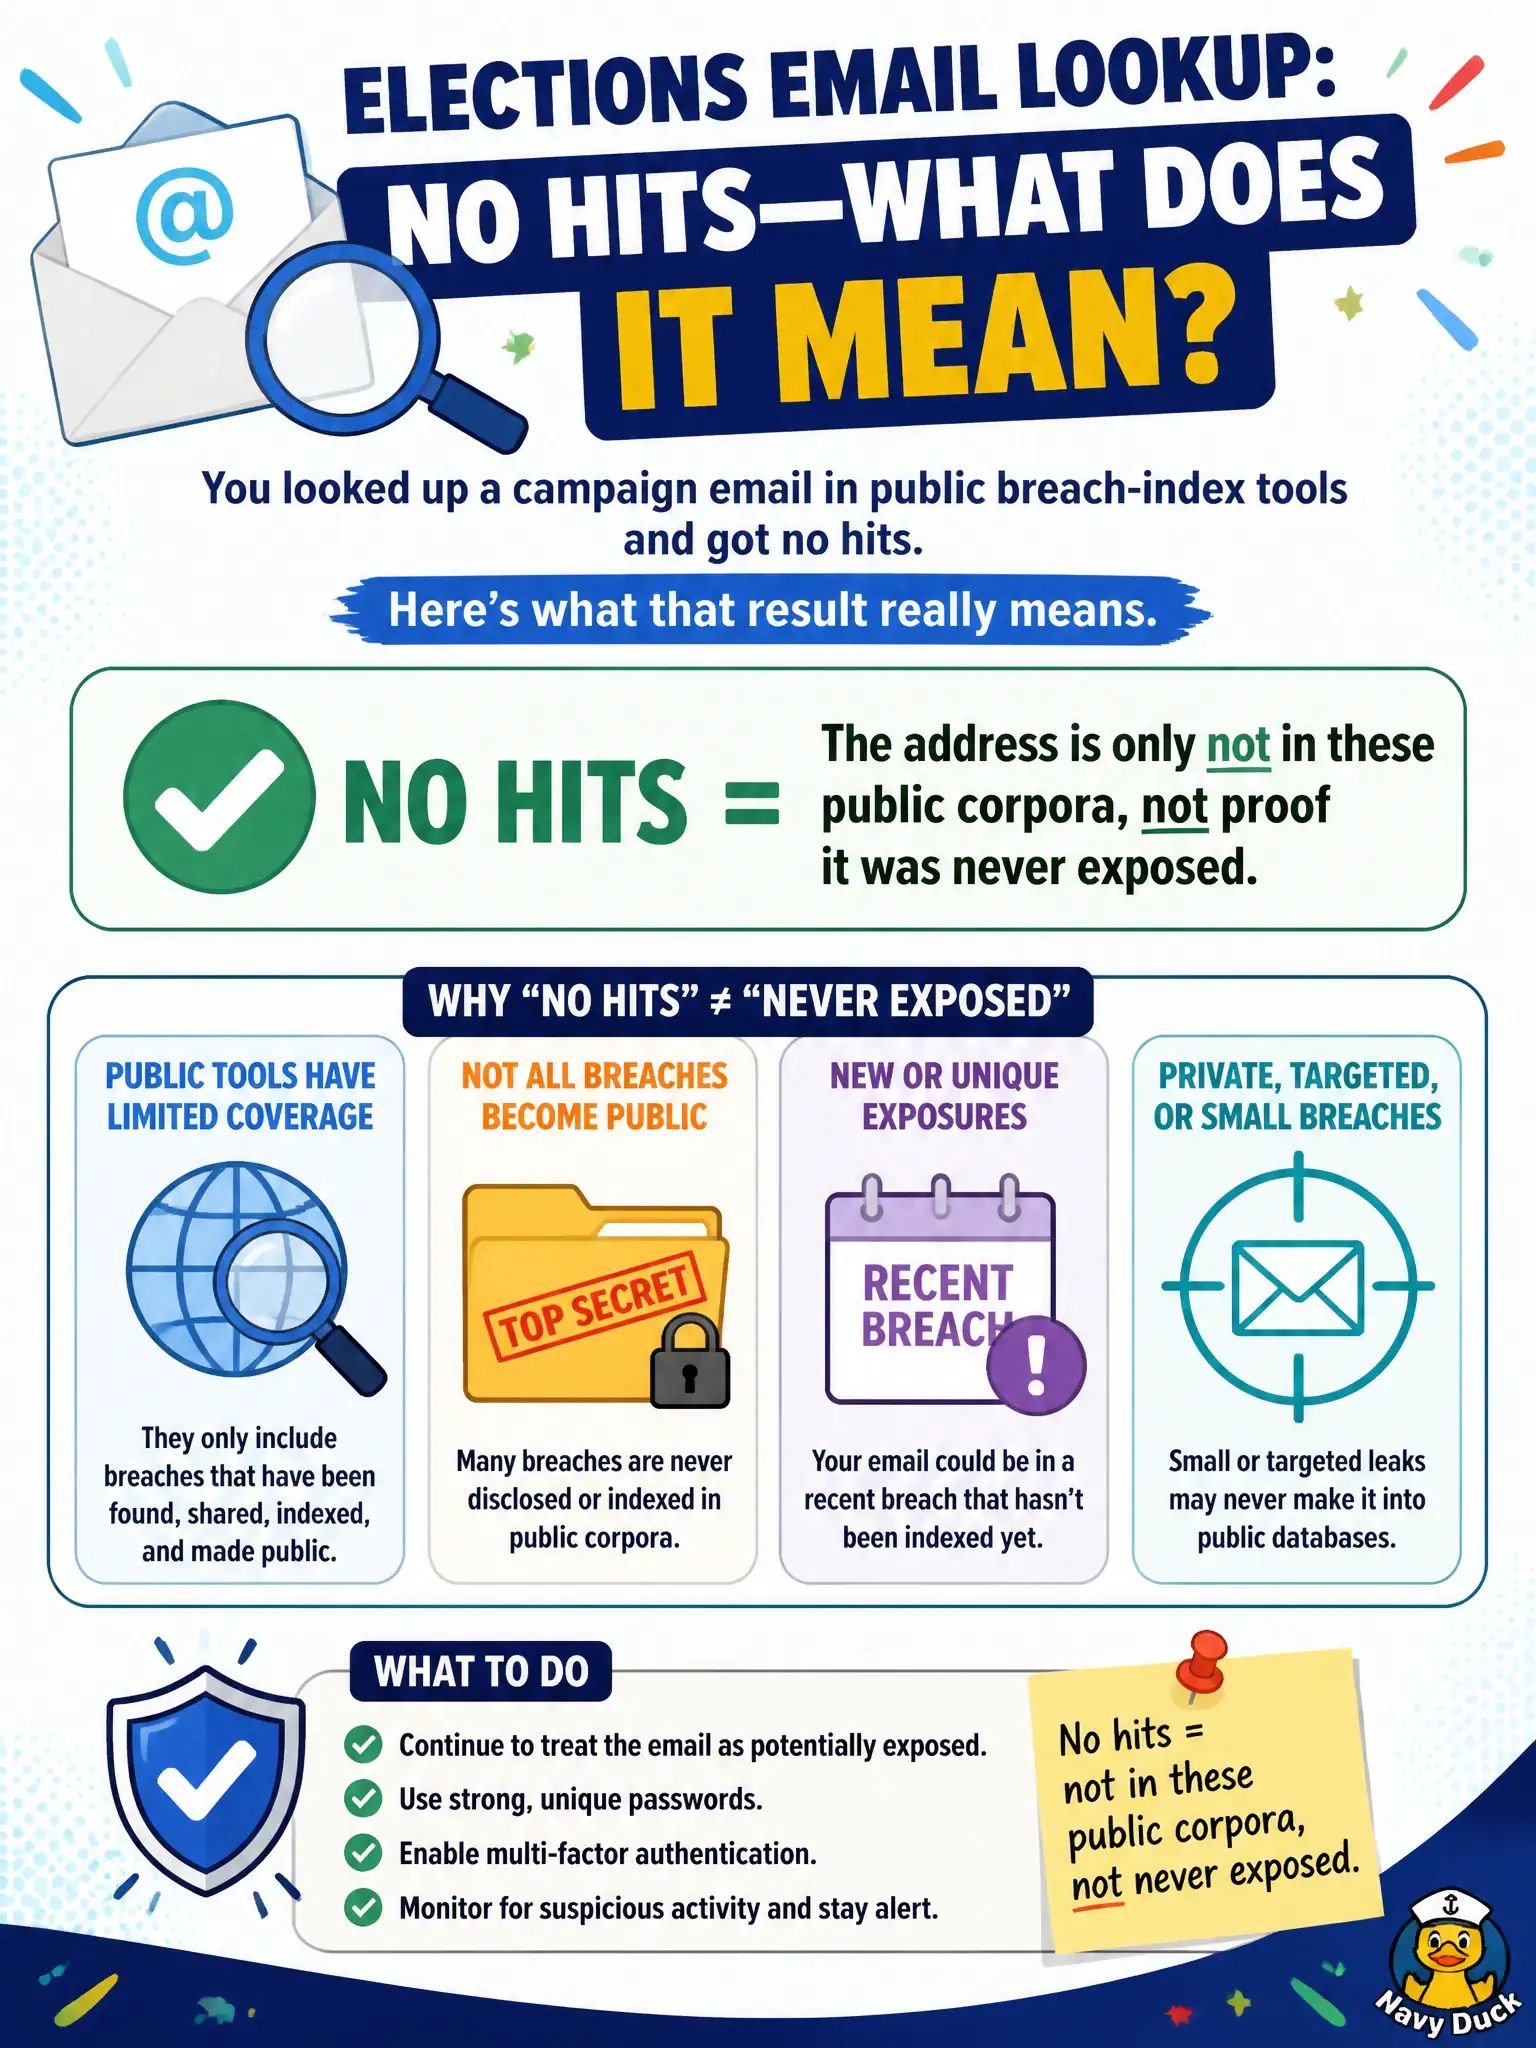
Short Explanation
A clean lookup is like a library that does not have that book—not a certificate that the book was never printed. Say what corpora were checked. Do not bless the campaign's OPSEC from a negative result.
Full Explanation
When elections staff look up a campaign email in public breach-index tools and get no hits, that result means only that the address is not in these public corpora—not proof it was never exposed elsewhere or later. Negative results are corpus-bound and time-bound and must be briefed with those limits visible. Declaring that the campaign has proven excellent security and needs no further OPSEC advice overreads a clean lookup into a security certification the tools cannot issue. Searching non-public databases until a hit appears leaves OSINT for restricted or unlawful collection that elections staff should not request under an OSINT label. Treating absence of a hit as authorization for the campaign to reuse one password everywhere converts a null result into dangerous advice that can increase real risk. Exam caveat: PORP requires analysts to report negative breach lookups as limited non-findings, not as clean bills of health for campaigns. Operational check: list which indexes and date ranges were queried, state “no hit in checked corpora,” recommend ordinary OPSEC hygiene without claiming proof of non-exposure, refuse to pivot into non-public databases for fishing, and document the limitation in the elections briefing note.