
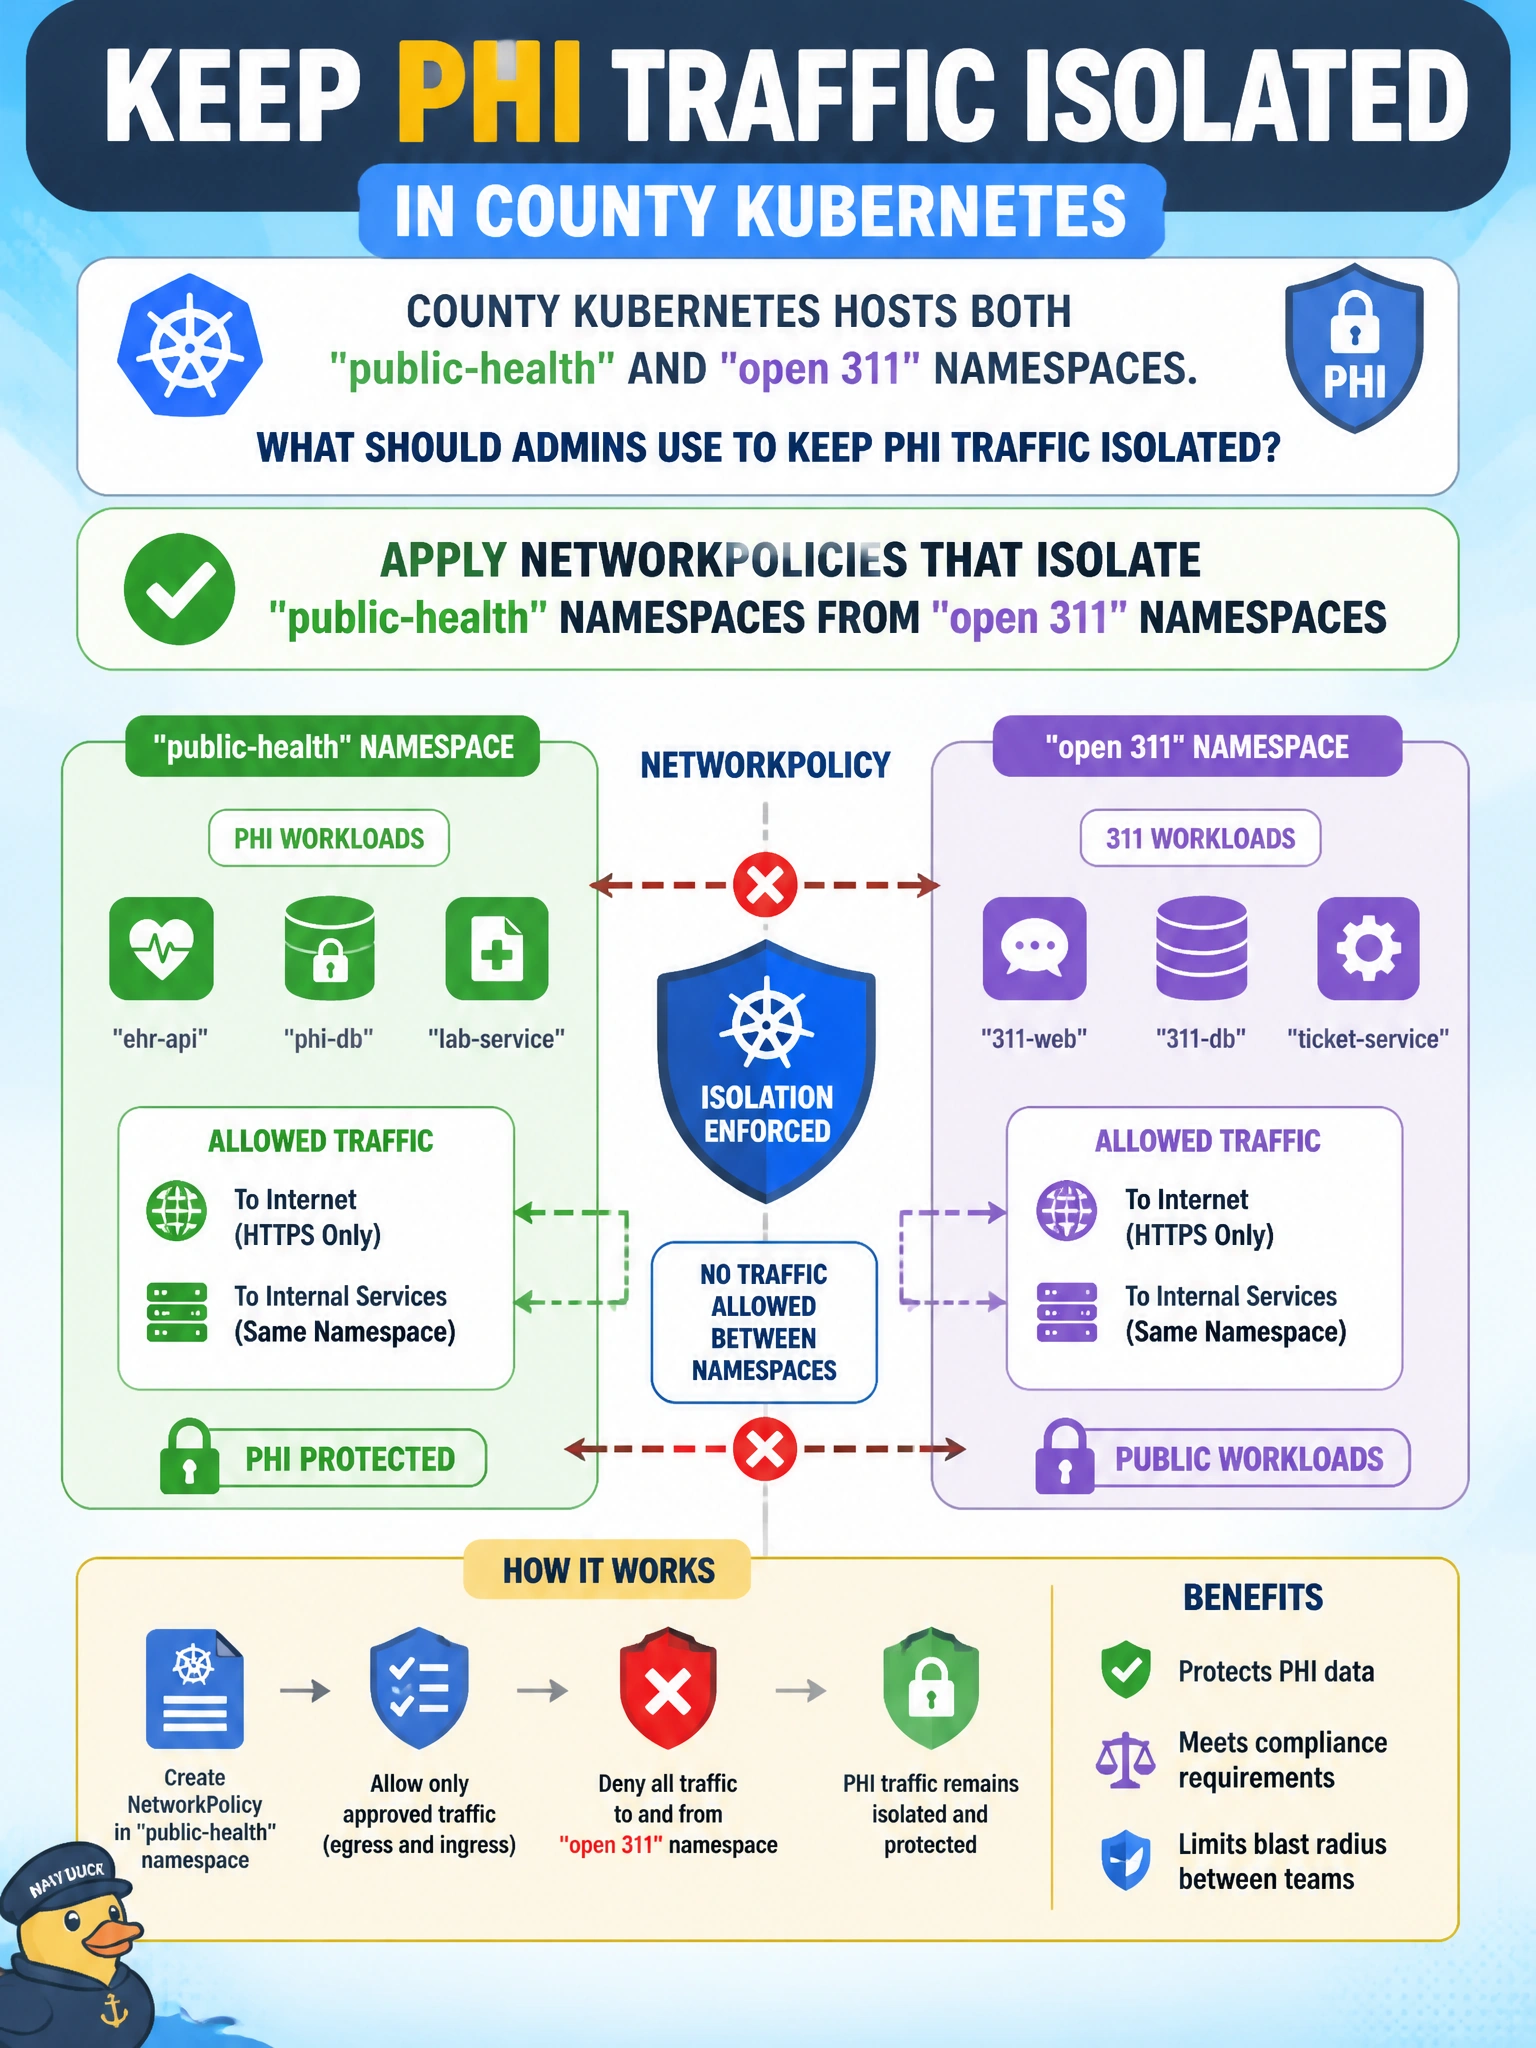
County Kubernetes hosts both public-health and open 311 namespaces. What should admins use to keep PHI traffic isolated?
Select an answer to reveal the explanation.
Short Explanation
NetworkPolicies are the locked doors between the clinic wing and the lobby—PHI stays put while 311 stays public. Flat networks, internet-facing health Services, and cluster-admin for 311 punch holes where civic policy needs walls.
Full Explanation
NetworkPolicies isolate traffic between namespaces, which is what County Kubernetes needs when public-health workloads that handle PHI share a cluster with open 311 namespaces. Default Kubernetes networking is permissive across pods; without policies, any 311 pod can reach health Services on pod IPs or ClusterIPs. Applying deny-by-default NetworkPolicies on the public-health namespace, then allowing only explicitly approved sources (clinician front-ends, approved health Services), keeps PHI paths off the open civic lobby while 311 continues to serve the public.
A flat cluster network with no policies leaves PHI reachable from every namespace—convenient for debugging, disastrous for compliance. Publishing public-health Services on the open internet for partner access expands the attack surface far beyond what partners need and bypasses civic perimeter controls; partners should meet a controlled ingress on the health network, not a world-readable endpoint. Granting 311 pods cluster-admin so they can reach any namespace freely conflates identity privilege with network reachability and gives a low-trust public workload the keys to the entire API and every secret.
Exam caveat: NetworkPolicies require a CNI that enforces them (Calico, Cilium, etc.). Installing YAML without an enforcing plugin does nothing. Policies are namespace-scoped; labels on pods and selectors must match exactly, and DNS/egress to system namespaces often needs explicit allow rules or health checks break.
Operational check: from a 311 test pod, confirm TCP to public-health Service ports is denied; from an approved health client, confirm the same path succeeds. Review audit logs for unexpected cross-namespace connections and ensure PHI Services are not LoadBalancer/NodePort on the public plane.