
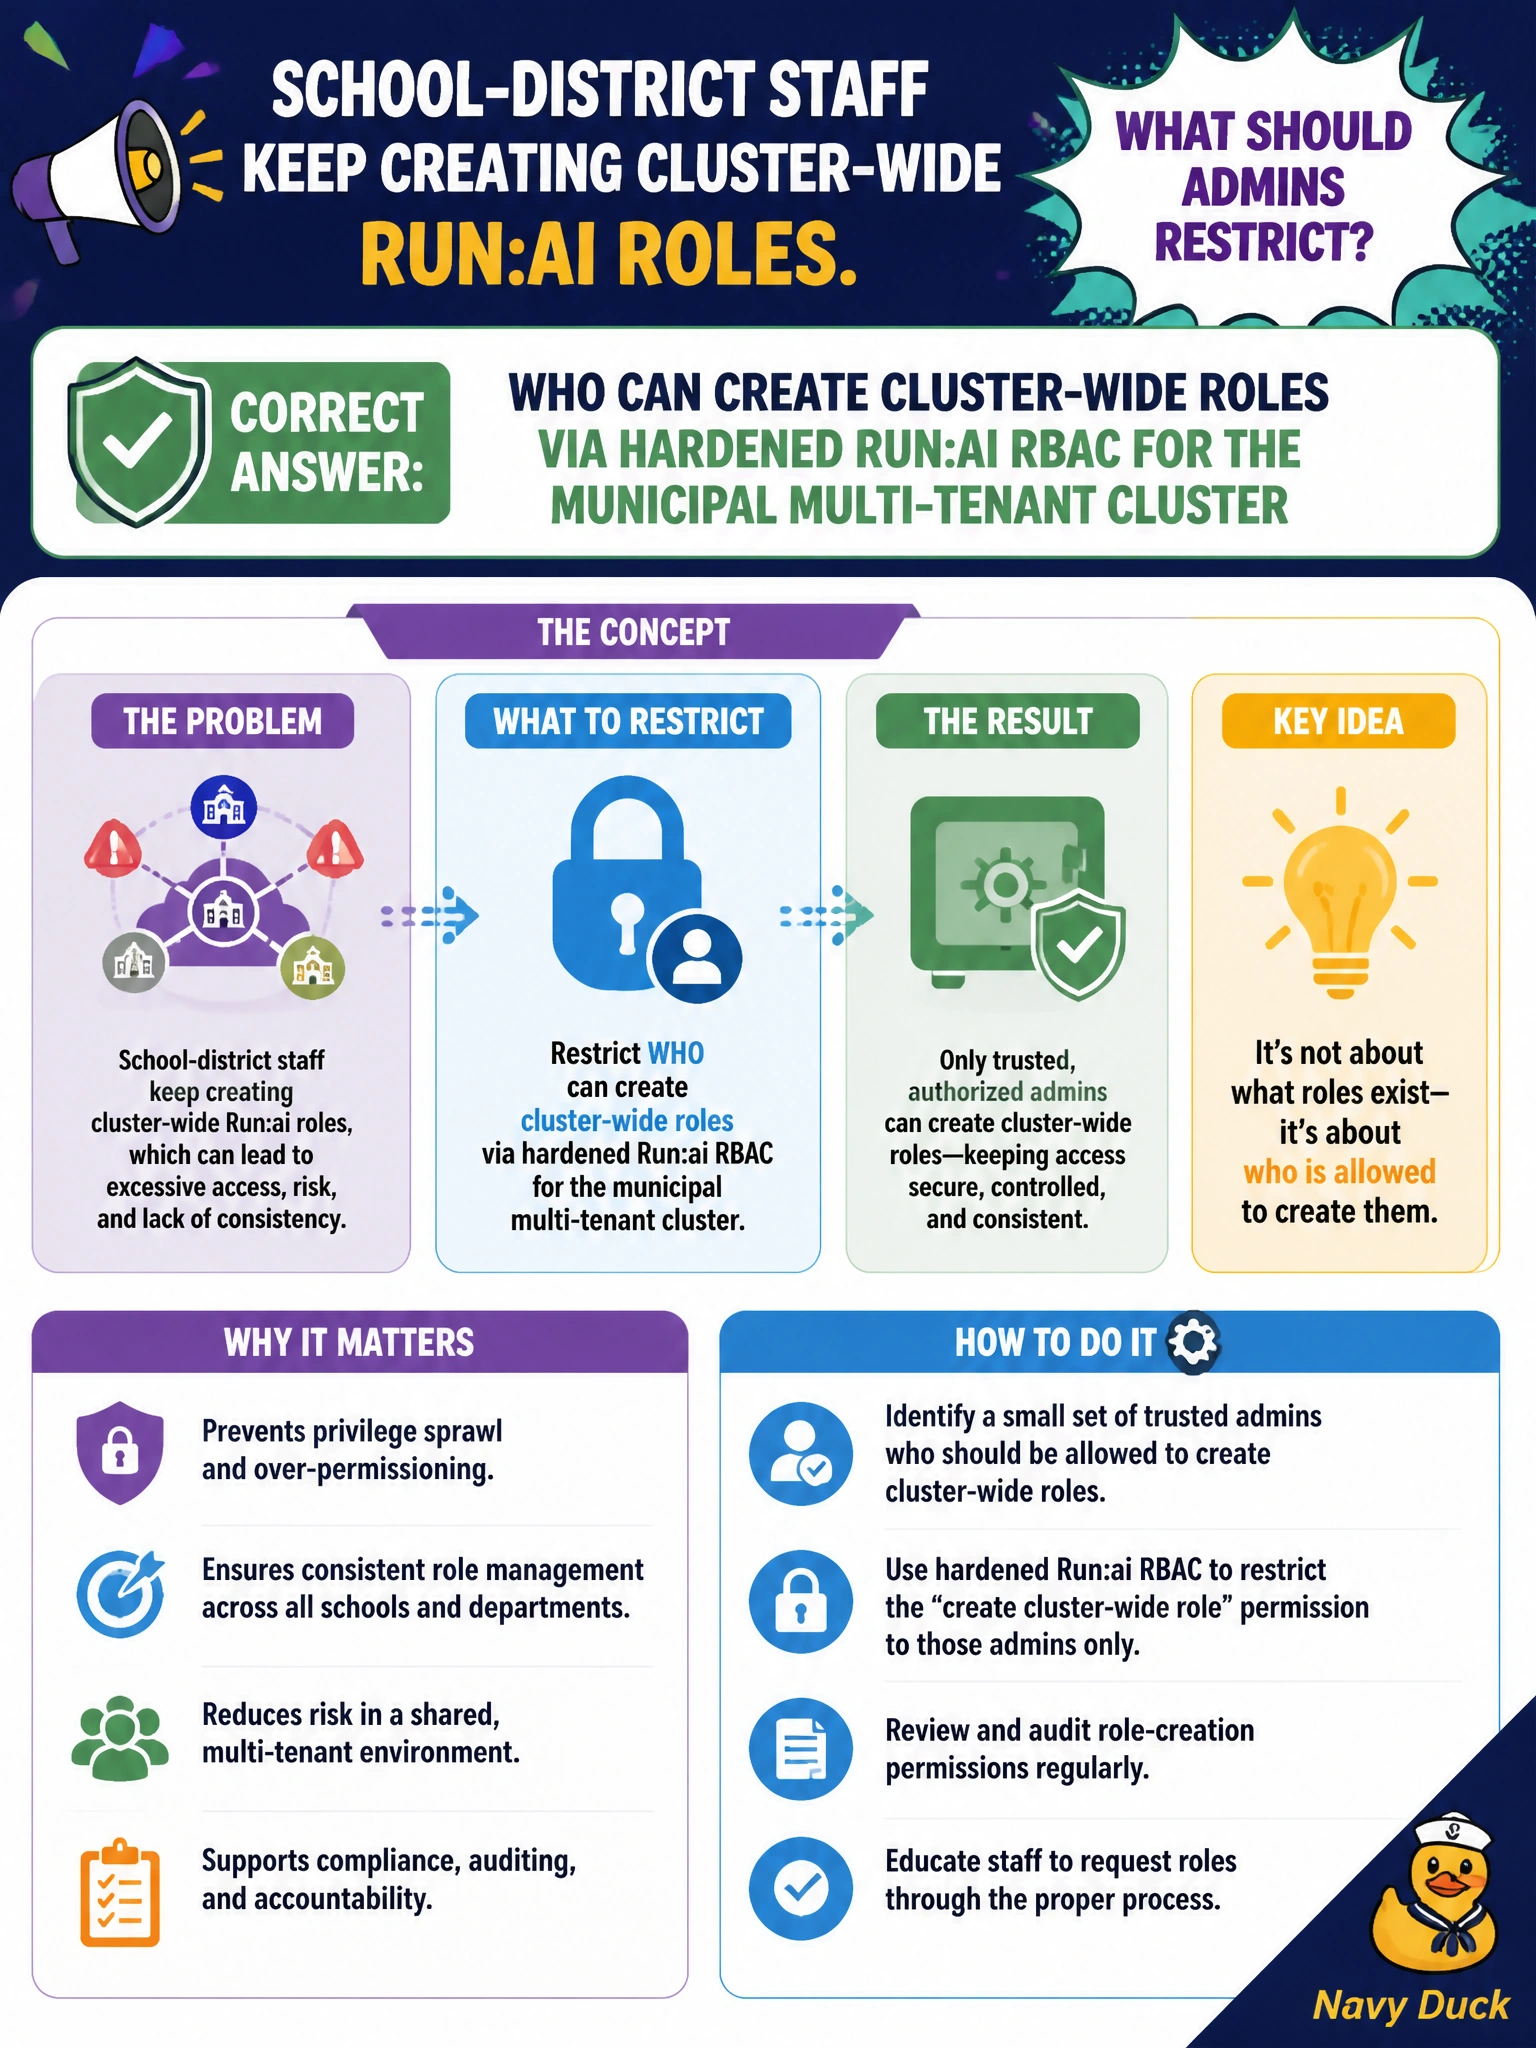
School-district staff keep creating cluster-wide Run:ai roles. What should admins restrict?
Select an answer to reveal the explanation.
Short Explanation
Lock down who can mint cluster-wide roles—RBAC is the key cabinet for a school-district Run:ai. Default cluster-admin for everyone or killing audit logs invites sprawl. Nightly cluster deletes are not access control.
Full Explanation
School-district staff who freely create cluster-wide Run:ai roles undermine multi-tenant security. Admins must restrict who can create cluster-wide roles through hardened Run:ai RBAC so only platform owners mint powerful bindings; teachers and researchers stay within project-scoped permissions. Controlling role creation is the least-privilege administration the stem targets. Doing nothing and giving every teacher cluster-admin by default maximizes privilege sprawl. Restricting logging so role changes cannot be audited hides abuse rather than preventing it. Deleting the cluster nightly to remove student projects is destructive non-management that wipes legitimate work and is not RBAC. Exam caveat: review existing cluster roles during hardening—new restrictions do not remove stale cluster-admin bindings already granted to staff. Operational check: attempt role creation as a normal teacher account and confirm denial; create a role only as an approved admin; verify audit logs record the change; inventory and remove unnecessary cluster-wide roles. Prefer project-admin and namespace-scoped roles for teachers; reserve cluster-role creation for a tiny platform group backed by change control. Periodically diff Run:ai/Kubernetes clusterrolebindings against the approved baseline so school-district multi-tenant clusters do not accumulate shadow superusers.