
A municipal AI factory retires a tenant from shared InfiniBand. What should operators do?
Select an answer to reveal the explanation.
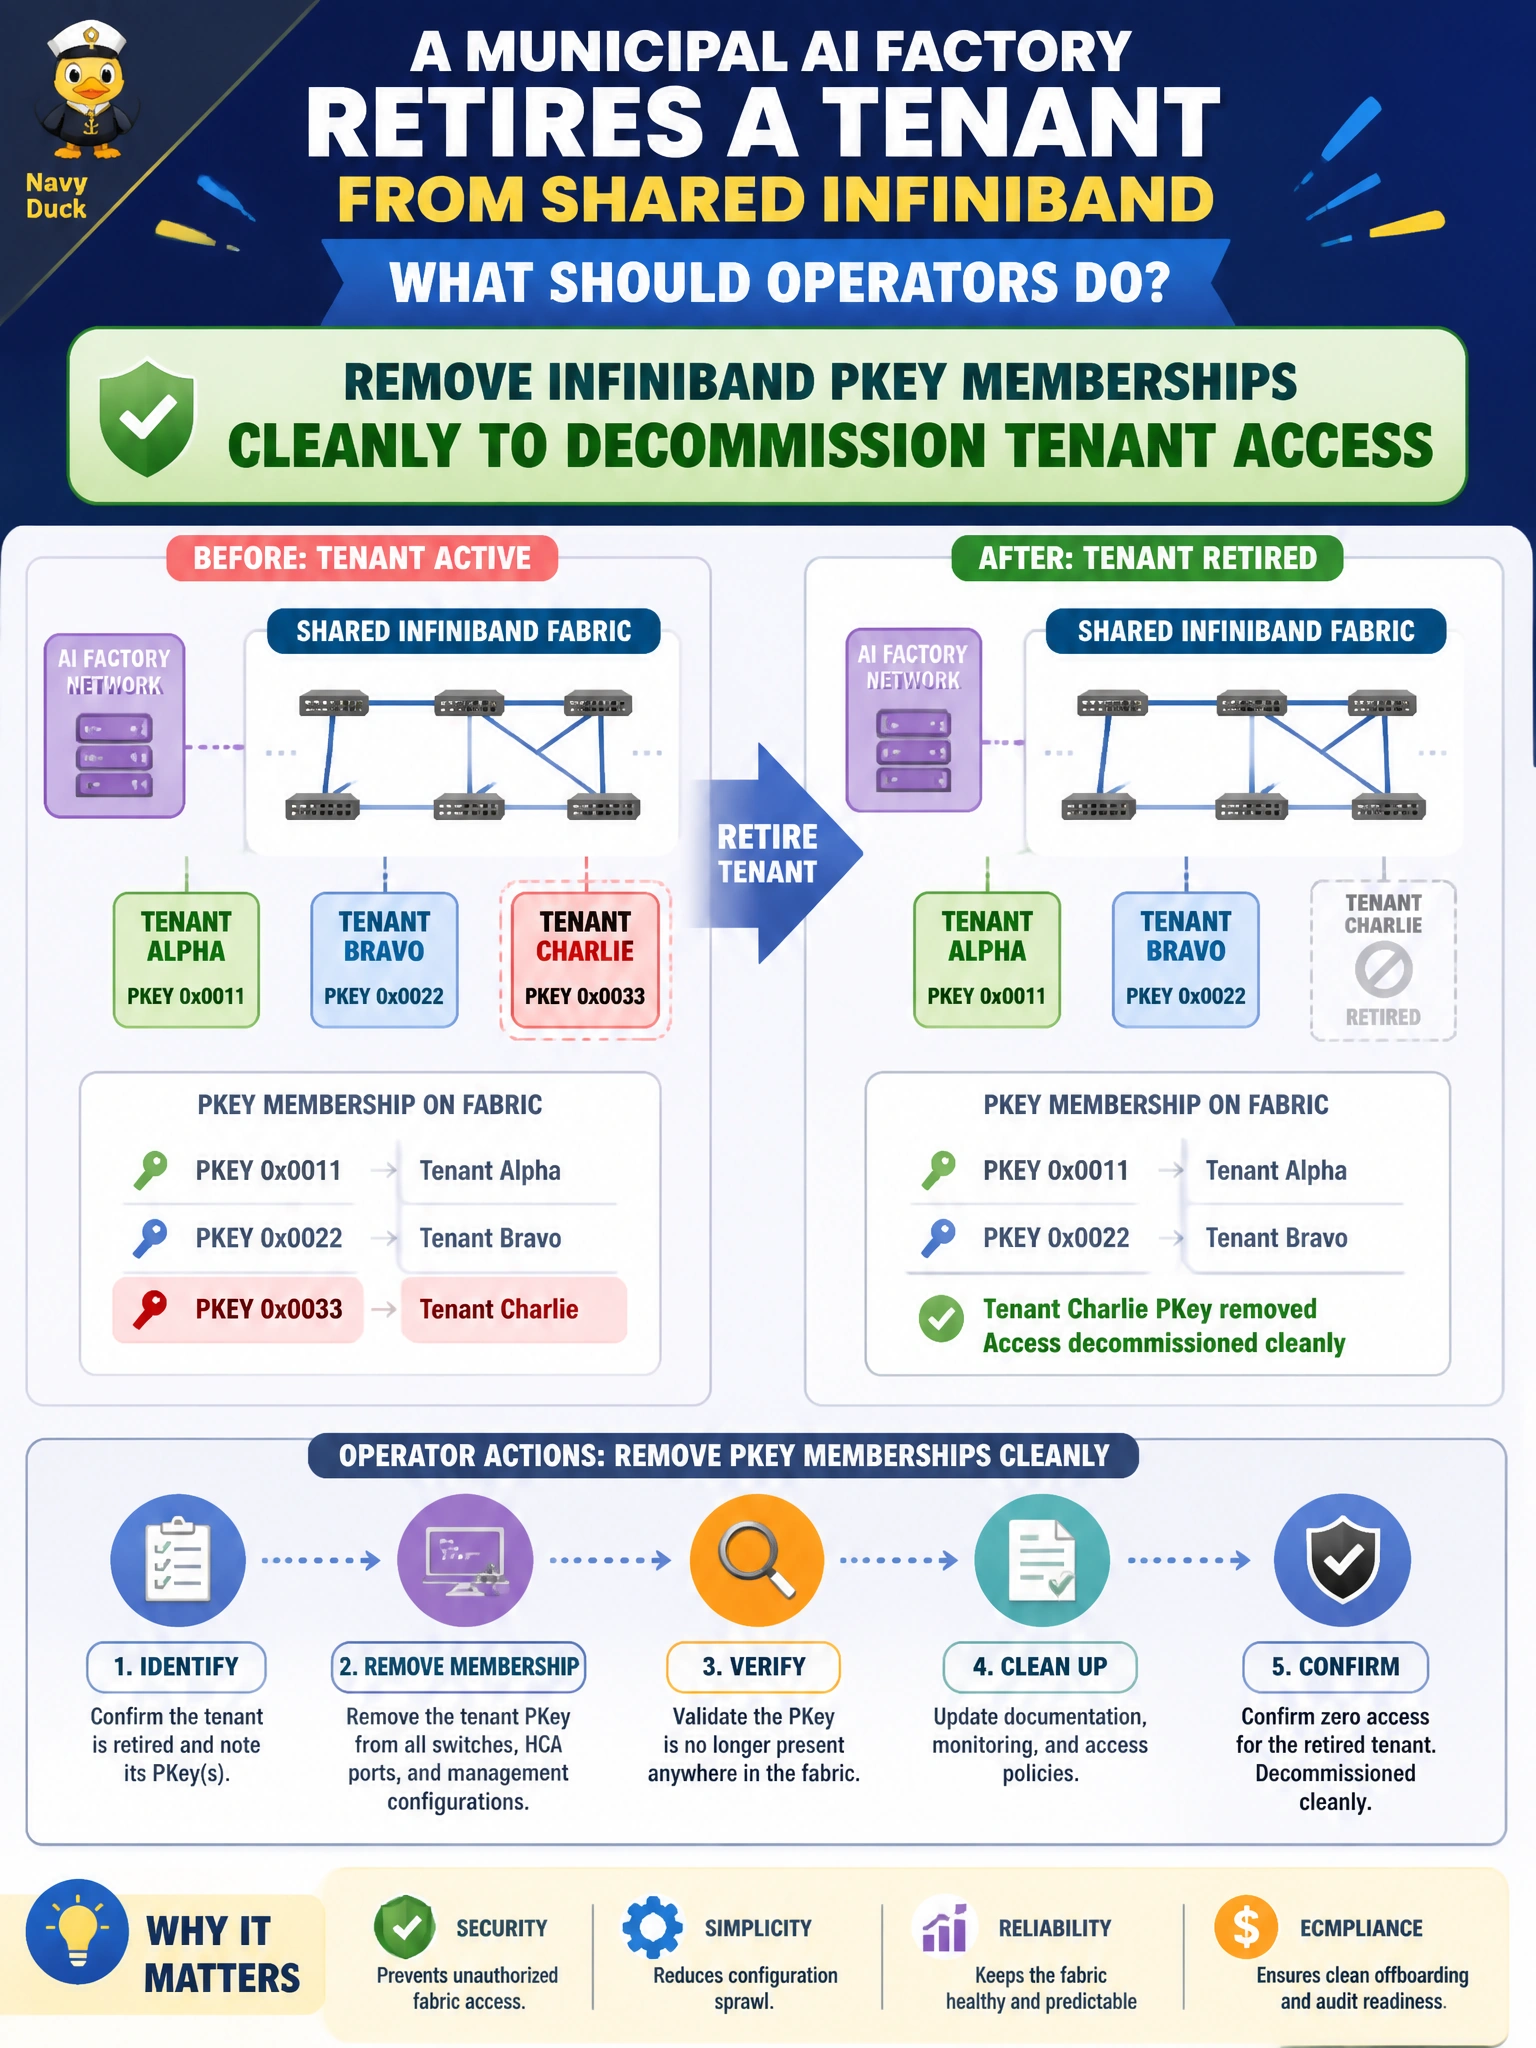
Short Explanation
Limiting or firewalling a retired tenant's access still leaves its PKey membership standing. Remove those memberships cleanly — that's how you make sure the fabric's reachability is actually gone once you decommission the tenant.
Full Explanation
When a municipal AI factory retires a tenant from shared InfiniBand, operators should remove InfiniBand PKey memberships cleanly to decommission tenant access. Clean removal deletes or disables that tenant’s GUID memberships in data (and any temporary) partitions so retired workloads lose IB reachability without disturbing other agencies. Moving retired endpoints to limited PKey membership fails by concept: limited membership still preserves IB reachability after the tenant is gone instead of cleanly removing it, and it leaves incomplete access and audit debt. Enforcing eviction with IPoIB firewall rules while retaining PKeys fails because it addresses the wrong layer and leaves the tenant’s IB PKey membership intact, so it is not a clean InfiniBand tenancy decommission. Triggering a subnet manager rescan to reassign the retired PKey for reuse fails because it does not remove the retiring tenant’s GUID memberships and risks reusing the partition before access is cleanly revoked. Exam caveat: tenant retirement is a scoped PKey membership removal problem, not an IPoIB firewall rule, an SM rescan for PKey reuse, or a limited PKey move. Operational check: inventory the retiring tenant’s GUIDs and PKeys, remove those memberships, verify the GUID can no longer join retired partitions, confirm other agencies’ partitions still function, and update the PKey-to-agency governance record.