
Parks InfiniBand tenant onboarding must limit access for a new civic project. What PKey practice should staff apply?
Select an answer to reveal the explanation.
Short Explanation
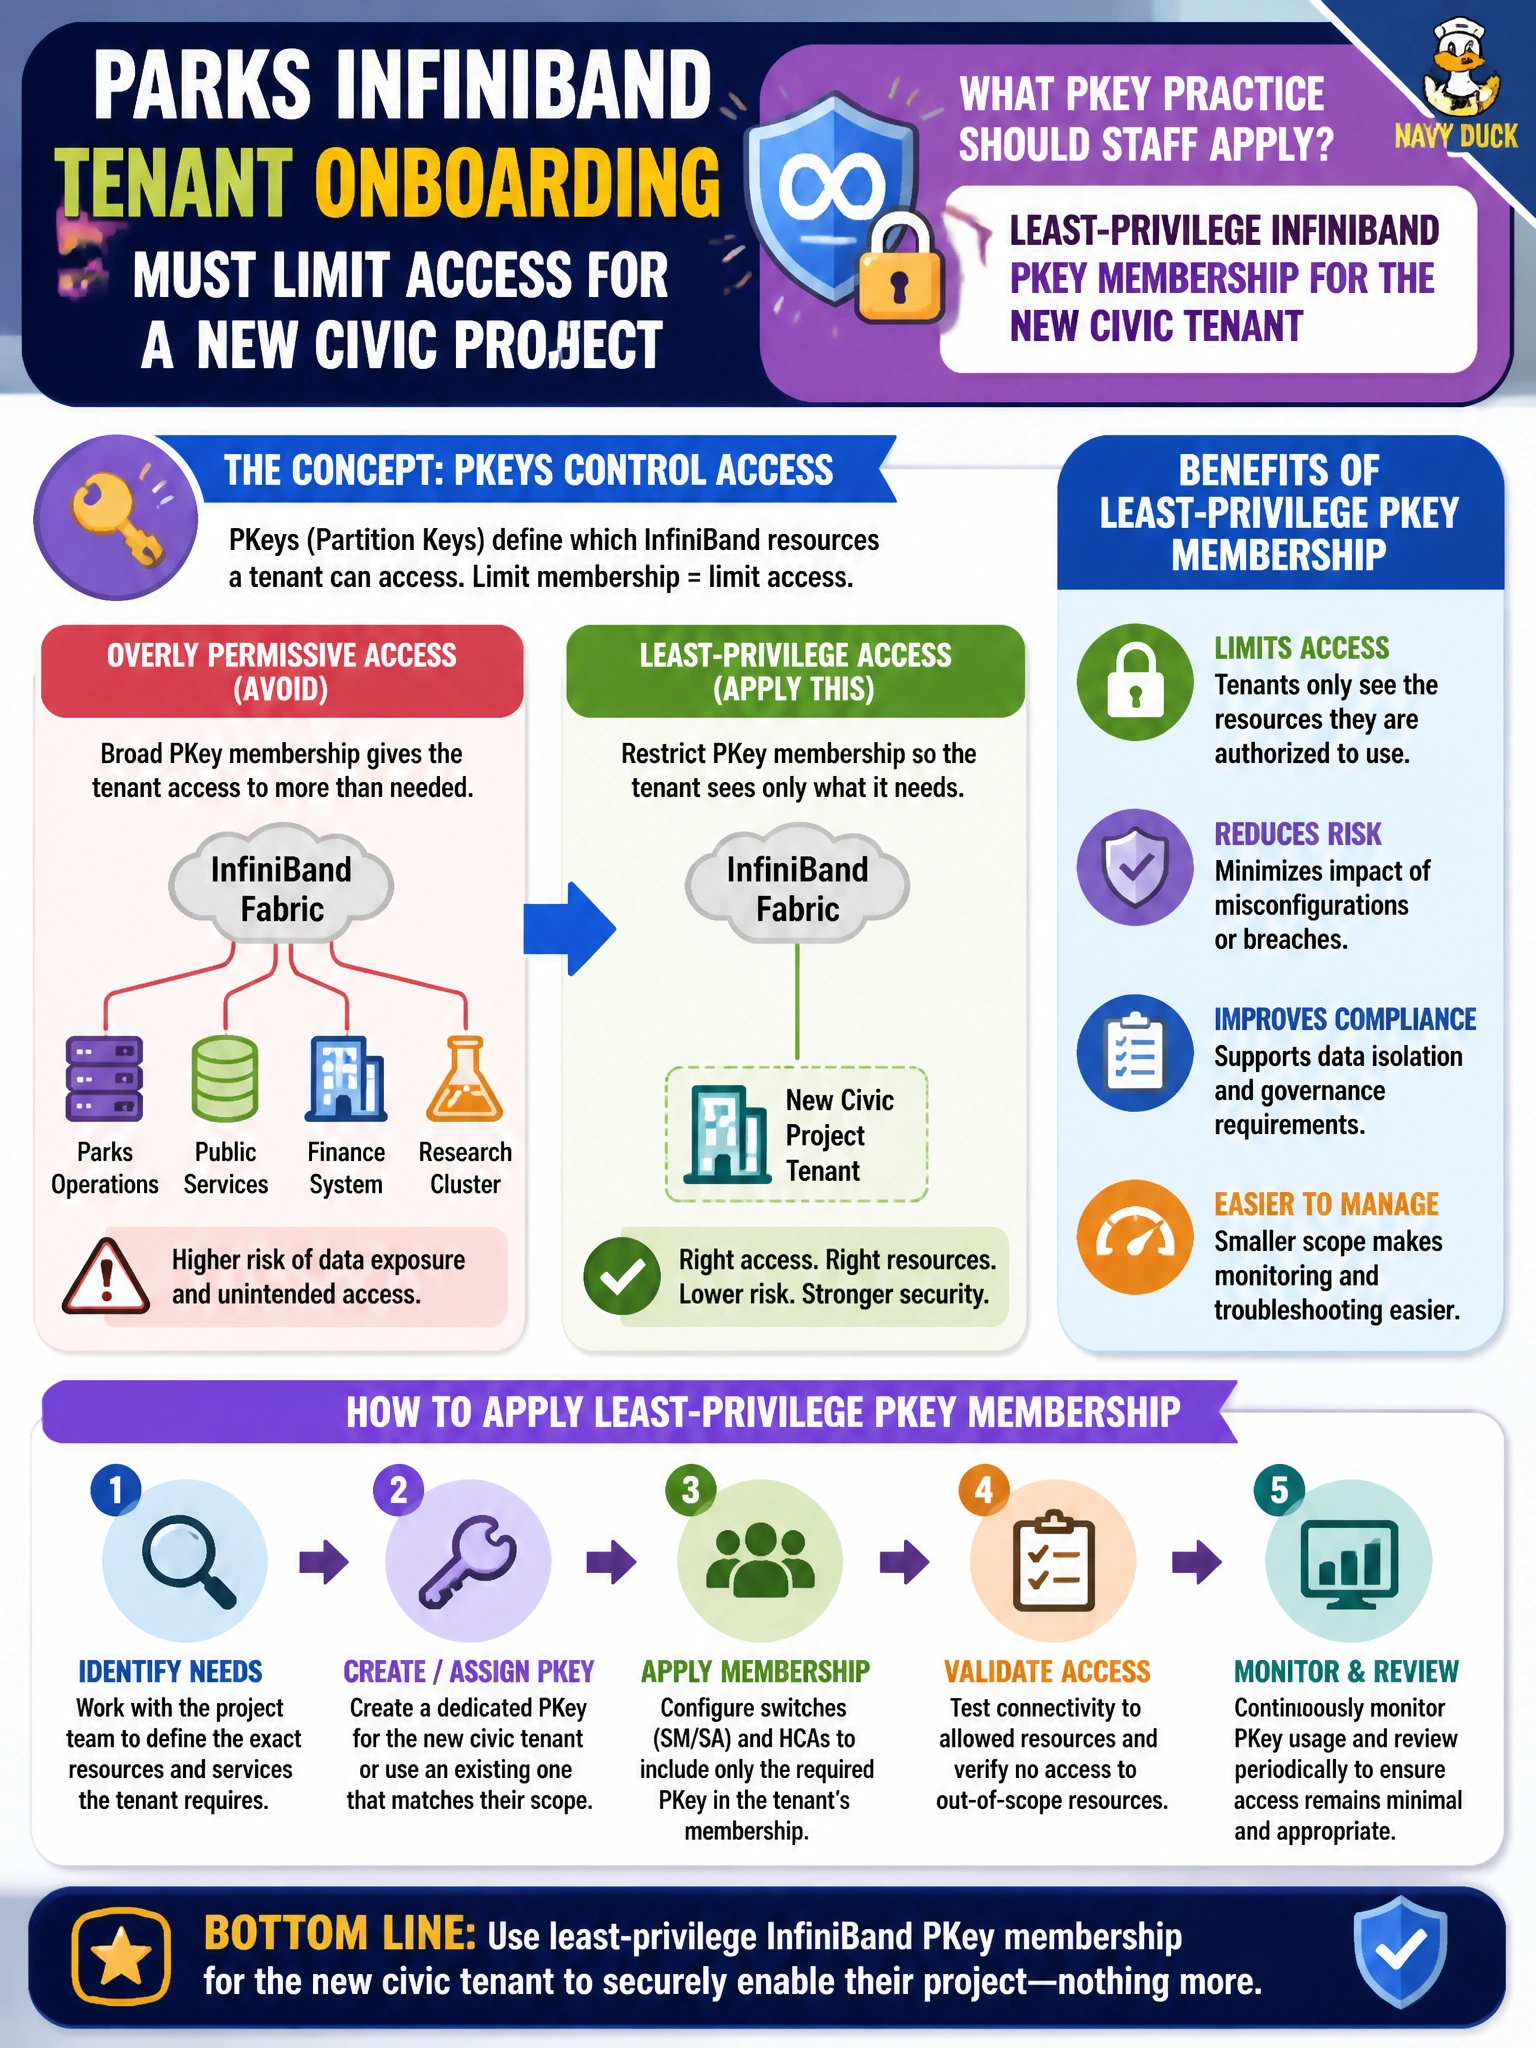
New parks projects get the keys they need—not the whole keychain. Apply least-privilege InfiniBand PKey membership at onboarding.
Full Explanation
Parks InfiniBand tenant onboarding for a new civic project should apply least-privilege InfiniBand PKey membership: grant only the partitions the project needs, including carefully scoped data PKeys and no casual management membership. Least privilege limits blast radius if a project workload is compromised and keeps shared IB multi-tenancy aligned with municipal access policy. Provisioning default partition PKey 0xFFFF with full membership for tenant access fails because it grants broad default-partition rights instead of least-privilege, project-scoped PKey membership and exposes the tenant to unnecessary fabric reach. Offering limited PKey membership for management partition monitoring by tenant fails because any management partition access gives the new civic project visibility into fabric operations outside its scope, violating least-privilege onboarding. Reusing a shared service PKey with full membership for tenant connectivity fails because a shared service PKey is not a requirements-based grant for the parks project and full membership over-shares connectivity rather than assigning only needed partitions. Exam caveat: onboarding questions reward least-privilege PKey assignment at day one, not “open wide then harden.” Operational check: define the parks project’s required partitions, assign only those PKeys with correct membership types, verify required RDMA works, confirm management and unrelated agency PKeys are absent, and record the grant in the tenancy register.