
Automated CI should fail an agent pipeline when which tool-governance condition is detected?
Select an answer to reveal the explanation.
Short Explanation
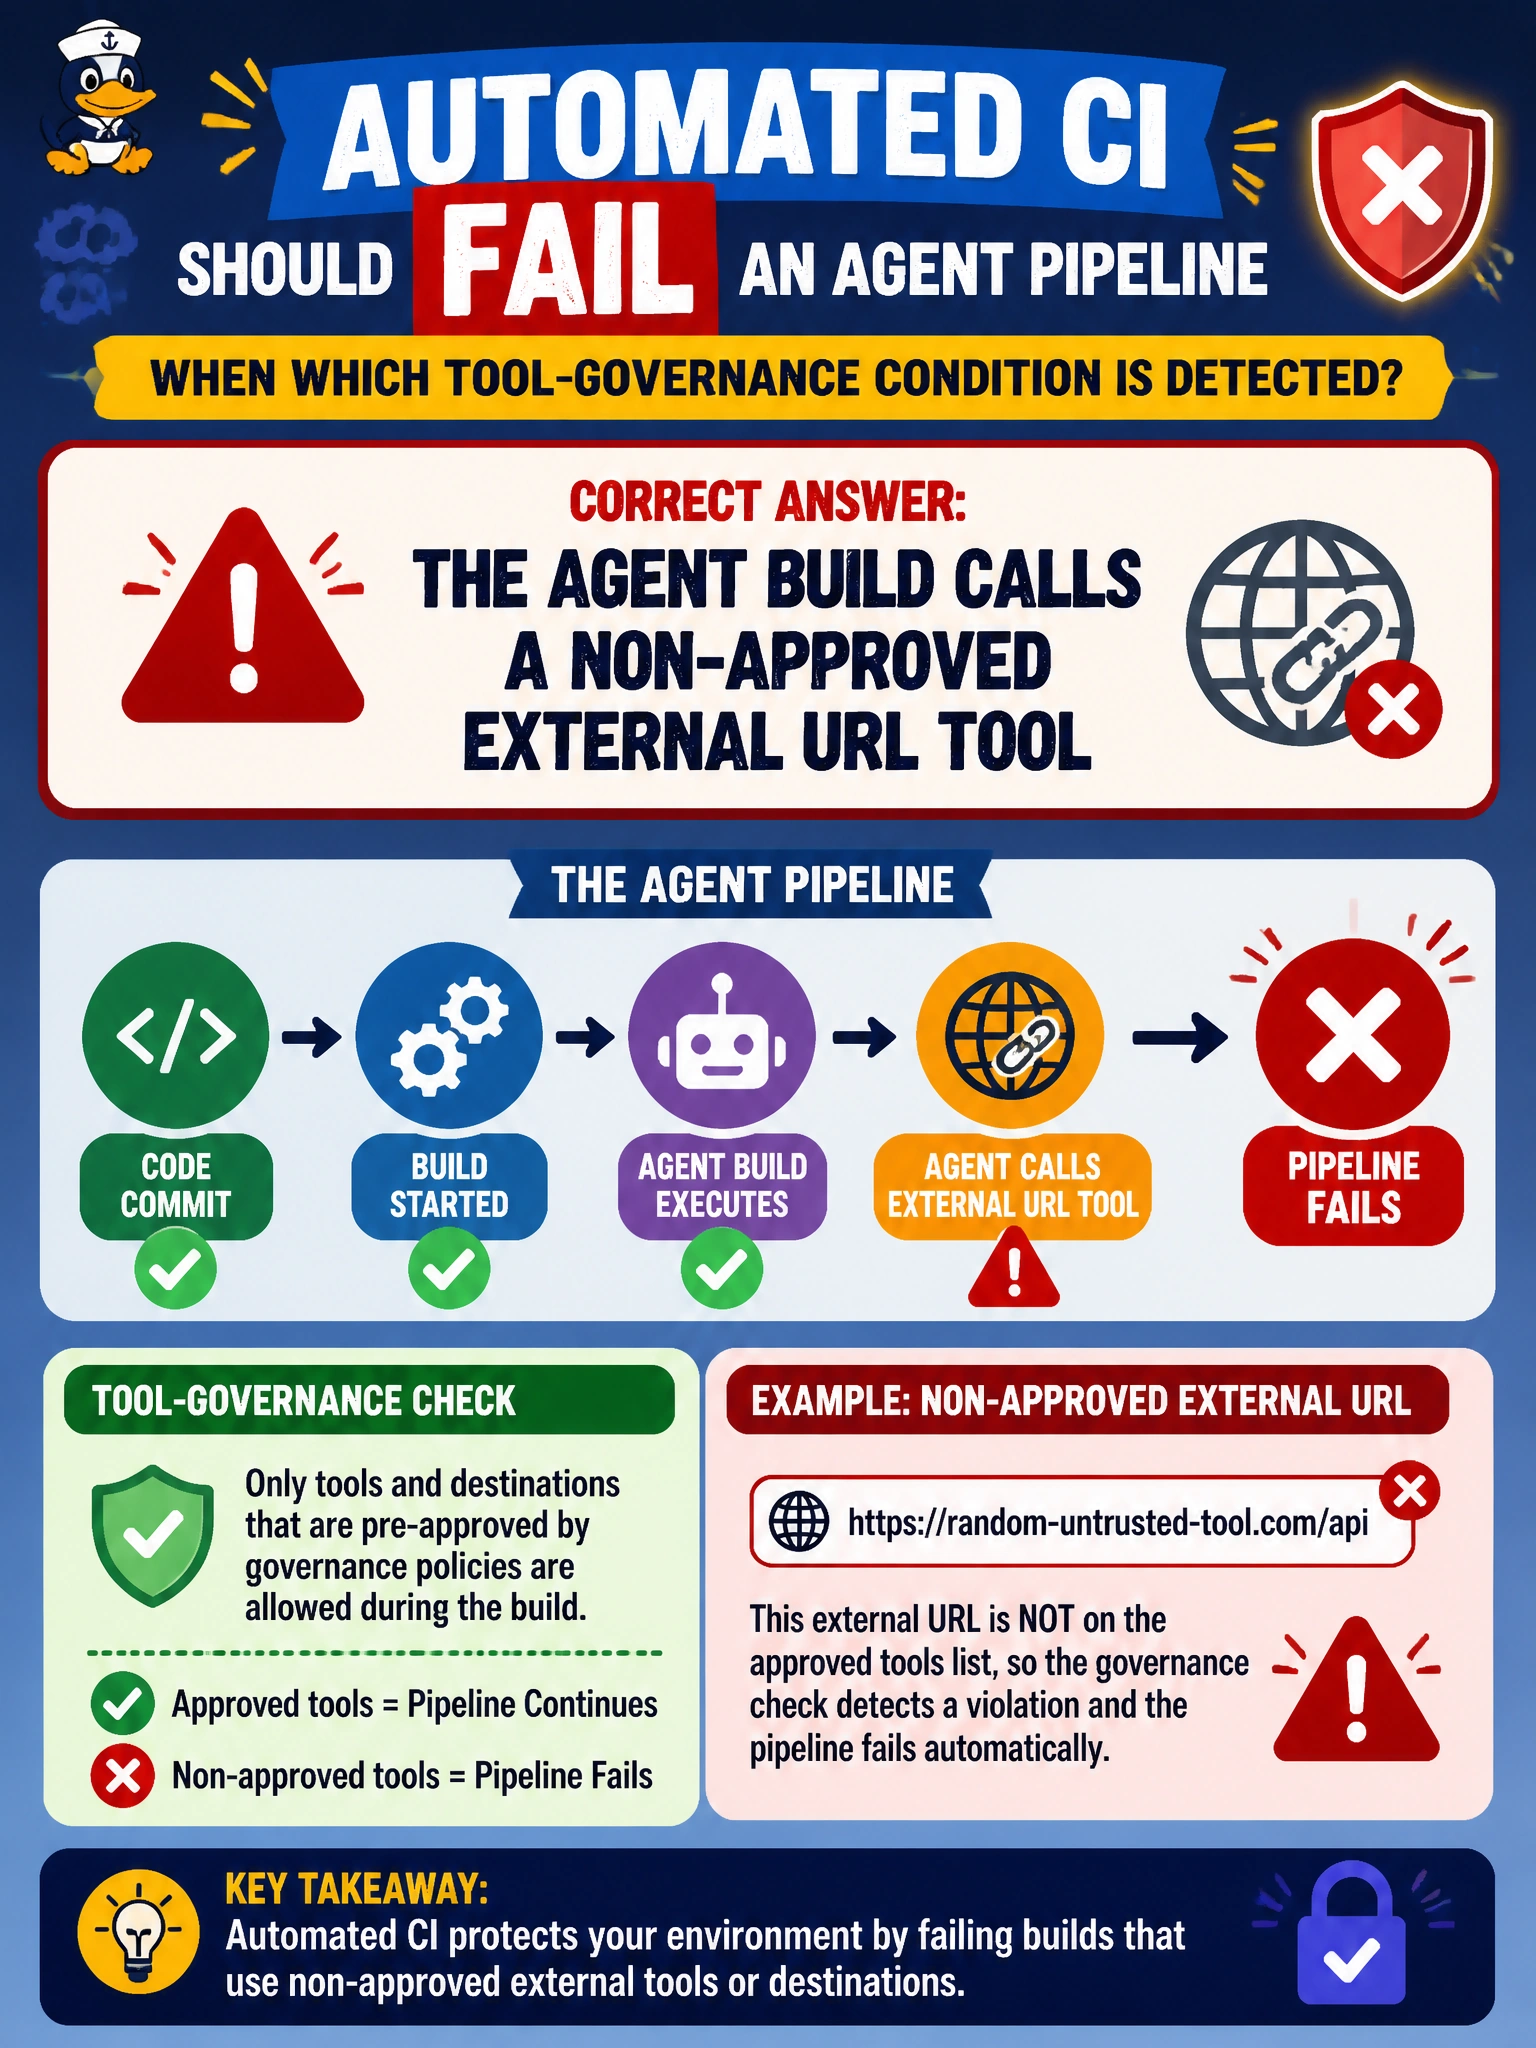
If the build sneaks in a random external URL tool, CI should slam the brakes. Approved city APIs and clean changelogs are fine—policy-as-code is there to catch the unapproved dial-out before it reaches residents.
Full Explanation
Policy-as-code checks in civic agent CI/CD fail builds that invoke non-approved external URL tools, enforcing tool governance before promotion. Automated CI should fail when the agent build calls a non-approved external URL tool so unvetted dial-out never reaches production municipal networks or resident data paths. Allowlists and deny rules encode city integration policy as executable gates rather than slideware that ops hope someone remembers.
Using an approved city API listed on the allowlist is the expected success path, not a failure trigger. Unit tests passing with coverage meeting threshold are healthy signals, not reasons to fail the pipeline. A changelog that documents approved tool schemas supports governance and auditability rather than violating tool policy.
Exam caveat: CI tool-governance gates fail on non-allowlisted external tools; allowlisted city APIs, passing tests, and clean changelogs are not failure conditions. Operational check: add a deliberate non-approved URL tool reference to a branch, confirm CI fails with a clear policy message; remove it and confirm the pipeline goes green; periodically audit the allowlist against the city’s approved integration inventory and revoke stale entries.