
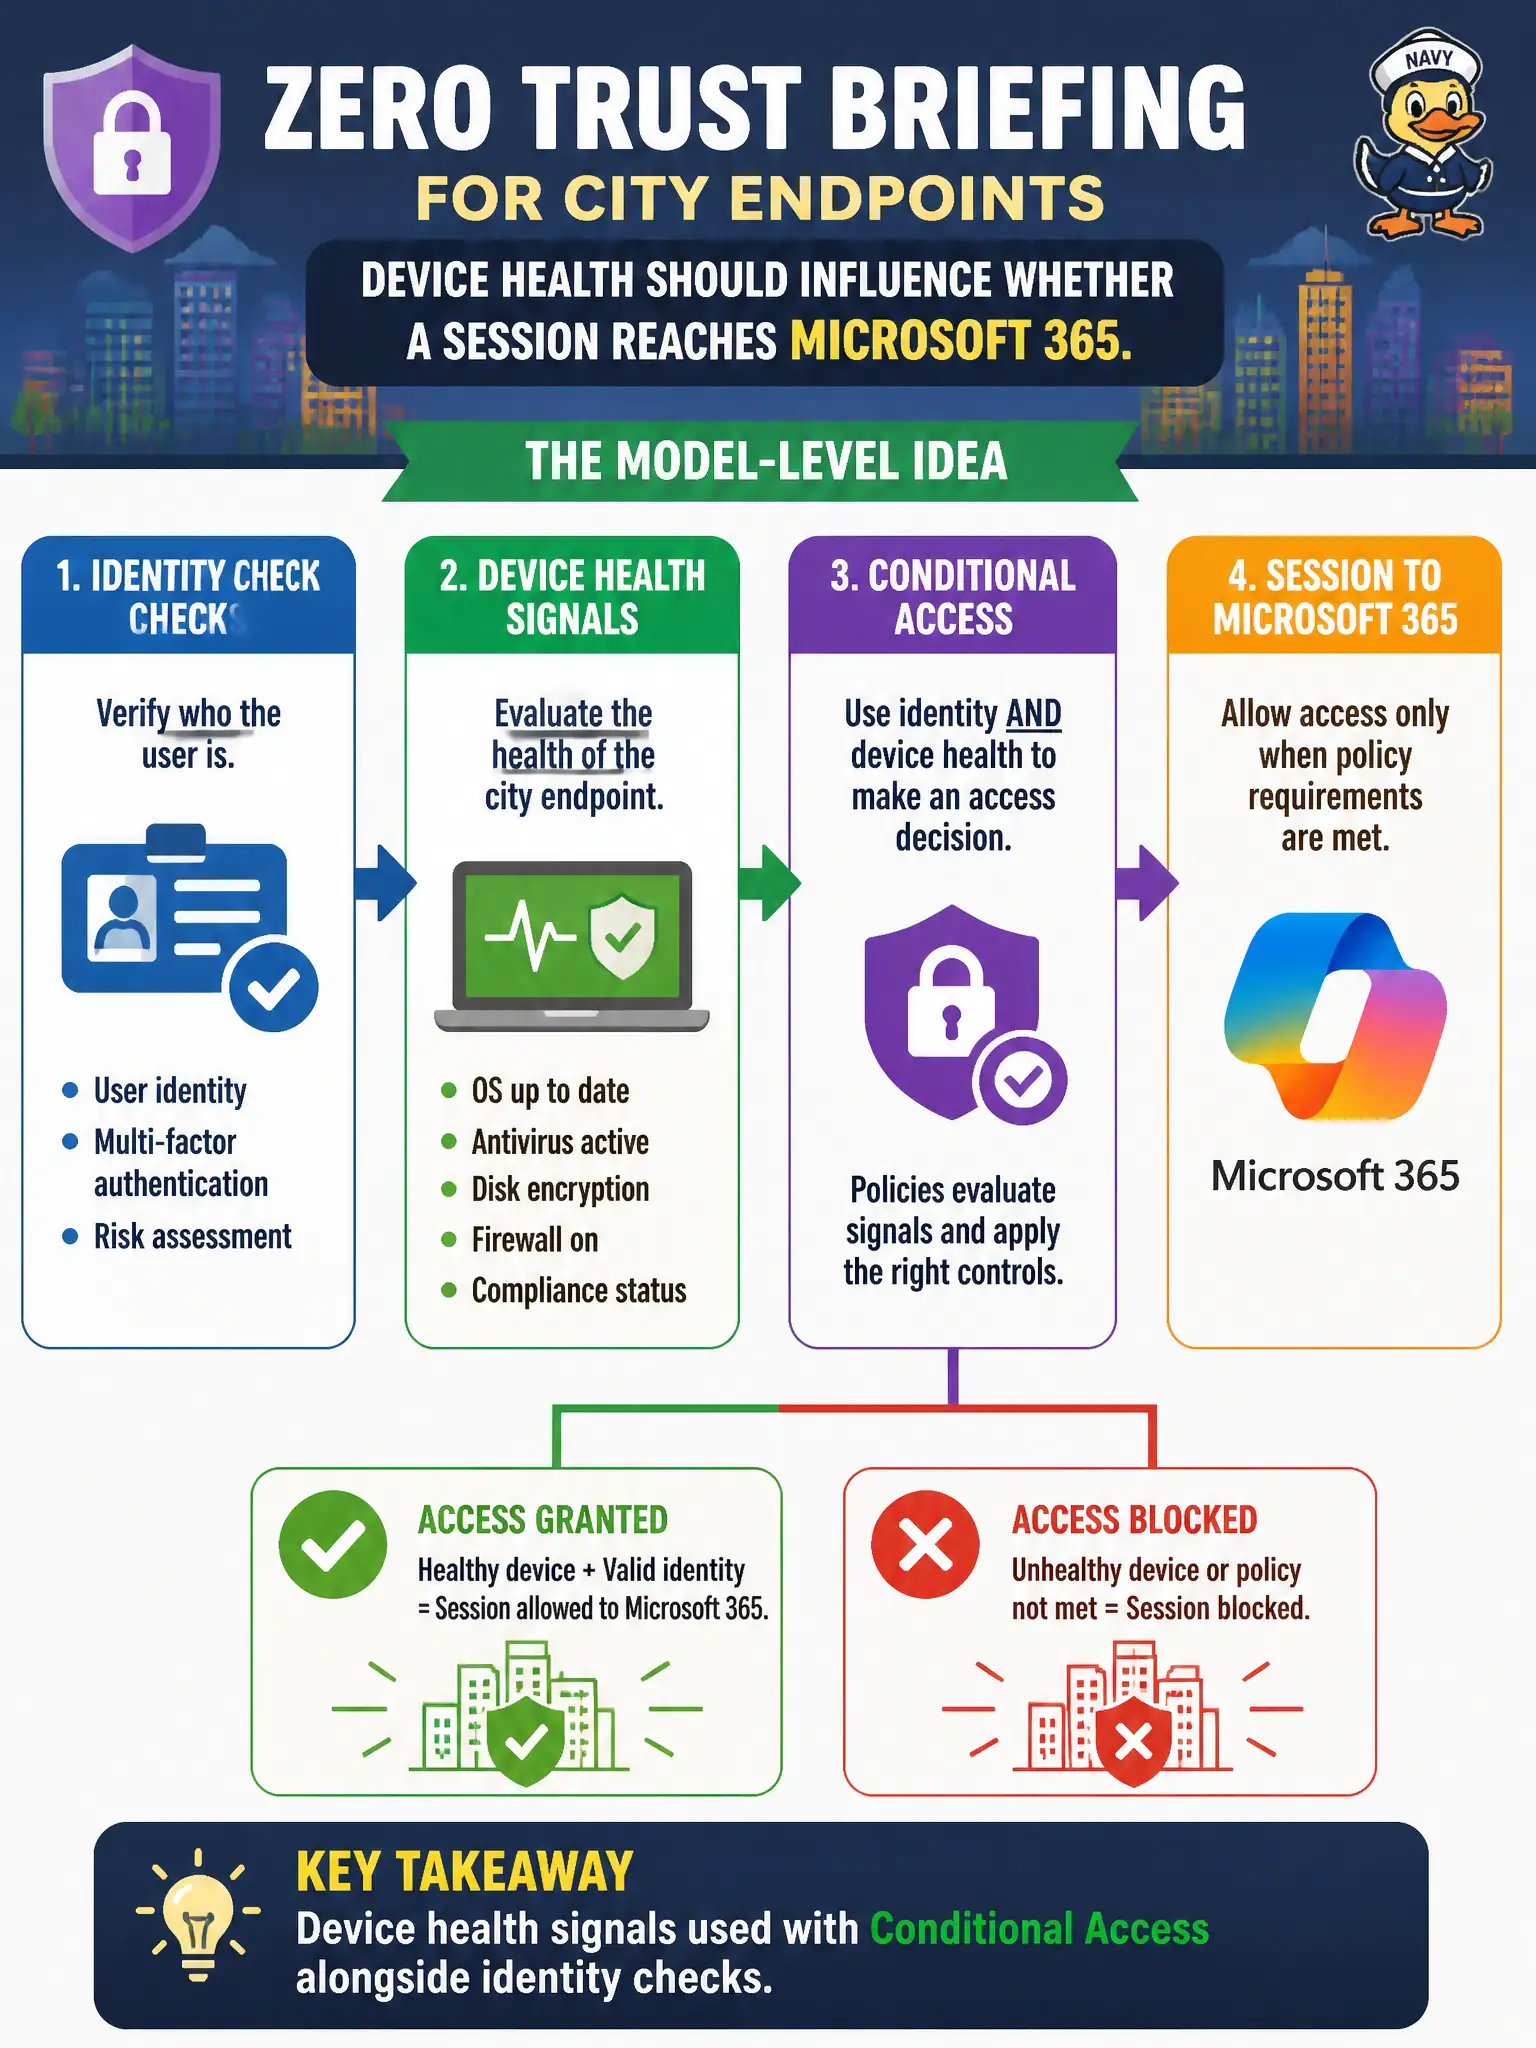
A Zero Trust briefing for city endpoints says device health should influence whether a session reaches Microsoft 365. Which pairing matches that model-level idea?
Select an answer to reveal the explanation.
Short Explanation
Zero Trust does not stop at the password. Healthy device signals and Conditional Access work with identity so risky machines do not stroll into city apps unchecked.
Full Explanation
A Zero Trust briefing for city endpoints that says device health should influence whether a session reaches Microsoft 365 matches pairing device health signals with Conditional Access alongside identity checks. Zero Trust evaluates more than passwords: compliant or healthy devices plus strong identity reduce the chance that risky machines reach municipal cloud apps.
Device health is not used only to choose Teams meeting backgrounds. Device health should not permanently disable Entra ID for every user. Device health does not replace Microsoft 365 licensing purchases.
Exam caveat: Intune compliance or Defender health signals typically feed Conditional Access—know the model-level idea without requiring deep policy authoring on MS-900. Operational check: require a compliant device grant in Conditional Access for a pilot group accessing Exchange Online, attempt access from a noncompliant test device, and confirm the block or remediation message. In municipal Microsoft 365 fundamentals scenarios, always map the business need to the named capability, reject distractors that describe a different pillar, and verify the control in the admin portal before telling leadership the risk is closed.