
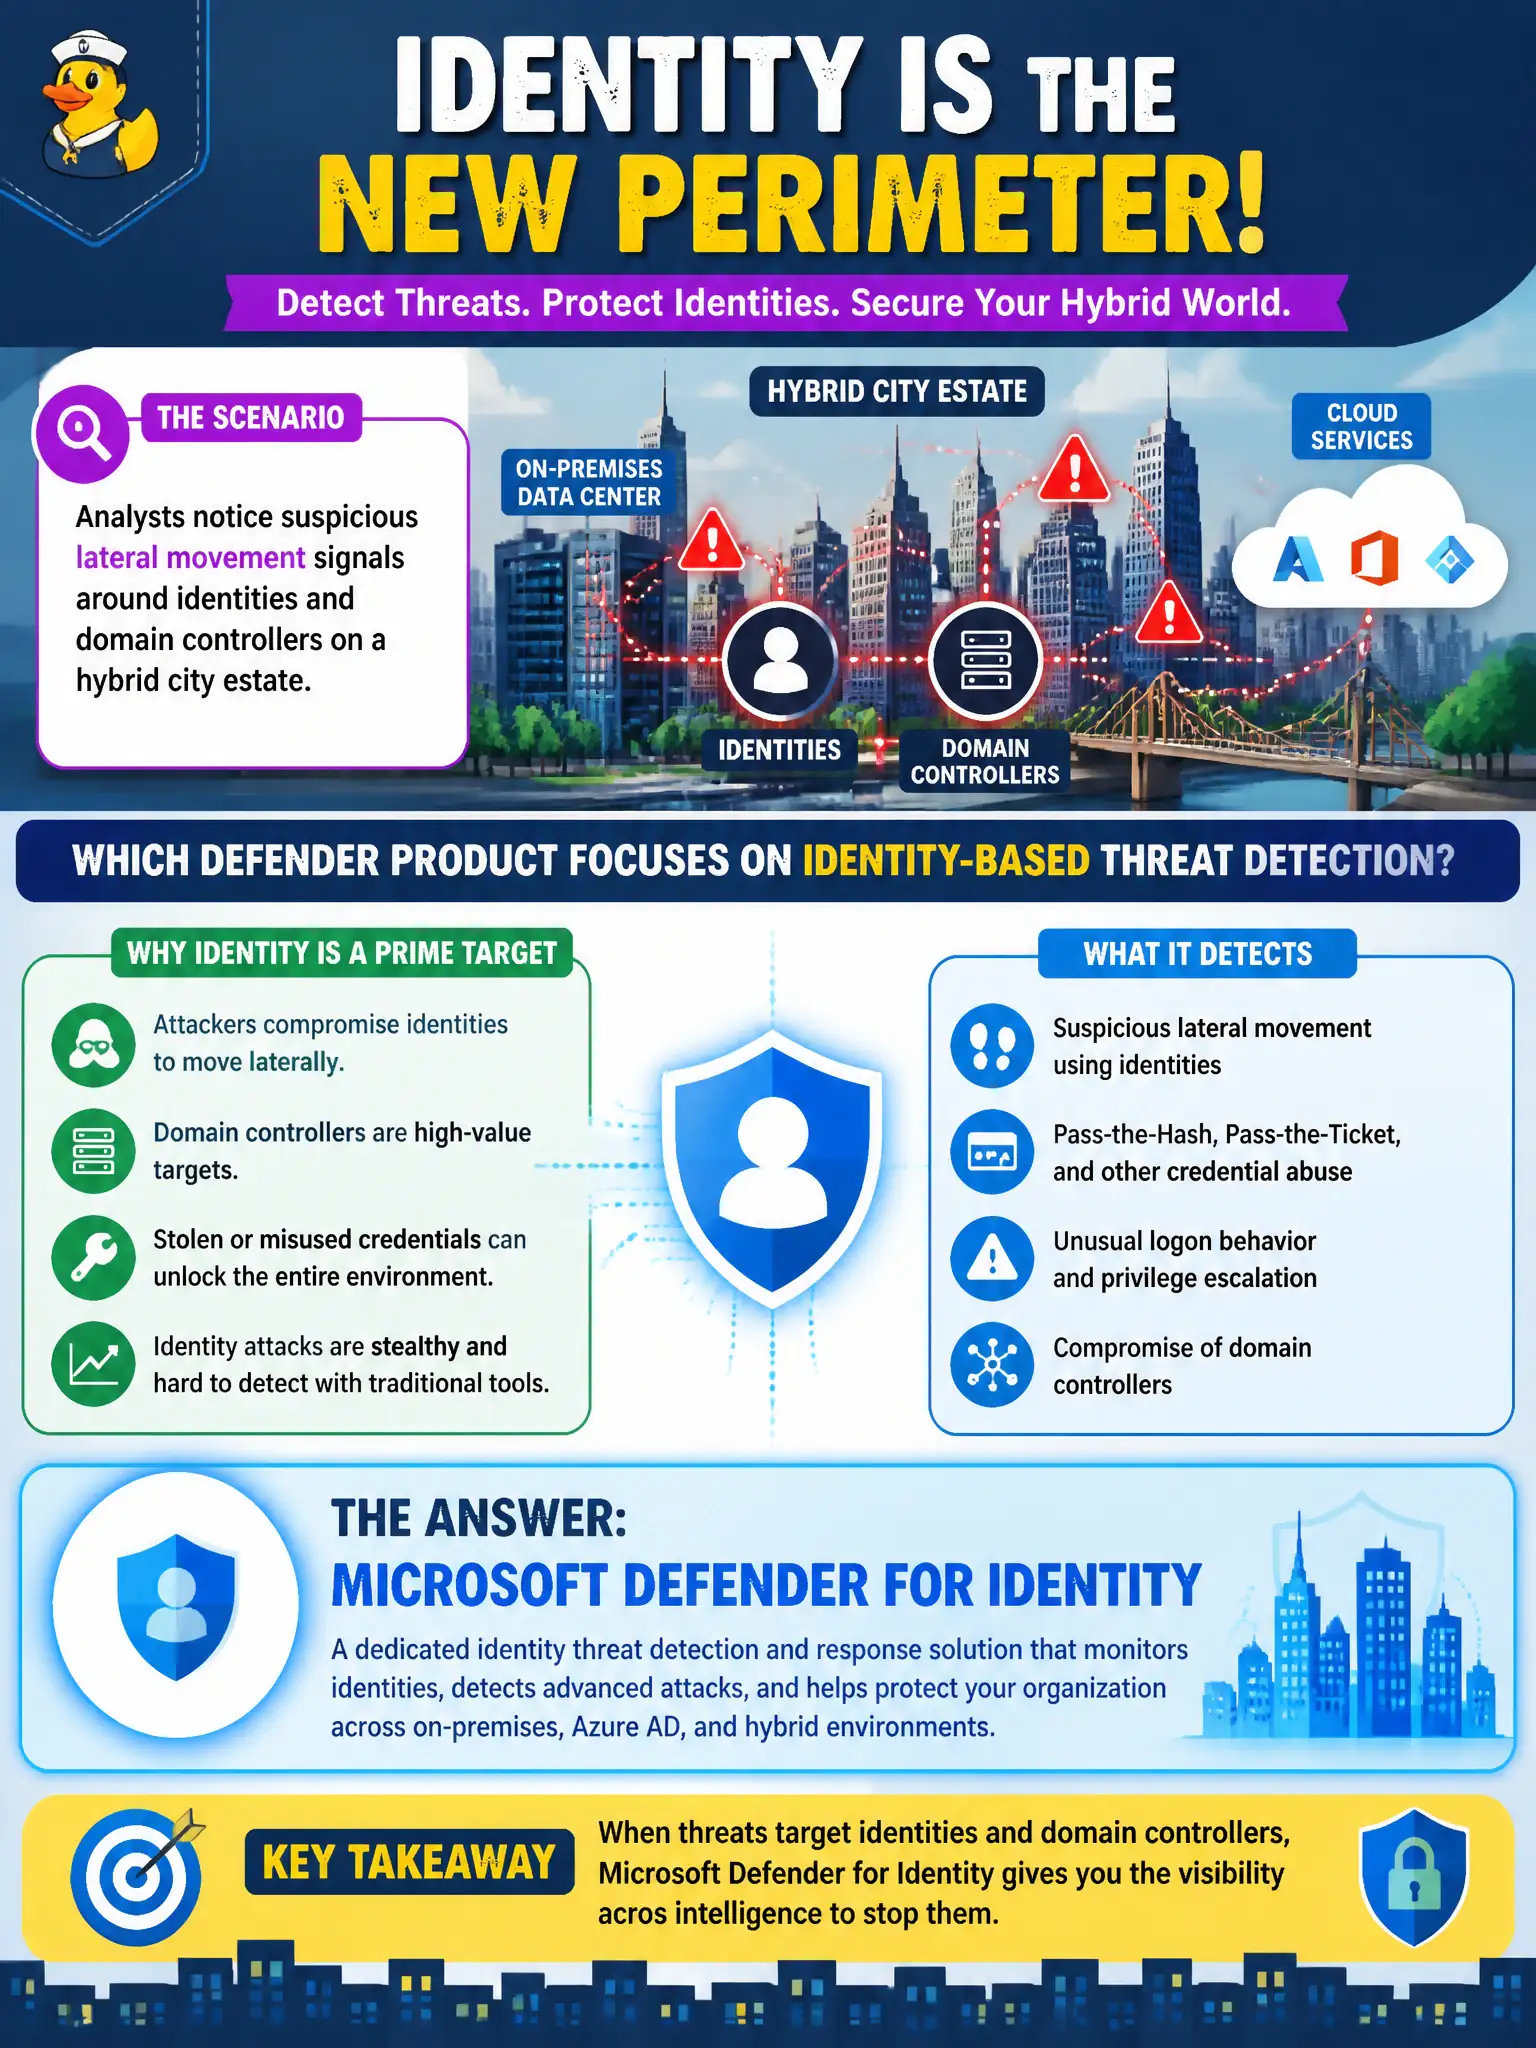
Analysts notice suspicious lateral movement signals around identities and domain controllers on a hybrid city estate. Which Defender product focuses on identity-based threat detection?
Select an answer to reveal the explanation.
Short Explanation
When the bad guys start hopping between accounts and domain controllers, that is an identity hunt. Defender for Identity watches those directory-side moves. Stream, Lists, and Viva Learning are not identity threat sensors.
Full Explanation
Microsoft Defender for Identity focuses on identity-based threat detection, which fits analysts noticing suspicious lateral movement signals around identities and domain controllers on a hybrid city estate. It watches identity infrastructure behaviors that endpoint or email tools alone may not contextualize well for municipal hybrid directories. For hybrid civic estates that still run domain controllers, Defender for Identity is the fundamentals product mapping for identity threat awareness and related detections.
Microsoft Stream for training video hosting is not an identity threat sensor. Microsoft Lists for parking permit tracking is a list app, not a SOC identity detector. Microsoft Viva Learning is a learning experience, not the SOC console for identity attacks.
An exam caveat is that Defender for Identity is especially relevant in hybrid scenarios with on-premises identity signals and pairs with broader Defender XDR correlation. Operationally, ensure hybrid identity sensors and configurations for Defender for Identity are healthy, open a representative identity alert in the Defender portal, and include identity lateral-movement playbooks in the city SOC’s hybrid estate documentation.