
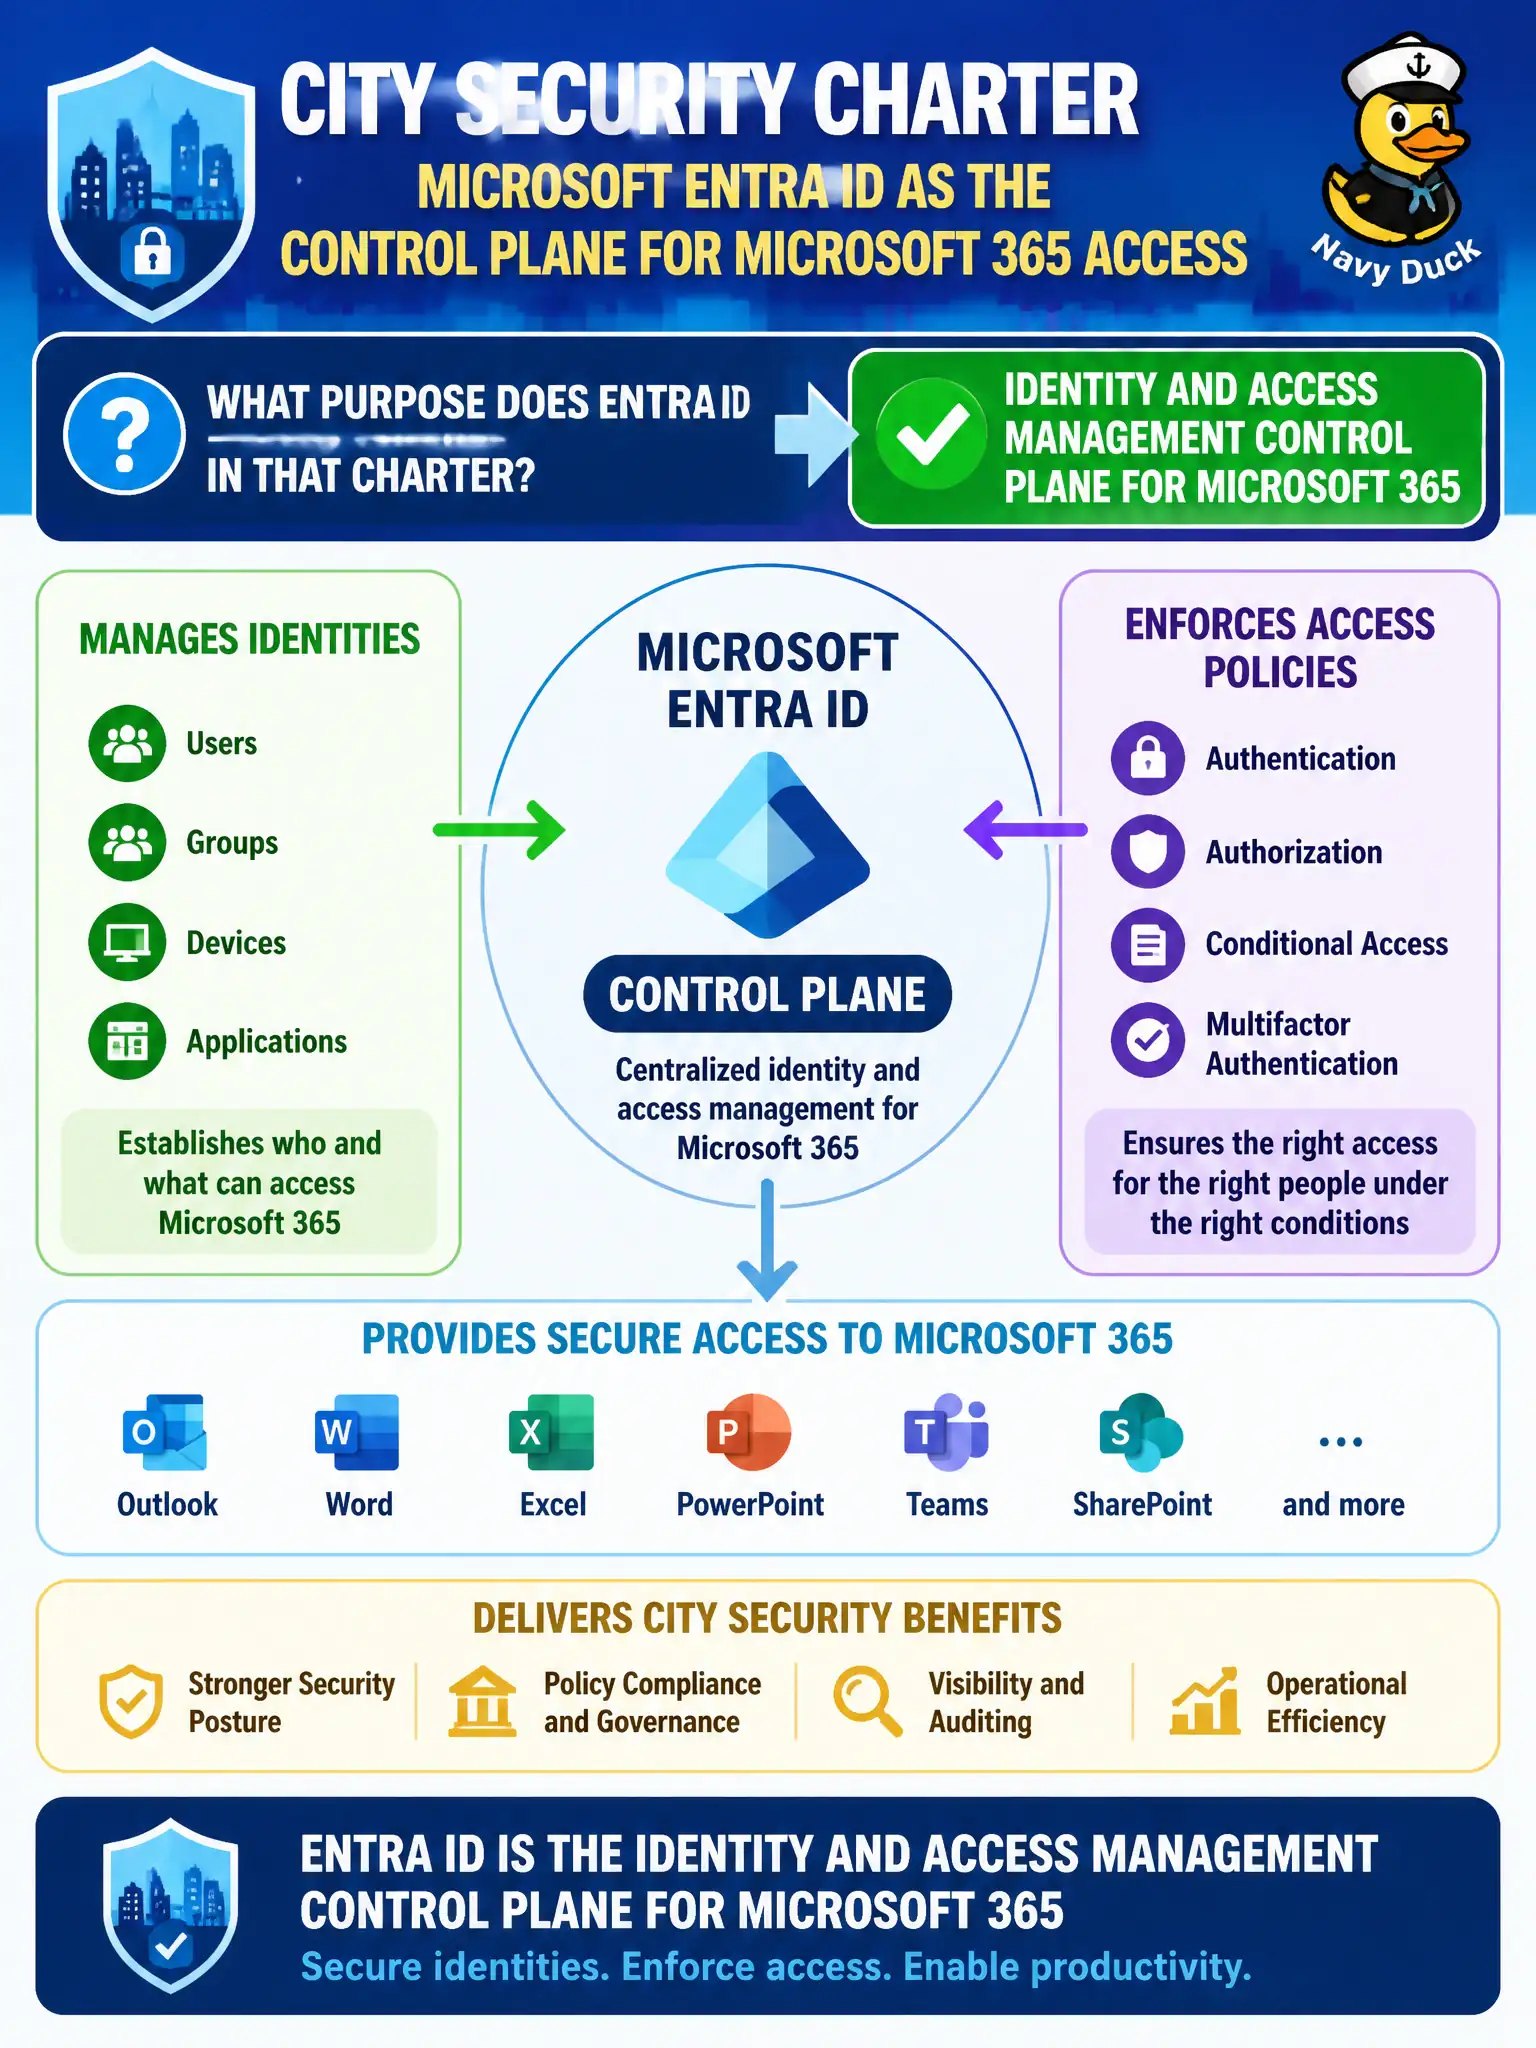
A city security charter lists Microsoft Entra ID as the control plane for Microsoft 365 access. What purpose does Entra ID serve in that charter?
Select an answer to reveal the explanation.
Short Explanation
Entra ID is the front door for who gets into Microsoft 365 — accounts, groups, and sign-in decisions live there. The charter is naming the identity and access control plane, not a firewall or a mailbox archive. Get the door right and everything else hangs on it.
Full Explanation
Microsoft Entra ID serves as the identity and access management control plane for Microsoft 365 when a city security charter lists it that way. Entra ID authenticates users, manages groups and roles, and provides the policy hooks for Conditional Access and related access decisions across Microsoft 365 workloads used by municipal departments. Framing Entra ID as the control plane helps civic security charters stay accurate, auditable, and actionable for both IT and oversight stakeholders.
Entra ID is not endpoint patch orchestration instead of Intune or Autopatch. It is not a mailbox journaling archive instead of Exchange Online. It is not a network firewall appliance for on-premises CAD systems.
An exam caveat is that other control planes still exist—Defender for threats, Purview for compliance, Intune for devices—but identity decisions for Microsoft 365 access center on Entra ID. Operationally, align the city’s security charter language to Entra ID for IAM, map privileged roles there, and verify Microsoft 365 app access failures are triaged first as identity or Conditional Access issues before blaming unrelated firewall or journaling systems. In practical city governance terms, naming Entra ID as the IAM control plane also clarifies budget and tooling ownership: identity incidents route to identity administrators first, while firewall and journaling teams remain responsible for their own domains. That clarity shortens municipal incident bridges when Microsoft 365 sign-in fails during peak citizen-service hours.