
A civic CIO asks whether on-premises Active Directory alone can natively authenticate users to Microsoft 365 cloud services with no cloud identity integration. What is the correct fundamentals answer?
Select an answer to reveal the explanation.
Short Explanation
Microsoft 365 lives in the cloud and expects Entra ID for cloud sign-in. Local AD can still matter in hybrid, but it does not natively host M365 cloud auth by itself. Integration—or cloud-only Entra ID—is required.
Full Explanation
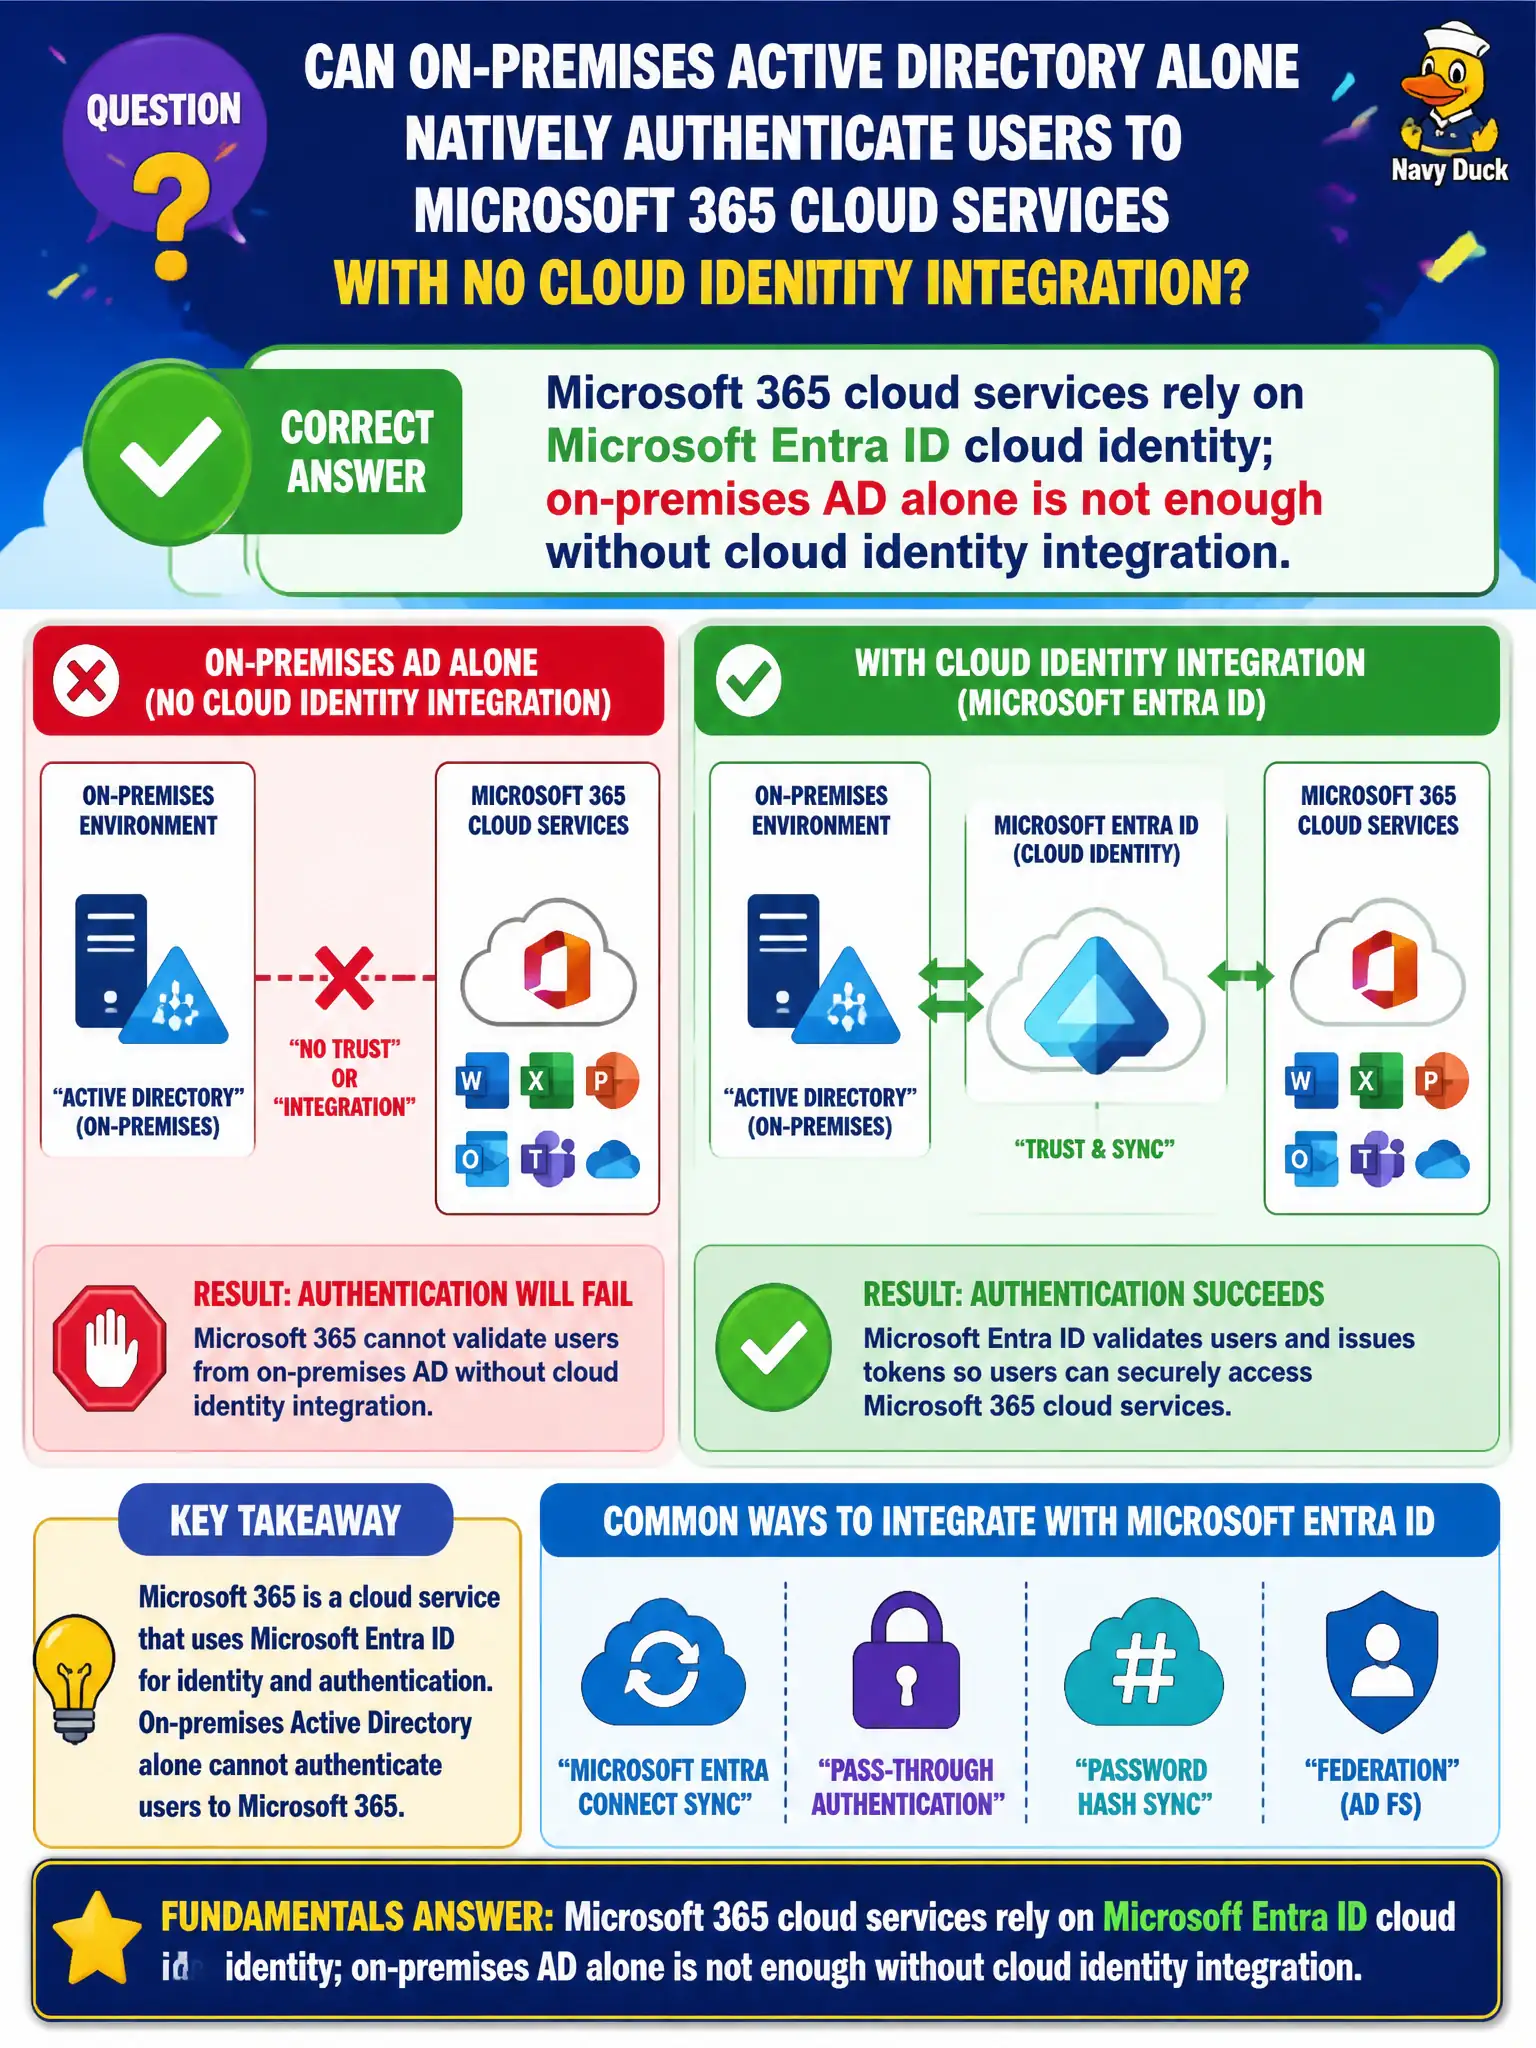
Microsoft 365 cloud services rely on Microsoft Entra ID cloud identity; on-premises Active Directory alone is not enough without cloud identity integration. A civic CIO asking whether AD DS by itself can natively authenticate users to Microsoft 365 must hear that Entra ID is required in the cloud authentication path, whether accounts are cloud-only or synchronized through hybrid identity. That distinction prevents municipal architecture teams from assuming classic domain controllers alone unlock Exchange Online, Teams, and SharePoint.
On-premises AD DS alone does not fully replace Entra ID for all Microsoft 365 cloud authentication scenarios. Microsoft 365 cloud apps do not authenticate only through Microsoft Stream CDN edges. Microsoft 365 does use directory services for sign-in; claiming it never does is false.
An exam caveat is that hybrid identity still depends on Entra ID on the cloud side even when AD DS remains authoritative on-premises—sync does not eliminate Entra ID. Operationally, attempt to explain the city’s Microsoft 365 sign-in path end to end, confirm users appear in Entra ID, and document that any remaining AD DS servers support on-premises resources or sync, not a pure AD-only Microsoft 365 authentication design.