
A township network engineer assumes Conditional Access is simply another perimeter firewall rule set. What is the more accurate description for Microsoft 365?
Select an answer to reveal the explanation.
Short Explanation
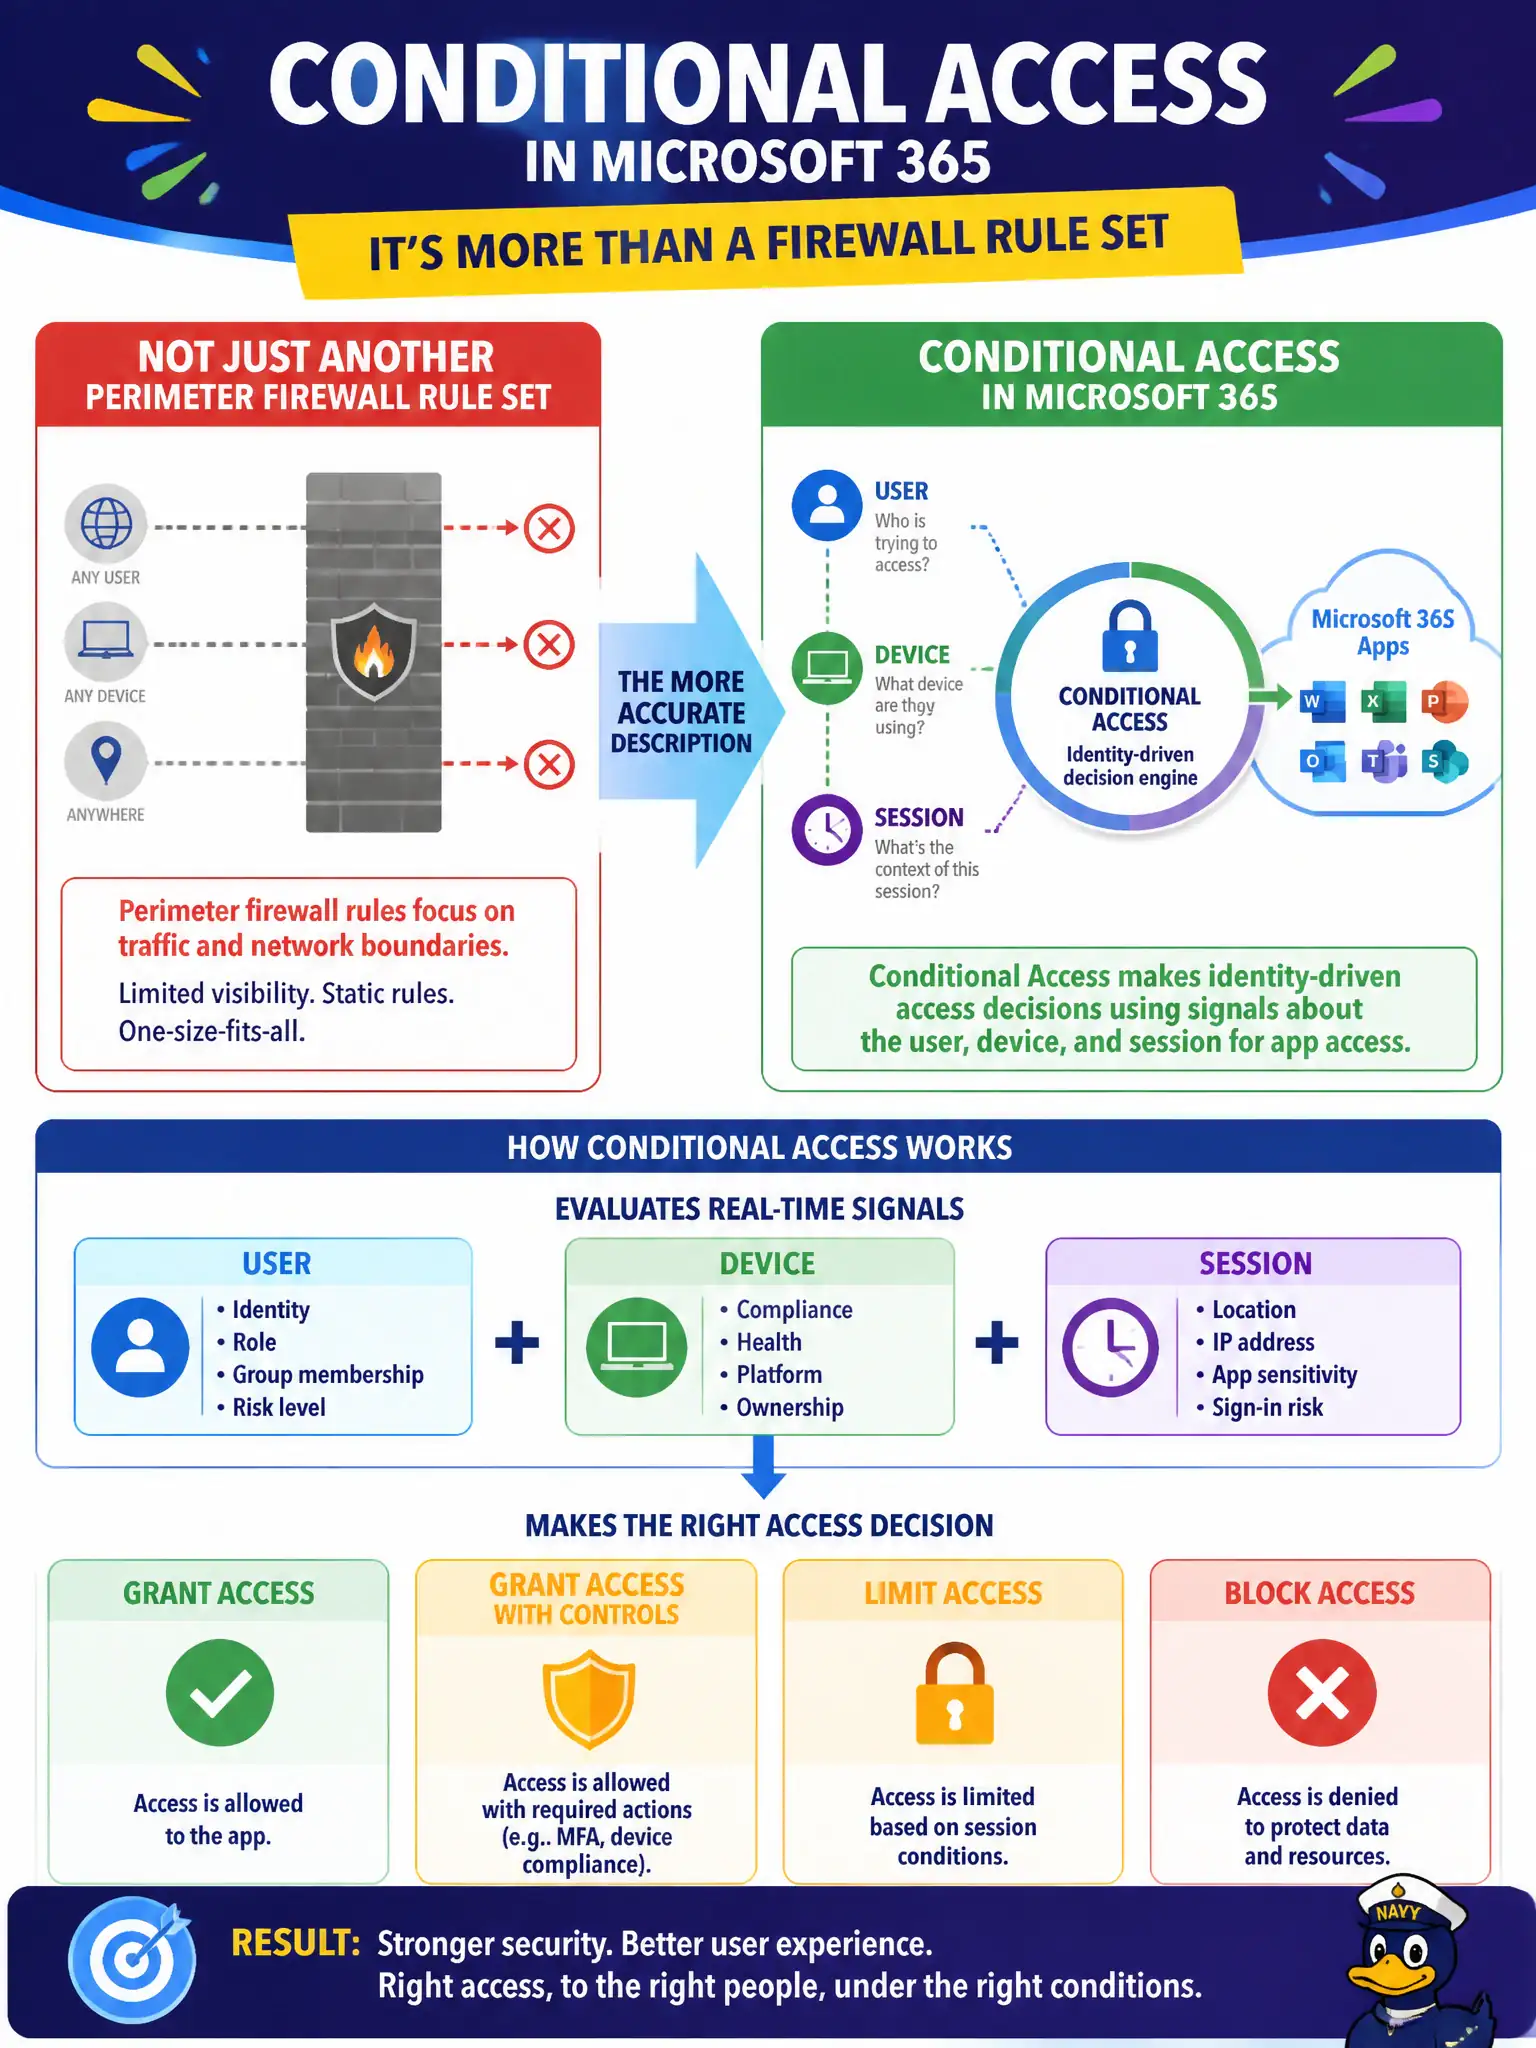
A firewall watches network ports; Conditional Access watches who is signing in, from what device, and under what conditions. Same goal of control, different layer. Think identity decisions for apps, not only packet filters.
Full Explanation
Conditional Access makes identity-driven access decisions using signals about the user, device, and session for app access, which is the accurate description when a township network engineer assumes it is simply another perimeter firewall rule set. Unlike edge packet filters, Conditional Access evaluates cloud sign-in context after identity authentication and before authorizing sessions to Microsoft 365 apps. That identity-centric model is essential for modern municipal Zero Trust narratives on MS-900.
Conditional Access does not only filter packets at the city’s internet edge router and never evaluate identity. It is not exclusively a Microsoft Word add-in for grammar checking. It does not replace Exchange Online mailboxes with public folder replicas.
An exam caveat is that Conditional Access complements network controls; cities may still use firewalls, but Conditional Access is not the firewall renamed. Operationally, review an existing Conditional Access policy’s assignments and grant controls with the network engineer, show a sign-in log where device or location signals influenced the result, and document Conditional Access as an Entra ID access policy layer rather than as router ACL syntax.