
A security engineer needs to configure Microsoft Entra ID to enforce that all OAuth 2.0 applications accessing Azure OpenAI must use the authorization code flow with PKCE (Proof Key for Code Exchange) instead of the implicit flow. Which Entra ID configuration enforces this requirement?
Select an answer to reveal the explanation.
Short Explanation
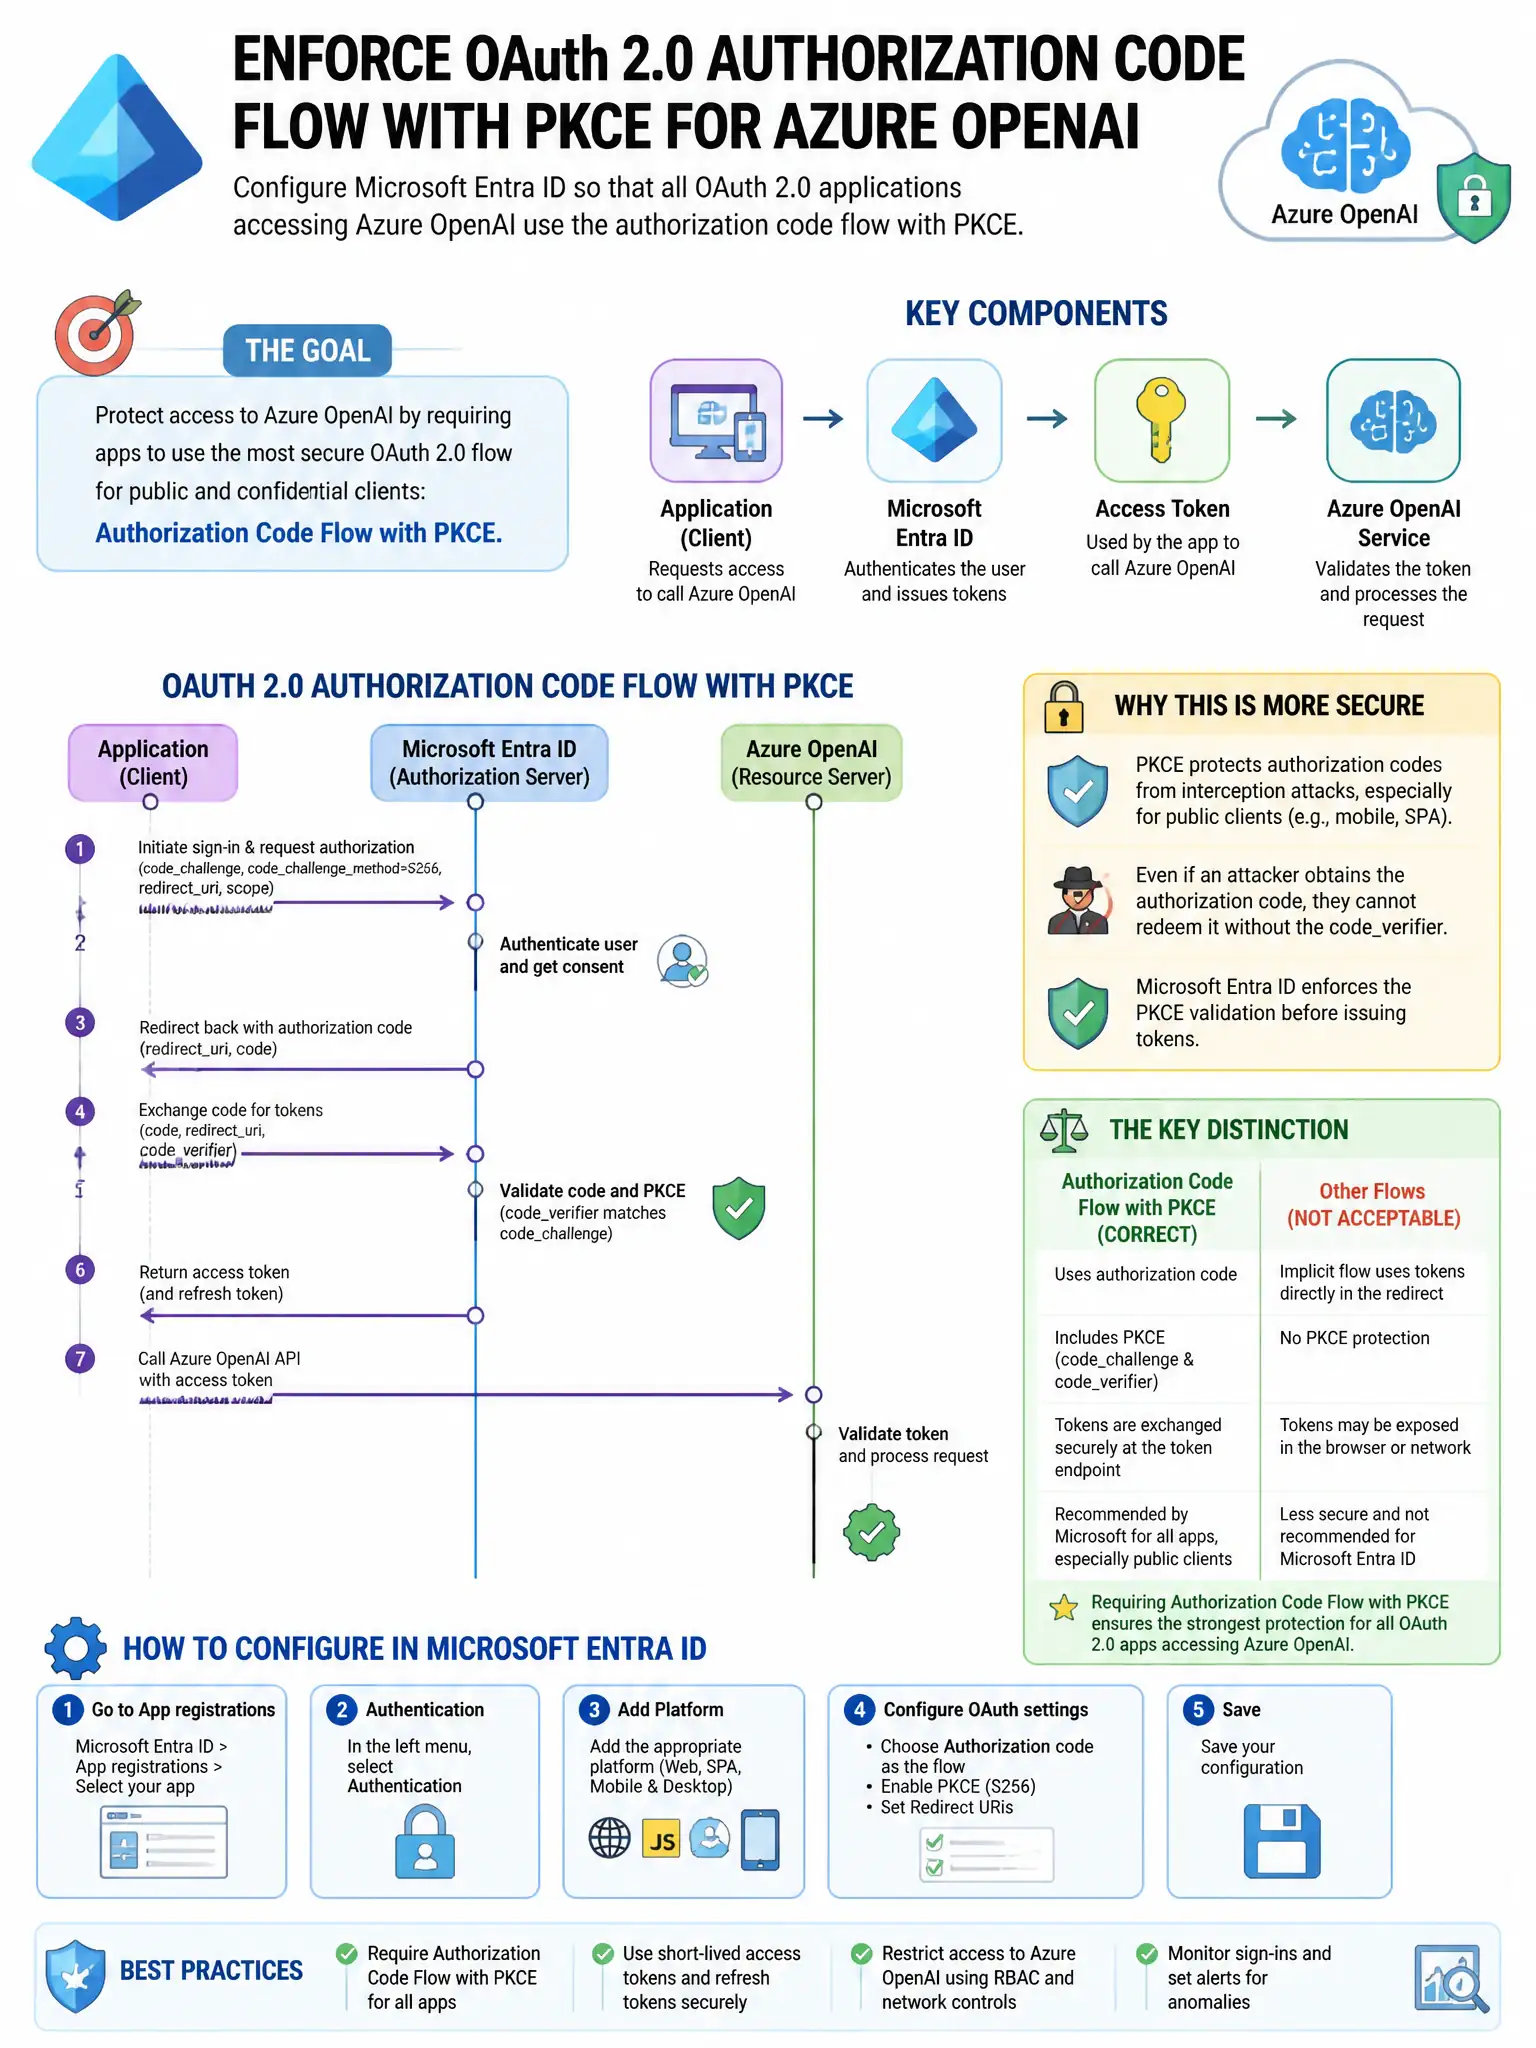
You disable the implicit grant flow on the Azure OpenAI app registration by unchecking ID tokens and access tokens under Authentication. That blocks the implicit flow and pushes clients to the authorization code flow, which you can combine with PKCE for public clients. It's the most direct way to enforce this in Entra ID.
Full Explanation
The correct configuration is the app registration setting that disables implicit grant by unchecking ID tokens and access tokens under Authentication > Implicit grant and hybrid flows. When implicit grant is disabled, client applications cannot use the implicit flow and must use authorization code flow, which can be combined with PKCE for public clients. This is the most direct enforcement mechanism. The conditional access policy requiring the authorization code flow for all applications accessing Azure OpenAI is incorrect because Conditional Access policies control access decisions such as MFA, device compliance, and location, but cannot enforce specific OAuth 2.0 grant types or require PKCE at the authentication protocol level. The managed identity setting to enable 'PKCE required' is incorrect because managed identities use client credentials flow for service-to-service authentication, not authorization code flow; PKCE is for user-facing flows. The app registration manifest setting that sets 'oauth2RequirePostResponse' to true is incorrect because it controls whether OAuth 2.0 responses use form_post, not whether PKCE is required.