
A security engineer needs to configure Microsoft Sentinel to detect when an Azure Machine Learning model training job accesses data outside its approved dataset scope. The engineer wants to detect when the training job service principal reads data from a storage account container not in the approved list. Which data source in Sentinel captures this activity?
Select an answer to reveal the explanation.
Short Explanation
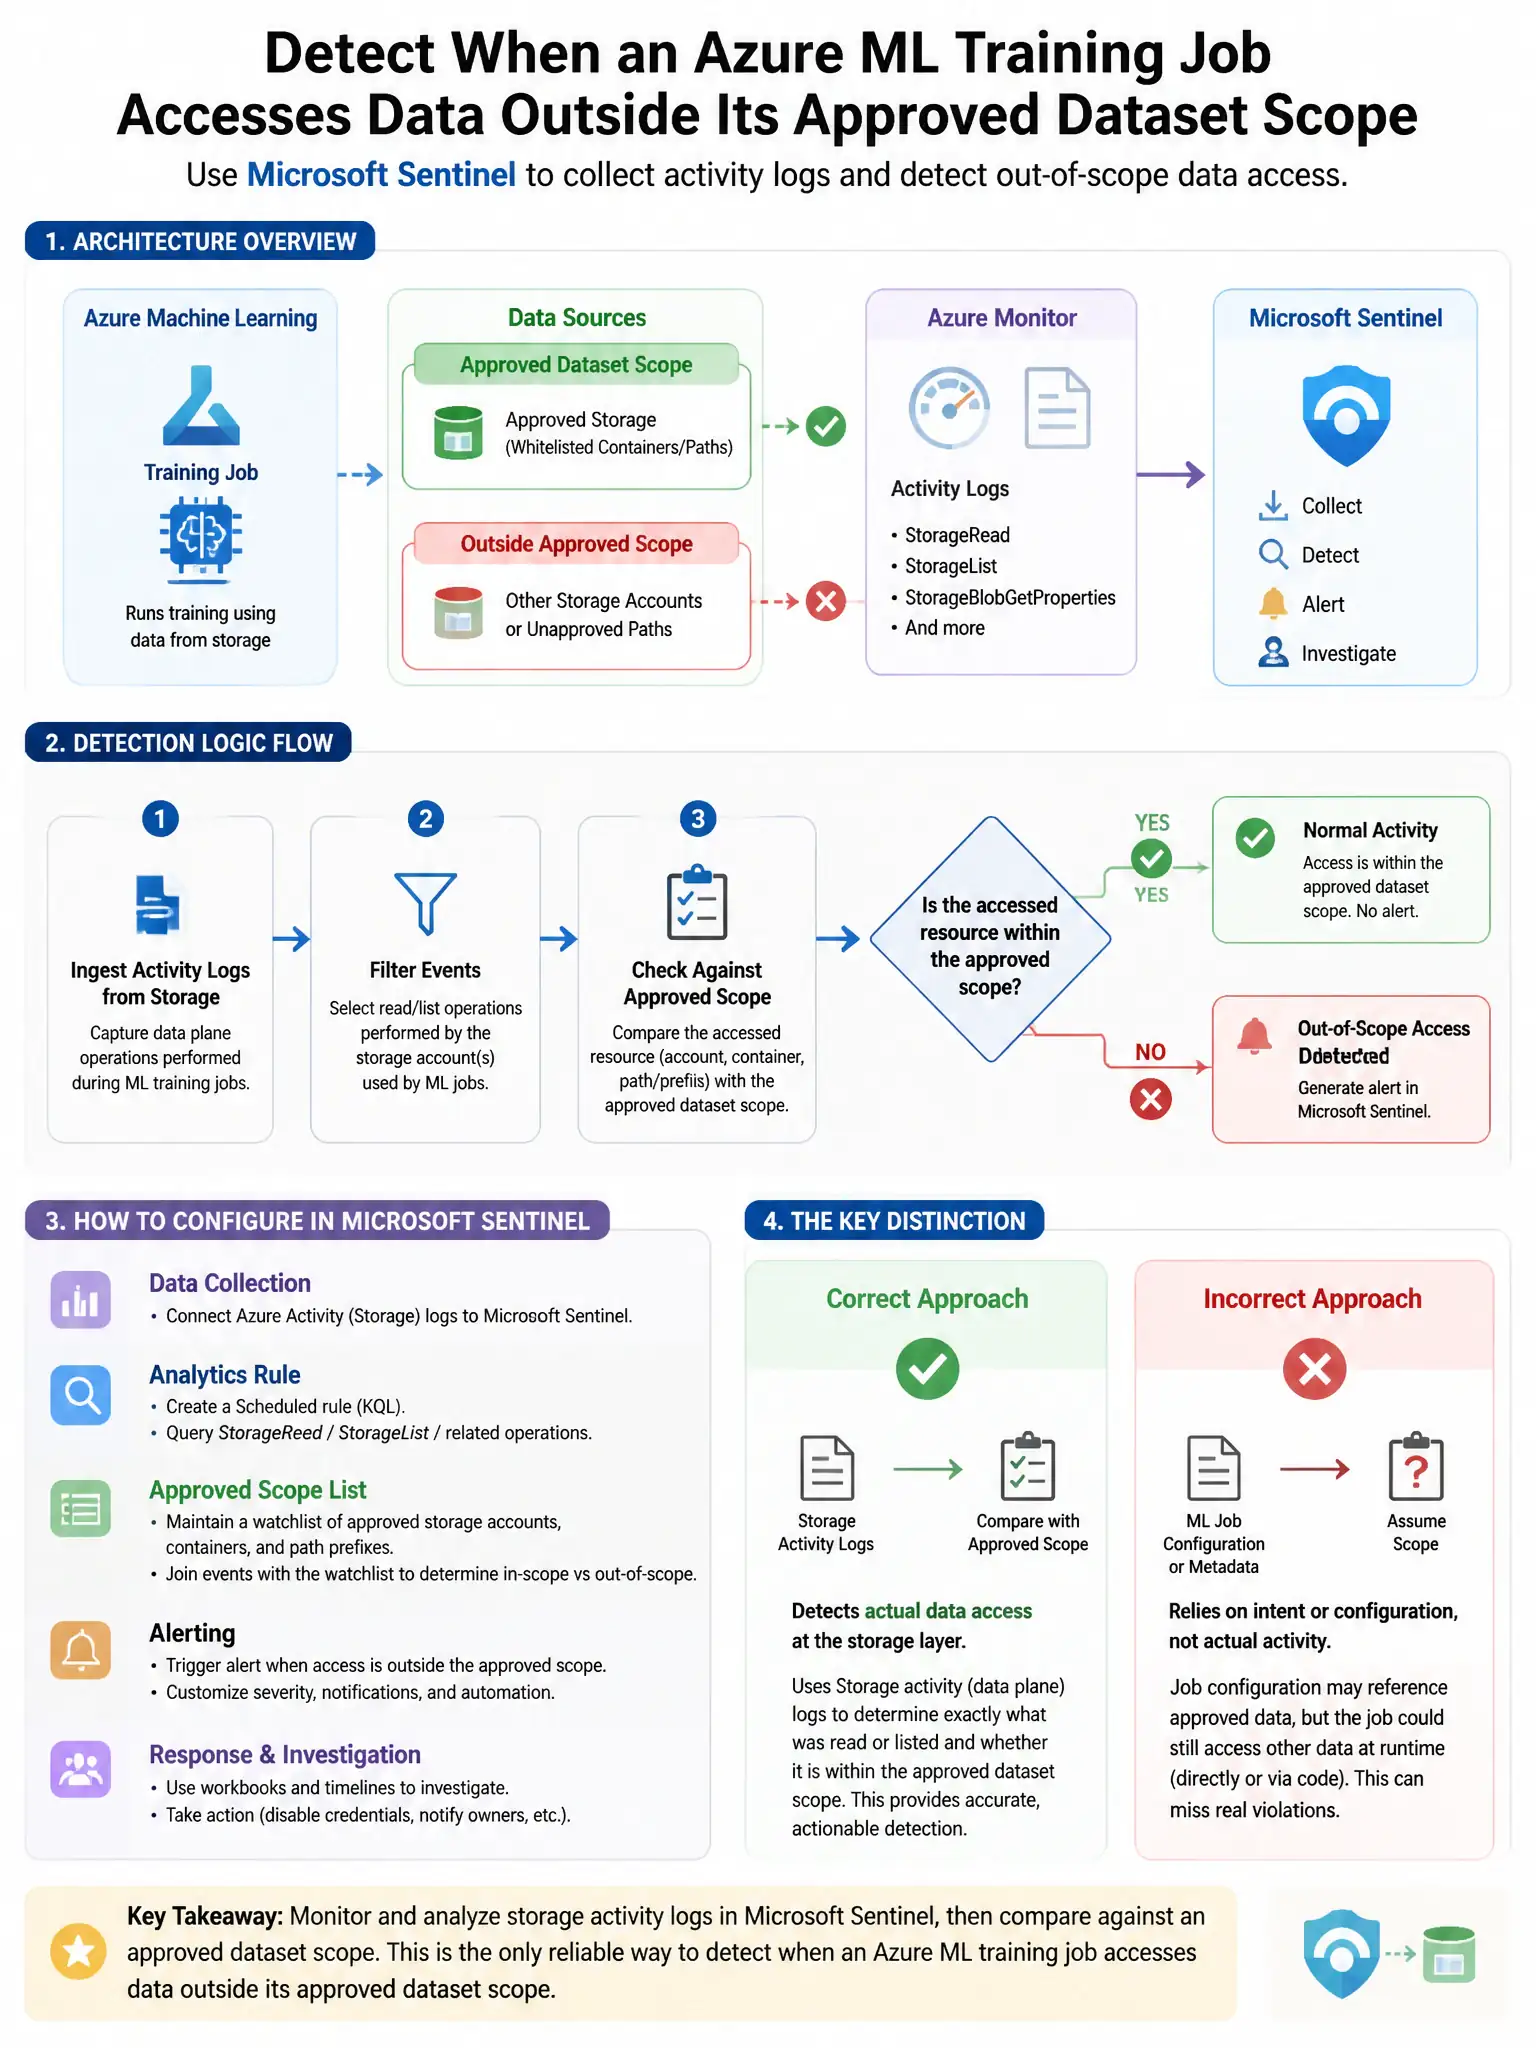
Here's the deal — you need the StorageBlobLogs table because it captures Azure Storage data plane reads, including which container was read and which service principal did it. That lets you spot a training job pulling data from a container outside the approved list.
Full Explanation
The StorageBlobLogs table (Azure Storage diagnostic logs) filtering for read operations by the training job service principal is correct because Azure Storage resource logs capture detailed data plane operations, including read operations on specific containers, along with the identity that performed the operation. By filtering for read operations by the training job's service principal or managed identity on containers not in the approved list, a Sentinel analytics rule can detect unauthorized data access during training. The AzureActivity table filtering for Microsoft.MachineLearningServices training job operations is incorrect because AzureActivity captures control plane operations, such as creating training jobs or stopping clusters, not data plane storage access operations. The AzureDiagnostics table with Category = 'AmlComputeClusterEvent' for training compute events is incorrect because AmlComputeClusterEvent logs capture compute cluster lifecycle events, such as scaling and node allocation, not the data operations performed during training jobs. The MicrosoftGraphActivityLogs table filtering for service principal data access is incorrect because MicrosoftGraphActivityLogs capture Microsoft Graph API calls, not Azure Storage data access operations.