
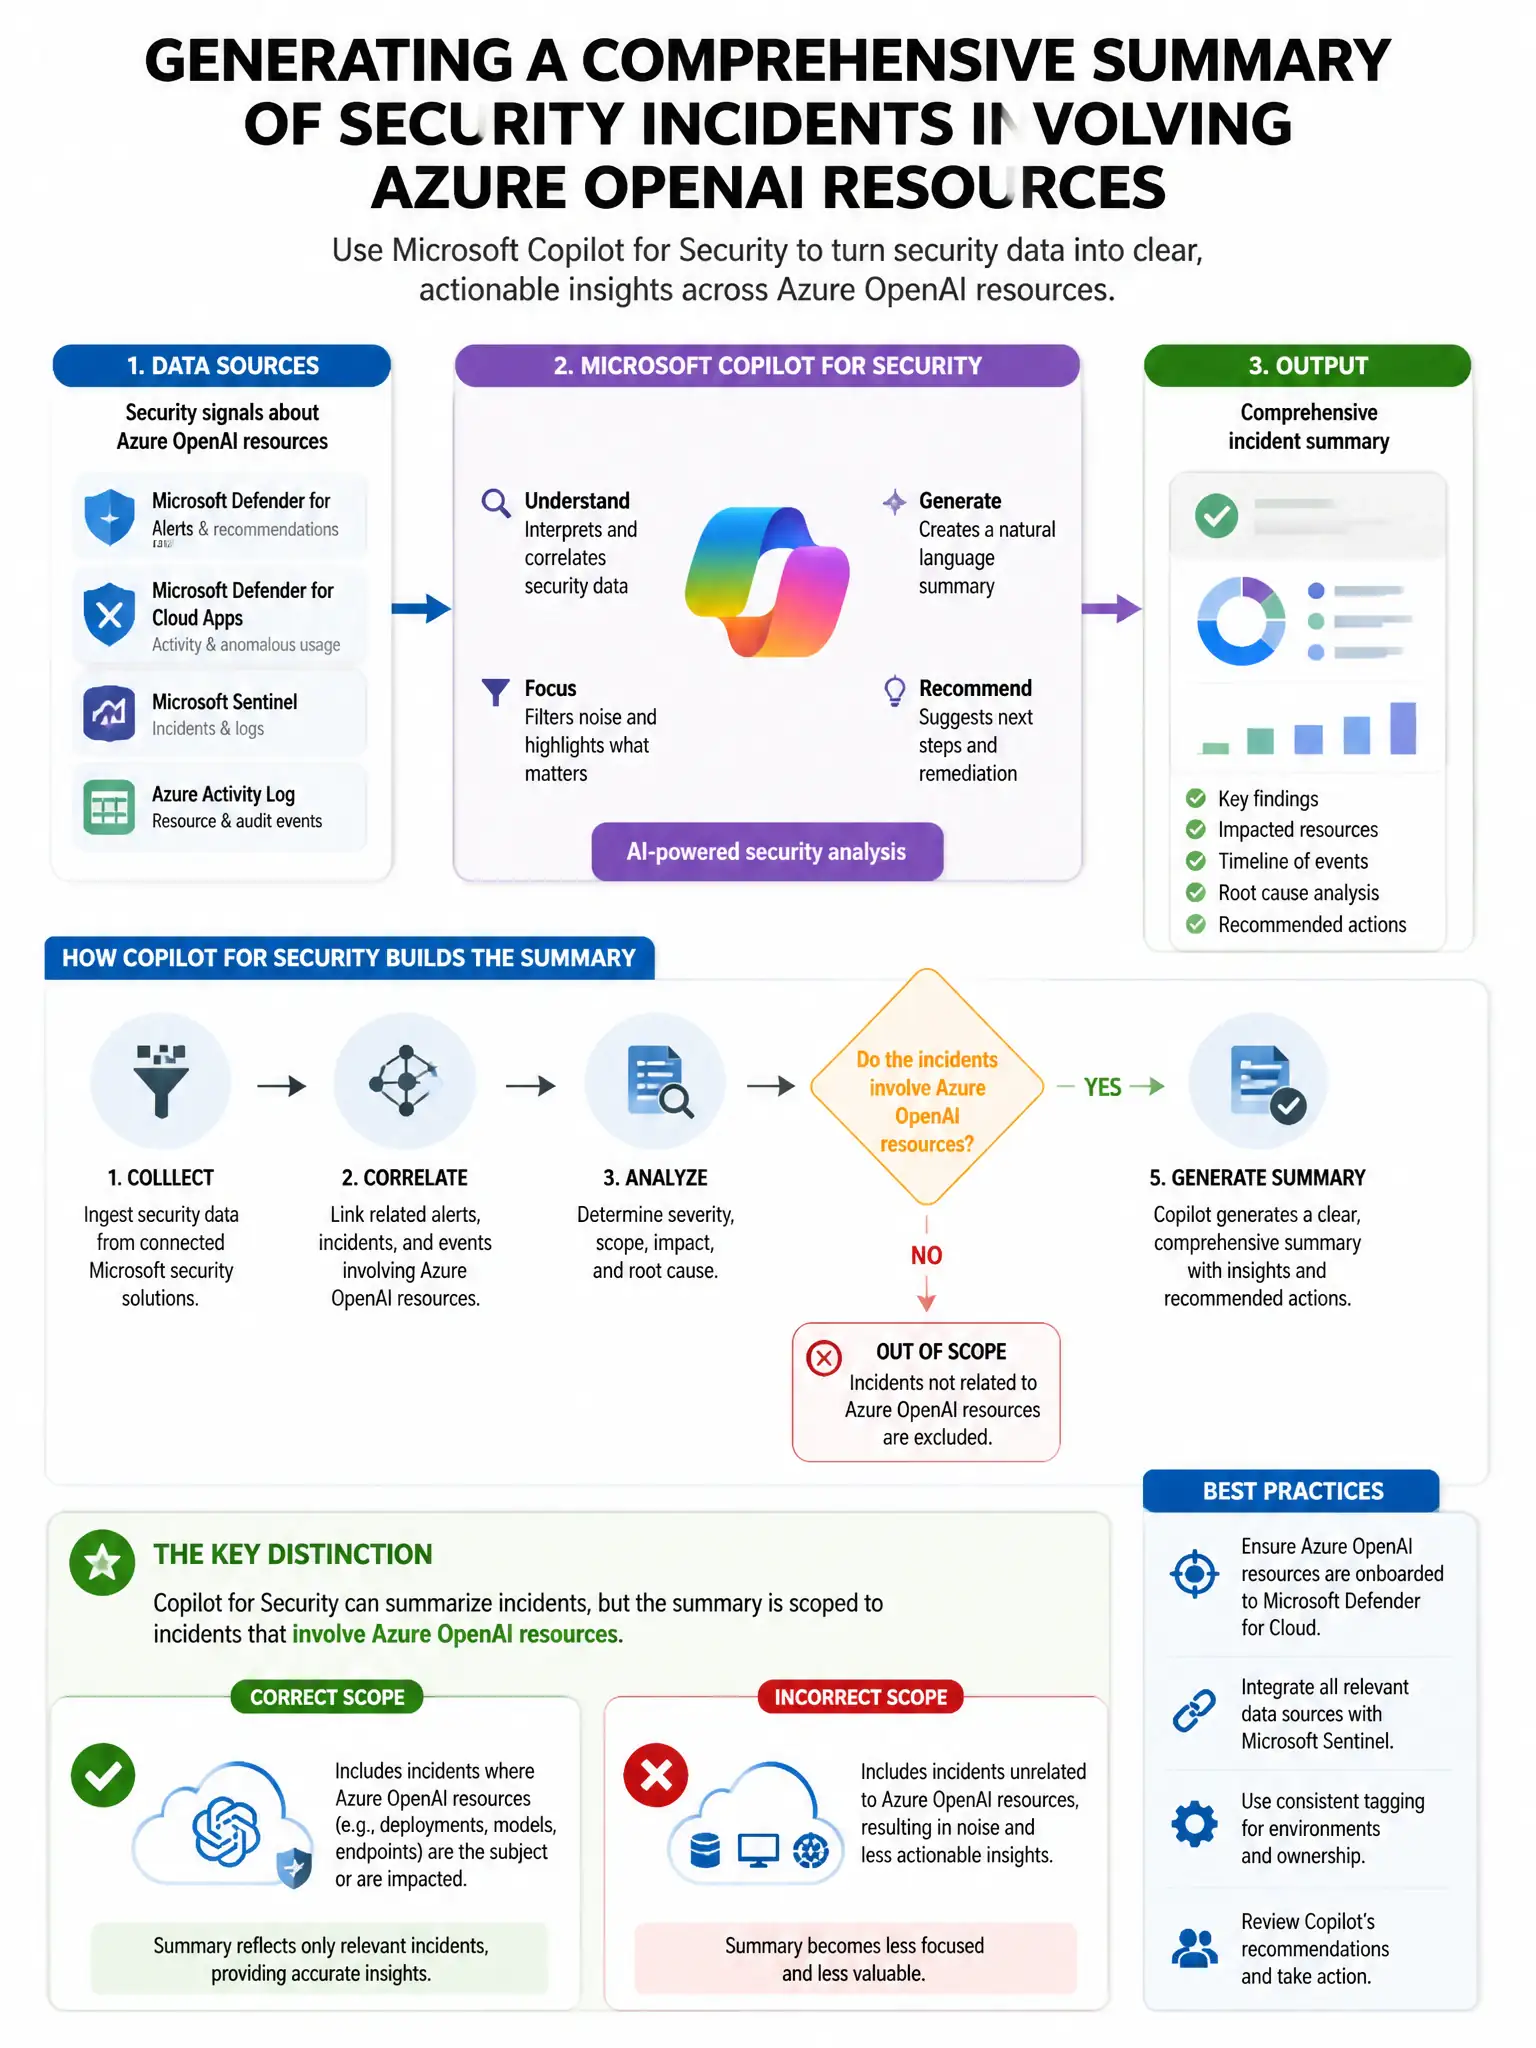
A company's security team wants to leverage Microsoft Copilot for Security to generate a comprehensive summary of all security incidents involving Azure OpenAI resources over the past 30 days, including common attack patterns and recommended mitigations. Which Copilot for Security feature is best suited for this retrospective analysis?
Select an answer to reveal the explanation.
Short Explanation
You want a custom prompt in Copilot for Security that asks the Sentinel plugin for Azure OpenAI incidents from the last 30 days, then summarizes patterns and recommends mitigations. That gives you flexible, cross-incident analysis instead of one-off reports.
Full Explanation
A custom prompt in Copilot for Security asking for a summary of Azure OpenAI-related incidents from the Sentinel plugin, specifying the 30-day timeframe, is correct because it instructs Copilot to use the Microsoft Sentinel plugin to query incidents related to Azure OpenAI resources over a 30-day window, then summarize patterns and recommend mitigations, leveraging Copilot's natural language reasoning over structured security data. This custom prompt approach is the most flexible and comprehensive for a retrospective multi-incident analysis. The Incident Investigation promptbook applied to each individual incident sequentially is incorrect because the Incident Investigation promptbook analyzes individual incidents one at a time; applying it sequentially to all incidents would be inefficient and would not produce a consolidated cross-incident pattern analysis. The Threat Intelligence Summary promptbook to generate a threat landscape report is incorrect because the Threat Intelligence Summary promptbook generates intelligence about known threat actors and campaigns based on global threat intelligence, not a retrospective analysis of the organization's specific incidents. The Vulnerability Impact Assessment promptbook to identify known CVEs in Azure OpenAI is incorrect because Vulnerability Impact Assessment focuses on CVE-based vulnerability analysis, not incident pattern summarization.