
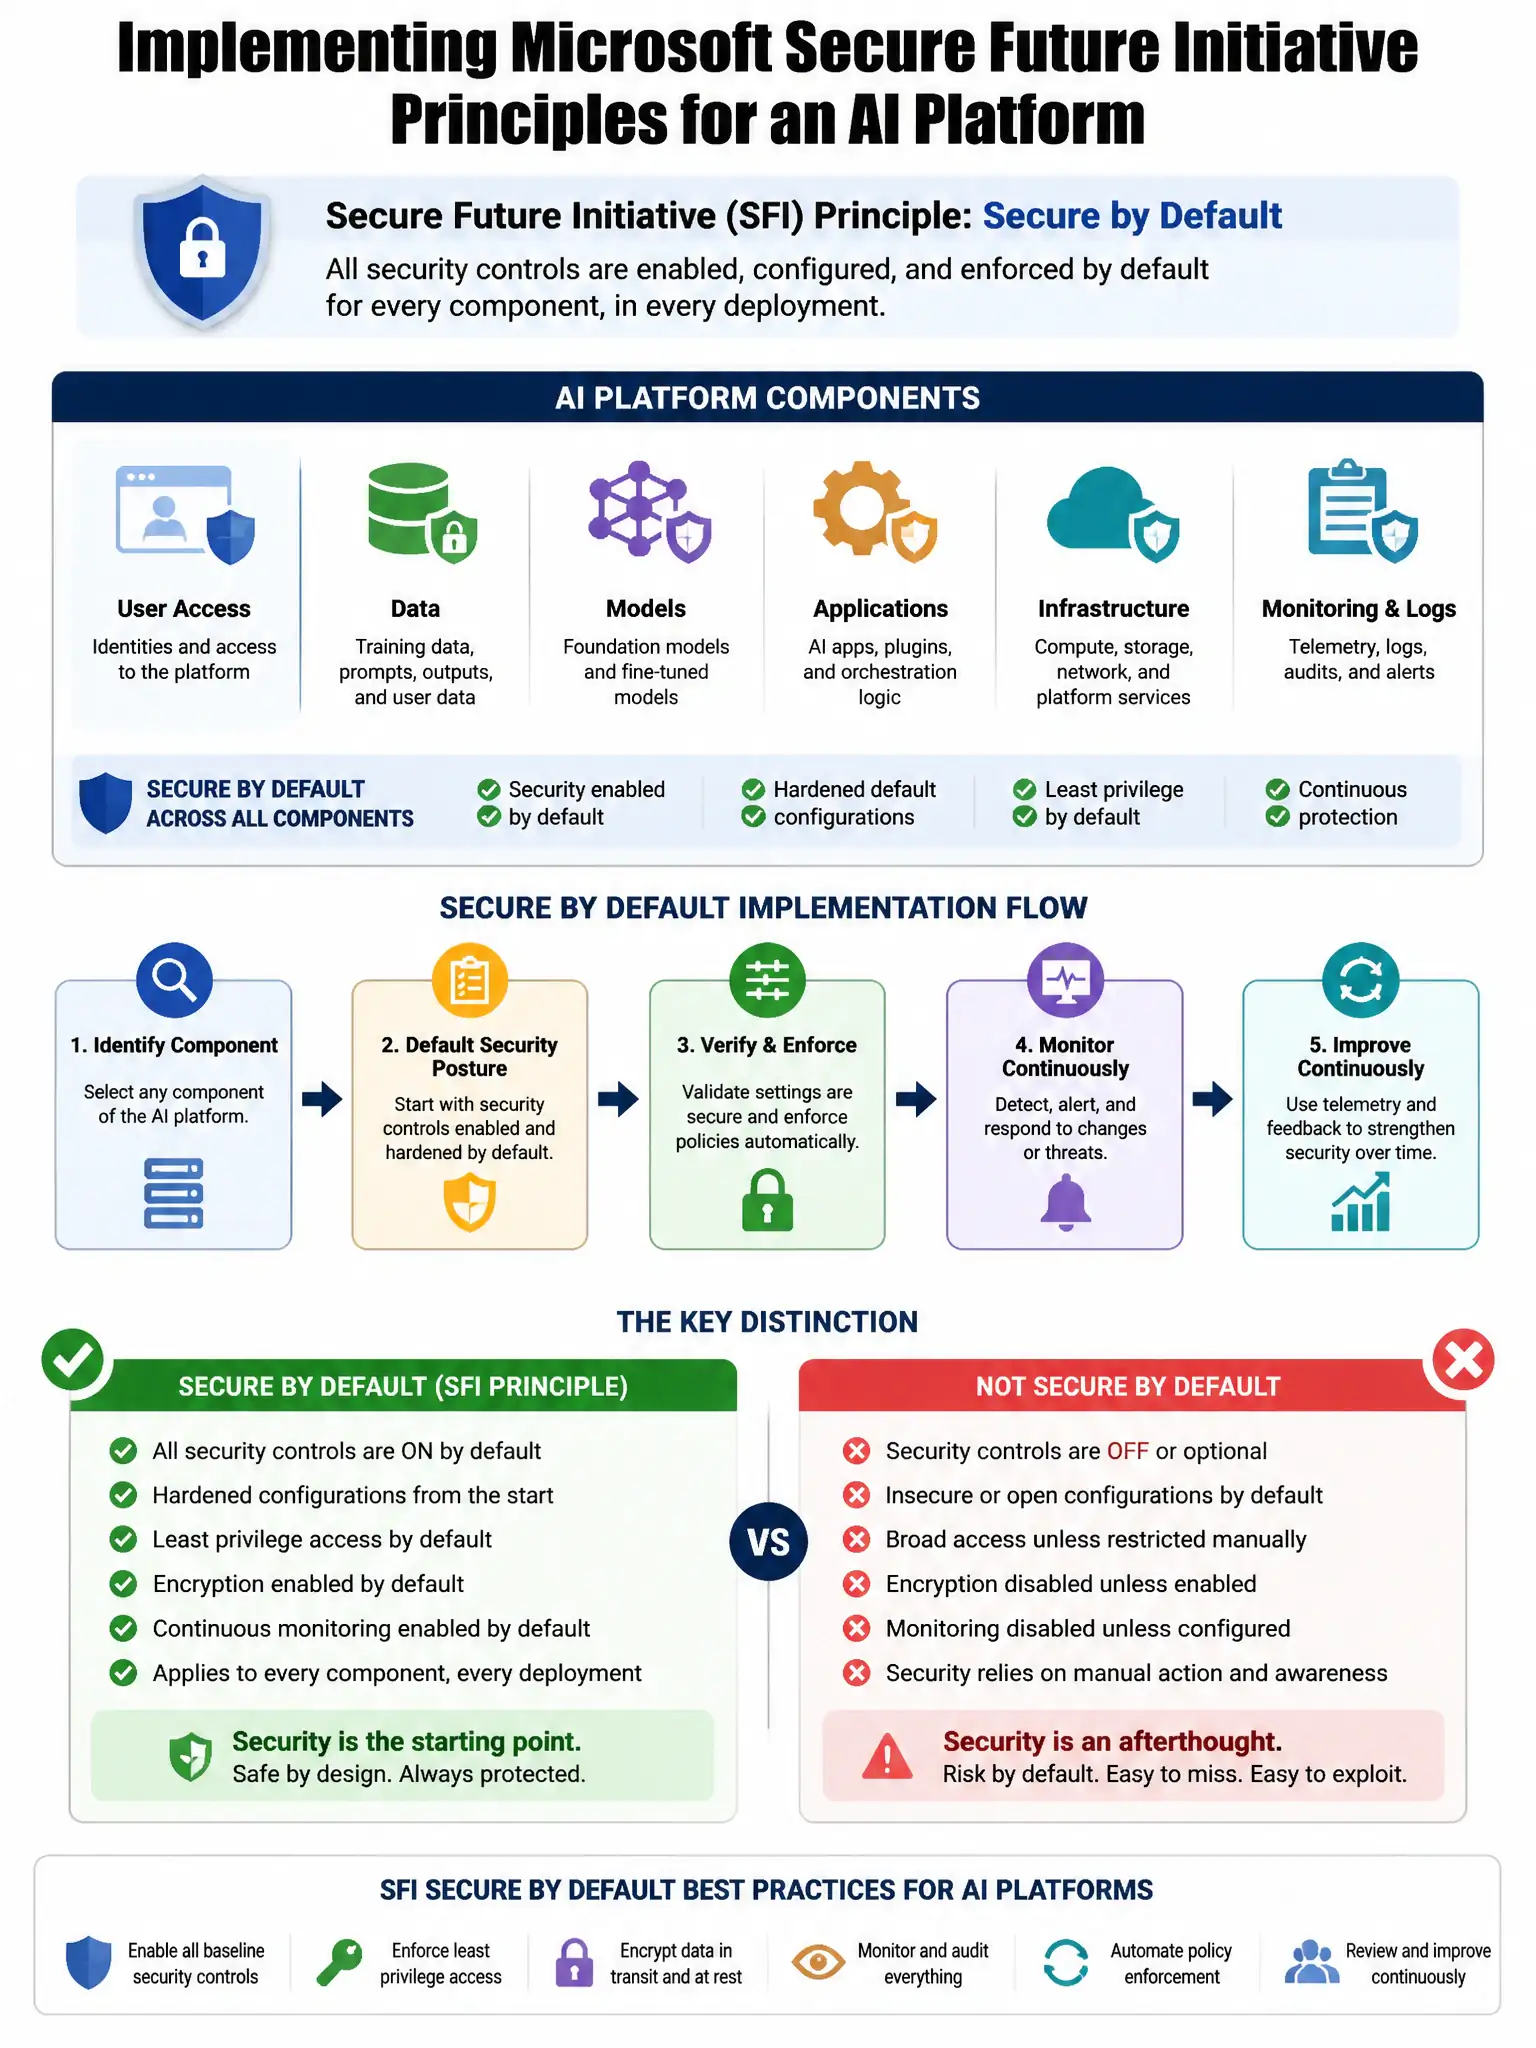
A security engineer is implementing Microsoft's Secure Future Initiative (SFI) principles for an AI platform. The SFI principle of 'Secure by Default' requires that all security controls are enabled automatically without customer action. For Azure OpenAI, which control is an example of a 'Secure by Default' implementation?
Select an answer to reveal the explanation.
Short Explanation
Here's the deal — you get Secure by Default when Azure OpenAI content filtering is already on for every model deployment, with baseline filters for violence, hate speech, sexual content, and self-harm. You don't have to turn it on yourself.
Full Explanation
The correct control is Azure OpenAI content filtering being enabled by default on all model deployments with baseline category filters, implemented as severity filters for harm categories (violence, hate speech, sexual content, self-harm) active. Customers do not need to take any action to enable this protection; it is the default state, which matches Secure by Default. The private endpoint control is incorrect because private endpoints for Azure OpenAI are not enabled by default; customers must manually configure them and disable public network access. The customer-managed key encryption control is incorrect because customer-managed key encryption is an optional configuration that customers must explicitly set up; Microsoft-managed keys are the default. The Microsoft Defender for AI control is incorrect because Microsoft Defender for AI requires customers to explicitly enable the plan in Defender for Cloud; it is not automatically enabled or free by default.