
A security team is implementing the MITRE ATLAS (Adversarial Threat Landscape for Artificial-Intelligence Systems) framework to categorize AI-specific threats to their Azure AI platform. Which MITRE ATLAS tactic corresponds to an attacker querying a deployed model with many inputs to understand its decision boundary and reconstruct proprietary training data?
Select an answer to reveal the explanation.
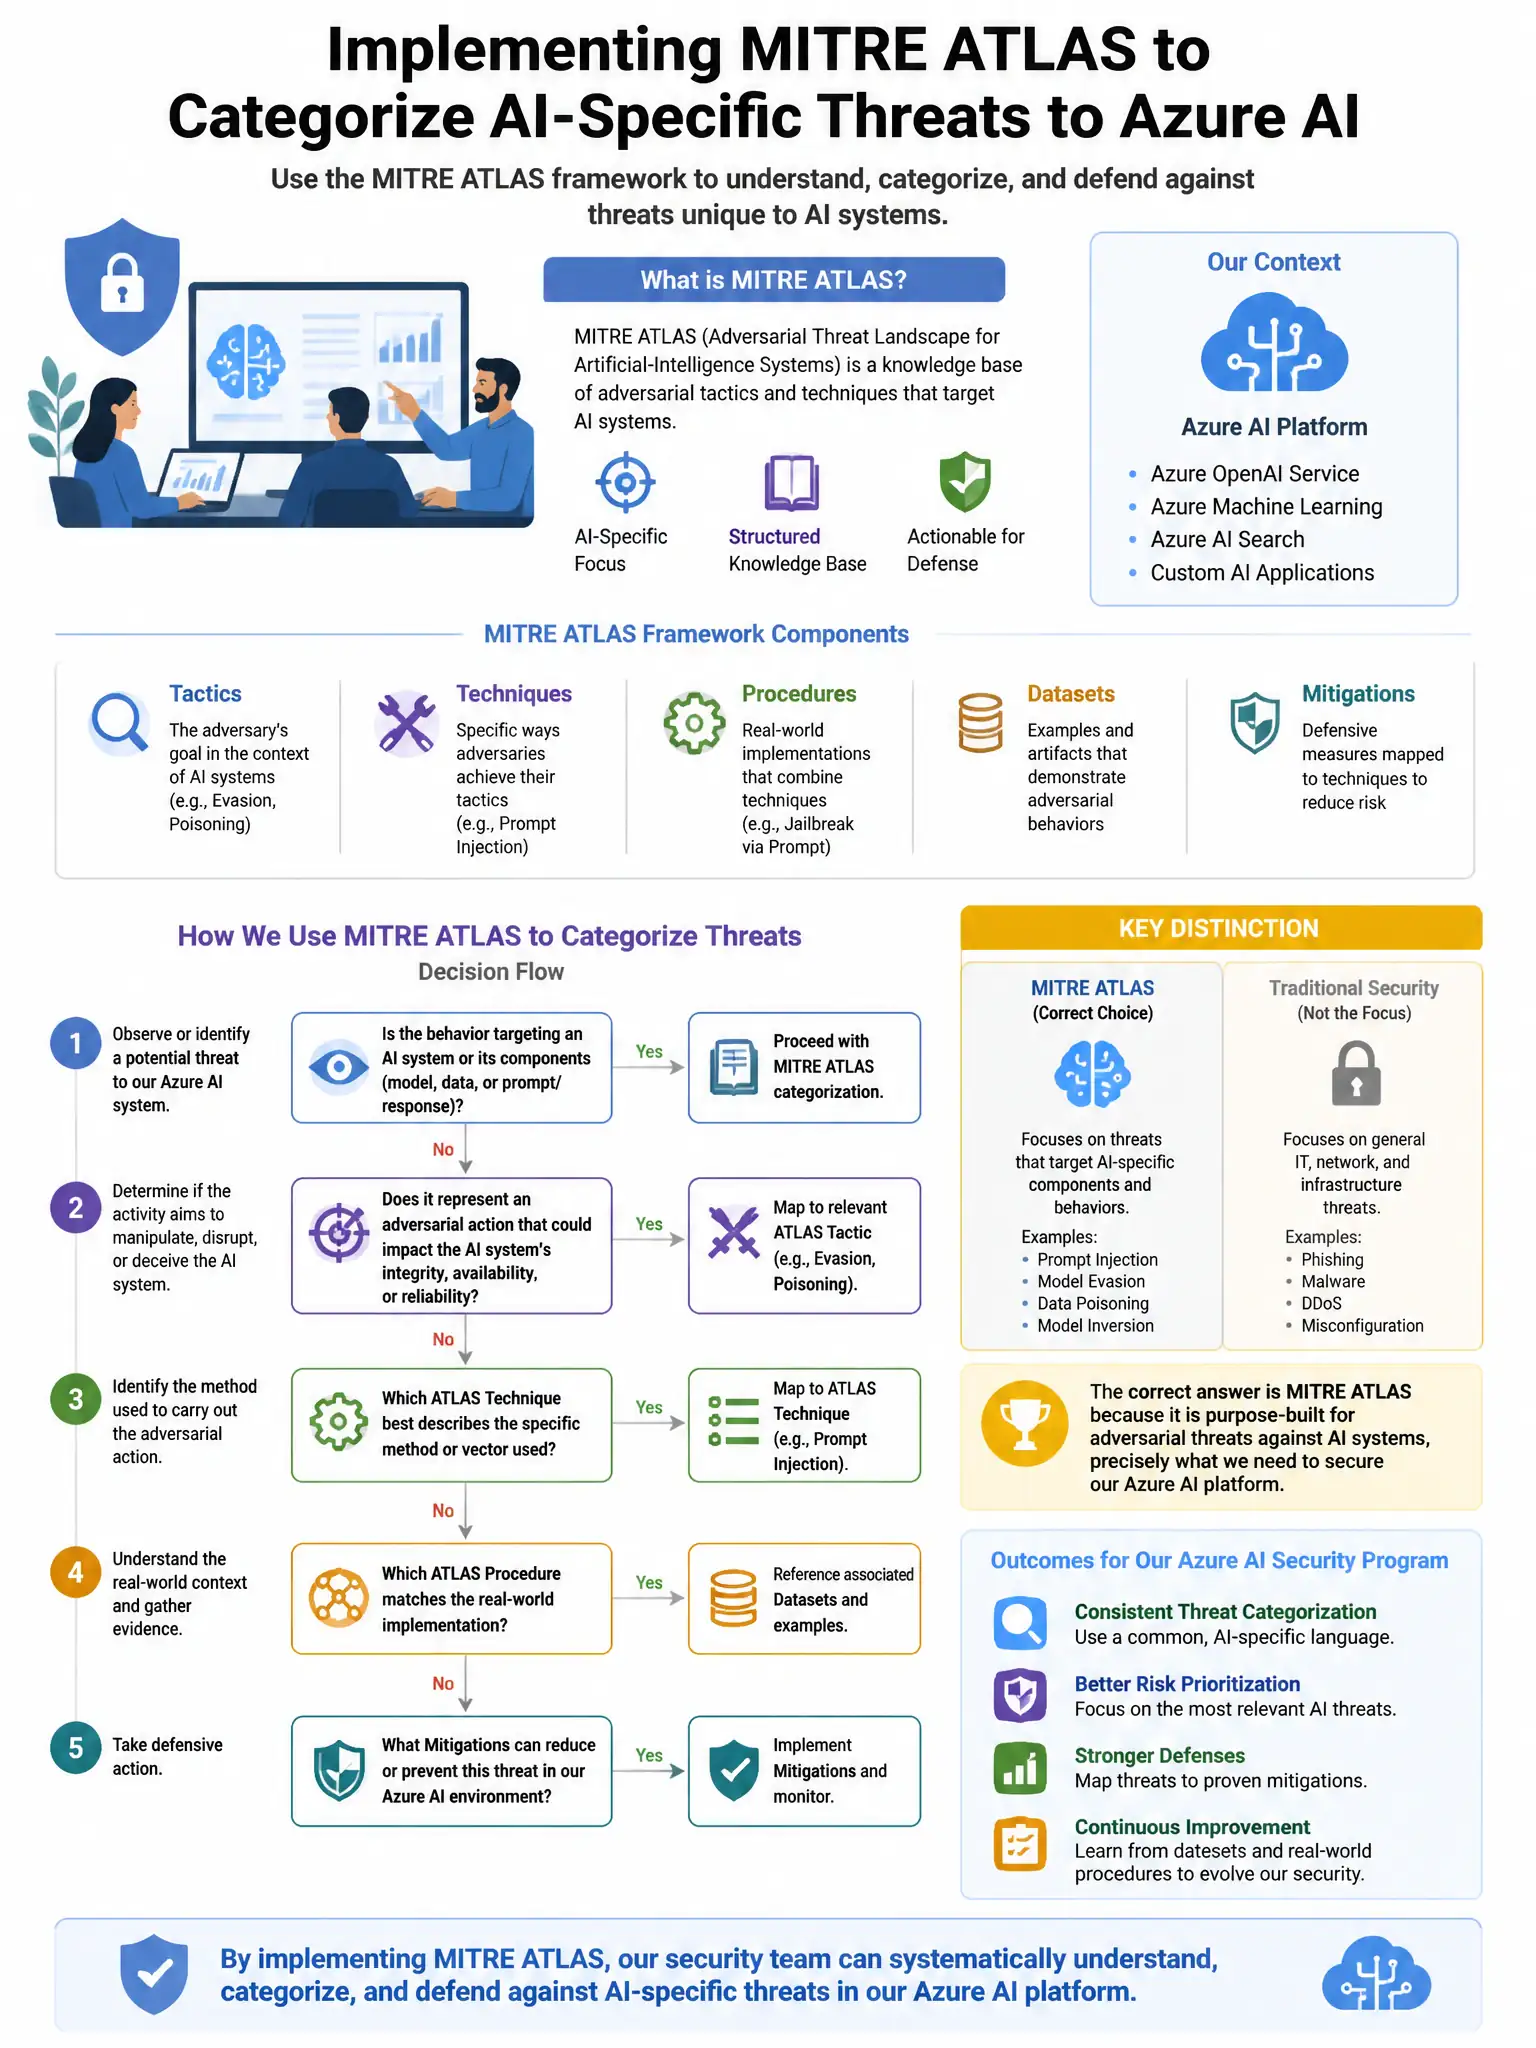
Short Explanation
Here's the deal — you pick the Exfiltration answer because MITRE ATLAS treats repeated model queries that reconstruct training data or steal model behavior as extracting proprietary information. You're not just accessing the model—you're pulling confidential data out of it.
Full Explanation
The Exfiltration answer is correct because, in the MITRE ATLAS framework, systematically querying a model to reconstruct training data through model inversion or to replicate the model's functionality through model extraction or model stealing falls under the Exfiltration tactic. The attacker uses repeated API queries to extract proprietary information, such as training data characteristics or model behavior, from the deployed AI system. The Initial Access answer is incorrect because Initial Access in MITRE ATLAS refers to gaining access to the AI system or pipeline, not the specific attack technique of model querying for data reconstruction. The ML Model Access answer is incorrect because ML Model Access is a prerequisite stage, meaning the attacker has gained the ability to query the model, but it is not the specific attack of using that access to reconstruct training data. The Impact answer is incorrect because Impact in MITRE ATLAS covers degrading model accuracy, causing harmful outputs, or denial of service through adversarial inputs, not data exfiltration through model queries.