
A security team needs to implement Microsoft Purview Insider Risk Management to detect when data scientists are exfiltrating AI model training data before departing the company. Which insider risk policy template is most appropriate, and what triggering event should be configured?
Select an answer to reveal the explanation.
Short Explanation
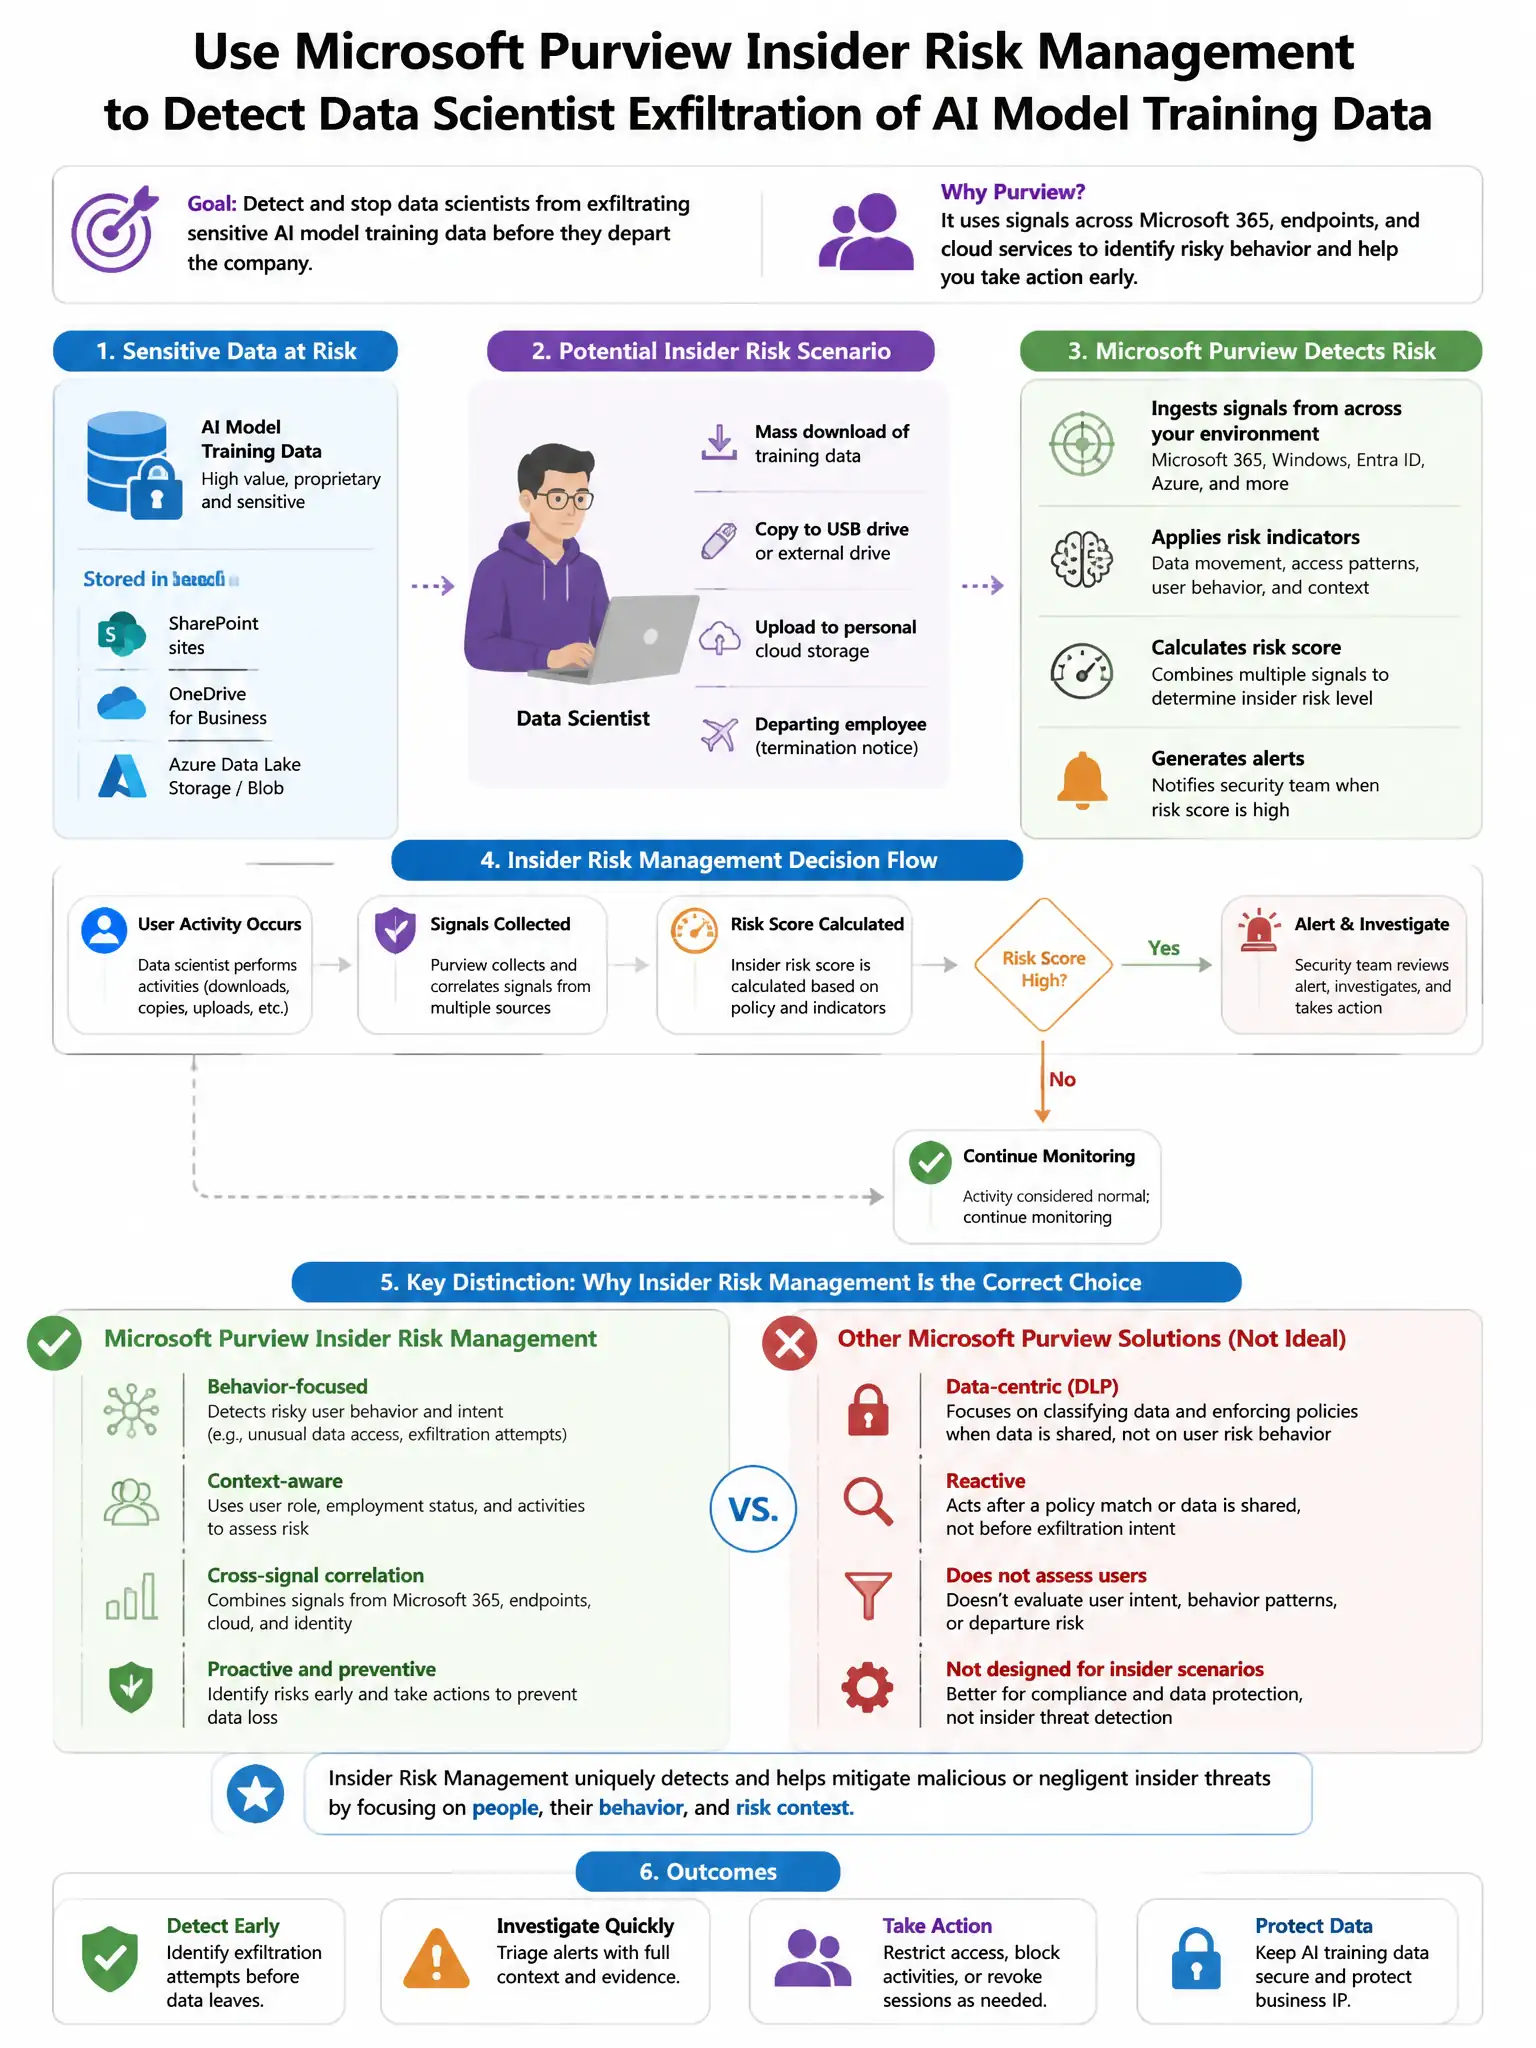
You want the 'Data theft by departing users' template because it's built for employees who are leaving and may steal data. Use the HR connector's resignation event to trigger monitoring during the notice period.
Full Explanation
The 'Data theft by departing users' policy template with an HR connector-based resignation event is correct because Microsoft Purview Insider Risk Management uses this template specifically for employees who are planning to leave and may exfiltrate data. The HR connector integration enables resignation or termination events from the HR system to serve as triggering events, which activates risk monitoring for the specific employee during their notice period. In this scenario, that triggering event aligns directly with detecting data scientists who may be exfiltrating AI model training data before departing. The 'General data leaks' policy template with anomalous file download activity is incorrect because it monitors for broad data leak patterns without a departure-specific triggering event, making it less targeted for the departing employee scenario. The 'Security policy violations by departing users' policy template with device compliance failure as the triggering event is incorrect because the security policy violations template focuses on security control bypasses, not data exfiltration patterns. The 'Risky browser usage' policy template with cloud storage upload as the triggering event is incorrect because the risky browser usage template focuses on web browsing behaviors, not file download and exfiltration activity related to AI model data.