
A security engineer is implementing the Microsoft Cloud Security Benchmark (MCSB) controls for an Azure AI platform deployment. The MCSB control 'IM-1: Use centralized identity and authentication system' requires all service-to-service authentication to use Entra ID. A legacy AI service component uses username/password authentication with a local account. Which migration path aligns with the MCSB IM-1 control?
Select an answer to reveal the explanation.
Short Explanation
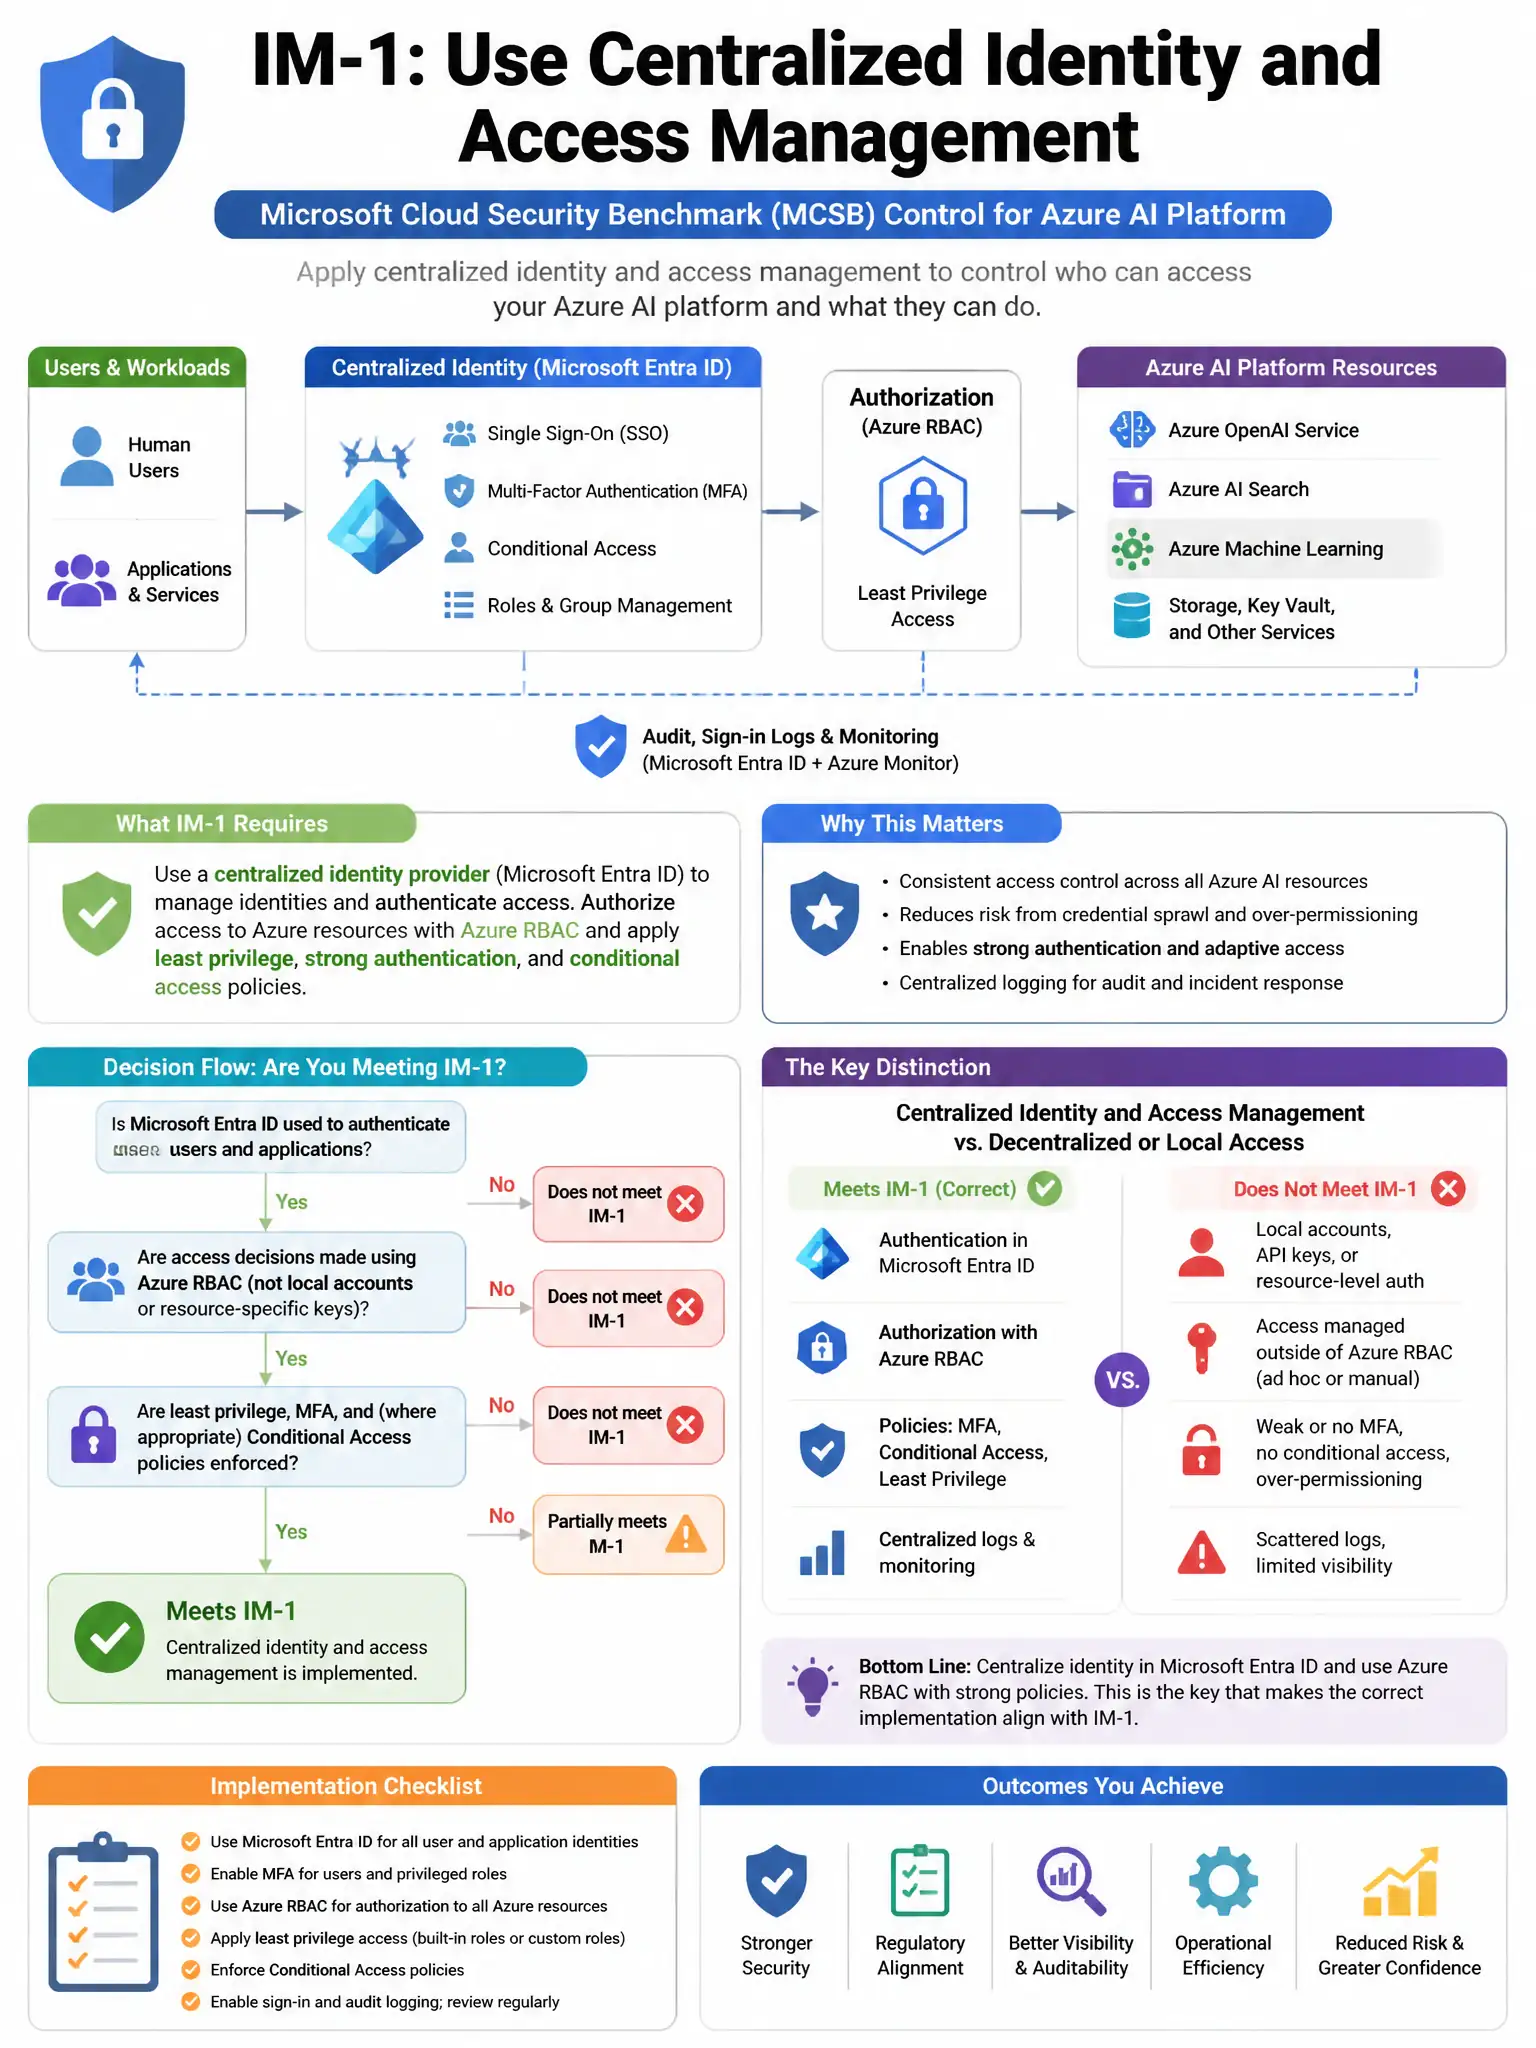
Here's the deal — you need to move the legacy service to Entra ID authentication. A system-assigned managed identity lets the calling service authenticate without secrets, and the target service validates Entra ID tokens, which satisfies MCSB IM-1.
Full Explanation
The correct migration path is to migrate authentication to use a system-assigned managed identity for the calling service and update the target service to accept Entra ID tokens. The MCSB IM-1 control specifically requires using Microsoft Entra ID as the centralized identity system for all authentication, eliminating local accounts and passwords. With a system-assigned managed identity, the calling service authenticates using its Entra ID identity and no credentials are needed, while the target service validates Entra ID tokens, fully aligning with IM-1. Storing the username and password in Azure Key Vault and accessing them via the Key Vault SDK is incorrect because it's a secrets management improvement but does not migrate to Entra ID centralized authentication as required by IM-1; it still uses username/password. Creating a service account in Entra ID with a complex password stored in Key Vault and rotating the password every 90 days is incorrect because it's still password-based authentication; managed identity, which is non-secret-based, is the MCSB IM-1 preferred approach. Implementing certificate-based authentication using a certificate stored in Azure Key Vault instead of username/password is incorrect because certificate-based authentication is more secure than passwords but still does not align with the IM-1 requirement for Entra ID centralized identity; managed identity is preferred.