
A security team needs to implement Microsoft Entra Permissions Management (CIEM) to identify and remediate over-privileged AI service identities across their Azure subscriptions. After a permissions discovery scan, the team finds several managed identities with unused permissions. Which Permissions Management action remediates over-privileged identities while maintaining operational continuity?
Select an answer to reveal the explanation.
Short Explanation
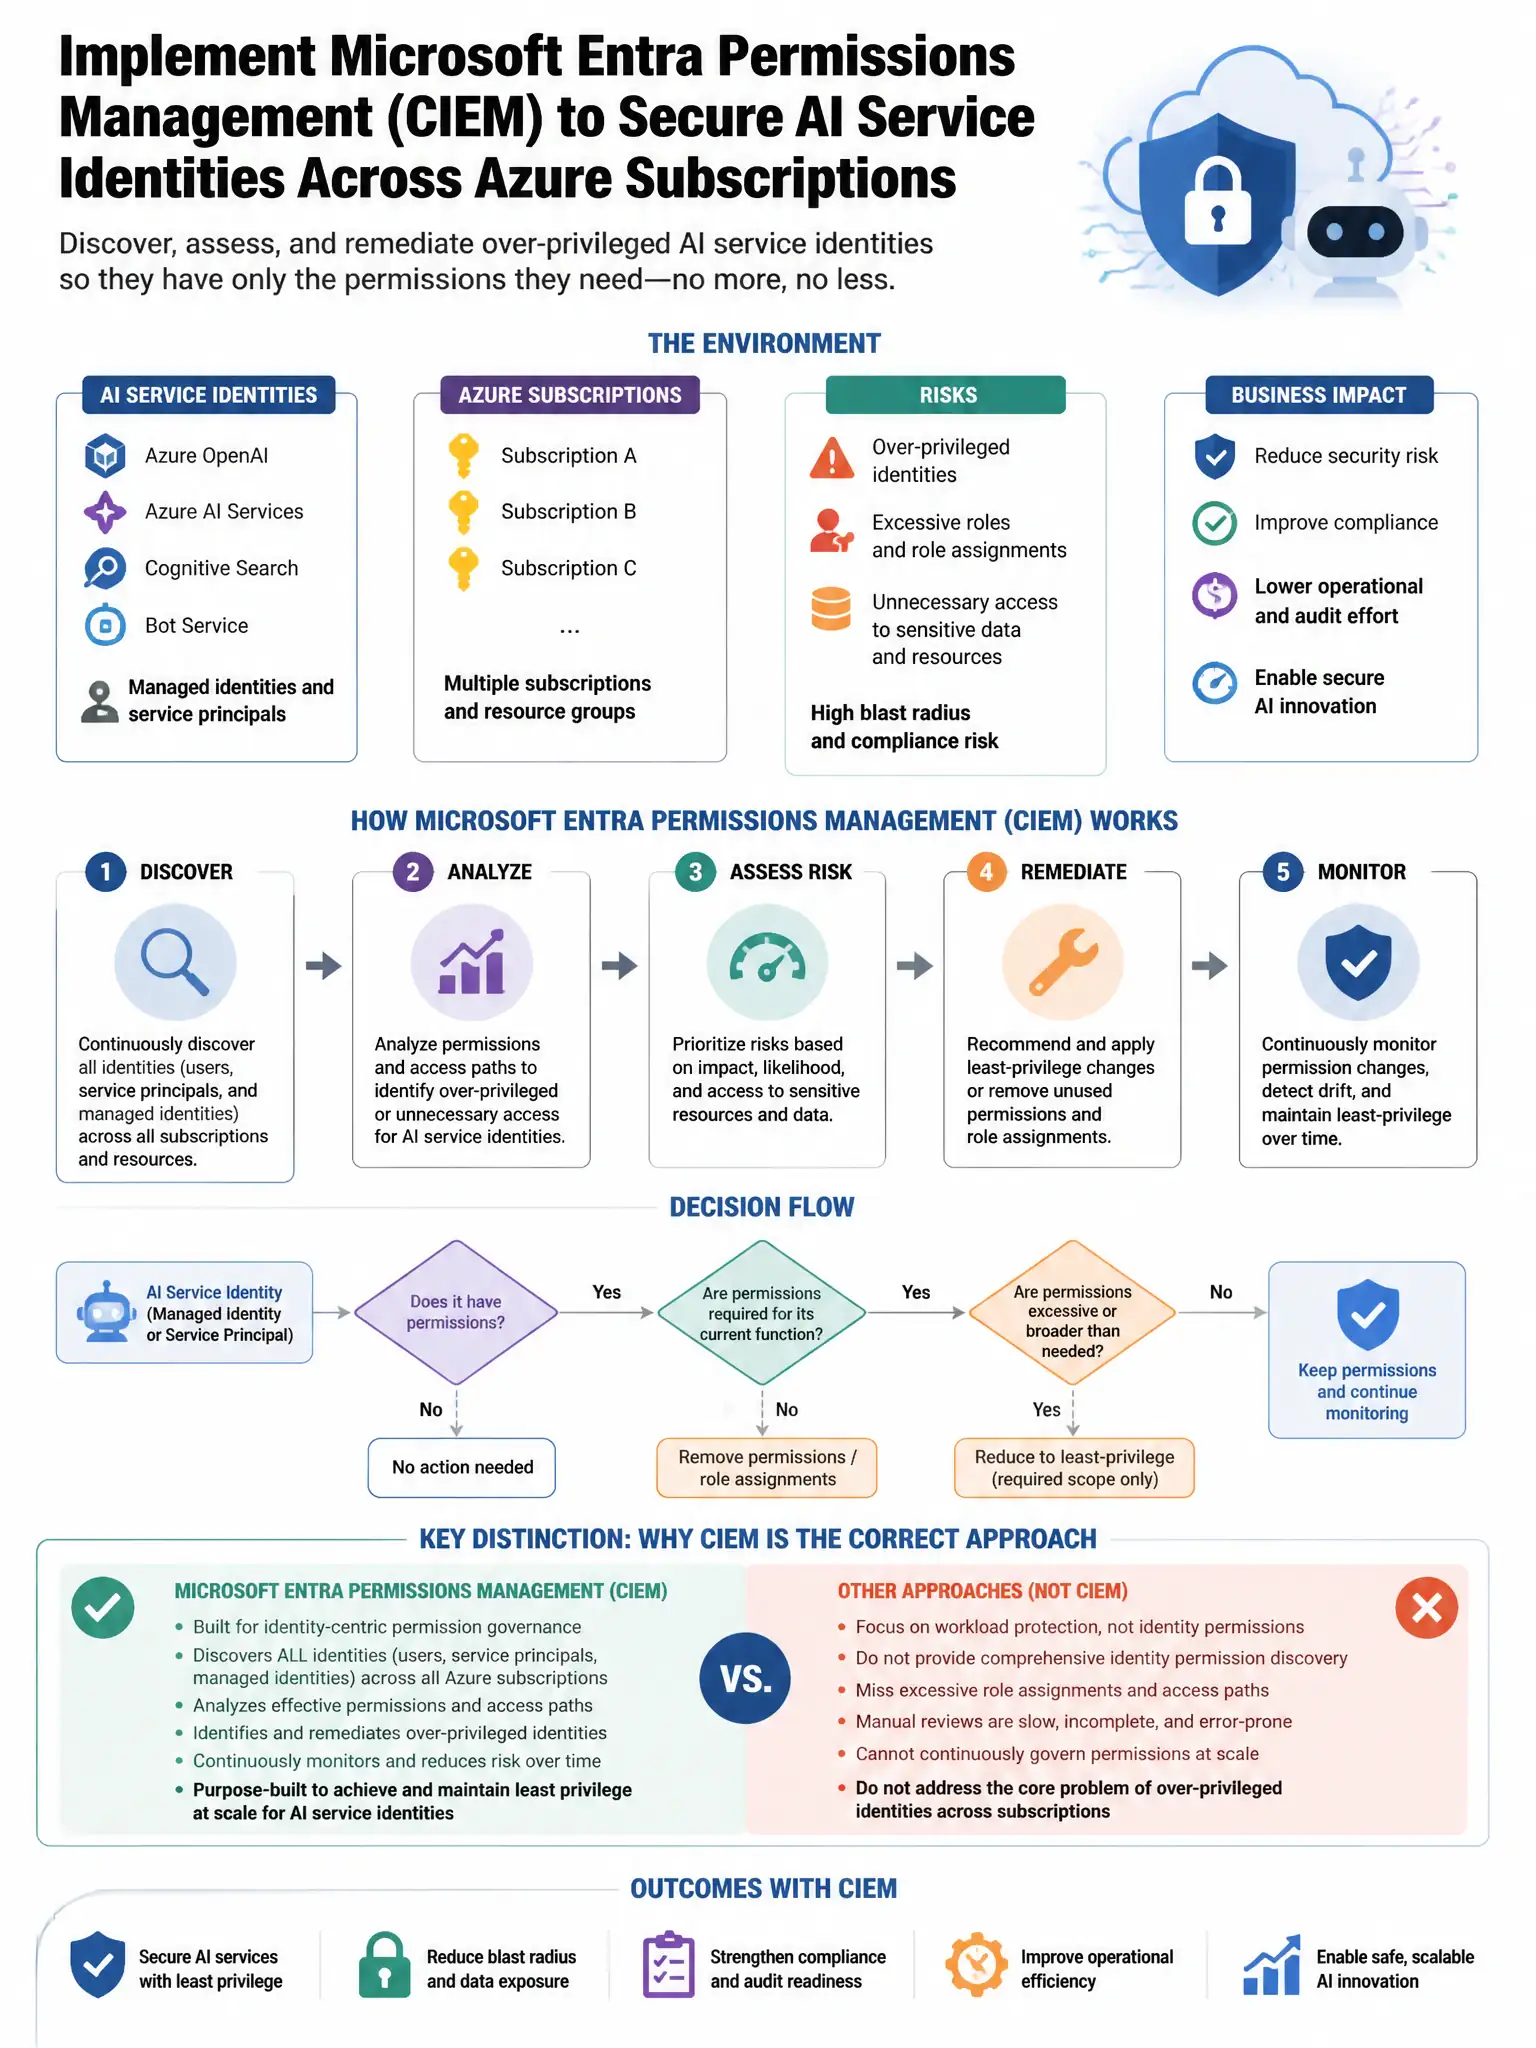
You should use the Permissions Management right-size feature to generate and apply right-sized role assignments based on actual usage data. It removes unused permissions while keeping the permissions the identity has actually used, so operations keep running.
Full Explanation
The correct action is to use the Permissions Management right-size feature to generate and apply right-sized role assignments based on actual usage data. Microsoft Entra Permissions Management, also known as CIEM, collects and analyzes real permission usage data, then provides right-sizing recommendations that assign only the permissions that have actually been used by the identity. This approach maintains operational continuity because previously used permissions are preserved while unused over-privileges are removed. Deleting the over-privileged managed identities and recreating them with minimum required permissions is not the best remediation because it risks operational disruption if any granted permissions are actually in use, even if only infrequently. Applying a Conditional Access policy restricting the managed identities to specific resource scopes is incorrect because Conditional Access policies control authentication conditions and cannot restrict specific resource-level permissions granted through Azure RBAC. Enabling PIM for managed identity role assignments to require activation before permission use is also incorrect because PIM for managed identity role assignments is not a generally available feature; PIM applies to human user role activations, and even if it were available, it would change the operational model rather than right-sizing the permissions themselves.