
A security engineer is implementing secure AI development practices using Azure DevOps. The organization requires that AI model training code must be scanned for hardcoded credentials and sensitive data before merging to the main branch. Which Azure DevOps feature provides this capability natively?
Select an answer to reveal the explanation.
Short Explanation
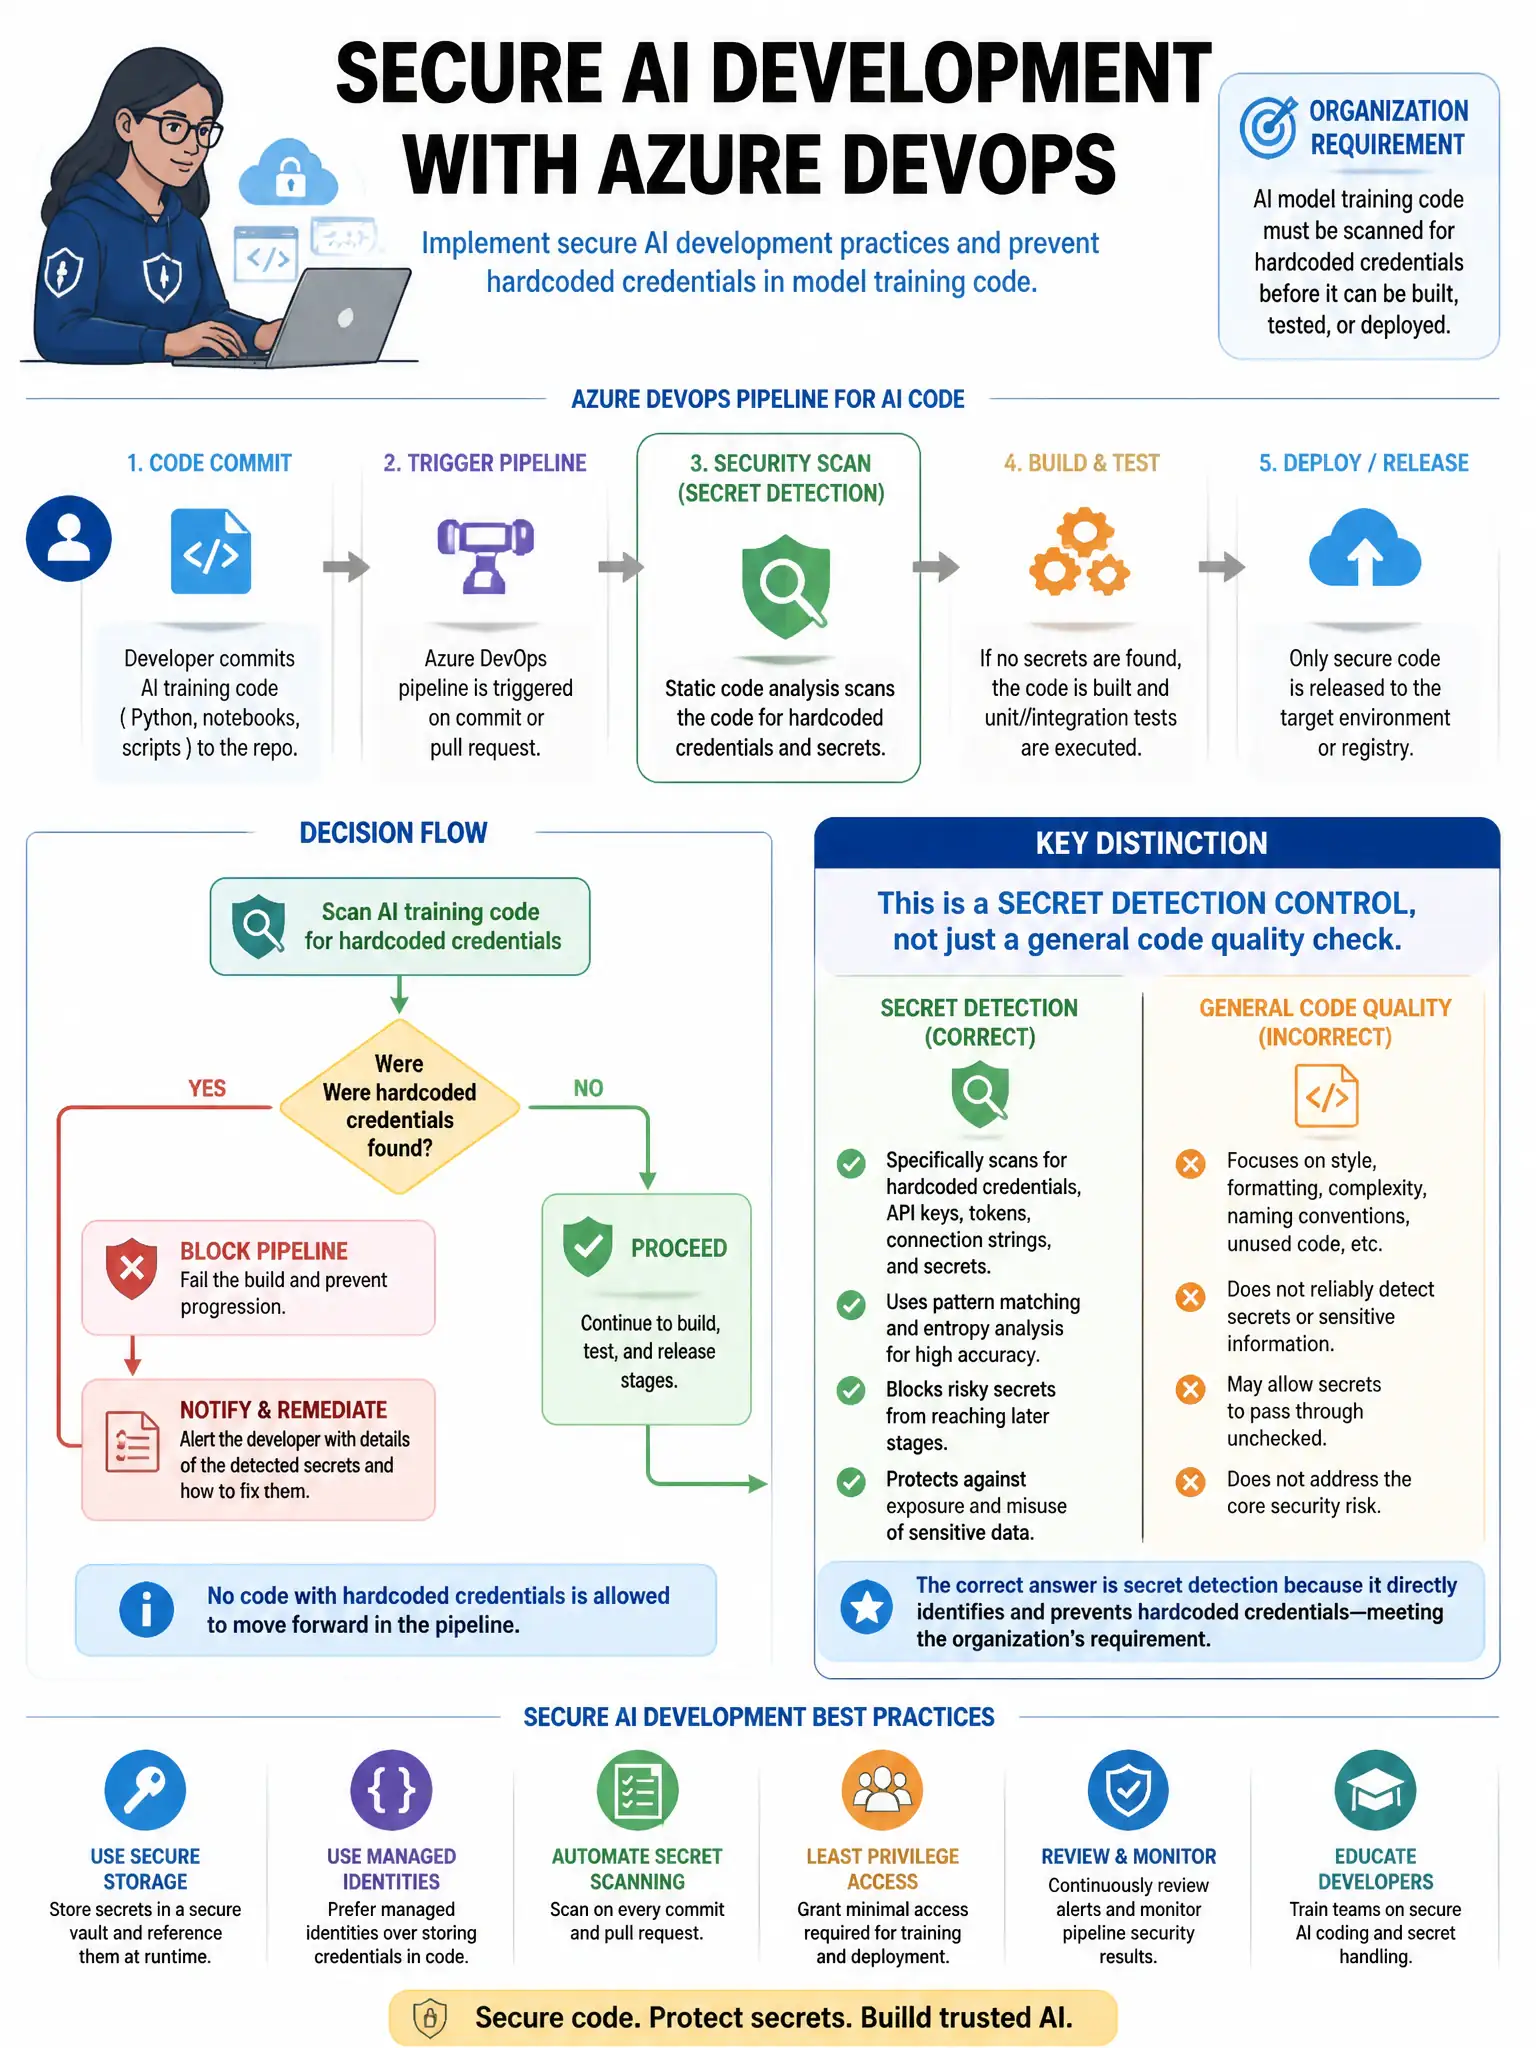
Here's the deal — you need Microsoft Security DevOps (MSDO) in Azure DevOps because it brings credential-scanning tools like CredScan into your pipeline and can stop a merge to main when it finds hardcoded secrets.
Full Explanation
Microsoft Security DevOps (MSDO) extension in Azure DevOps with credential scanning tools is correct because it integrates multiple security scanning tools into CI/CD pipelines, including CredScan (Credential Scanner), which detects hardcoded credentials, keys, and sensitive data in source code as part of pull request validation. It can be configured as a required pipeline gate before merging to main. Azure DevOps branch policies with required reviewers as a proxy for credential scanning is incorrect because required reviewers add human review gates but do not perform automated credential scanning; human reviewers may miss credentials in large codebases. Azure DevOps work item tracking with a credential review task is incorrect because Azure DevOps work items are project management tools and do not perform code scanning. Azure Container Registry vulnerability scanning applied to model training containers is incorrect because Azure Container Registry vulnerability scanning checks container images for OS and package vulnerabilities, not hardcoded credentials in source code.