
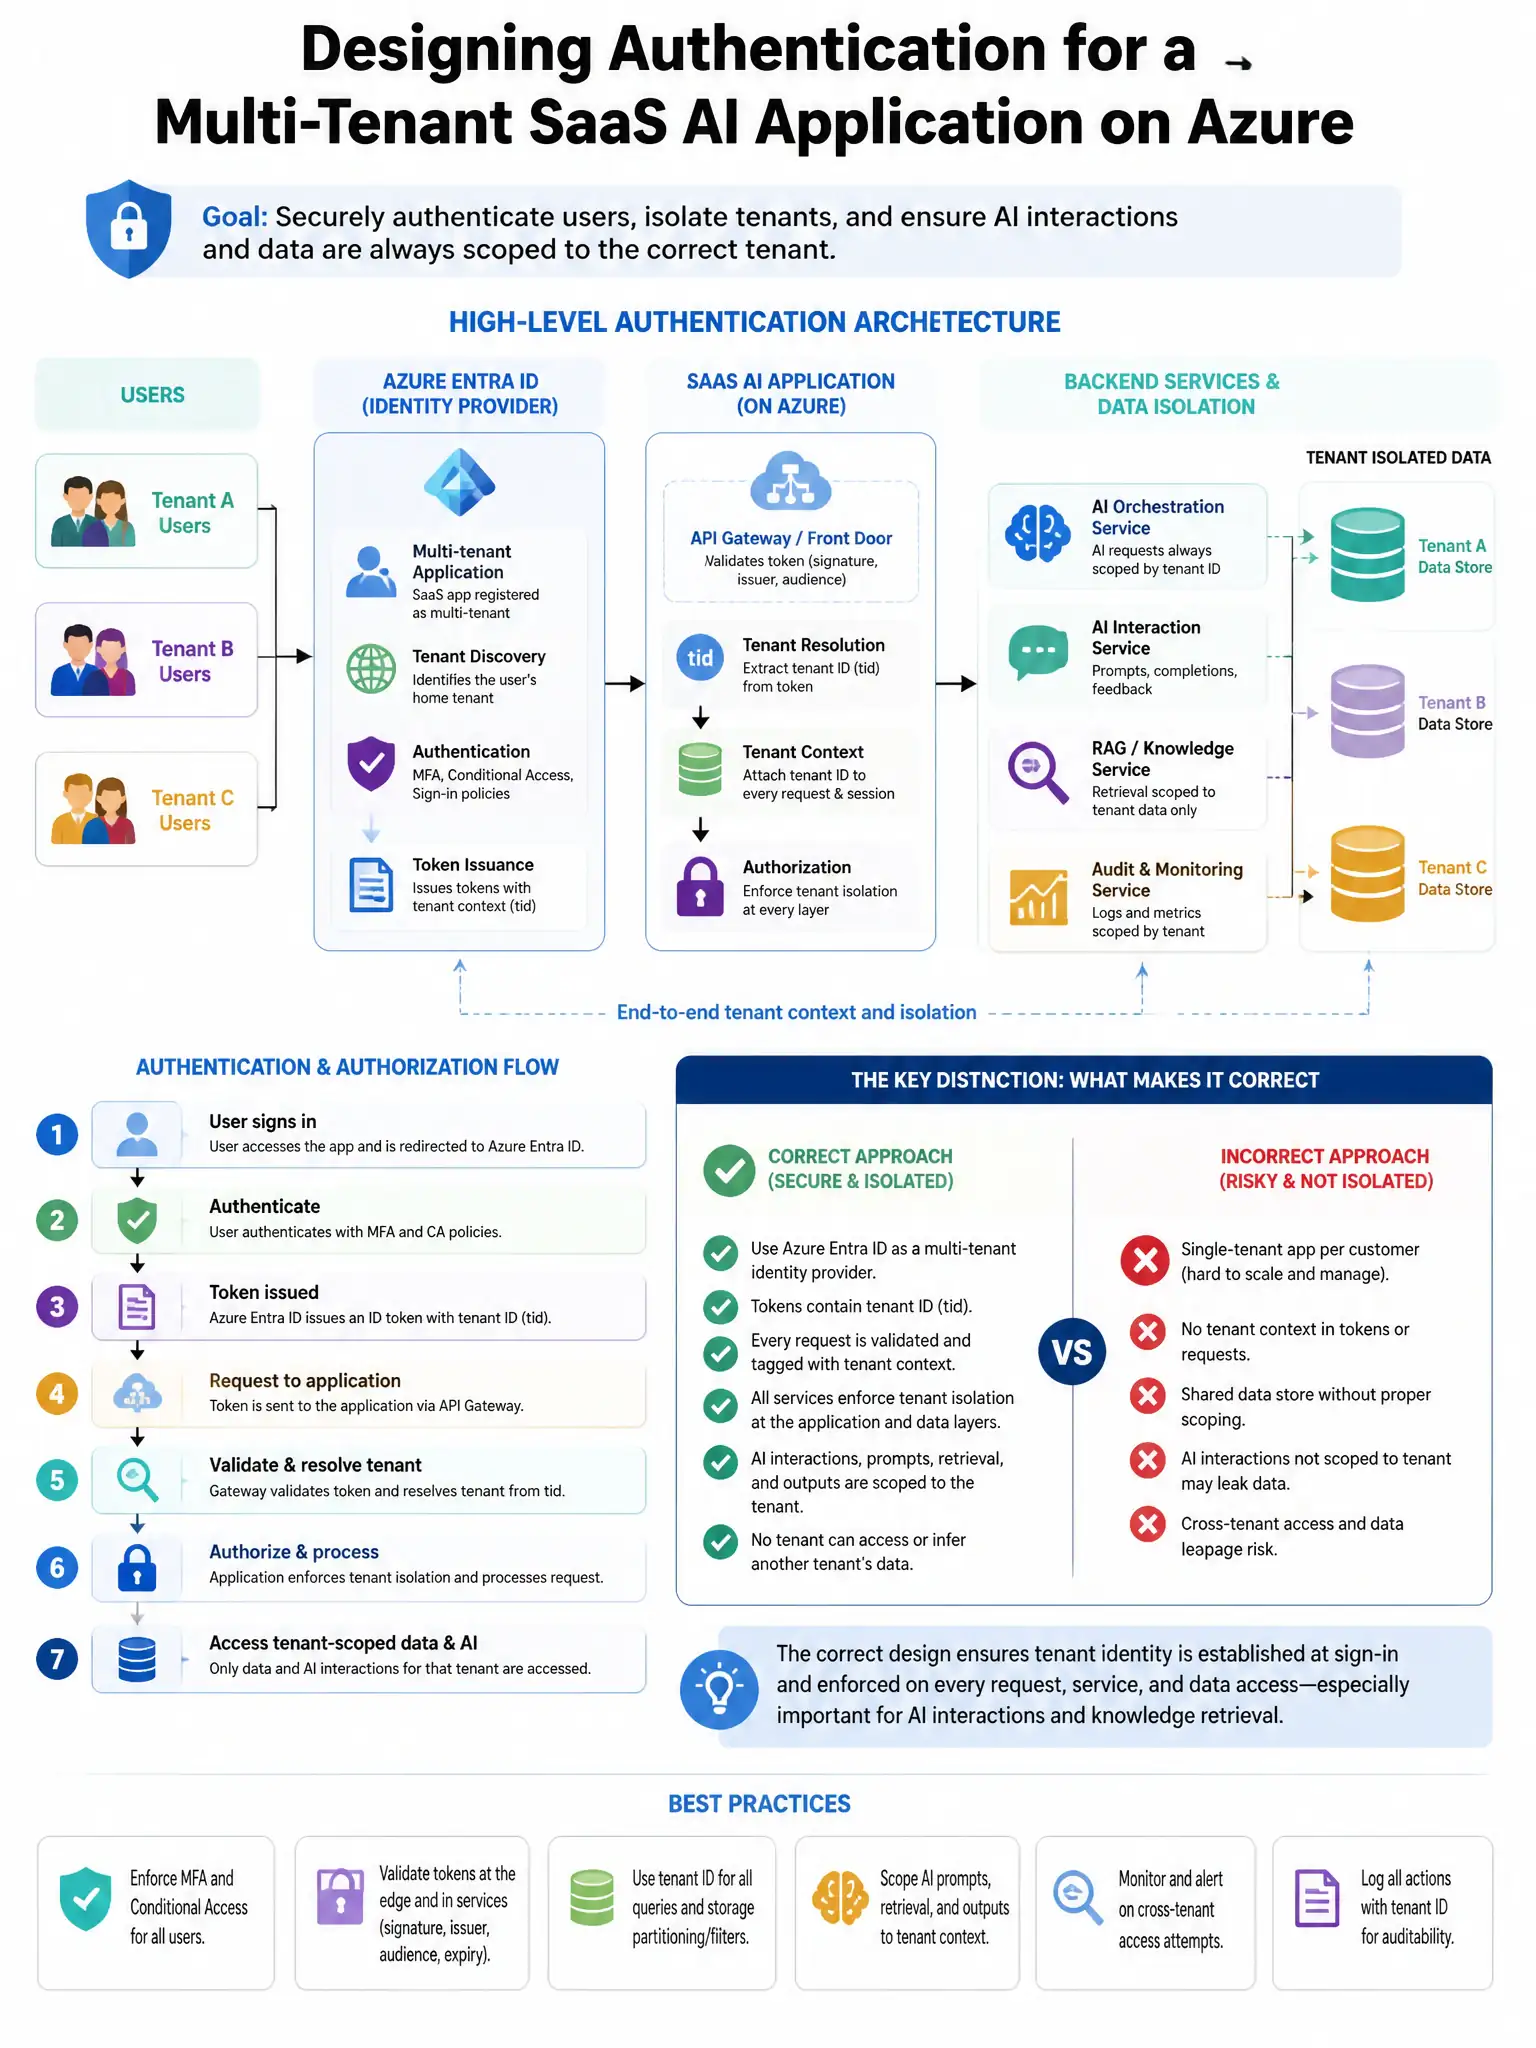
A security engineer is designing the authentication architecture for a multi-tenant SaaS AI application built on Azure. Each customer tenant must be isolated and their AI interactions must not be visible to other tenants. Which Azure architecture pattern best achieves tenant isolation for the AI components?
Select an answer to reveal the explanation.
Short Explanation
You want separate Azure OpenAI resources per customer tenant, each with its own managed identity and subscription or resource group. That puts tenant isolation at the infrastructure layer, so one tenant's AI traffic, keys, and configuration can't touch another's.
Full Explanation
Deploying separate Azure OpenAI resources per customer tenant with dedicated managed identities and separate Azure subscriptions or resource groups per tenant is correct because it achieves the strongest isolation: each tenant's AI resource, authentication, and data are completely separate at the infrastructure layer, preventing any cross-tenant data access or configuration influence. A shared Azure OpenAI resource with per-tenant API keys and application-level tenant filtering is incorrect because it relies entirely on application-level isolation, which can be bypassed by bugs or compromises in the application layer. Separate Azure OpenAI deployments per customer within a single Azure OpenAI resource using deployment-level RBAC is incorrect because, while model deployments within an Azure OpenAI resource can have separate names, they share the same resource plane and data plane endpoint, making true tenant isolation difficult to achieve. A single Azure OpenAI resource with conversation history segregated in separate Azure Cosmos DB containers per tenant is incorrect because shared infrastructure with application-level data separation in Cosmos DB introduces cross-tenant risks if the application layer is compromised.