
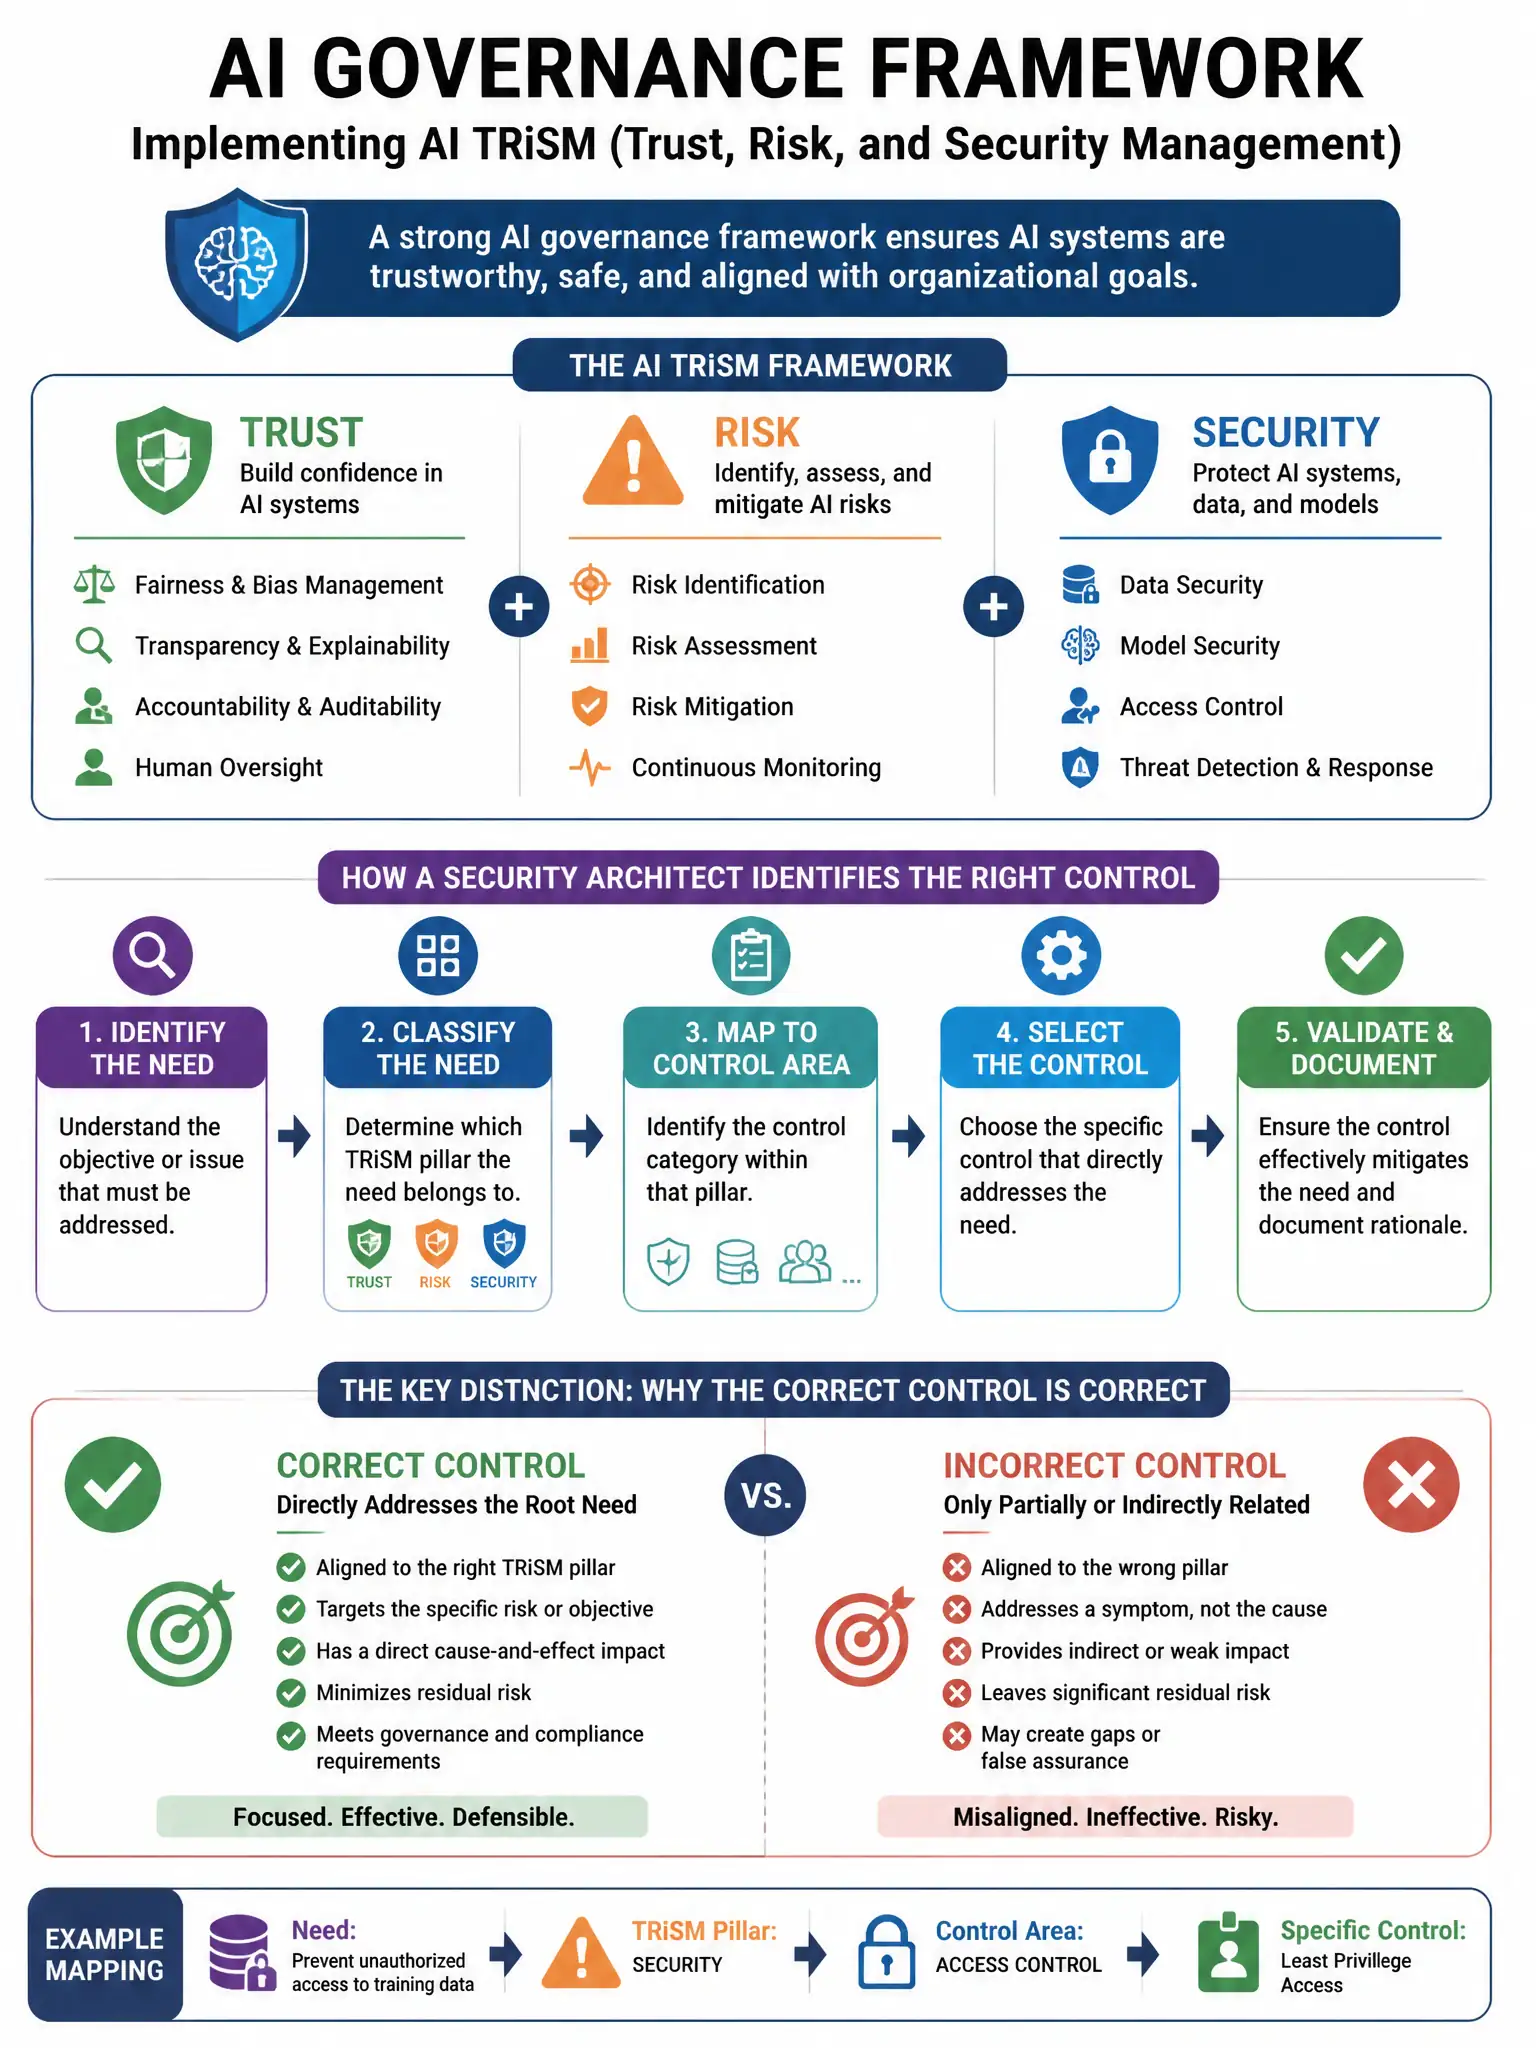
An organization's AI governance framework requires implementing AI TRiSM (Trust, Risk, and Security Management). A security architect must identify which control specifically addresses the risk that an AI model's decisions cannot be explained or audited. Which AI TRiSM pillar addresses this risk?
Select an answer to reveal the explanation.
Short Explanation
Here's the deal — AI Explainability is the right pillar because it makes AI model decisions interpretable, understandable, and auditable. You'll use controls like model documentation, feature importance analysis, decision audit trails, and explainable AI techniques.
Full Explanation
The AI Explainability option is correct because it is the AI TRiSM pillar that addresses the requirement for AI model decisions to be interpretable, understandable, and auditable. Controls under this pillar include model documentation, feature importance analysis, decision audit trails, and explainable AI techniques. The AI Security option is incorrect because it focuses on protecting AI systems from attacks, data breaches, and adversarial inputs, not on decision explainability. The AI Privacy option is incorrect because it focuses on protecting personal data used in AI training and inference. The AI Reliability option is incorrect because it focuses on model performance consistency and uptime, not on decision explainability.