
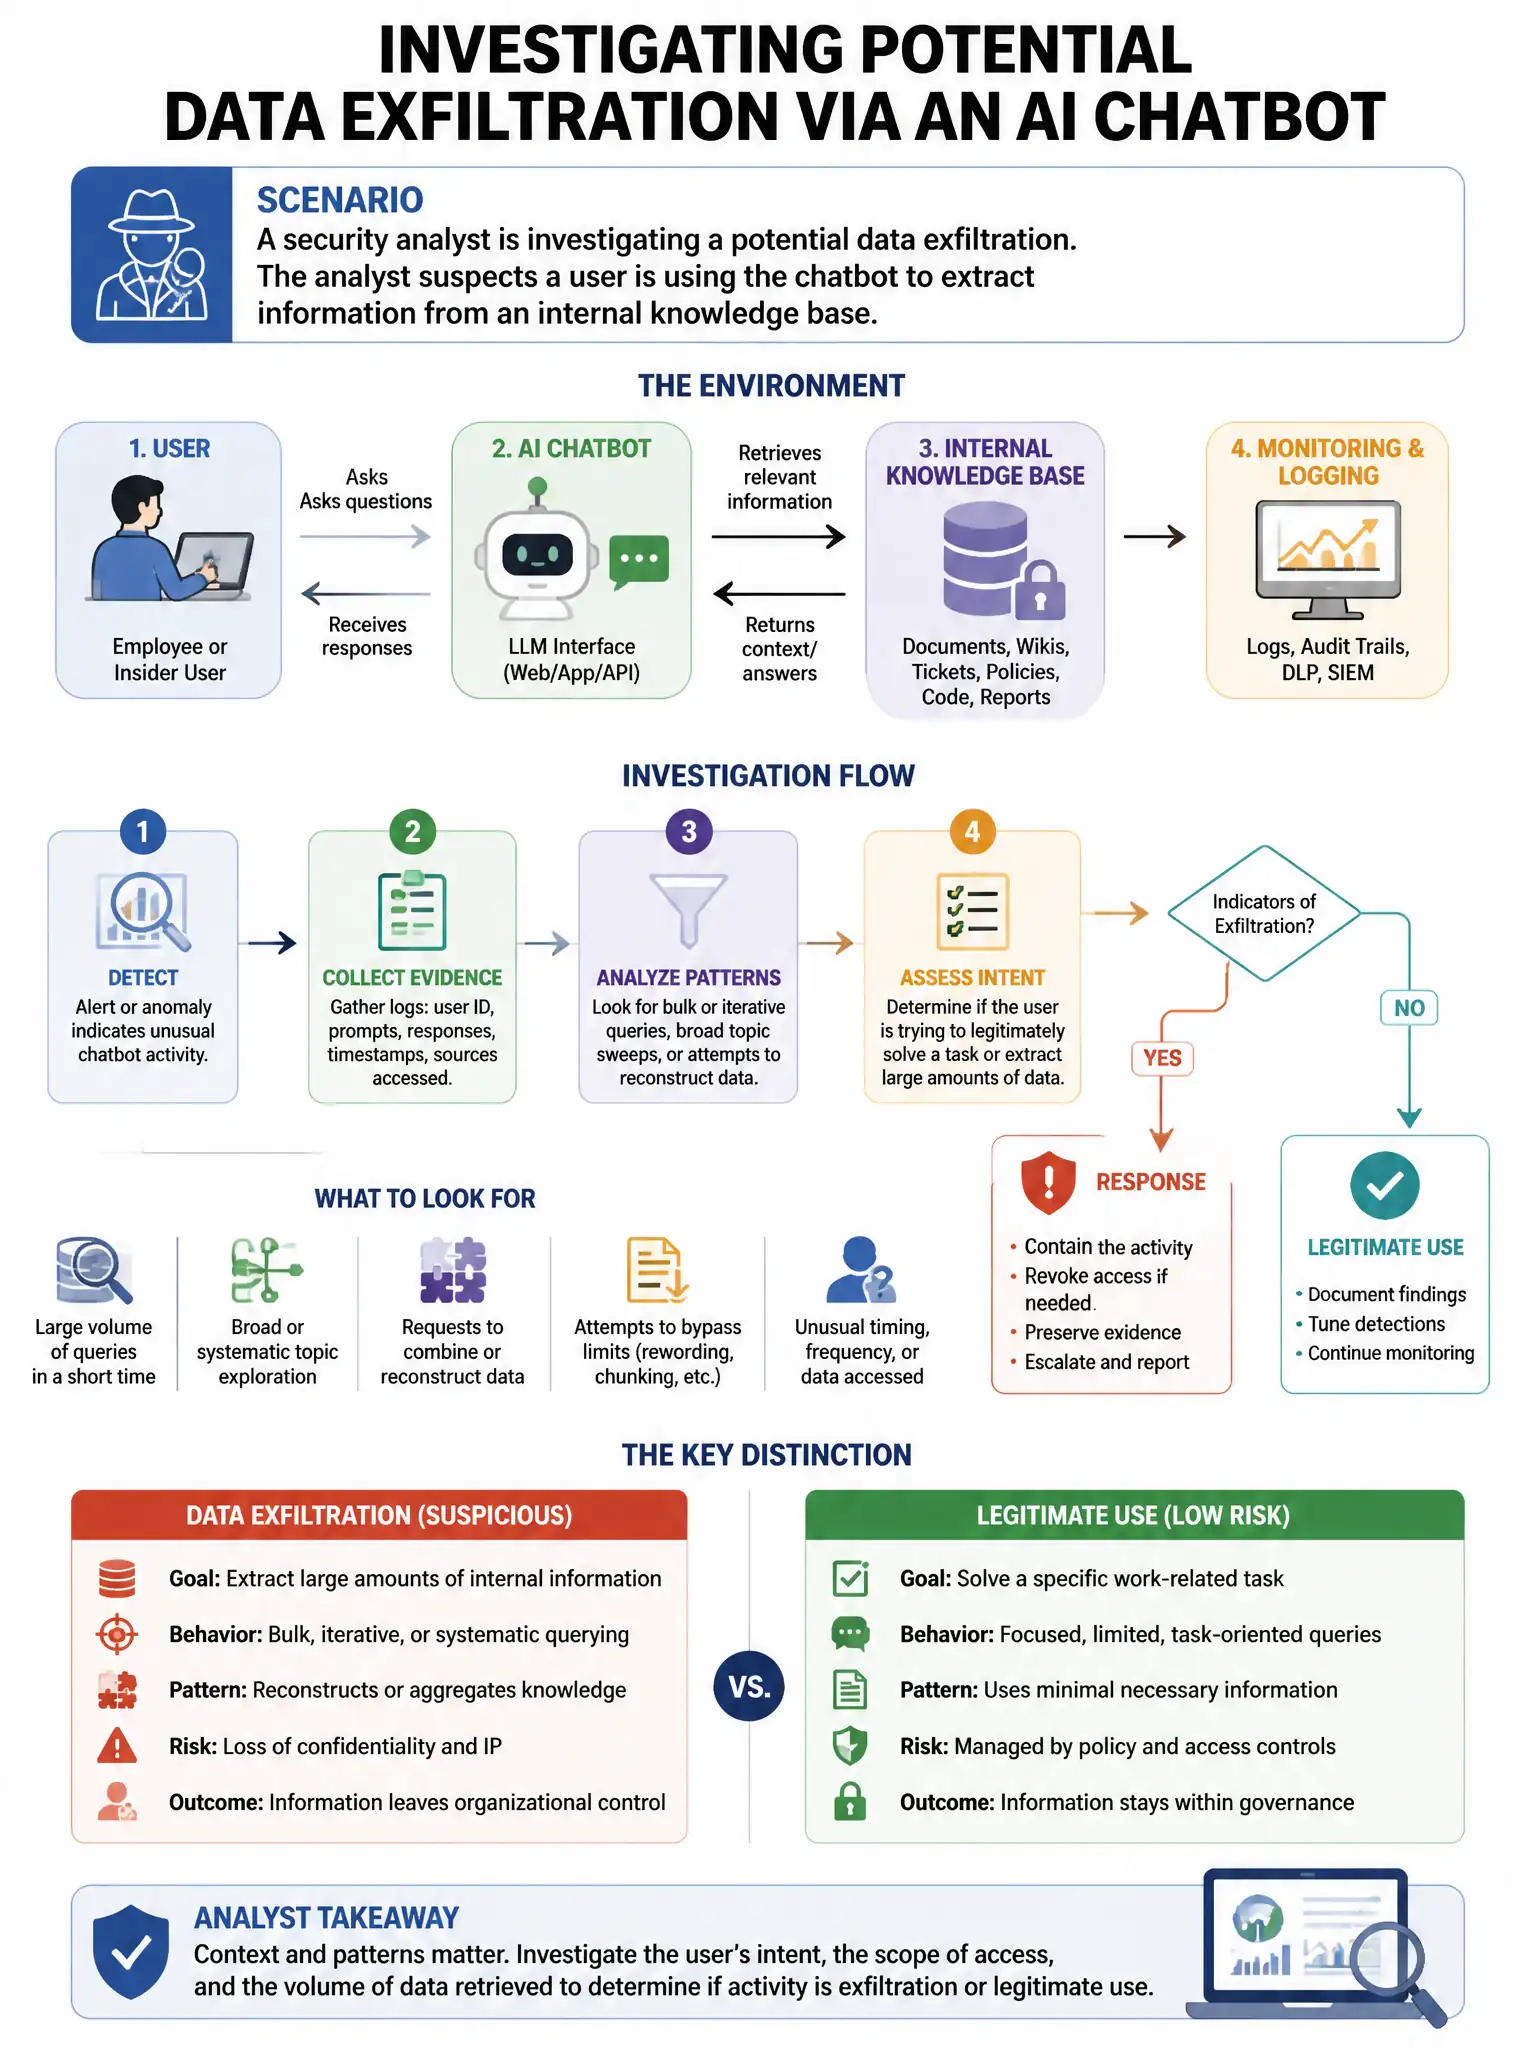
A security analyst is investigating a potential data exfiltration via an AI chatbot. The analyst suspects a user is using the chatbot to extract information from an internal knowledge base by crafting specific questions. Which Microsoft Sentinel hunting query would best identify this behavior?
Select an answer to reveal the explanation.
Short Explanation
Here's the deal — if someone's pulling info out of a chatbot, you'll usually see small questions and huge answers. Hunt for one user whose response tokens dwarf request tokens across multiple sessions.
Full Explanation
The best hunt is for chatbot API calls where response token count significantly exceeds request token count across multiple sessions from a single user because data exfiltration via AI chatbot typically manifests as a pattern where users send targeted questions (low token input) and receive large amounts of retrieved knowledge base content (high token output). Hunting for sessions where the response-to-request token ratio is anomalously high across multiple queries from the same user is the most semantically appropriate indicator of systematic information extraction. The SQL injection pattern hunt is incorrect because SQL injection patterns indicate a different attack type, not data exfiltration through legitimate question answering. The high-volume hunt for users with more than 100 chatbot queries in a single day is incorrect because high query volume alone does not distinguish legitimate heavy users from exfiltration. The non-corporate IP hunt is incorrect because external IP addresses may indicate unauthorized access but not specifically chatbot-based data exfiltration.