
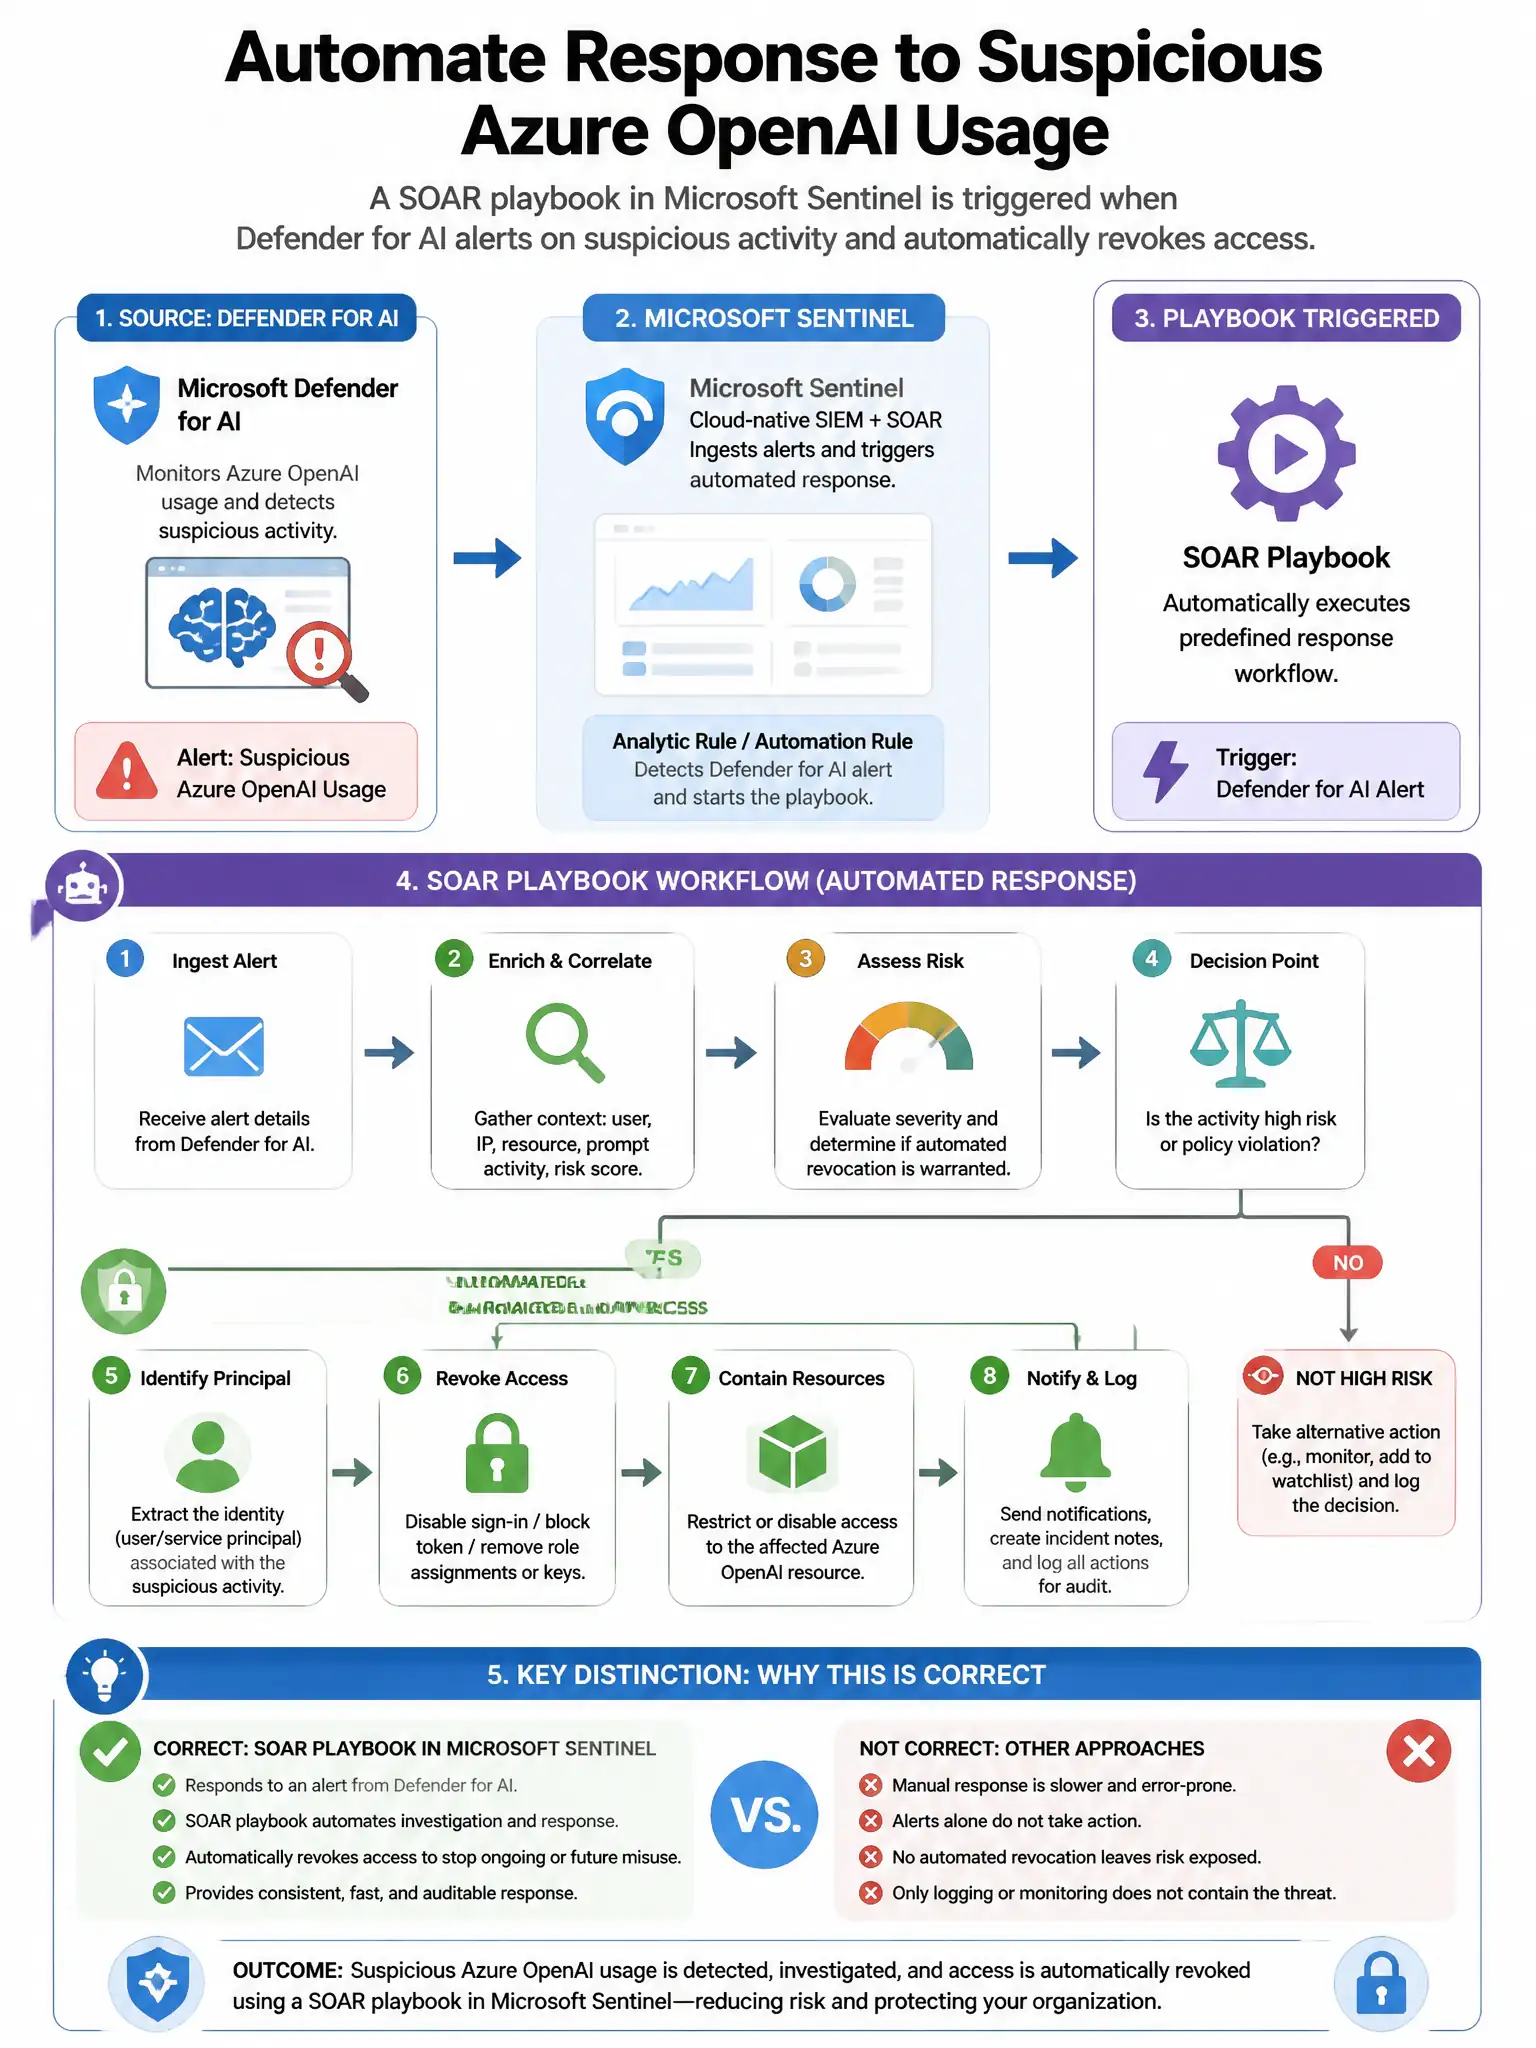
An organization deploys a SOAR playbook in Microsoft Sentinel triggered when a Defender for AI alert fires for suspicious Azure OpenAI usage. The playbook must automatically revoke the API key used in the suspicious request. Which Logic App connector action should be used?
Select an answer to reveal the explanation.
Short Explanation
You need to use the Azure Resource Manager connector action that invokes the resource operation to regenerate the Azure OpenAI API key. That invalidates the key at the resource level, stopping the suspicious caller from using it.
Full Explanation
The Azure Resource Manager connector action that invokes a resource operation to regenerate the Azure OpenAI API key is correct. Azure OpenAI API keys are managed through the Azure Resource Manager API. The Logic App Azure Resource Manager connector can invoke the 'regenerateKey' operation on the Azure OpenAI resource, which invalidates the existing API key, preventing further use by the compromised caller. The HTTP connector option making a POST request to the Azure OpenAI management endpoint to delete the key is incorrect because Azure OpenAI key regeneration is accessed through the ARM API, and using the ARM connector is the appropriate abstraction. The Azure Key Vault connector option to delete the secret containing the API key is incorrect because revoking a secret in Key Vault only helps if the application fetches the key from Key Vault at runtime; the ARM key regeneration is required regardless. The Microsoft Sentinel connector option to add the API key to the block list is incorrect because Microsoft Sentinel does not have a native 'block list' for Azure OpenAI API keys.