
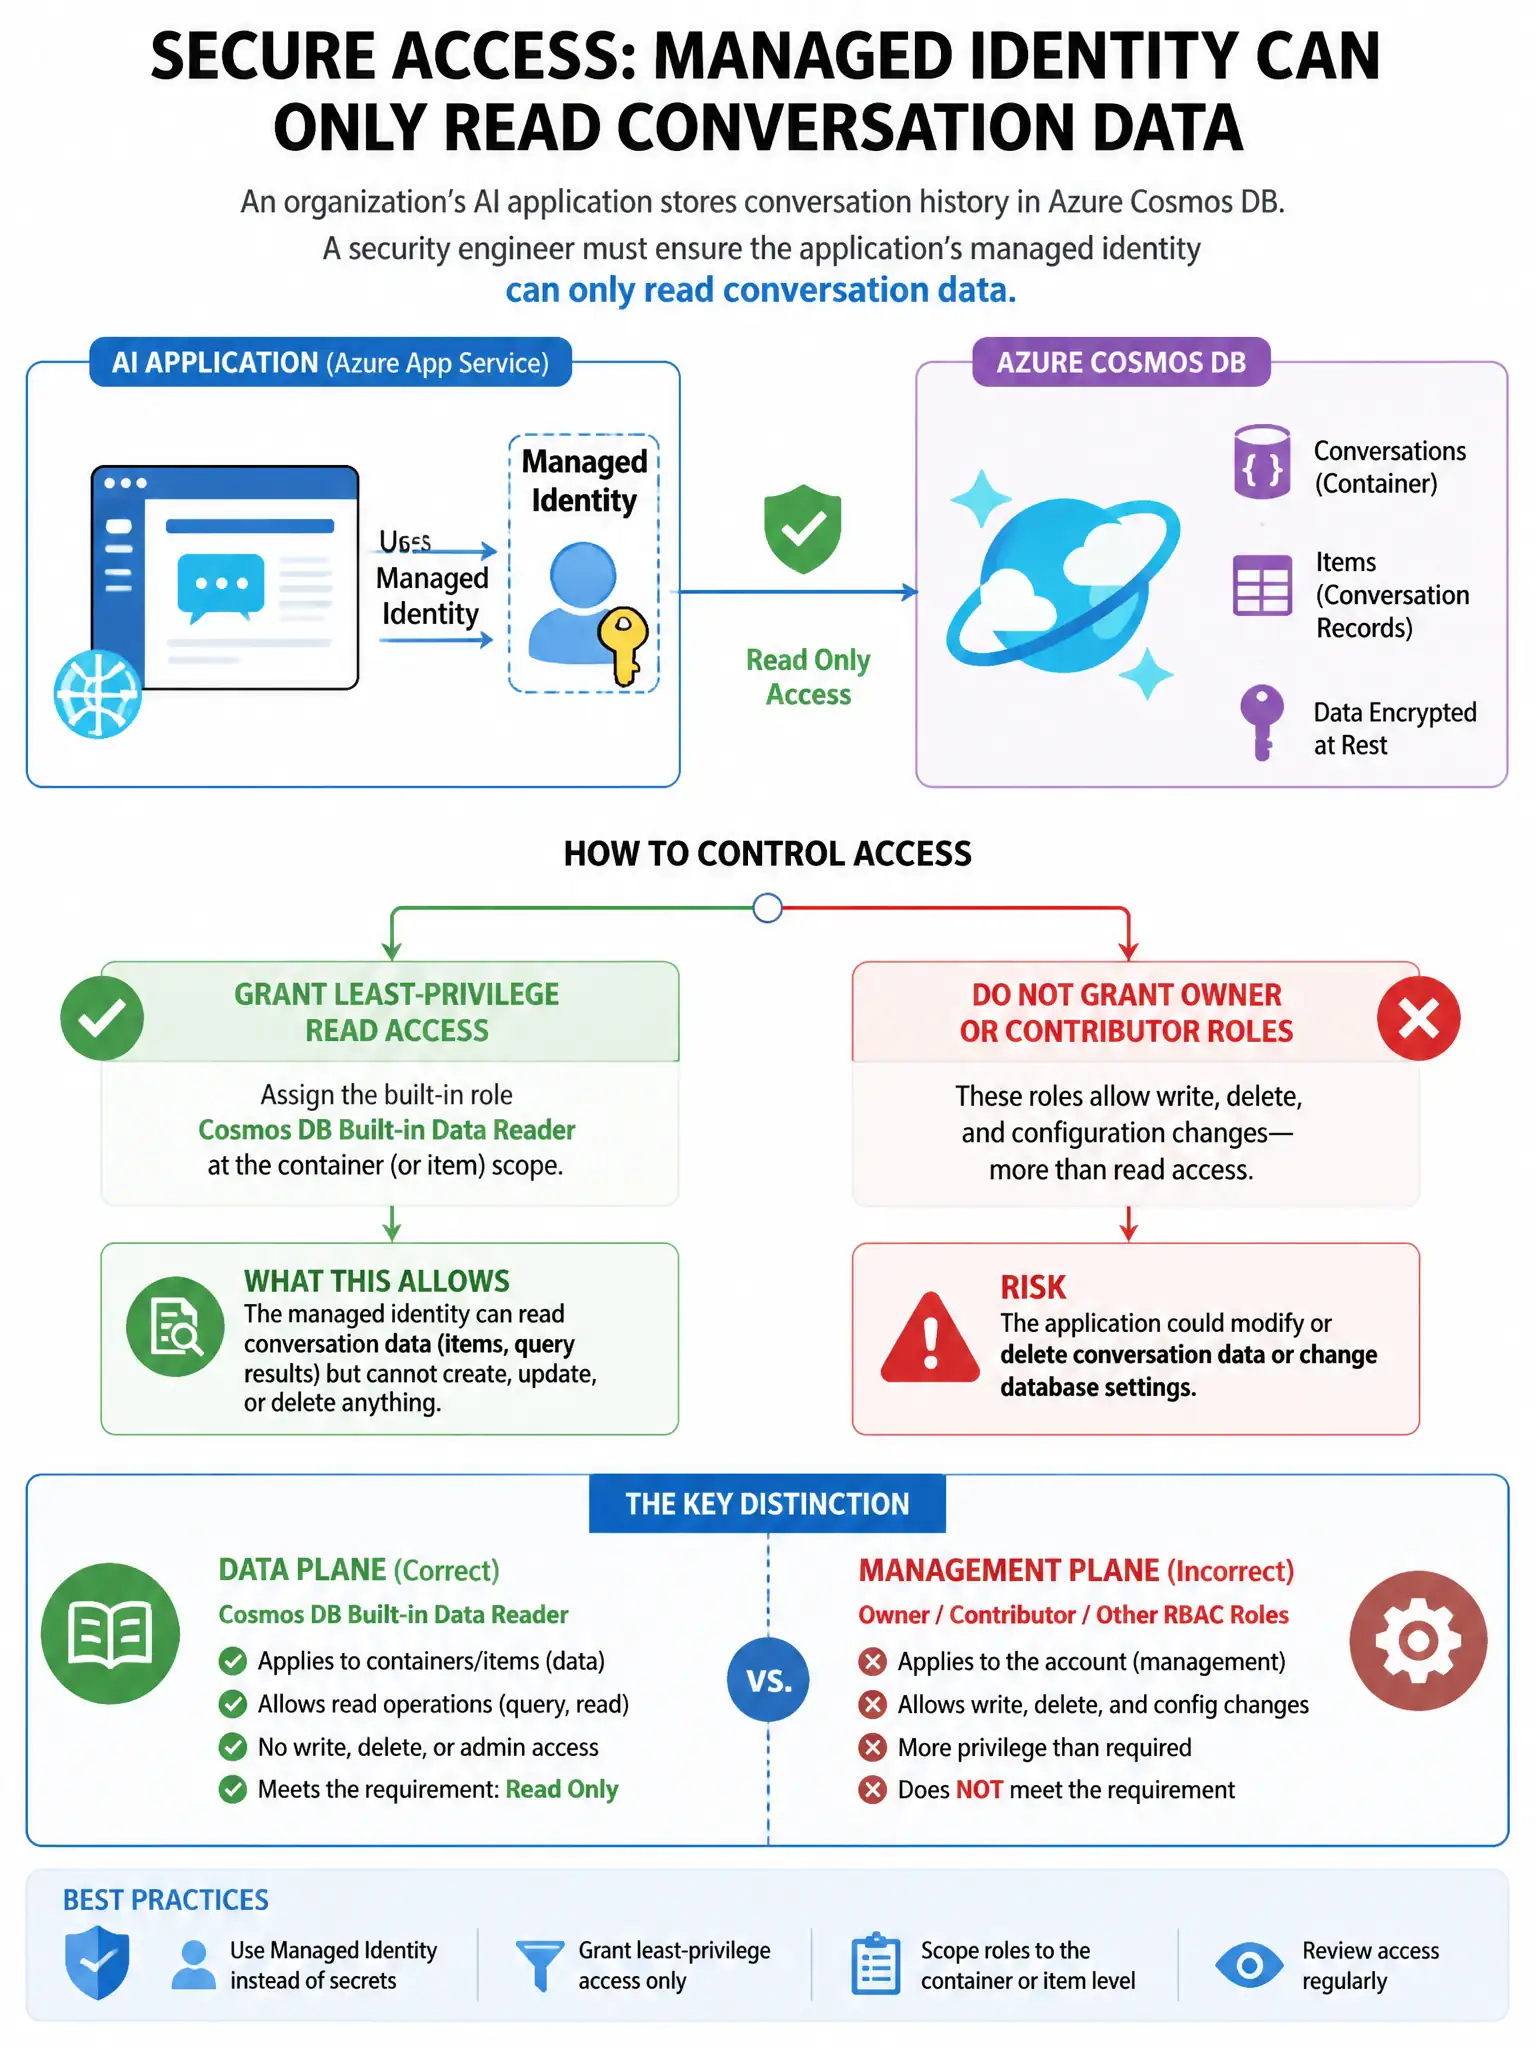
An organization's AI application stores conversation history in Azure Cosmos DB. A security engineer must ensure the application's managed identity can only read conversation data and cannot write or delete records. Which approach achieves least-privilege access to Cosmos DB?
Select an answer to reveal the explanation.
Short Explanation
Here's the deal — you need a custom Cosmos DB data plane RBAC role with only the items read action, then assign it to the managed identity. That gives read-only access to conversation data while blocking write and delete.
Full Explanation
The correct approach is to create a custom Cosmos DB data plane RBAC role definition with the 'Microsoft.DocumentDB/databaseAccounts/sqlDatabases/containers/items/read' action and assign it to the managed identity. Azure Cosmos DB supports data plane RBAC with granular action-level permissions, so a role definition that includes only the read action for items provides least-privilege read-only access to conversation data without write or delete permissions. The account-level 'Cosmos DB Account Reader Role' is incorrect because it is a control plane role that grants access to account metadata and settings, not data plane read access to documents. The custom Cosmos DB RBAC role with only 'Microsoft.DocumentDB/databaseAccounts/readMetadata' permission is incorrect because that permission only grants access to metadata about the database structure, not to actual conversation history items. Configuring Cosmos DB firewall rules to allow only the managed identity's IP address is incorrect because firewall rules control network-level access but do not enforce data plane least-privilege permissions.