
An organization uses Azure AI Content Safety and wants to receive real-time alerts in Microsoft Sentinel when Azure AI Content Safety detects and blocks high-severity hate content in their AI application. Azure AI Content Safety metrics and logs are sent to a Log Analytics workspace connected to Sentinel. Which Sentinel component generates these alerts?
Select an answer to reveal the explanation.
Short Explanation
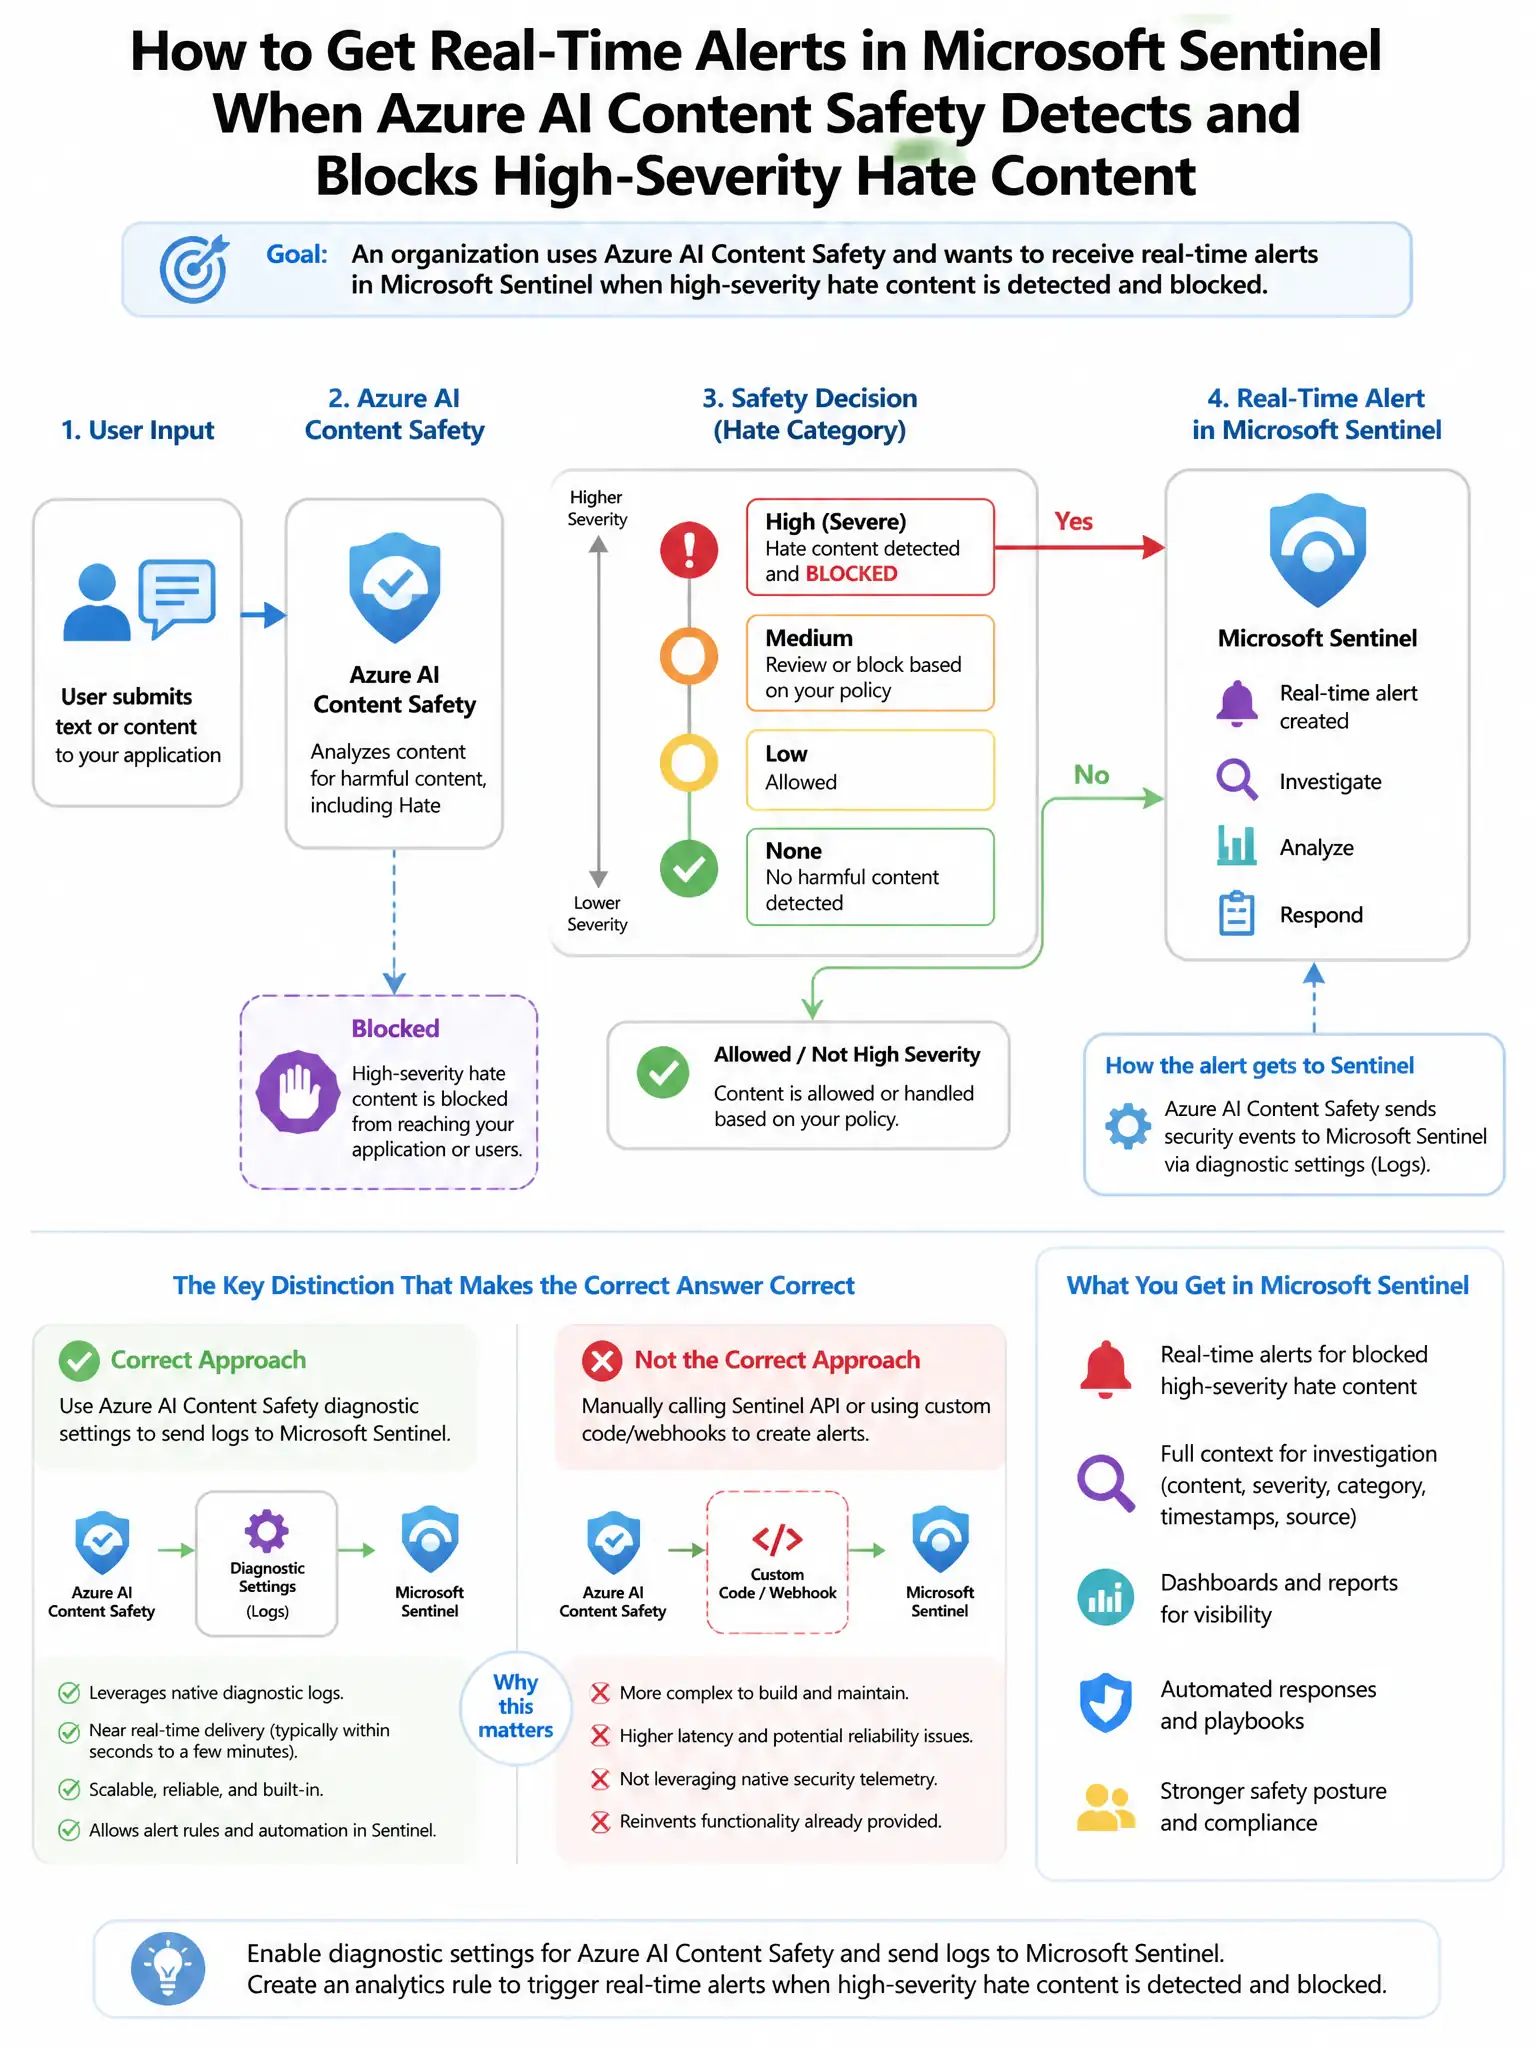
Here's the deal — you need the Sentinel scheduled analytics rule querying Azure AI Content Safety diagnostic logs for blocked high-severity hate detections. Those logs land in Log Analytics with category, severity, and action, so the rule can spot blocks and create incidents fast.
Full Explanation
The correct approach is the Sentinel scheduled analytics rule querying the Azure AI Content Safety diagnostic logs for blocked requests with high-severity hate category detections. Azure AI Content Safety sends diagnostic logs to Log Analytics, including content moderation decision records that capture the content category, severity level, and action taken (blocked/allowed) for each request. That rule can query these logs to detect high-severity hate content blocks in real time, creating incidents for analyst review. It can filter for category='Hate', severity='High', and action='Blocked' to focus on the most critical content safety events. The Fusion rule correlating AI Content Safety events with Entra ID sign-in anomalies is wrong because Fusion rules correlate specific Microsoft security alert types using ML; they cannot be configured to correlate AI Content Safety logs with Entra ID events in any meaningful way for this use case. The Microsoft Defender for Cloud alerts forwarded to Sentinel via the Defender for Cloud connector are wrong because Defender for Cloud alerts cover AI resource security threats (like jailbreak attempts), not content policy enforcement events from Azure AI Content Safety moderation—those are operational content moderation logs. The Azure Monitor Metric alerts for Azure AI Content Safety forwarded to Sentinel as incidents are wrong because Azure Monitor Metric alerts based on counts or averages do not include the content category details (hate, high-severity) needed to generate meaningful security incidents; diagnostic log-based analytics rules provide the required granularity.