
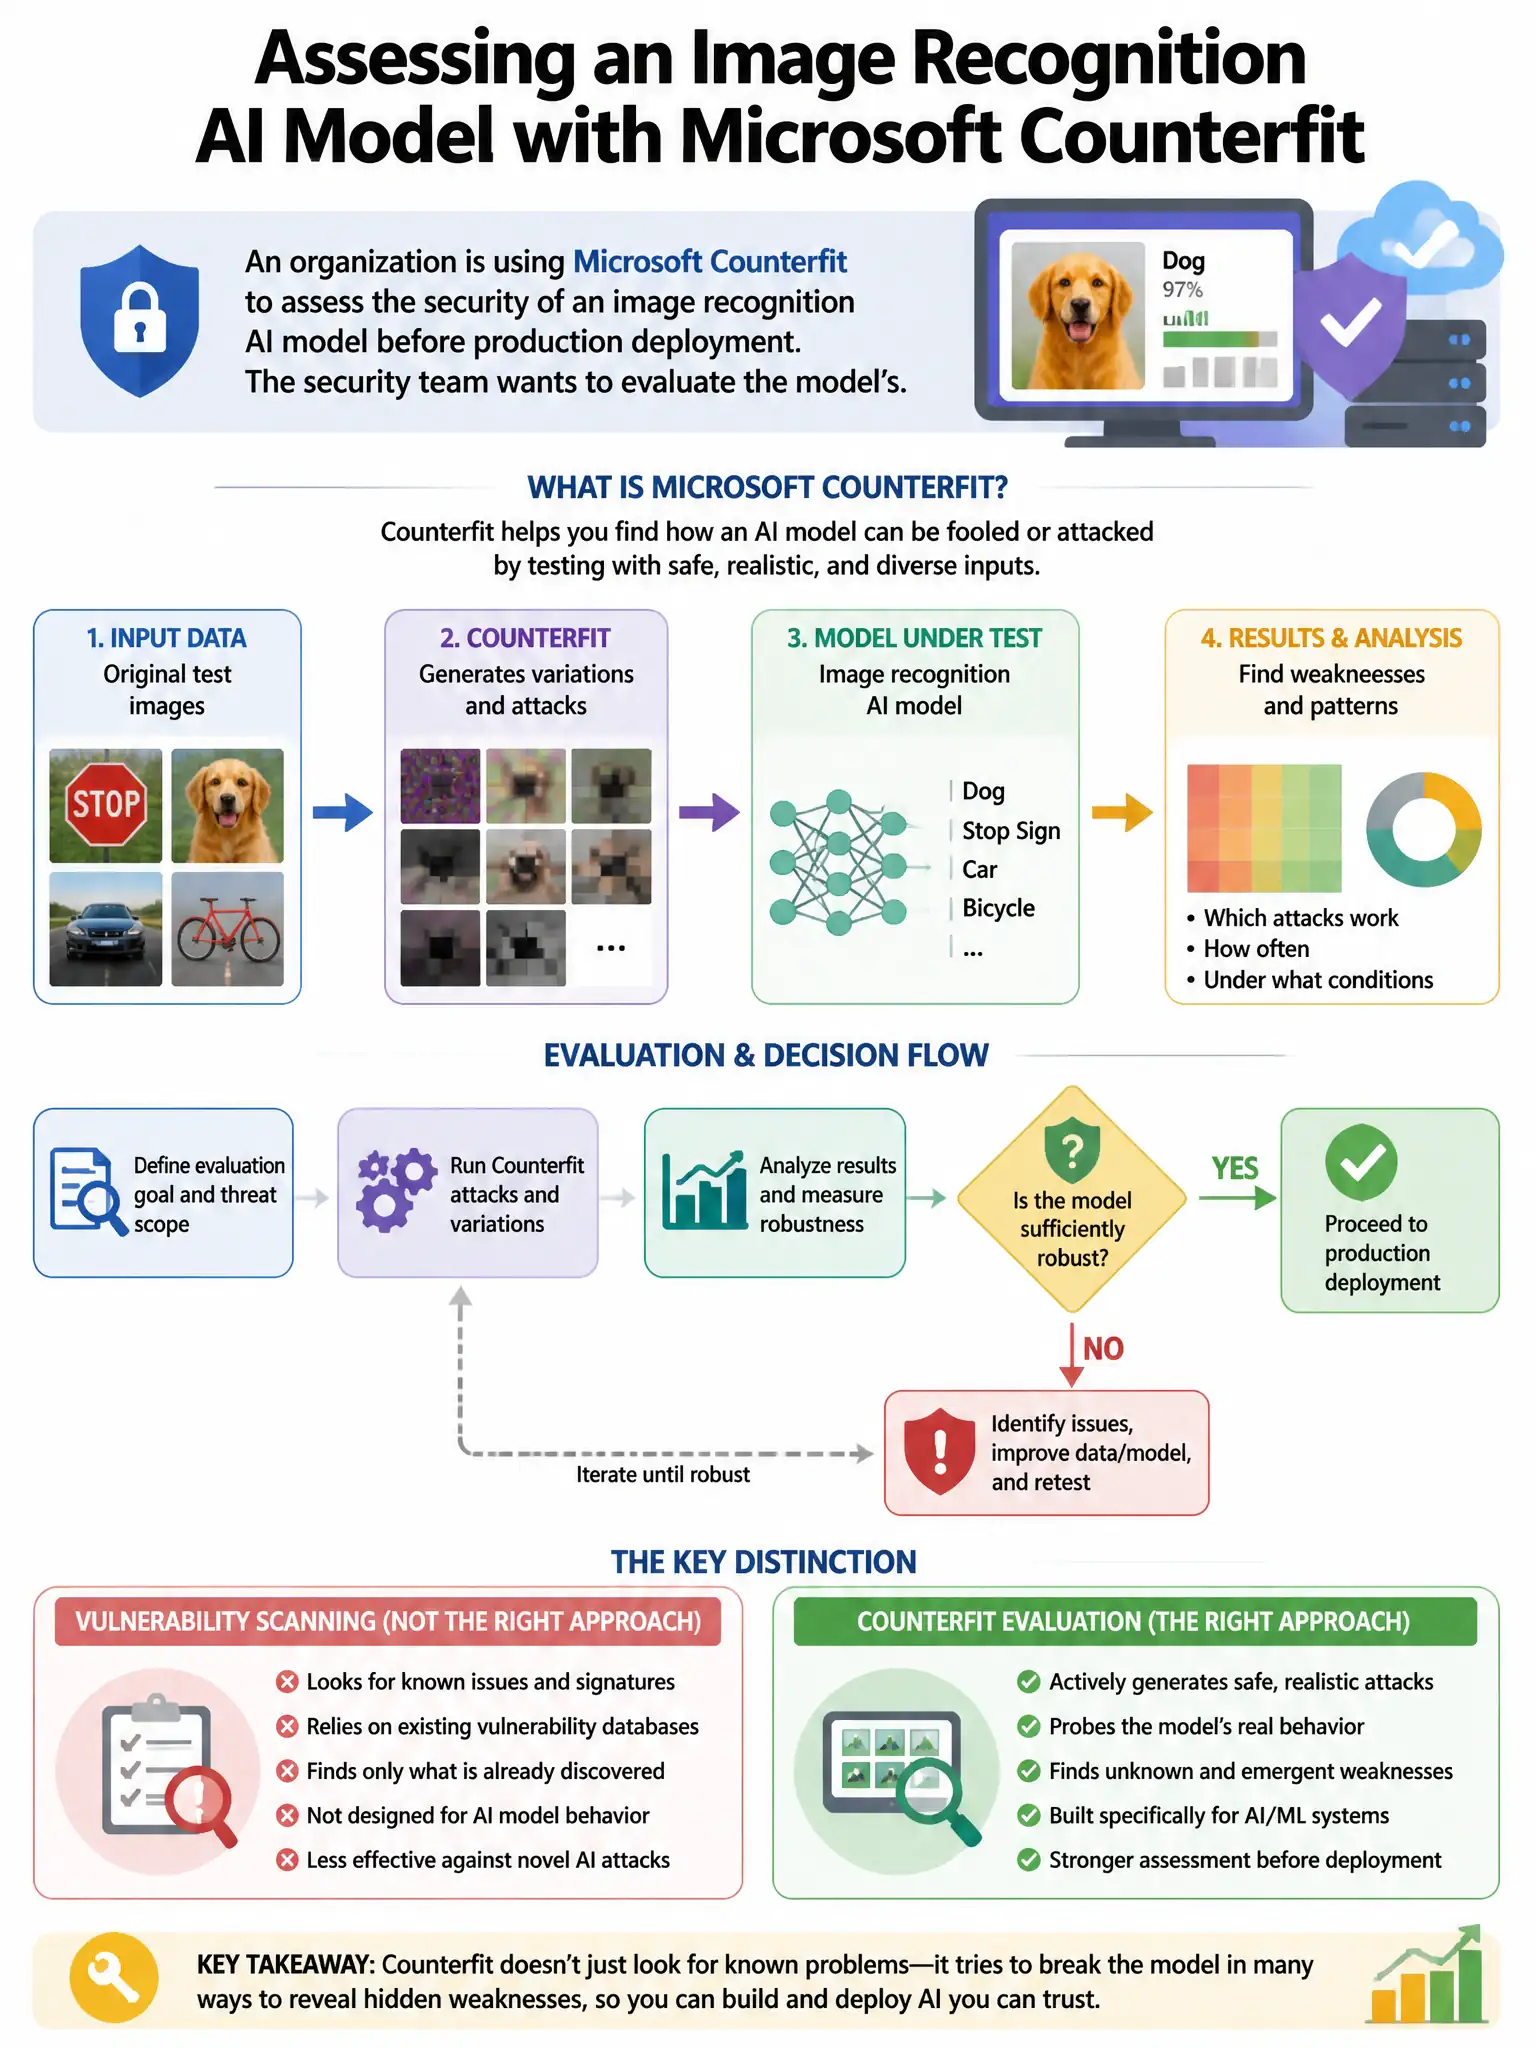
An organization is using Microsoft Counterfit to assess the security of an image recognition AI model before production deployment. The security team wants to evaluate the model's resilience to black-box adversarial attacks—where the attacker can only query the model and observe outputs, without access to model weights or architecture. Which Counterfit attack configuration represents a black-box attack?
Select an answer to reveal the explanation.
Short Explanation
Here's the deal — you're right to pick the black-box attack using ZOO or boundary attack methods because these only need to query the model and watch outputs. They don't touch weights, gradients, or architecture, which is exactly what a black-box attacker has.
Full Explanation
The correct choice is the black-box attack using ZOO (Zeroth Order Optimization) or boundary attack methods that only require model output queries, because black-box adversarial attacks operate under the assumption that the attacker cannot access model internals—only the interface for submitting inputs and receiving predictions. Attacks like ZOO and boundary attacks craft adversarial examples by systematically querying the model and estimating decision boundaries from outputs alone. Microsoft Counterfit supports these attack algorithms and can assess how resilient the model is to real-world attackers who only have inference access. The white-box attack using FGSM with access to model gradients is wrong because FGSM (Fast Gradient Sign Method) is a white-box attack that requires access to model gradients, computed via backpropagation through the model, which is not available in a black-box scenario. The gray-box attack using model architecture knowledge is wrong because a gray-box attack uses partial knowledge, like model architecture, that would not be available in a pure black-box evaluation. The transfer attack using a surrogate model trained on the same dataset is wrong because a transfer attack uses a surrogate model to craft adversarial examples and then transfers them to the target model—this requires training data and represents a different threat model.