
An organization needs to federate a GitHub Actions CI/CD pipeline identity with Microsoft Entra ID so the pipeline can deploy Azure OpenAI models without storing any Azure credentials in GitHub secrets. Which Entra ID feature enables this credential-free federation?
Select an answer to reveal the explanation.
Short Explanation
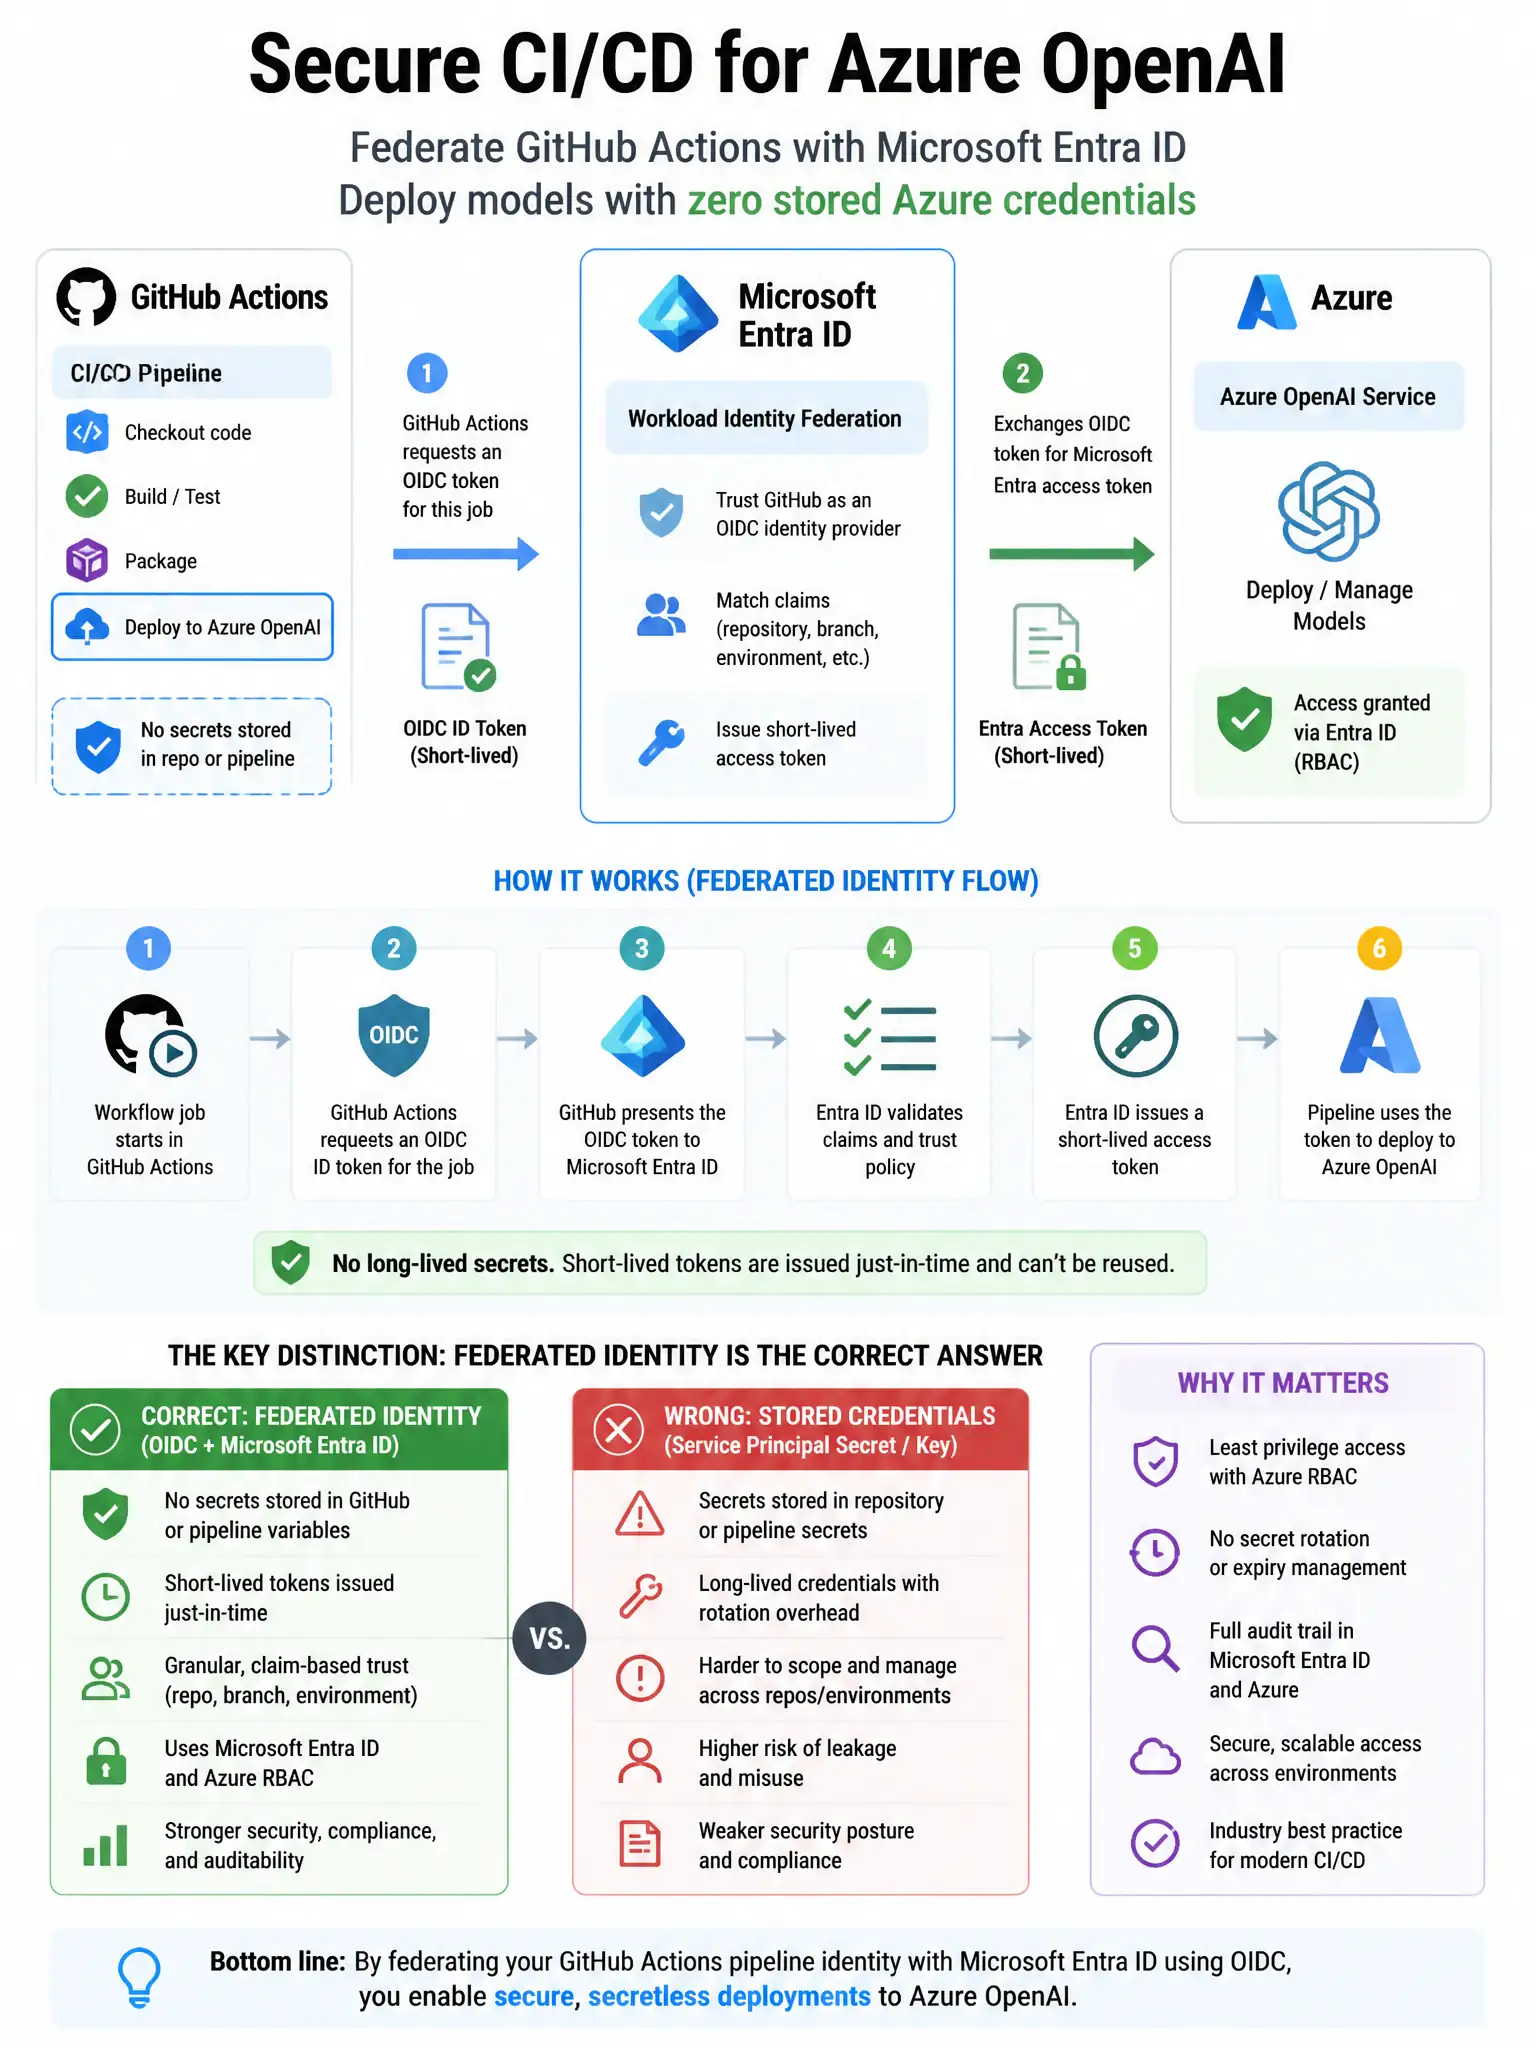
Here's the deal — you want Workload Identity Federation using OpenID Connect (OIDC) between GitHub Actions and an Entra ID app registration. It lets GitHub Actions trade its own token for an Entra ID access token, so you don't store Azure secrets in GitHub. Set up the federated credential and assign the right RBAC roles.
Full Explanation
Workload Identity Federation using OpenID Connect (OIDC) between GitHub Actions and an Entra ID app registration is correct because it lets an external identity provider, such as GitHub Actions, exchange its own issued tokens for Microsoft Entra ID access tokens without requiring stored secrets. The configuration involves creating a federated credential on an Entra ID app registration that trusts GitHub Actions OIDC tokens from a specific repository and branch, and assigning the app registration the necessary Azure RBAC roles. GitHub Actions workflows then use the OIDC token issued by GitHub to request an Entra ID token, enabling Azure CLI or SDK authentication with no secrets in GitHub. The Entra ID Application Proxy for GitHub Actions option is wrong because Application Proxy provides remote access to on-premises web apps through Entra ID; it is not a federation mechanism for CI/CD pipelines. The Entra ID PIM eligible assignment for the GitHub service principal option is wrong because PIM eligible assignments manage role activation for users; they do not provide credential-free federation for external identity providers. The Entra ID External Identities B2B invite for the GitHub organization option is wrong because B2B invite is for inviting human external users as guest accounts, not for federating CI/CD pipeline identities.