
A company's Microsoft Entra ID administrator wants to protect the action of removing a Conditional Access policy that enforces MFA for Azure AI Foundry, so that even Global Administrators cannot remove the policy without satisfying an additional authentication challenge. Which Entra ID feature enables this protection for administrative actions?
Select an answer to reveal the explanation.
Short Explanation
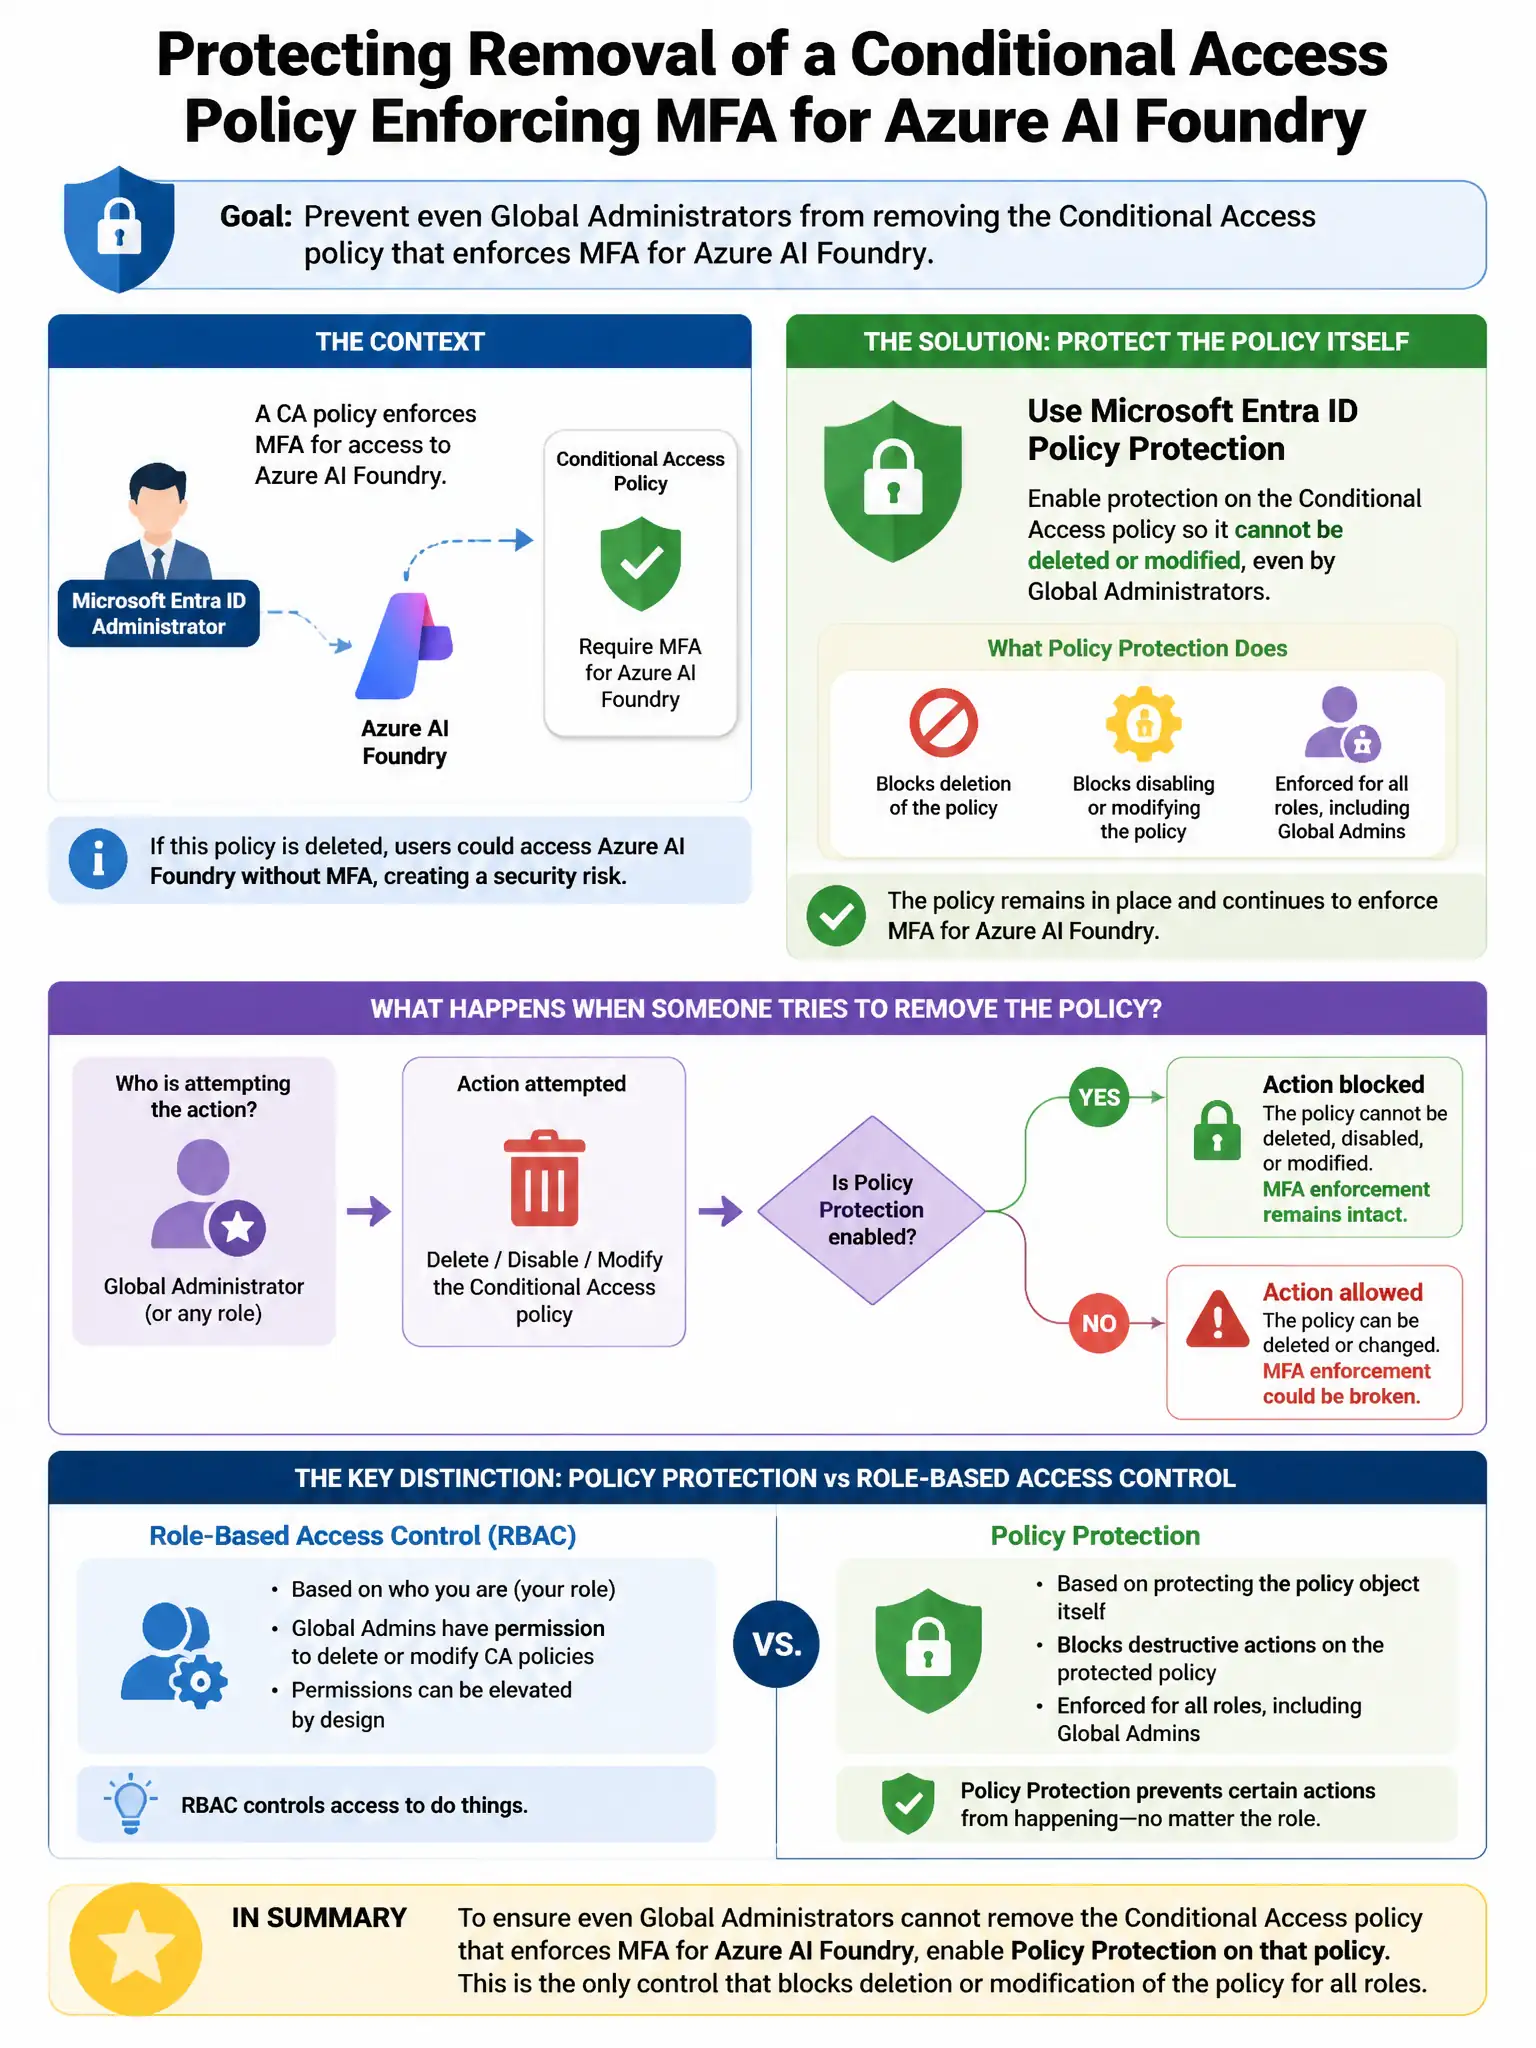
Here's the deal — you want Protected Actions, because it forces a step-up Conditional Access authentication context when someone tries to change or remove that sensitive policy. That means even a Global Administrator has to satisfy the extra challenge before the action succeeds.
Full Explanation
The correct choice is the one that uses Microsoft Entra ID Protected Actions configured to require a Conditional Access authentication context for the 'Update Conditional Access policies' permission. Protected Actions lets you designate specific Entra permissions—such as 'microsoft.directory/conditionalAccessPolicies/delete' or 'microsoft.directory/conditionalAccessPolicies/basic/update'—as protected. When an administrator attempts to delete or modify the Conditional Access policy, they must satisfy a Conditional Access authentication context, such as completing phishing-resistant MFA again, even if they already have a session. This raises the bar for even highly privileged users to modify critical security policies. The privileged identity management approval workflow for the Global Administrator role is wrong because PIM approval workflows require approval when activating the Global Administrator role; however, once the role is activated, Protected Actions can still require step-up authentication for specific sensitive operations. The Azure Resource Lock on the Conditional Access policy resource is wrong because Azure Resource Locks apply to Azure resources, also known as ARM resources; Conditional Access policies are Entra ID directory objects and cannot be protected with Azure Resource Locks. The custom two-administrator approval workflow is wrong because it requires building custom tooling; Protected Actions is the built-in Entra ID feature designed for this scenario.