
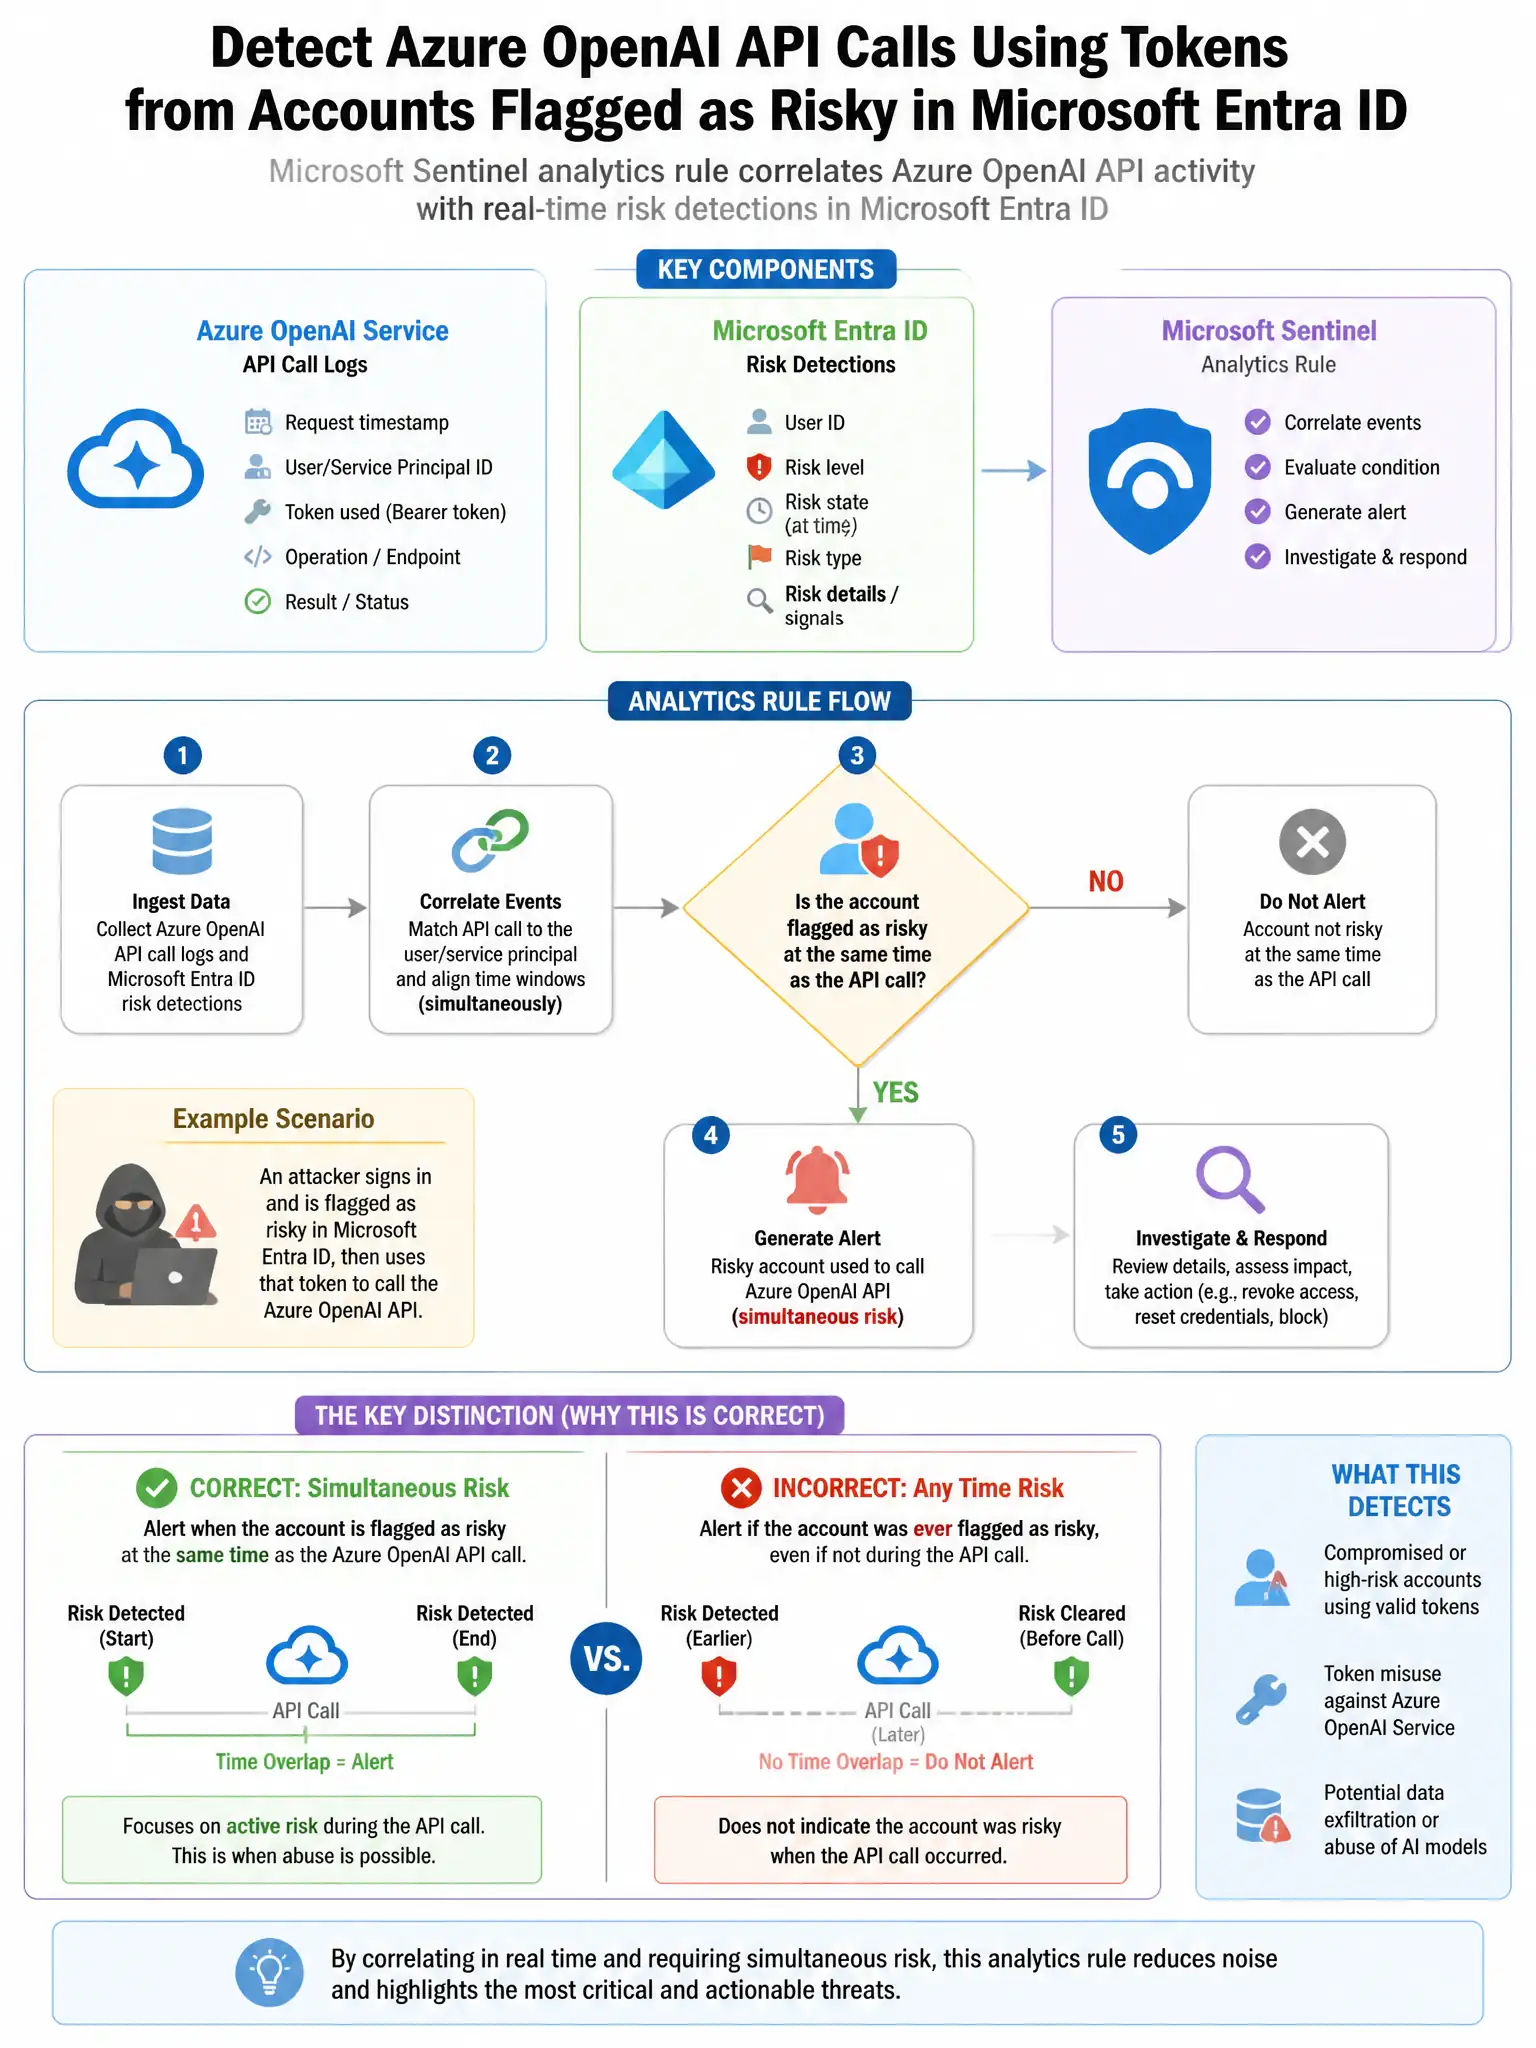
A Microsoft Sentinel analytics rule needs to detect when Azure OpenAI API calls are made using tokens from accounts that are simultaneously flagged as risky in Microsoft Entra ID Protection. Which Sentinel feature enables correlation across these two data sources?
Select an answer to reveal the explanation.
Short Explanation
You need a scheduled KQL analytics rule that joins the Entra ID risk tables with Azure OpenAI diagnostic logs on the user identity. That gives Sentinel a real-time correlated detection instead of separate alerts or static lists.
Full Explanation
The correct approach is to write a scheduled KQL analytics rule that joins the AADRiskyUsers or AADUserRiskEvents table with the AzureDiagnostics table on the user identity. Microsoft Sentinel allows joining multiple log tables in a single scheduled analytics rule using KQL join operators. The AADRiskyUsers or AADUserRiskEvents tables, which come from the Entra ID data connector, contain risk-flagged users, and AzureDiagnostics contains Azure OpenAI API calls. A KQL query can join these tables on the user identity field to detect when a currently risky user is making Azure OpenAI API calls, creating a correlated detection. The option that creates separate analytics rules for each source and links them in the same workbook is wrong because separate analytics rules generate separate alerts, and workbooks provide visualization, not correlated detection logic across data sources. The option that uses a Fusion analytics rule to correlate Entra ID risk events with OpenAI diagnostic logs is wrong because Fusion rules use machine learning to detect multi-stage attacks by correlating specific alert types from Microsoft products; they cannot be configured with custom join logic across arbitrary tables. The option that creates a Sentinel watchlist containing all risky users and queries it against OpenAI logs is wrong because using a watchlist is a valid approach but is static—it requires manual maintenance of the risky user list, whereas joining against AADRiskyUsers provides a real-time risk signal from Entra ID Protection.