
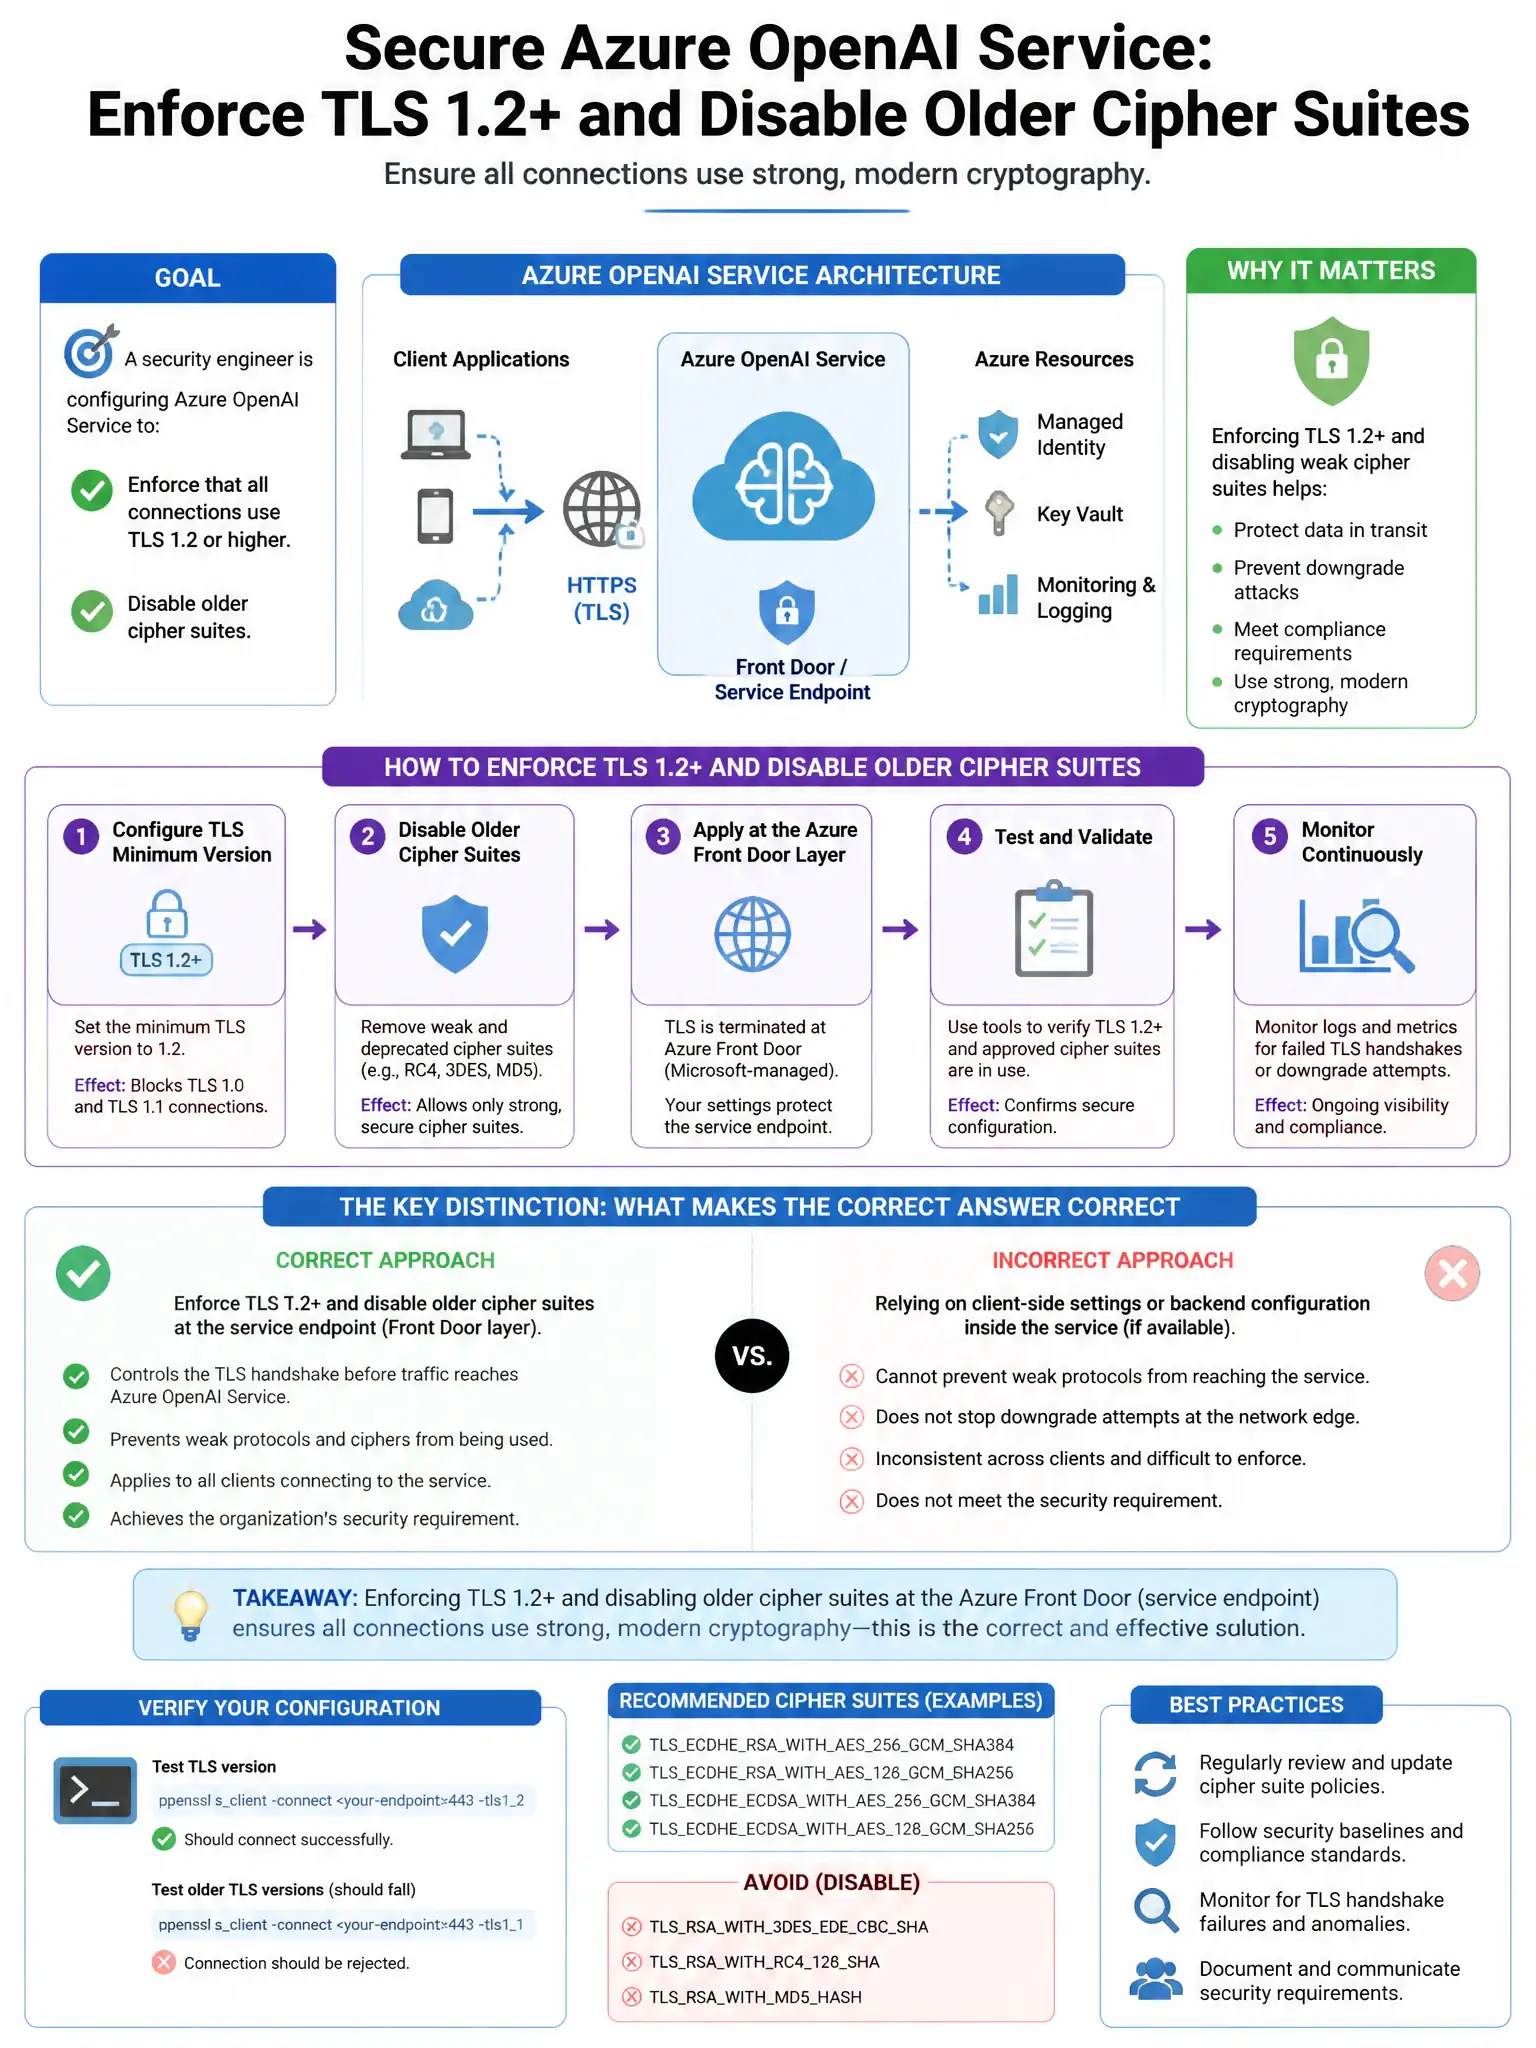
A security engineer is configuring Azure OpenAI Service and needs to enforce that all connections use TLS 1.2 or higher. The organization also wants to disable older cipher suites. Which Azure feature controls the minimum TLS version for Azure OpenAI Service?
Select an answer to reveal the explanation.
Short Explanation
Here's the deal — you set the minimum TLS version directly on the Azure OpenAI resource. That resource-level setting rejects older protocol versions when you choose TLS 1.2.
Full Explanation
The Azure OpenAI resource's minimum TLS version setting in the resource configuration is correct because Azure Cognitive Services, including Azure OpenAI Service, expose a configurable 'Minimum TLS version' setting at the resource level. This setting can be set to TLS 1.0, TLS 1.1, or TLS 1.2, and setting it to TLS 1.2 ensures that connections using older protocol versions are rejected. This configuration is available in the Azure portal under the resource's networking settings or via ARM templates. The Azure Front Door WAF policy TLS settings are wrong because they apply to the Front Door endpoint if you route traffic through Front Door; they do not directly control the TLS version of the Azure OpenAI Service endpoint itself. The Azure Application Gateway SSL policy configuration is wrong because Application Gateway SSL policies apply to the Application Gateway listener, not to the Azure OpenAI backend service. The Azure Policy for Cognitive Services TLS version enforcement is wrong because while Azure Policy can audit TLS version compliance, the actual enforcement setting is on the individual resource, not through Policy directly.