
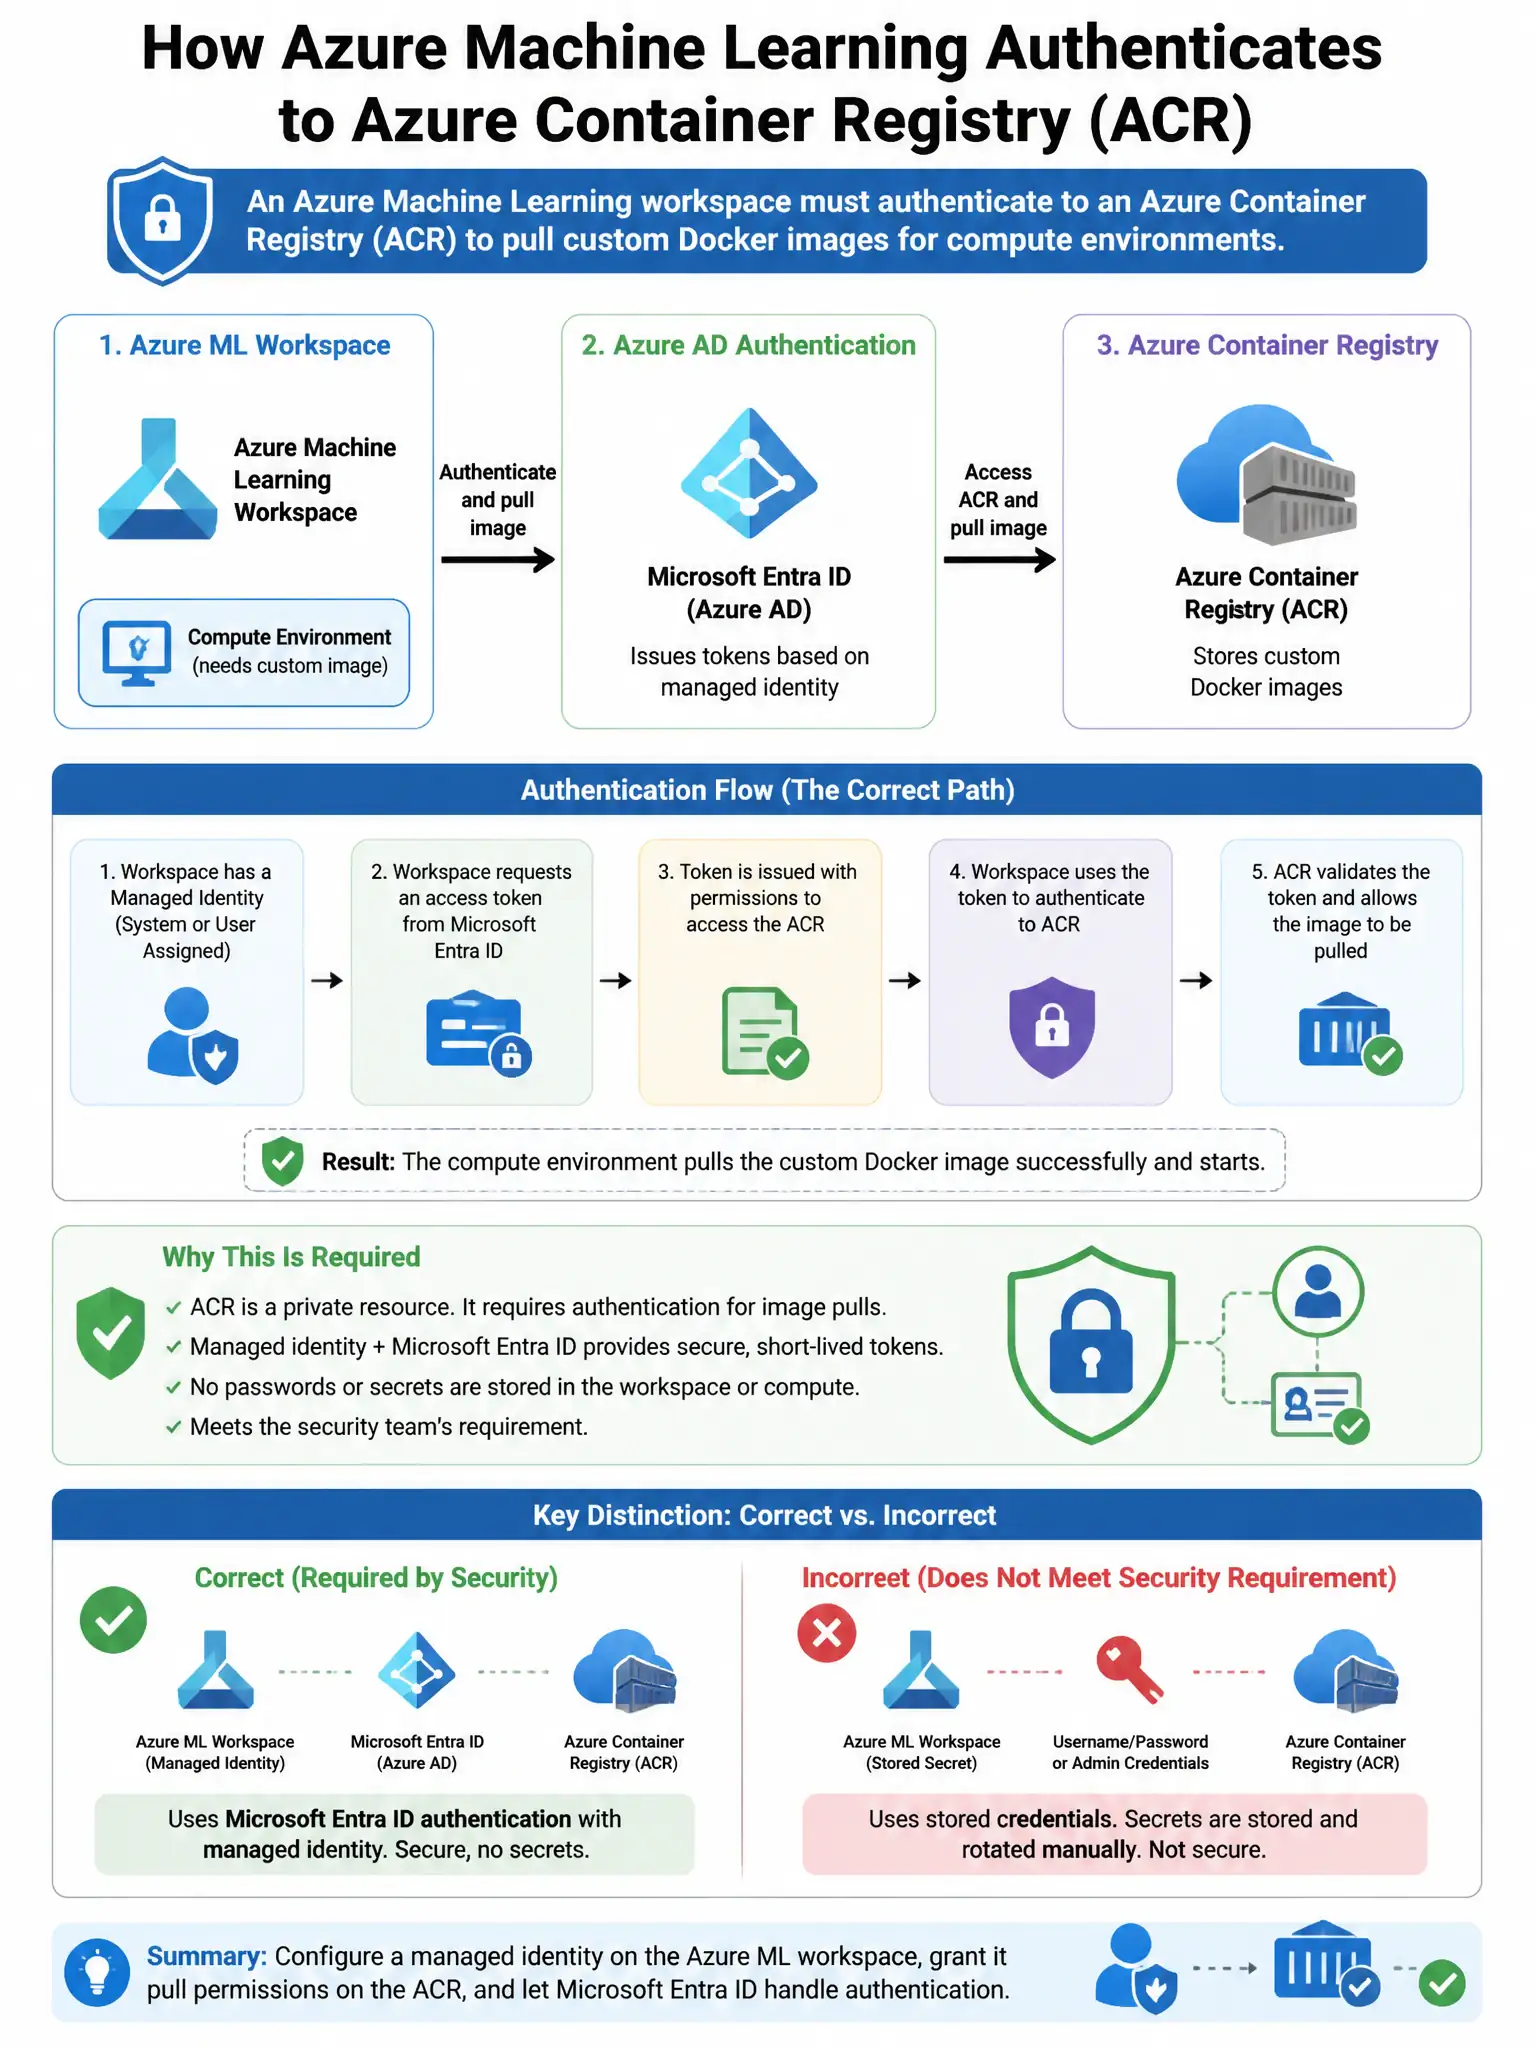
An Azure Machine Learning workspace must authenticate to an Azure Container Registry (ACR) to pull custom Docker images for compute environments. The security team requires that no service principal secrets are used. Which authentication method should be configured?
Select an answer to reveal the explanation.
Short Explanation
Here's the deal — enable the workspace's managed identity and grant it AcrPull on the registry. That lets Azure ML pull images without service principal secrets, passwords, or stored credentials.
Full Explanation
The correct method is to enable the Azure Machine Learning workspace's managed identity and grant it the AcrPull role on the Azure Container Registry. Azure ML workspaces support managed identities, and the workspace can use that identity to authenticate to ACR. Granting AcrPull lets AML pull images without stored secrets, service principal credentials, or admin account passwords, making it the most secure credential-free approach. The option that configures the ACR admin account and stores credentials in Azure Key Vault is wrong because the admin account is a static credential that should be disabled per security best practices; storing it in Key Vault reduces but does not eliminate the credential risk. The option that uses a shared access signature token for ACR authentication is wrong because SAS tokens are time-limited but still represent stored credentials that require management and rotation. The option that configures basic authentication on the ACR with a rotating password is wrong because it is credential-based and violates the requirement for no service principal secrets.