
An organization needs to implement Microsoft Purview Customer Key for Microsoft 365 to encrypt Copilot interaction data with organization-managed keys. What is a prerequisite for configuring Customer Key?
Select an answer to reveal the explanation.
Short Explanation
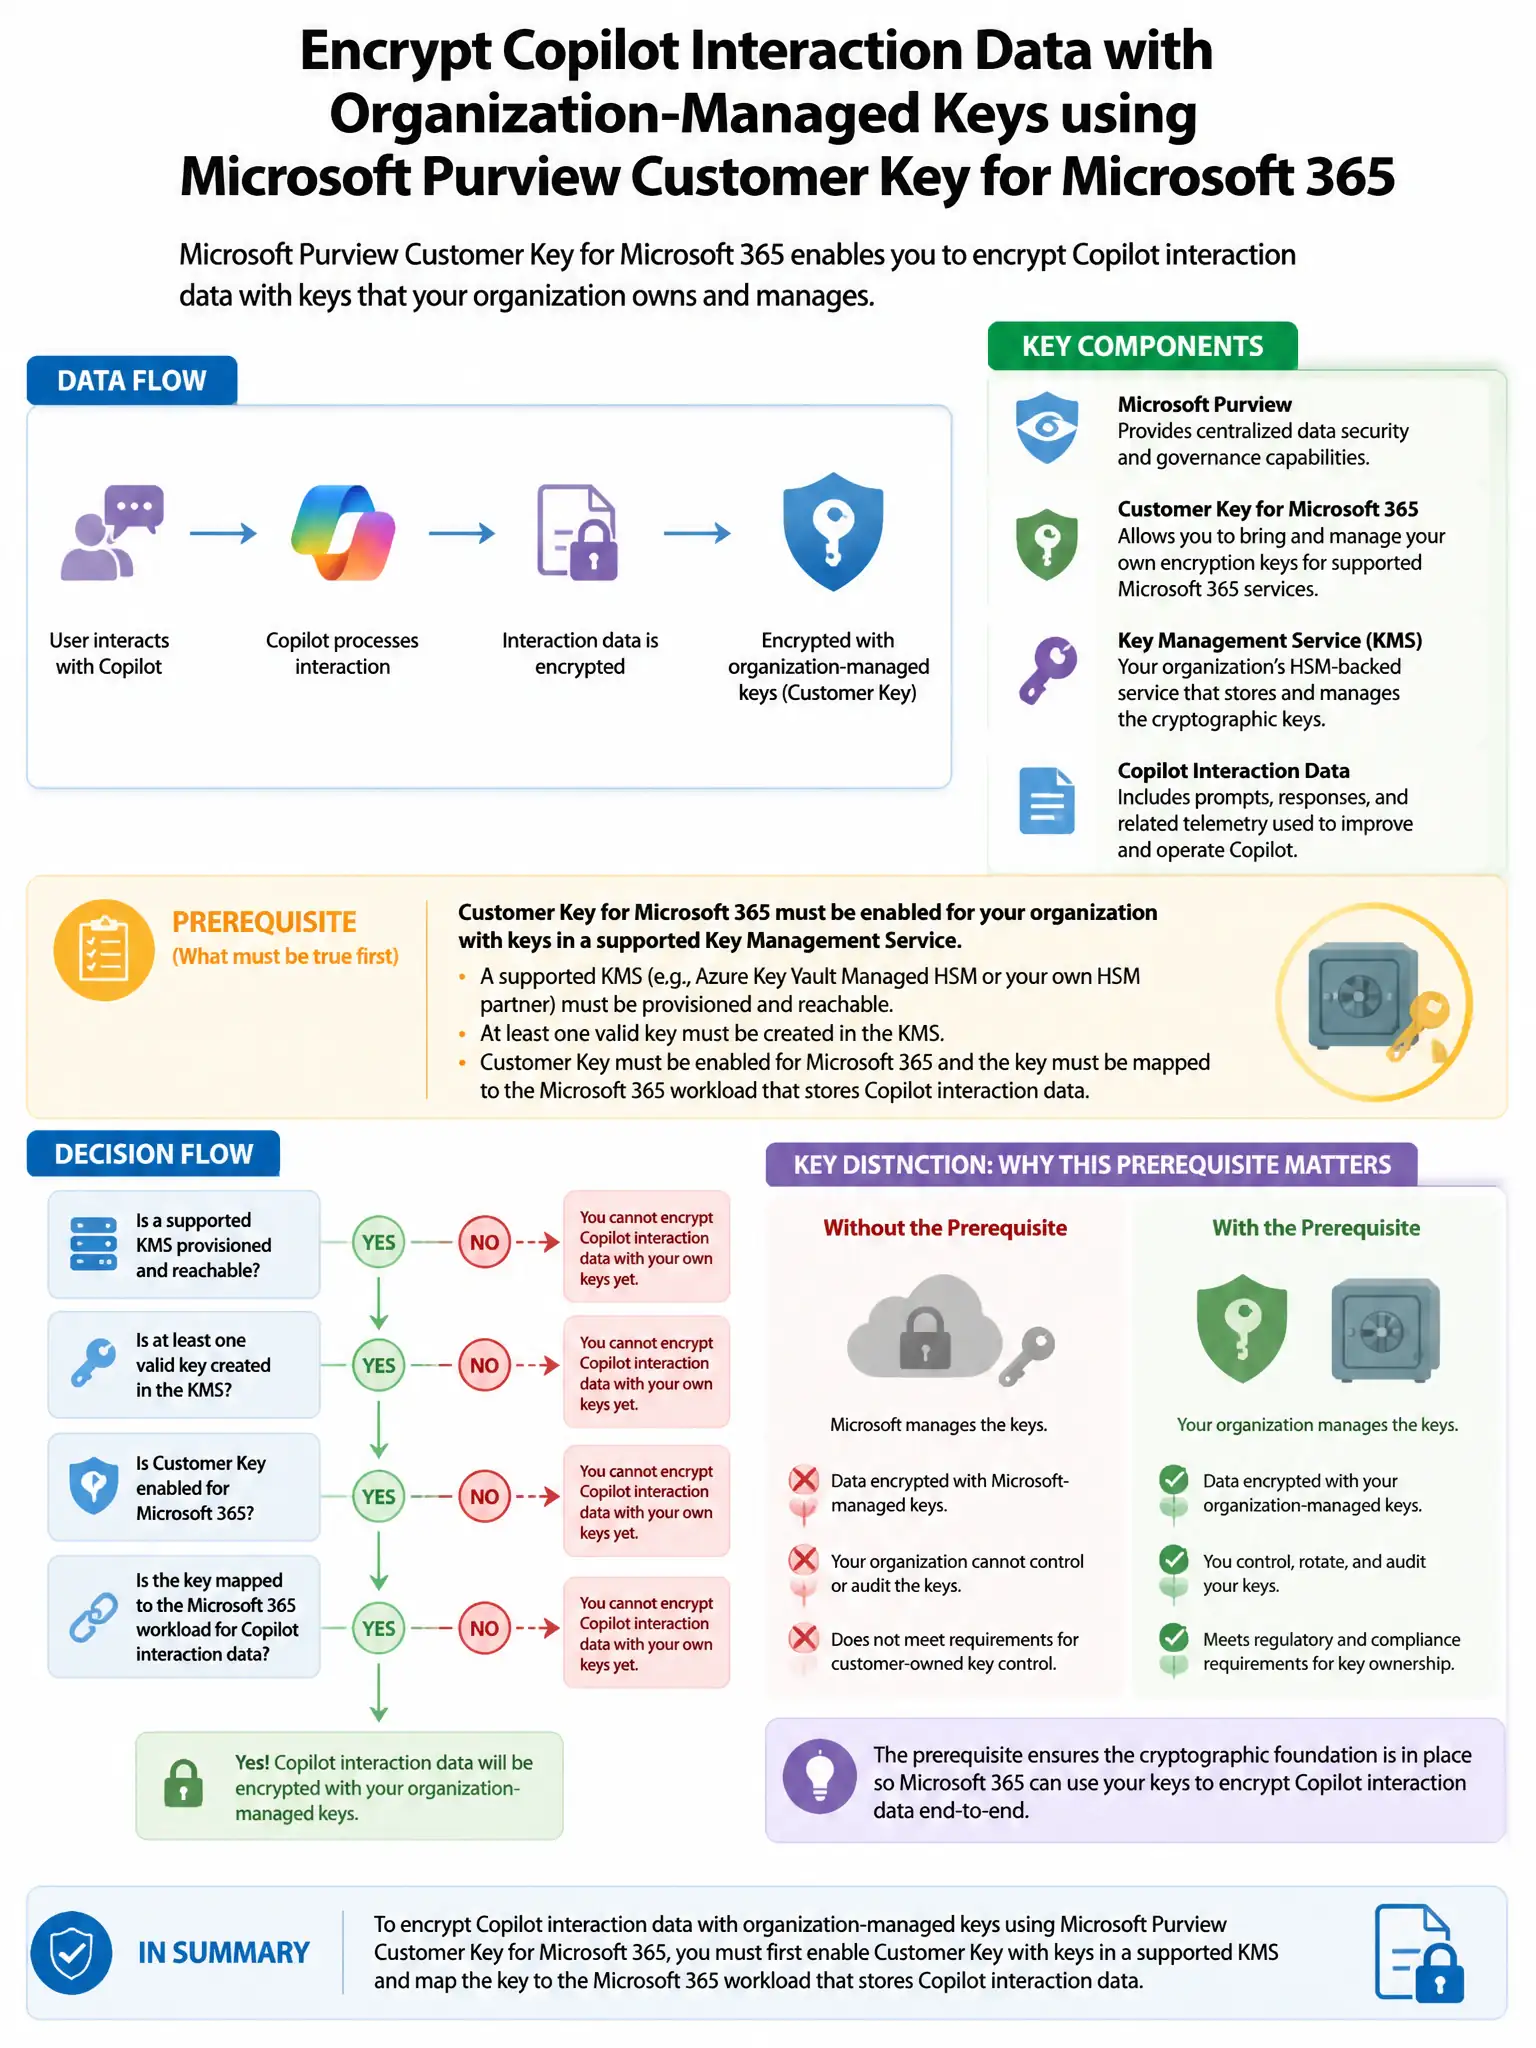
Here's the deal — you need two Azure Key Vault instances in different Azure regions, each with soft delete and purge protection enabled. That gives geographic redundancy and stops keys from being accidentally or permanently deleted before Customer Key can protect Copilot interaction data.
Full Explanation
The correct prerequisite is two Azure Key Vault instances in two different Azure regions with purge protection and soft delete enabled. Microsoft 365 Customer Key requires this geographic redundancy, and each Key Vault must have soft delete enabled to prevent accidental key deletion and purge protection enabled to prevent hard deletion of keys for a minimum retention period. These prerequisites ensure key availability and resilience before Customer Key can be configured for Microsoft 365 services, including Copilot. The Microsoft 365 E3 license minimum is wrong because Customer Key for Microsoft 365 requires Microsoft 365 E5, or the Microsoft 365 E5 Compliance add-on, not E3. The Microsoft Entra ID P2 license for all affected users is wrong because Entra ID P2 is required for features such as Privileged Identity Management and Identity Protection, not for configuring Customer Key. The Azure Information Protection scanner deployment is wrong because the scanner is used for discovering and labeling on-premises files; it is not a prerequisite for Customer Key configuration.