
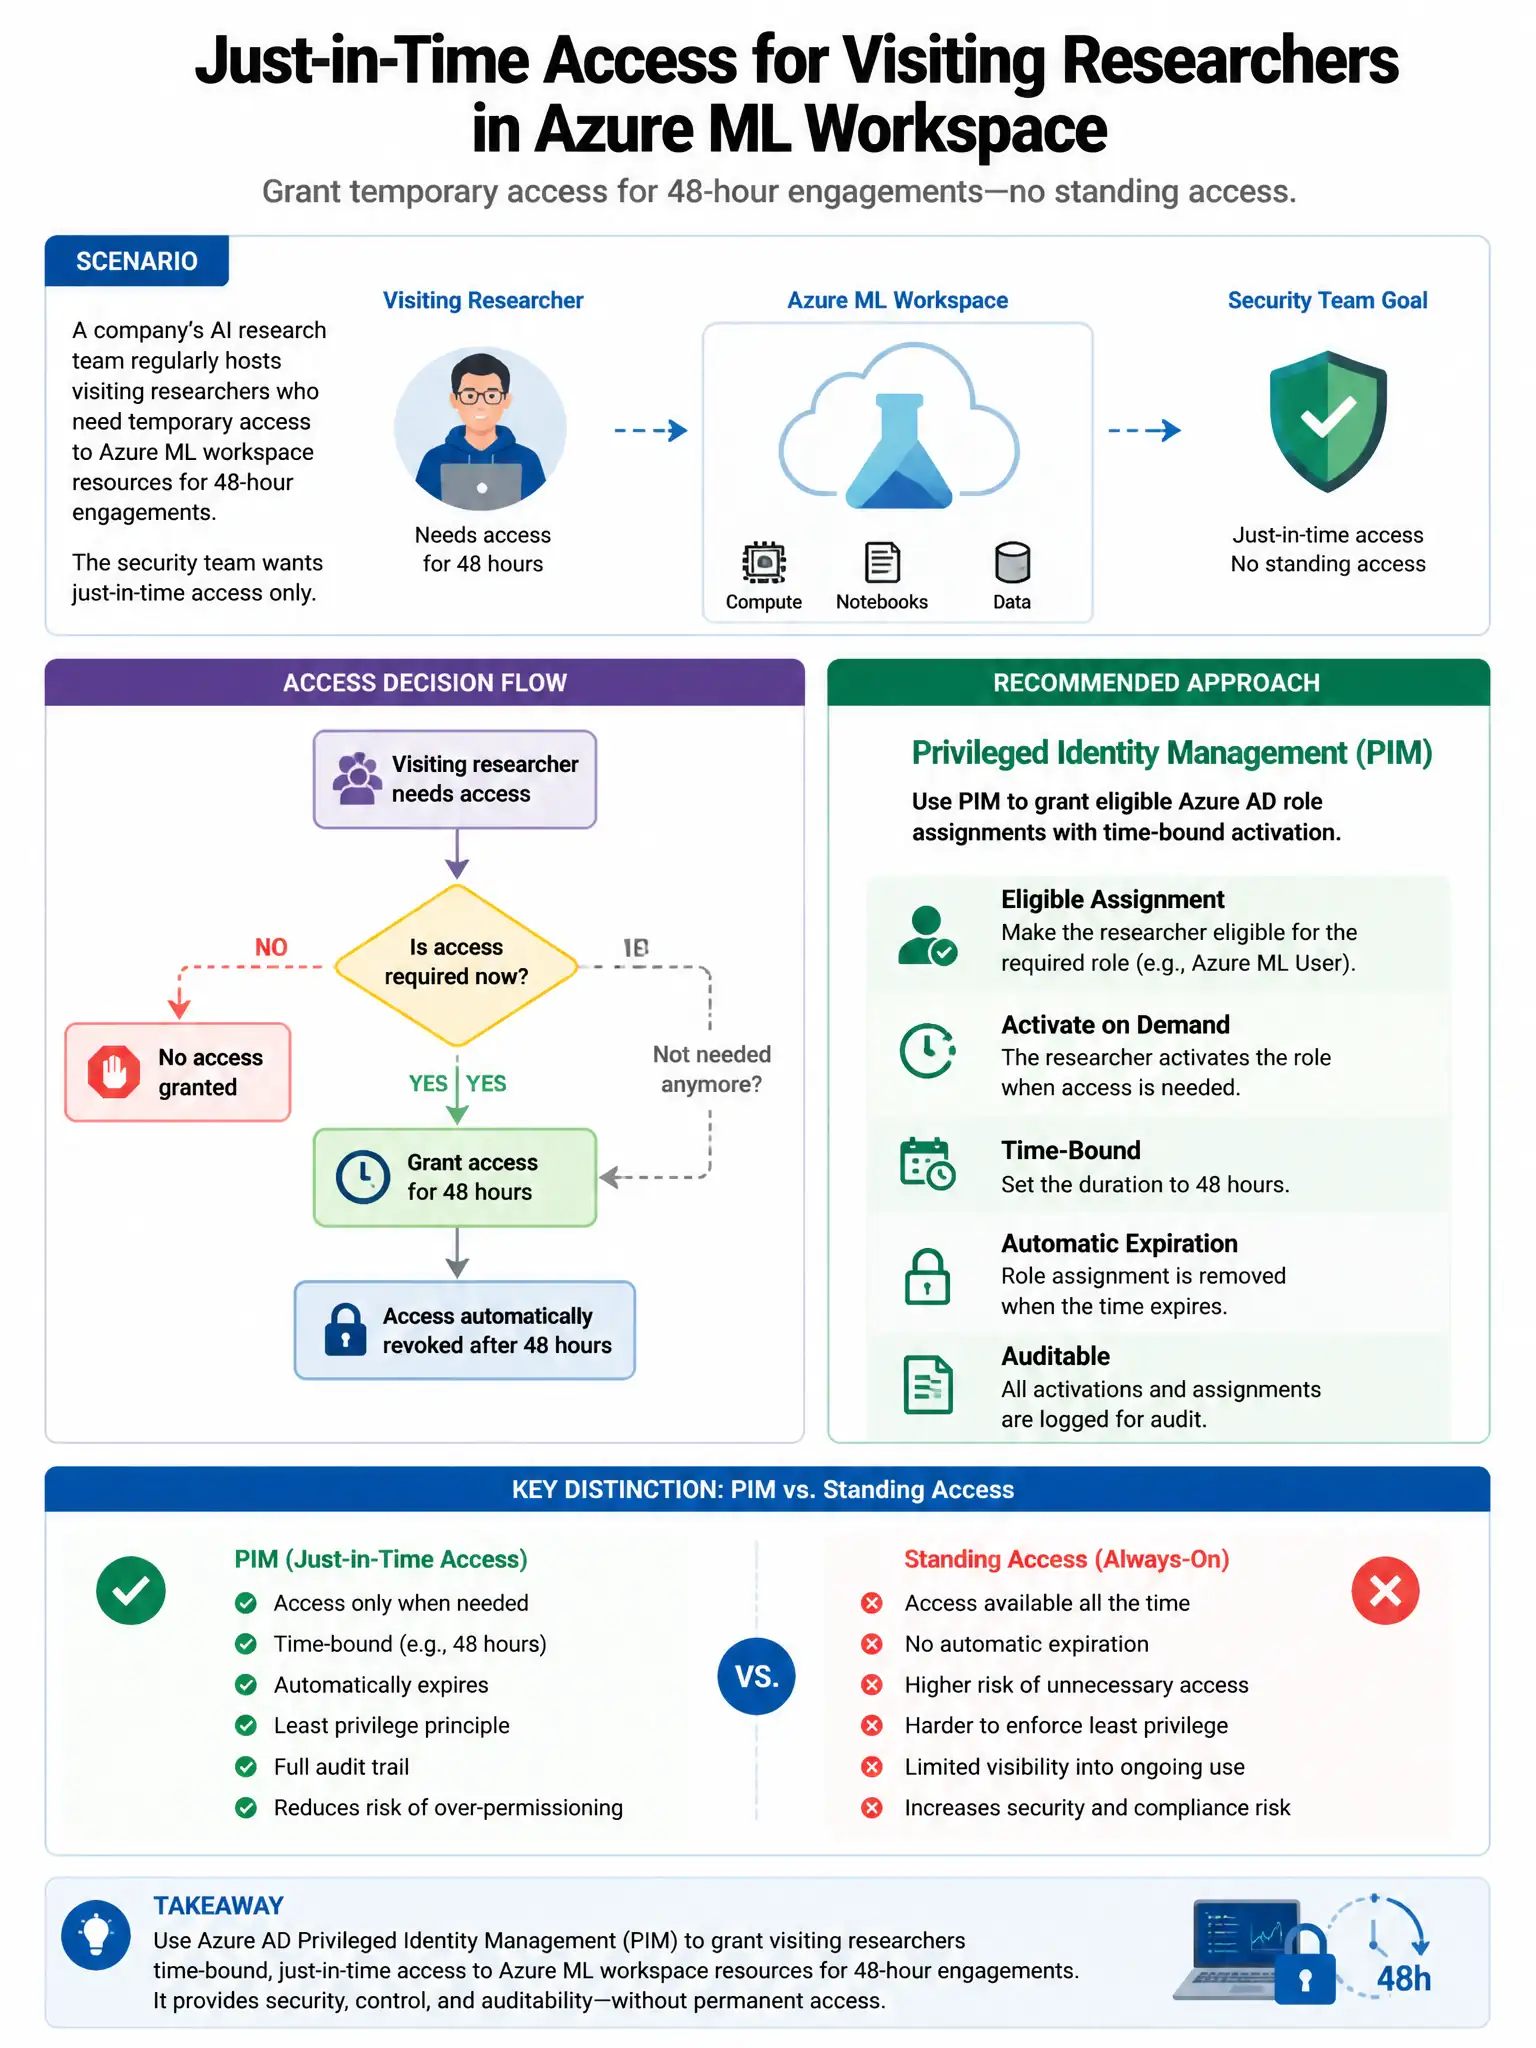
A company's AI research team regularly has visiting researchers who need temporary access to Azure ML workspace resources for 48-hour engagements. The security team wants just-in-time access with automatic expiration. Which Microsoft Entra ID capability is most appropriate?
Select an answer to reveal the explanation.
Short Explanation
Here's the deal — you want the access package approach in Microsoft Entra ID Governance Entitlement Management because it bundles Azure ML workspace resources and expires after 48 hours automatically. That gives you just-in-time access for guests without manual cleanup.
Full Explanation
The access package approach in Microsoft Entra ID Governance Entitlement Management is correct because it lets you bundle resources, such as Azure ML workspace group membership, into an access package and configure a policy with a maximum access duration of 48 hours. External users or guests can request the access package, and access automatically expires after the configured duration, removing access without manual intervention. The guest invitation paired with a 48-hour temporary access pass is wrong because a Temporary Access Pass is a time-limited passcode used for initial device setup or account recovery, not for granting access to Azure ML resources. The PIM time-bound active global admin role for two days is wrong because PIM time-bound active assignments are appropriate for Azure RBAC or Entra roles, not for flexible researcher onboarding at scale with self-service request workflows, and granting global admin for two days is far too broad for temporary Azure ML workspace access. The manual group membership with a calendar reminder to remove access after 48 hours is wrong because manual processes with calendar reminders are error-prone and do not scale or provide automated enforcement.