
A company deploys an AI application on Azure App Service. The application uses a service principal to authenticate to Azure AI services. The security team wants to prevent this service principal's tokens from being used from outside the corporate network. Which Entra ID feature enforces this restriction?
Select an answer to reveal the explanation.
Short Explanation
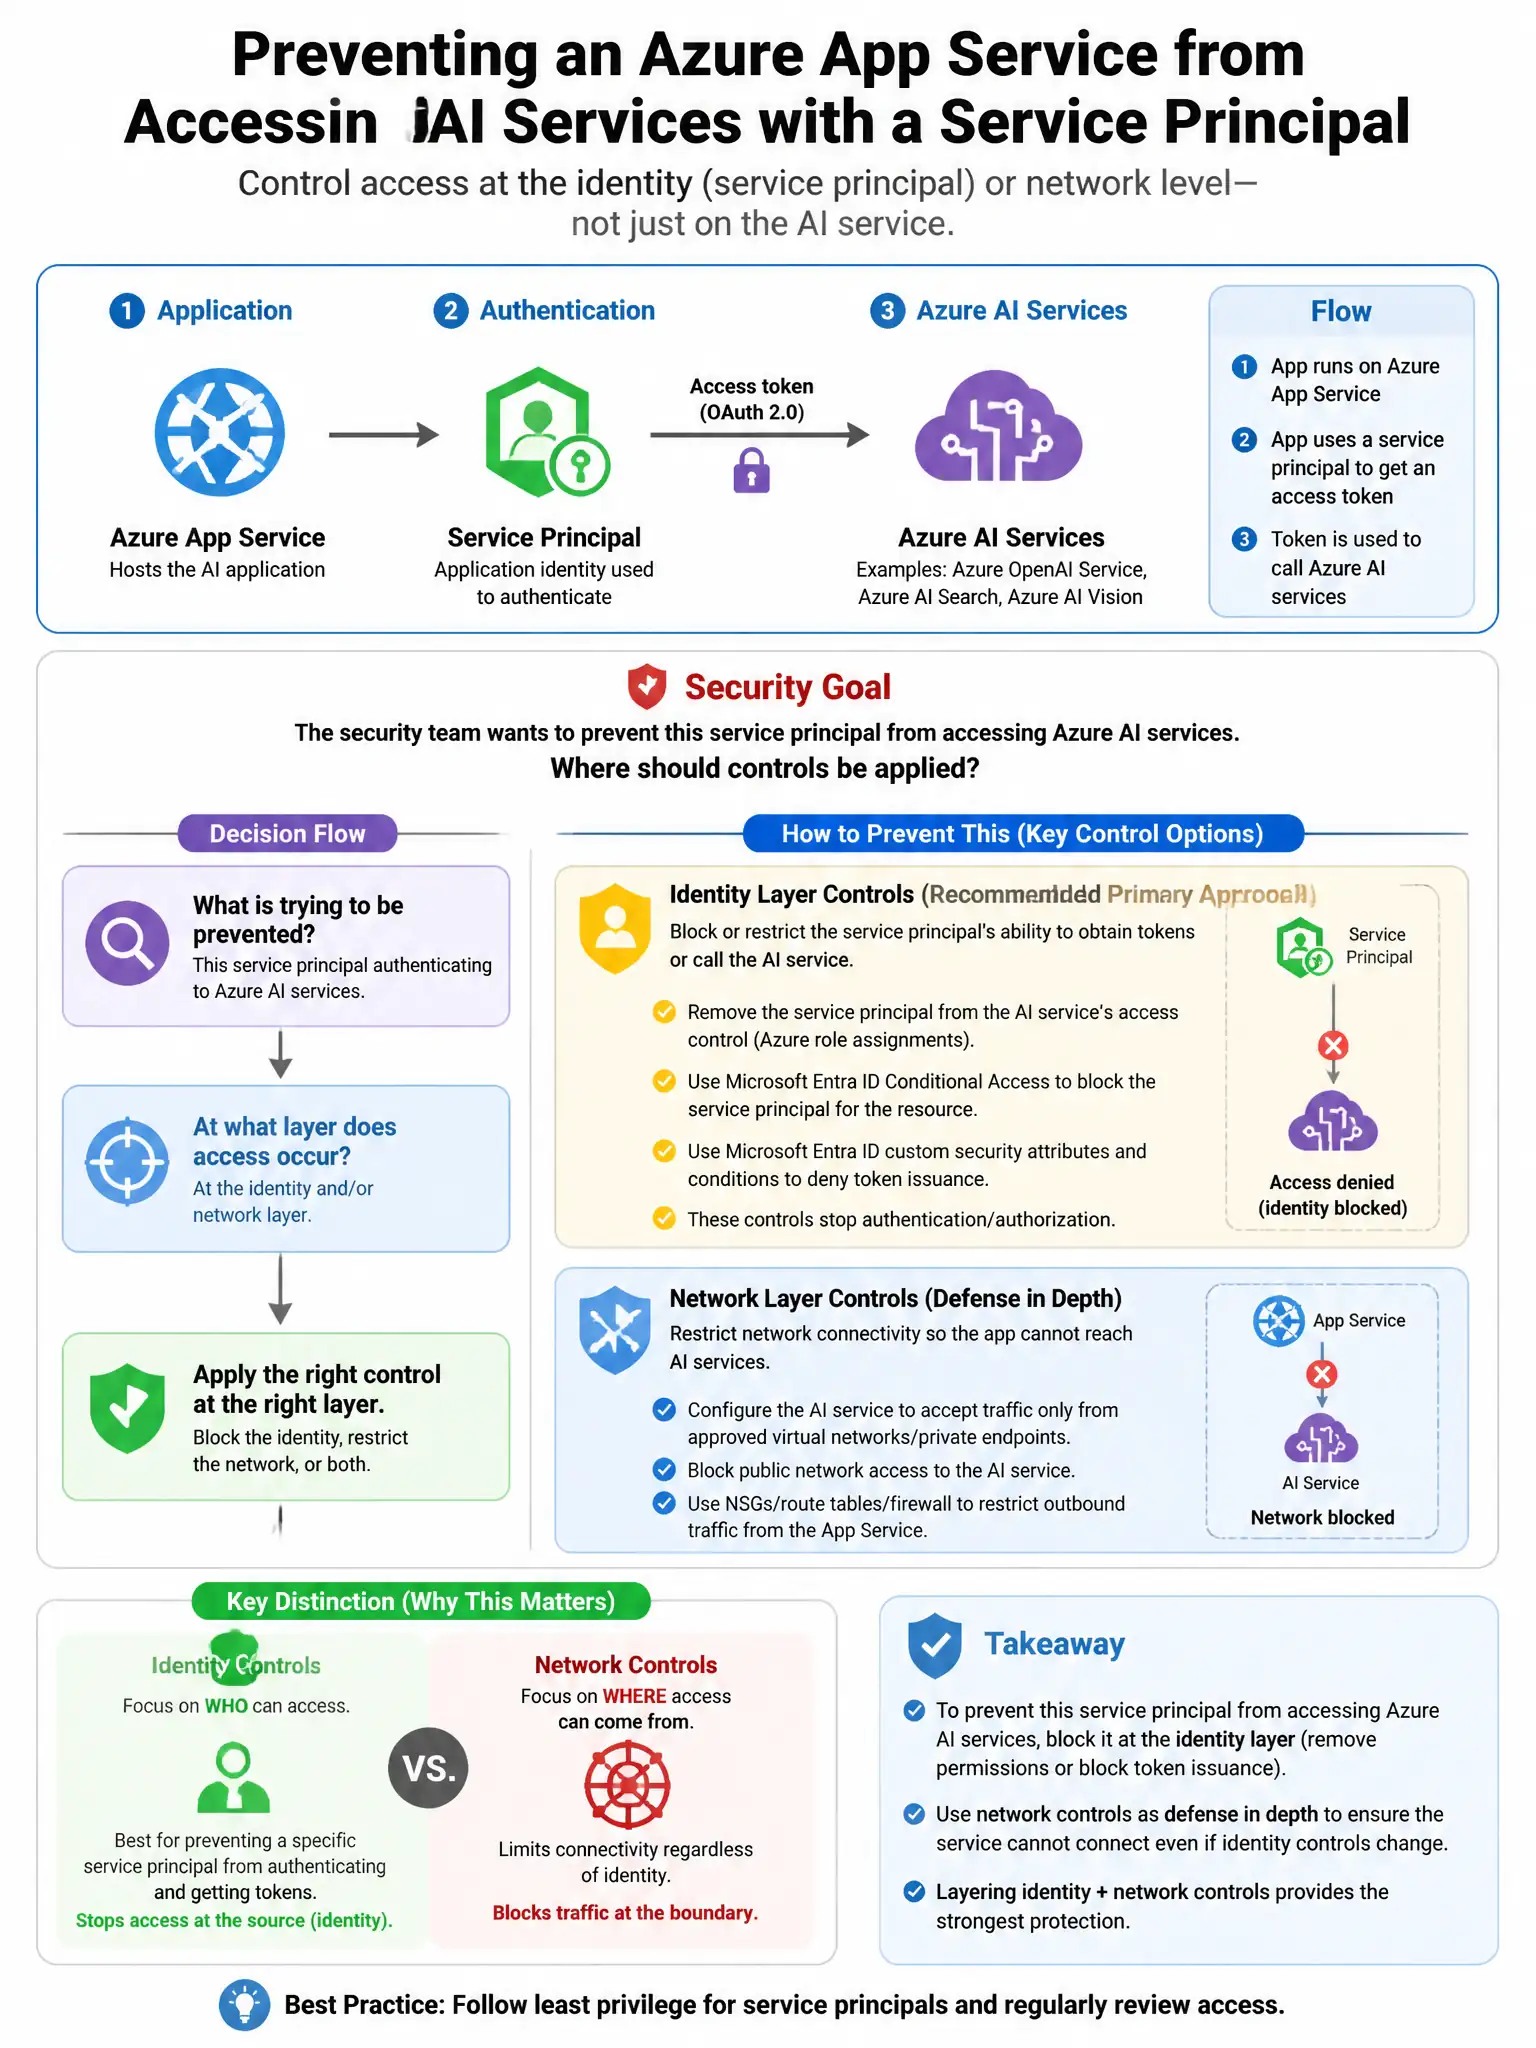
Here's the deal — you need Conditional Access for workload identities with location-based conditions. It blocks the service principal from getting tokens when the request comes from outside your named corporate locations, so tokens can't be used off-network.
Full Explanation
The correct approach is Microsoft Entra Conditional Access for workload identities with location-based conditions, available with Microsoft Entra Workload ID Premium. It lets you apply Conditional Access policies to service principals, so you can block the service principal from obtaining tokens when the request originates from outside named locations, such as corporate IP ranges, preventing token misuse from outside the network. The Microsoft Entra ID Protection user risk policy for service principals is wrong because user risk policies apply to user identities, not service principals; workload identity risk requires the Workload ID Premium feature and specific configuration. The Azure Active Directory Application Proxy network restriction is wrong because Azure AD Application Proxy provides secure remote access to on-premises web apps; it does not restrict where service principal tokens can be used for Azure AI service calls. The Privileged Identity Management for service principal role assignments option is wrong because it manages when a service principal can have an active role assignment, not the network location from which its tokens are used.