
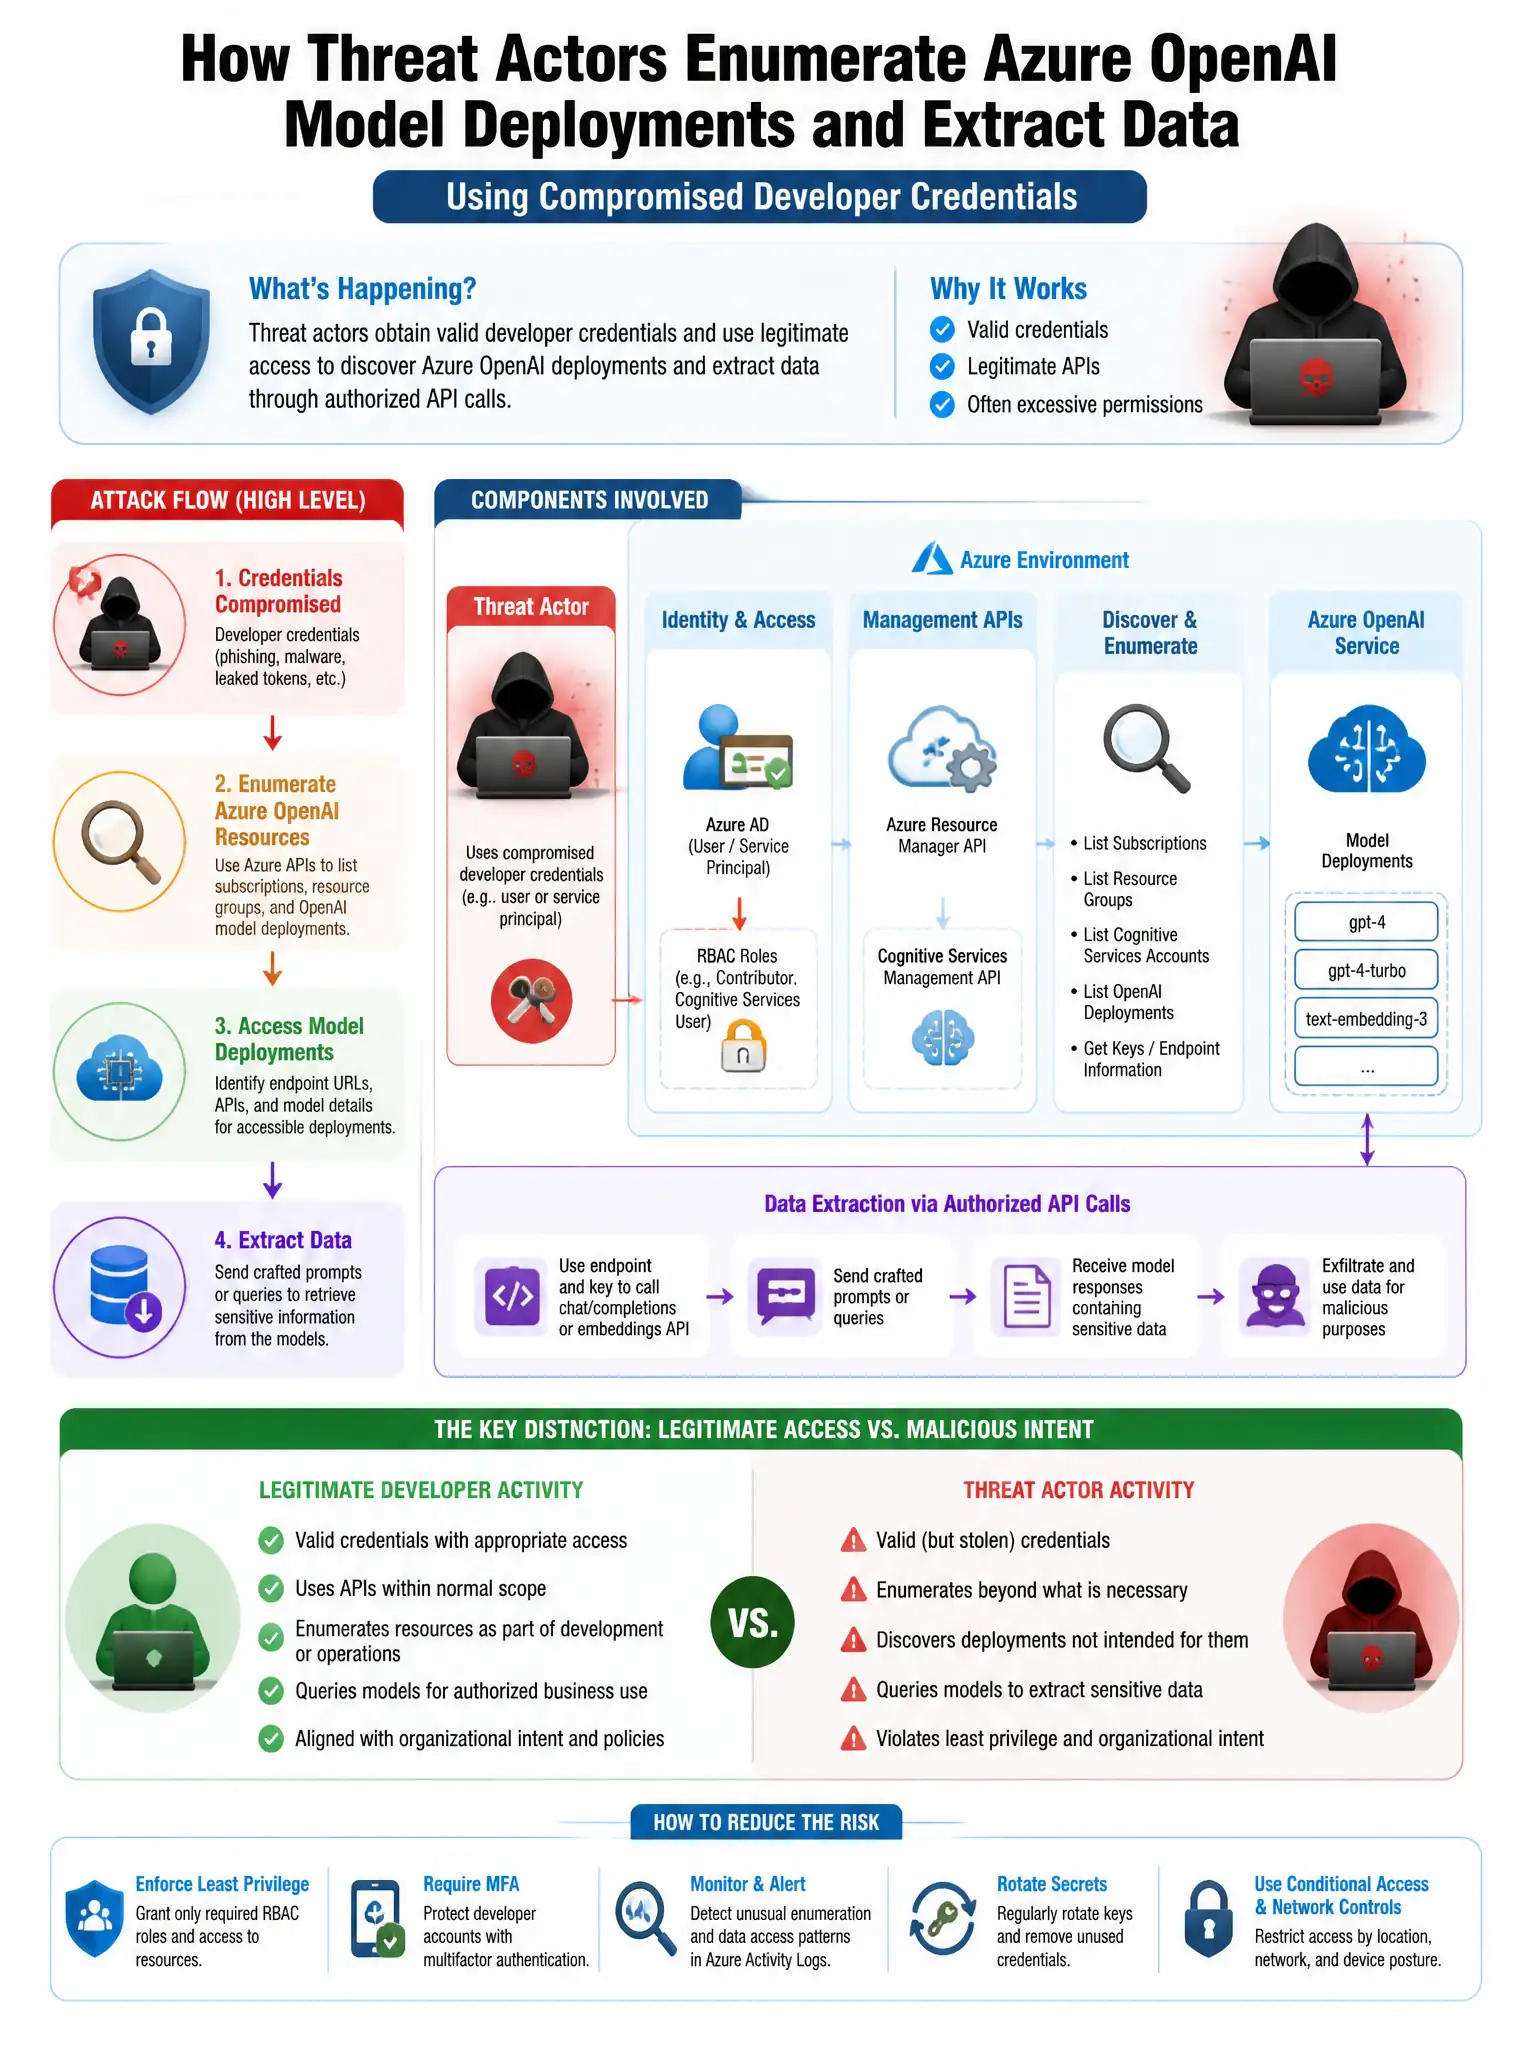
An organization's security team has identified a pattern where threat actors are using compromised developer credentials to enumerate Azure OpenAI model deployments and extract prompt configurations. Which Microsoft Sentinel data connector and analytic approach best detects this reconnaissance activity?
Select an answer to reveal the explanation.
Short Explanation
Here's the deal — you need Azure Activity logs because enumerating Azure OpenAI deployments is a control plane operation. Connect those logs to Sentinel and alert on ListDeployments calls from anomalous locations.
Full Explanation
The Azure Activity logs connector with an analytics rule detecting ListDeployments operations from anomalous locations is correct because enumerating Azure OpenAI deployments is a control plane operation recorded in Azure Activity logs, which capture management plane API calls. These include ListDeployments calls to the Azure OpenAI management API. By connecting Azure Activity logs to Sentinel and writing an analytics rule that flags frequent ListDeployments operations from unusual IP addresses or locations compared to a baseline, the team can detect reconnaissance of AI model configurations. The Microsoft Defender for Endpoint option is wrong because Defender for Endpoint monitors endpoint telemetry, while enumeration of Azure OpenAI management APIs is a cloud control plane activity, not endpoint activity. The Azure AD Sign-in logs option is wrong because failed MFA attempts indicate authentication attacks, not post-authentication API enumeration. The Microsoft 365 Defender option is wrong because Microsoft 365 Defender monitors Microsoft 365 workloads, while enumeration of Azure OpenAI management endpoints is captured in Azure Activity logs, not Microsoft 365 telemetry.