
A security operations analyst is using Microsoft Sentinel to detect anomalous usage of Azure OpenAI Service. The analyst wants to create an analytics rule that alerts when the number of Azure OpenAI API calls from a single IP address exceeds 10,000 within one hour. Which Sentinel analytics rule type is most appropriate?
Select an answer to reveal the explanation.
Short Explanation
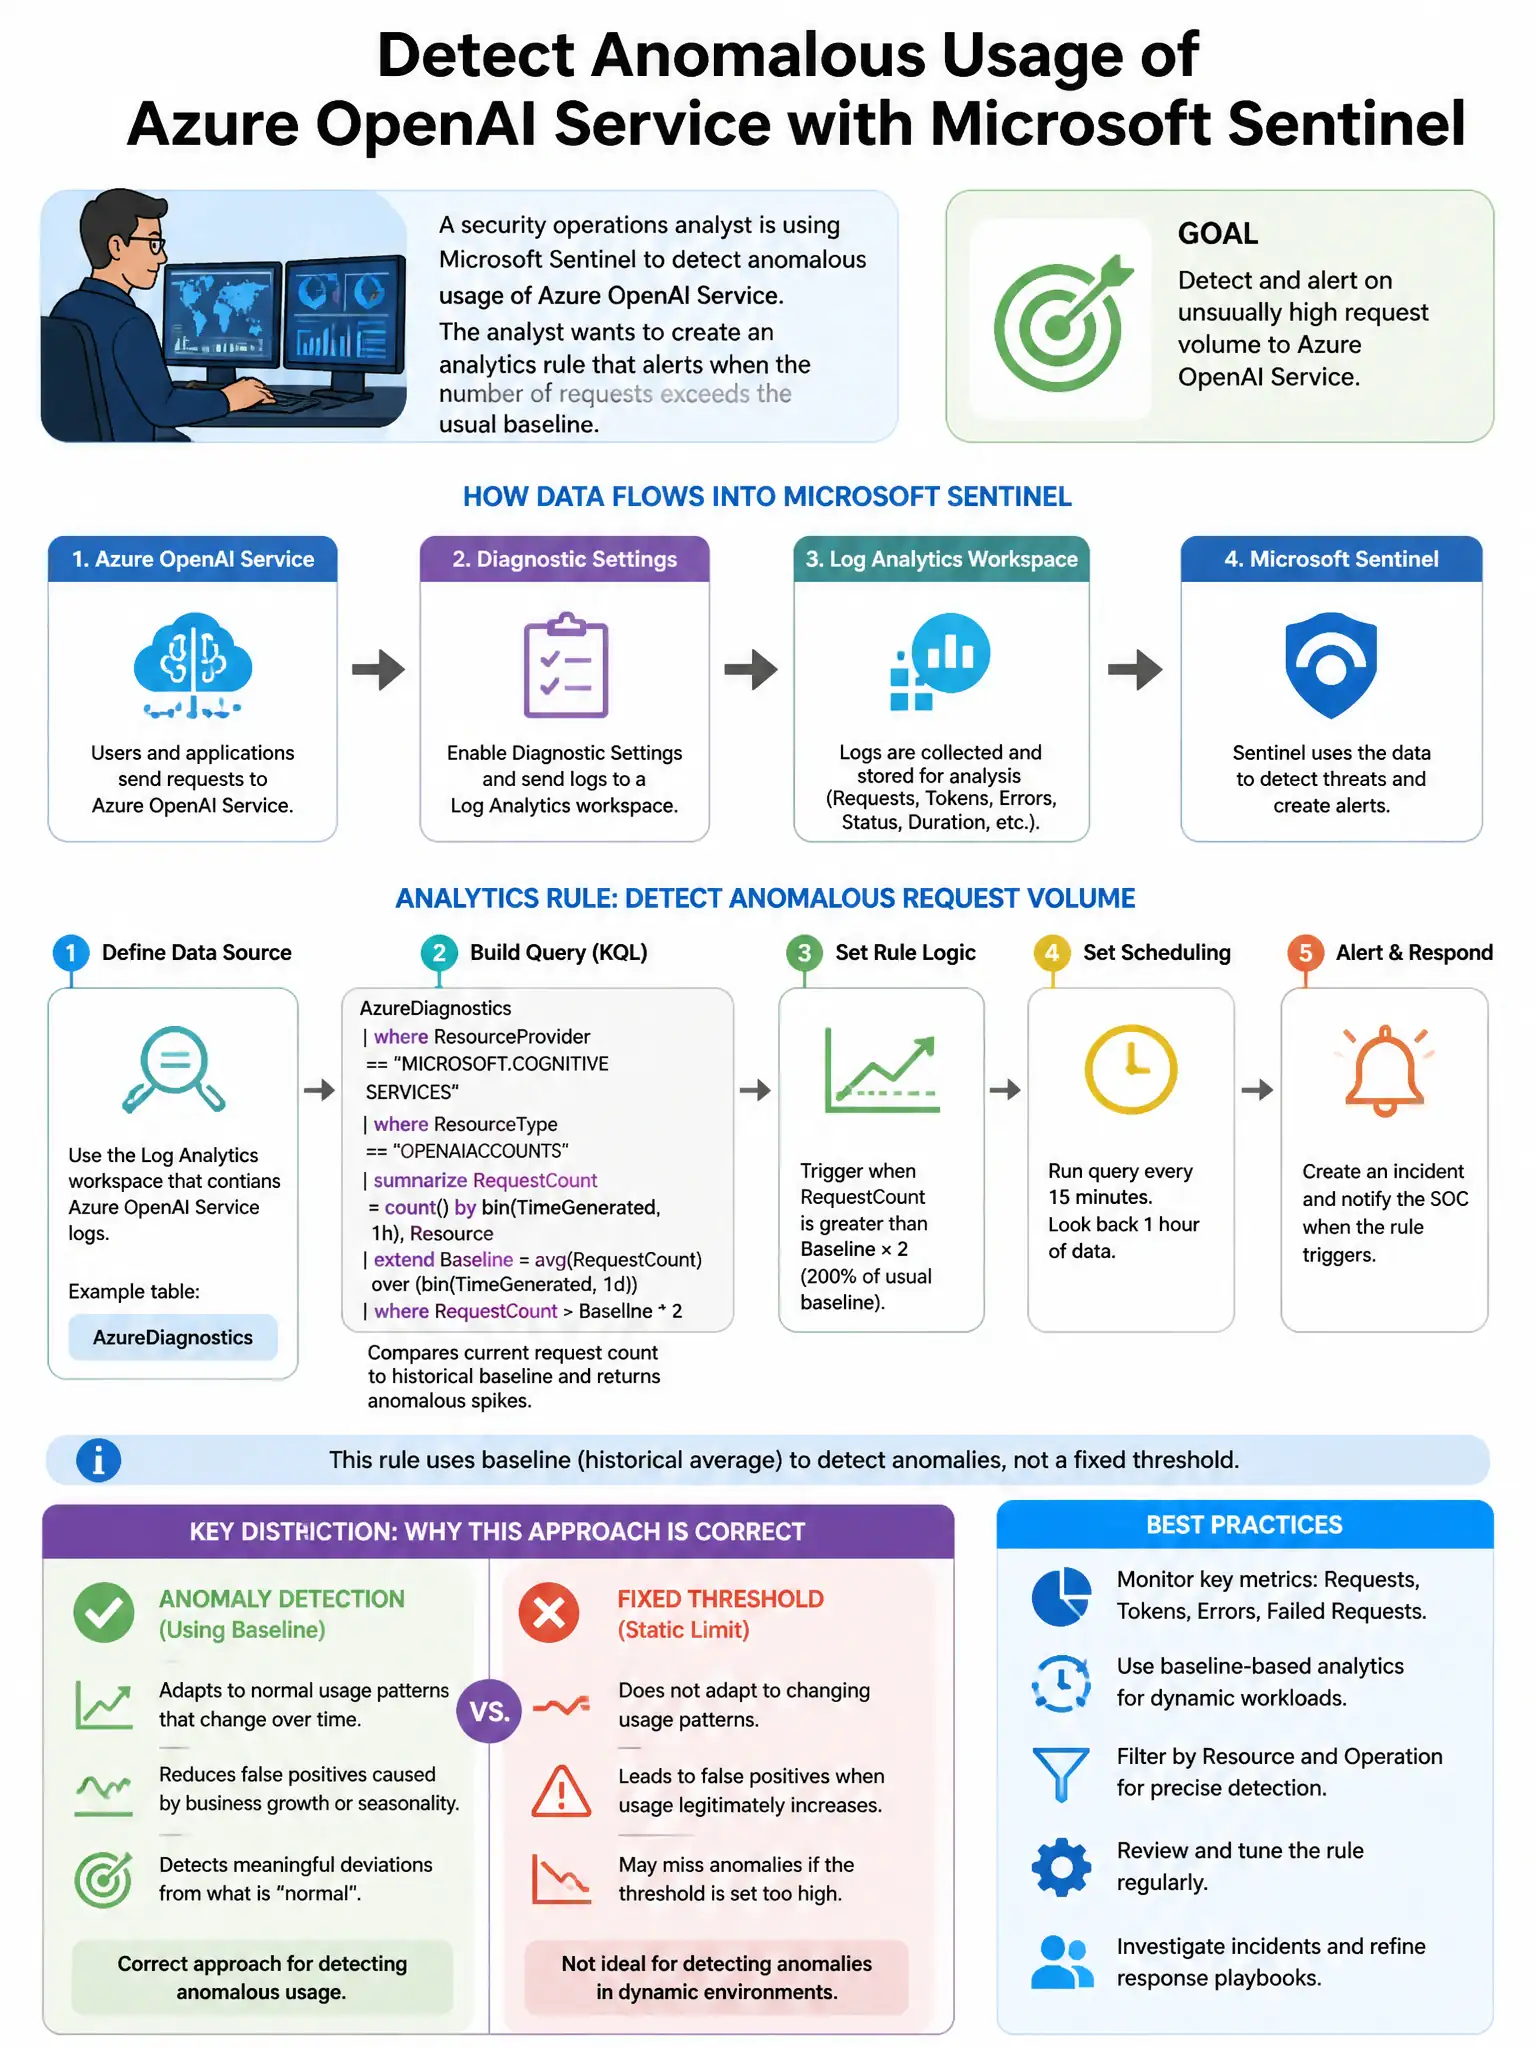
Here's the deal — a scheduled analytics rule with a KQL query and threshold configuration is what you want because it runs your query on a schedule, like hourly, against Azure OpenAI diagnostic logs and alerts when one IP crosses 10,000 calls. That's the standard way to catch threshold-based volume abuse.
Full Explanation
A scheduled analytics rule with a KQL query and threshold configuration is correct because it runs a KQL query on a defined schedule (e.g., every hour) against ingested logs (Azure OpenAI diagnostic logs) and fires an alert when the query results meet a defined threshold (>10,000 calls per IP per hour). This is the standard approach for threshold-based volume detection. A Fusion rule is wrong because Fusion rules correlate signals from multiple data sources to detect multi-stage attacks; they cannot be configured with custom thresholds for a single data source pattern. An ML behavior analytics rule is wrong because ML behavior analytics rules use machine learning to detect anomalies across users and hosts (UEBA); they do not support custom threshold logic. A near real-time (NRT) rule is wrong because NRT rules provide low-latency alerting (near real-time) but are still KQL-based and appropriate when sub-minute detection is required; the question asks for a one-hour window, so a scheduled rule is more appropriate.