
A company's security team needs to review all interactions users have with Microsoft Copilot for Microsoft 365, including the prompts submitted and responses generated, to investigate a potential policy violation. Which Microsoft service provides access to this audit data?
Select an answer to reveal the explanation.
Short Explanation
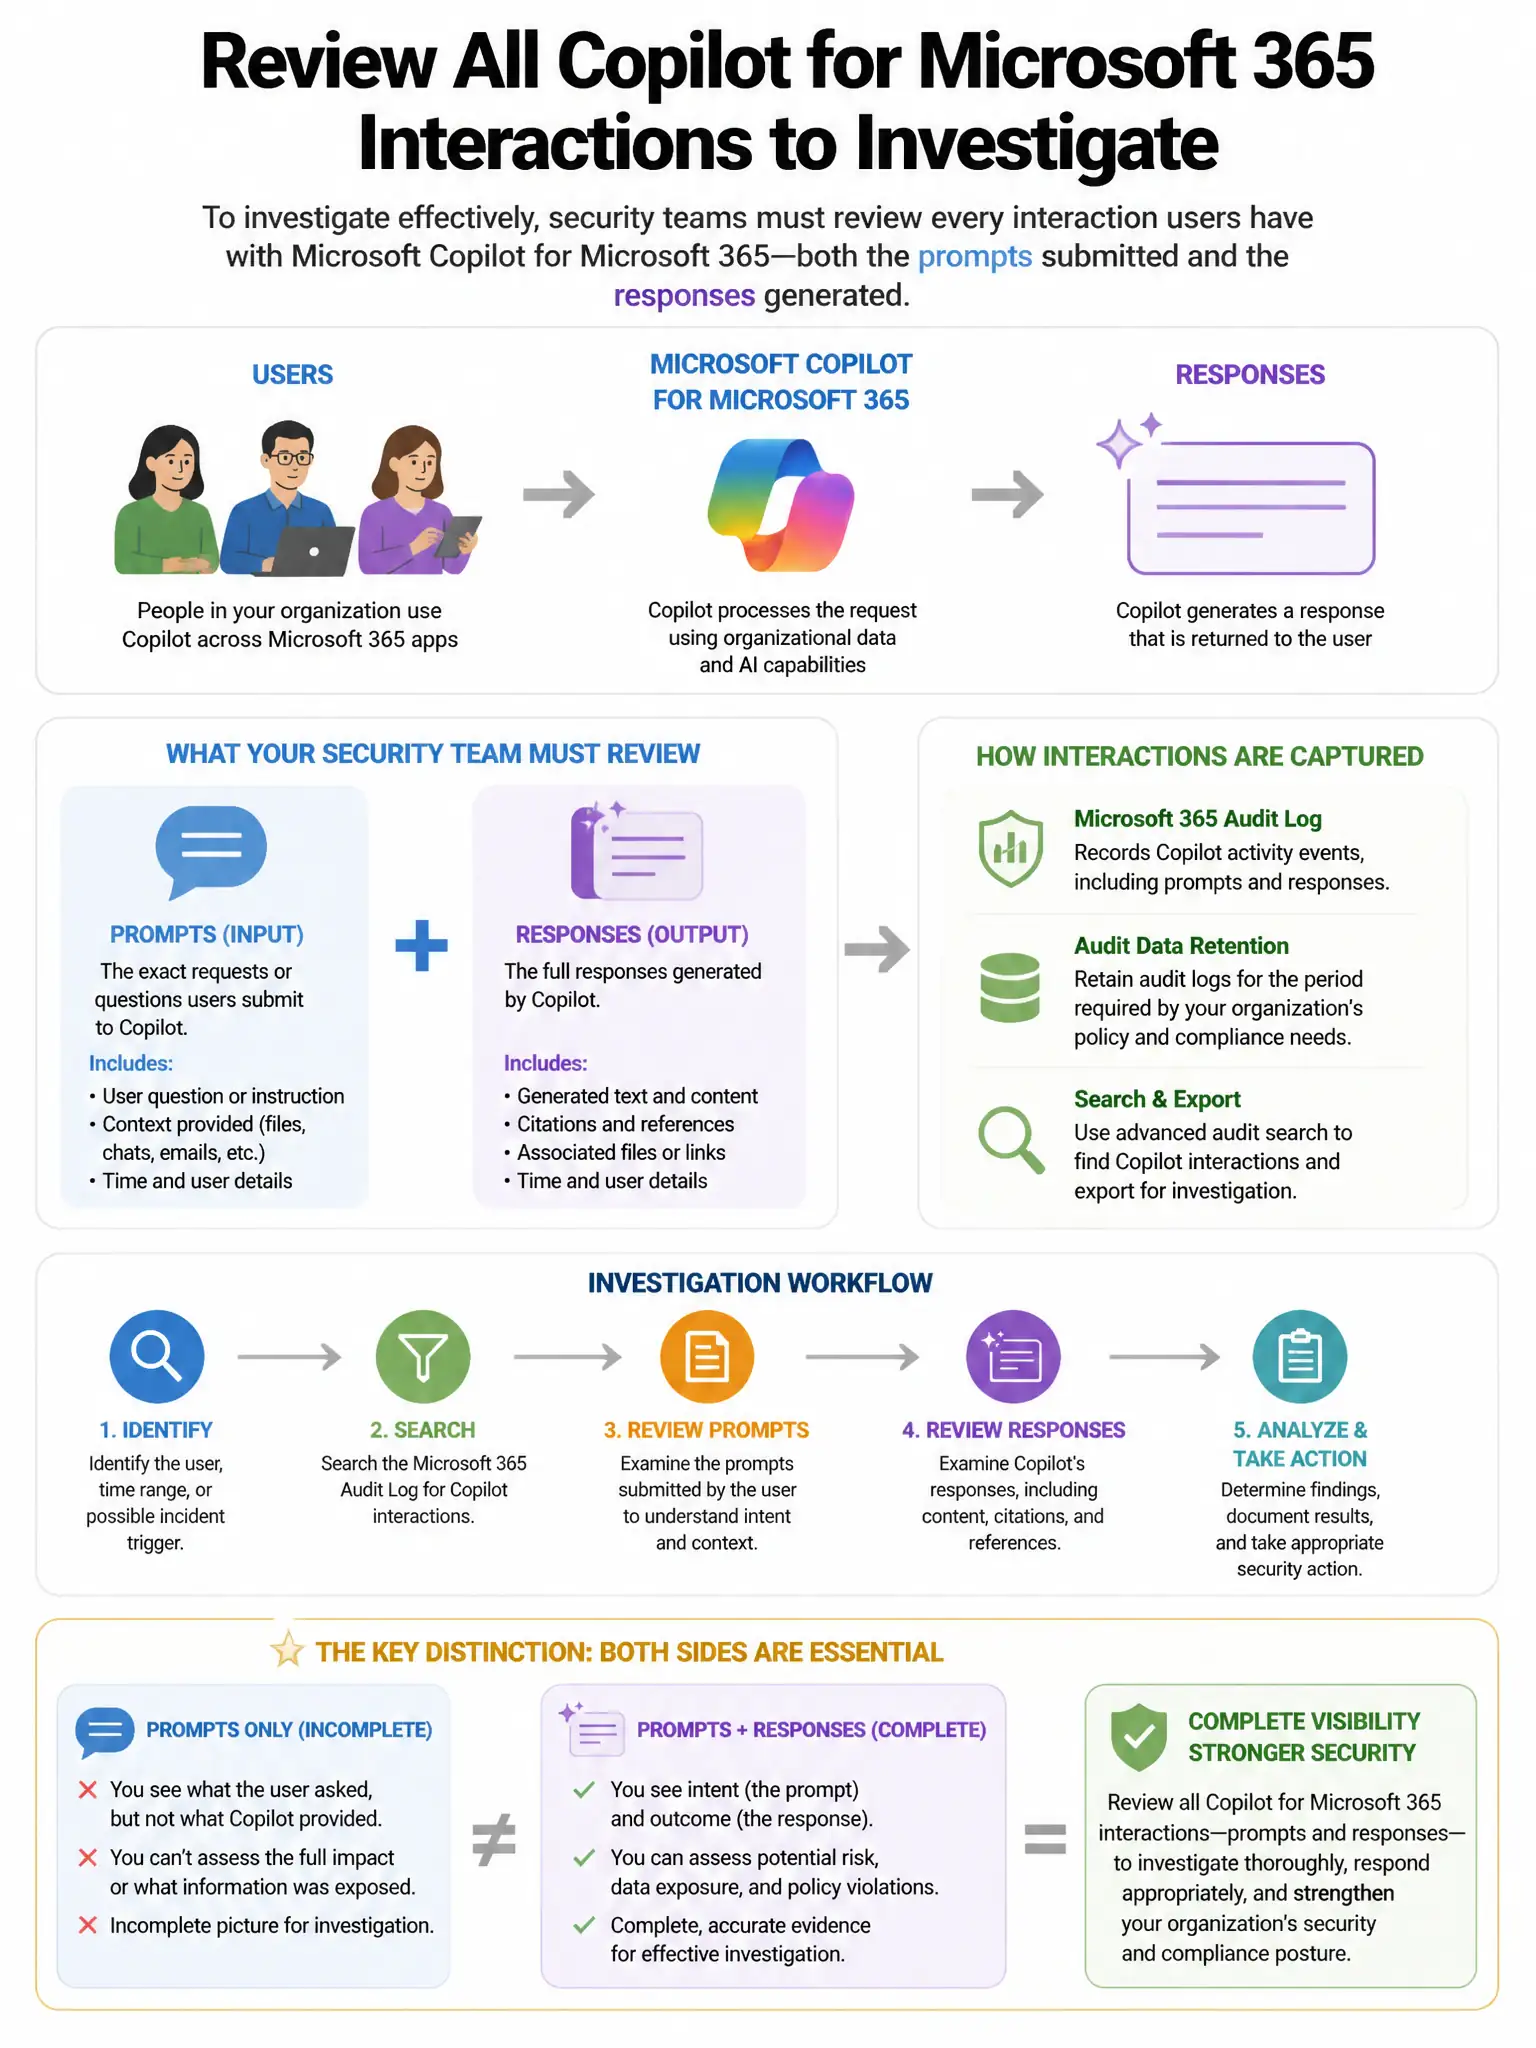
Here's the deal — if you need to review every Copilot prompt and response for a policy investigation, you go to Microsoft Purview Audit (Premium). It captures Copilot interaction events in the unified audit log, including the prompts users submitted and the AI-generated responses.
Full Explanation
Microsoft Purview Audit (Premium) is the correct service because it captures Copilot interaction events in the unified audit log, including the user prompts sent to Copilot and the AI-generated responses, enabling compliance investigations. Copilot interaction records are surfaced through the CopilotInteraction audit schema. Microsoft Defender XDR Advanced Hunting is wrong because it contains endpoint and identity security telemetry, not Copilot conversation logs. Microsoft Entra ID Sign-in logs are wrong because they record authentication events, not the content of Copilot sessions. Microsoft Defender for Cloud Apps Activity log is wrong because it records app-level governance events, not the full content of individual Copilot prompts and responses.