
A school-district CI must keep Azure Databricks CLI production deploys tightly governed. Which control is appropriate?
Select an answer to reveal the explanation.
Short Explanation
Production CLI deploy is the district vault key—you'll keep it on protected main with approvals, not after approvals in development workspace that can't govern production. Don't authenticate production deploy with a personal access token since it's tied to you and isn't a governed pipeline identity. You'll still run validate and dry-run checks in development, but they won't lock down production by themselves.
Full Explanation
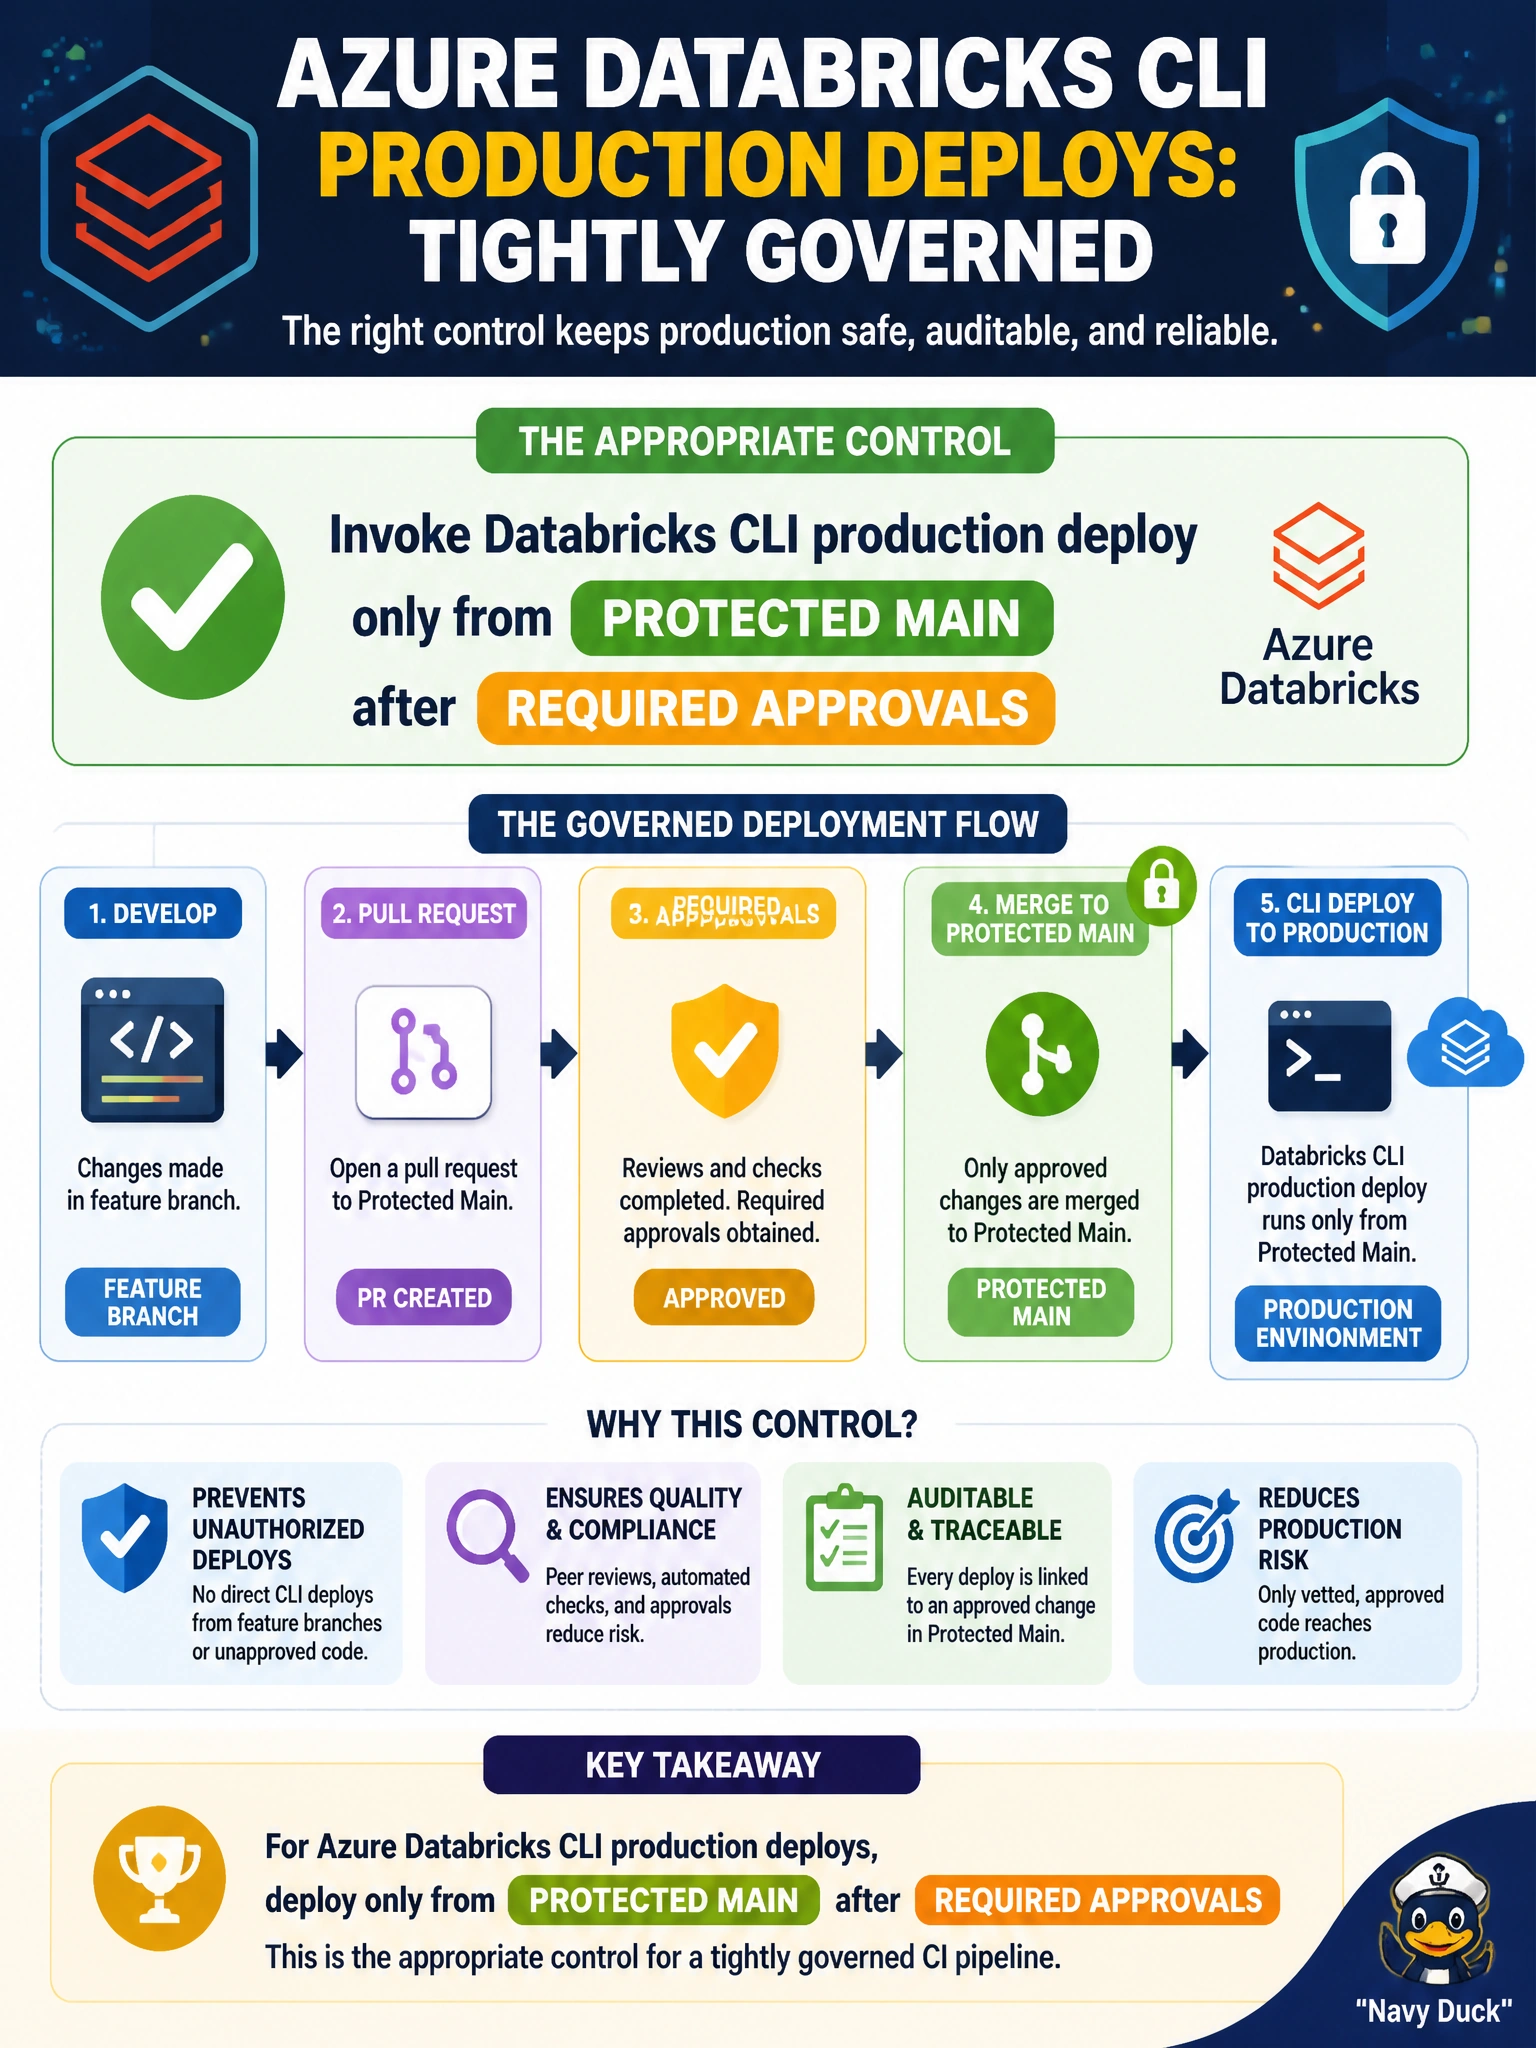
School-district CI that must keep Azure Databricks CLI production deploys tightly governed should invoke Databricks CLI production deploy only from protected main after required approvals. That control concentrates production credentials and deploy authority in a hardened path: branch protection, reviewers, and automated gates precede any CLI bundle deploy into the production workspace. Running Databricks CLI production deploy from protected main after approvals in development workspace fails because development-workspace approvals do not govern production promotion and cannot authorize release into the production workspace; production requires approvals tied to the protected production path. Authenticating Databricks CLI production deploy from protected main with a personal access token fails because a personal token is user-bound and lacks governed rotation and least-privilege automation for pipelines; production CI requires a production-scoped automated identity from the secret store. Running Databricks CLI validate and dry-run checks in development workspace before production deploy fails as a production governance control because pre-deploy validation does not enforce protected-main approvals or control production credentials; it is a useful quality check, not a production deploy gate. Exam caveat: DP-750 governance questions treat production CLI deploy as a privileged municipal operation—protected main plus approvals is the expected pattern. Operational check: verify branch protection and required reviewers on main, confirm production deploys use a production-scoped identity from the CI secret store (not a personal access token), and ensure CLI production deploys are gated by required production approvals, not approvals in development workspace.
Prefer to study offline? Printable PDF study book + test engine ($7.50, unofficial). These questions stay free here.