
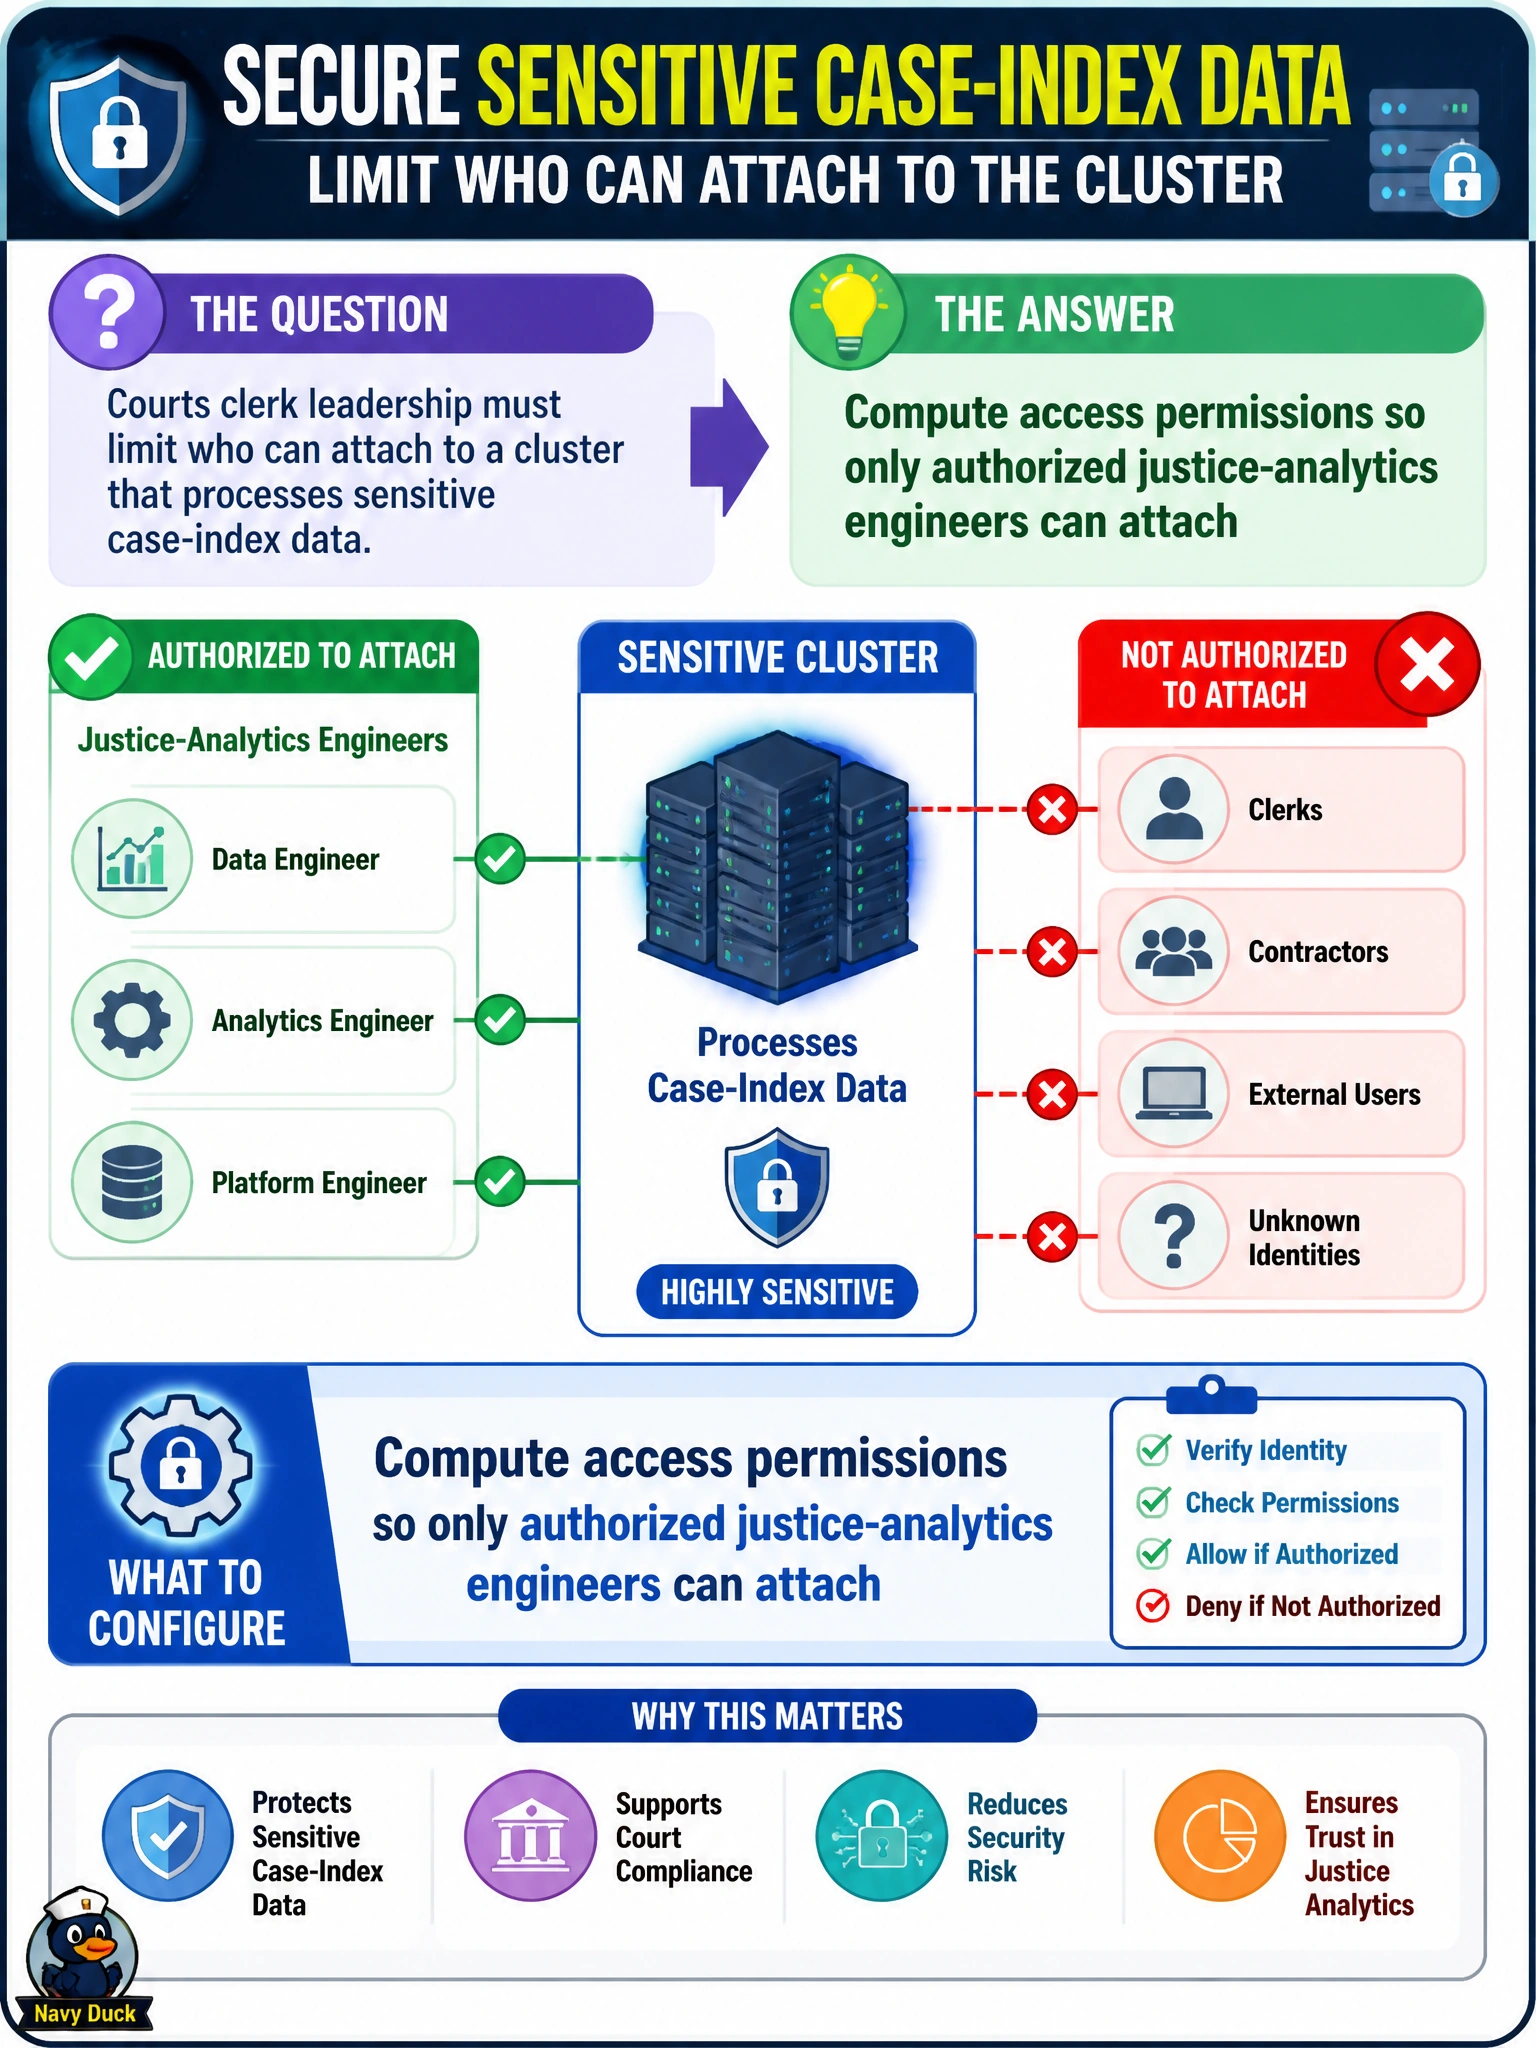
Courts clerk leadership must limit who can attach to a cluster that processes sensitive case-index data. What should they configure?
Select an answer to reveal the explanation.
Short Explanation
Cluster permissions are the locked evidence room door—only justice-analytics folks with the right badge get to attach. Granting cluster creation permissions so those engineers can attach doesn't limit who can attach to the sensitive cluster; it just lets them spin up new compute, so you still haven't locked that door. Configuring Unity Catalog grants only controls table access and private subnets only limit network reach, so neither will stop others attaching and you'll still leave that door open.
Full Explanation
Courts clerk leadership limiting who can attach to a cluster processing sensitive case-index data should configure compute access permissions so only authorized justice-analytics engineers can attach. Databricks cluster ACLs / compute permissions enforce which principals may attach, manage, or restart a cluster—essential for CJIS-minded municipal isolation of sensitive workloads beyond table grants alone. Least-privilege attach is the control the stem asks for.
Granting cluster creation permissions so authorized justice-analytics engineers can attach governs who can spin up new compute, not who may attach to this existing sensitive cluster, so it does not enforce the stem's requirement to limit attach to authorized justice-analytics engineers. Configuring Unity Catalog grants so authorized justice-analytics engineers can attach controls table and schema access to case-index data, not who may attach to this specific cluster, so it does not restrict attach to the sensitive compute boundary and still leaves the cluster open to other workspace users. Placing compute in private subnets so authorized justice-analytics engineers can attach controls network-level reachability, but it does not configure Databricks cluster/compute access permissions—anyone on the network or with workspace access could still attempt to attach unless attach permissions are explicitly restricted, which is the control the stem actually asks for.
Exam caveat: table/schema permissions and cluster attach permissions are complementary—UC can protect data while cluster ACLs still matter for who can run code on a privileged compute boundary (secrets, mounted paths, local temp). Configuring Unity Catalog grants alone is not the security improvement the stem asks for, because data grants cannot substitute for limiting cluster attach. Personal compute can help single-user isolation, but the stem specifically asks to limit attach via permissions on the sensitive cluster pattern.
Operational check: set cluster permissions to attach/manage for a justice-analytics group only, deny workspace-wide attach, verify a non-member cannot attach, and pair with Unity Catalog grants on case-index tables plus audit log review for attach events.
Prefer to study offline? Printable PDF study book + test engine ($7.50, unofficial). These questions stay free here.