
Security wants shift-left testing of a multi-agent Foundry solution for jailbreaks, tool abuse, and data exfiltration attempts before external launch. Which capability should you incorporate into the SDLC?
Select an answer to reveal the explanation.
Short Explanation
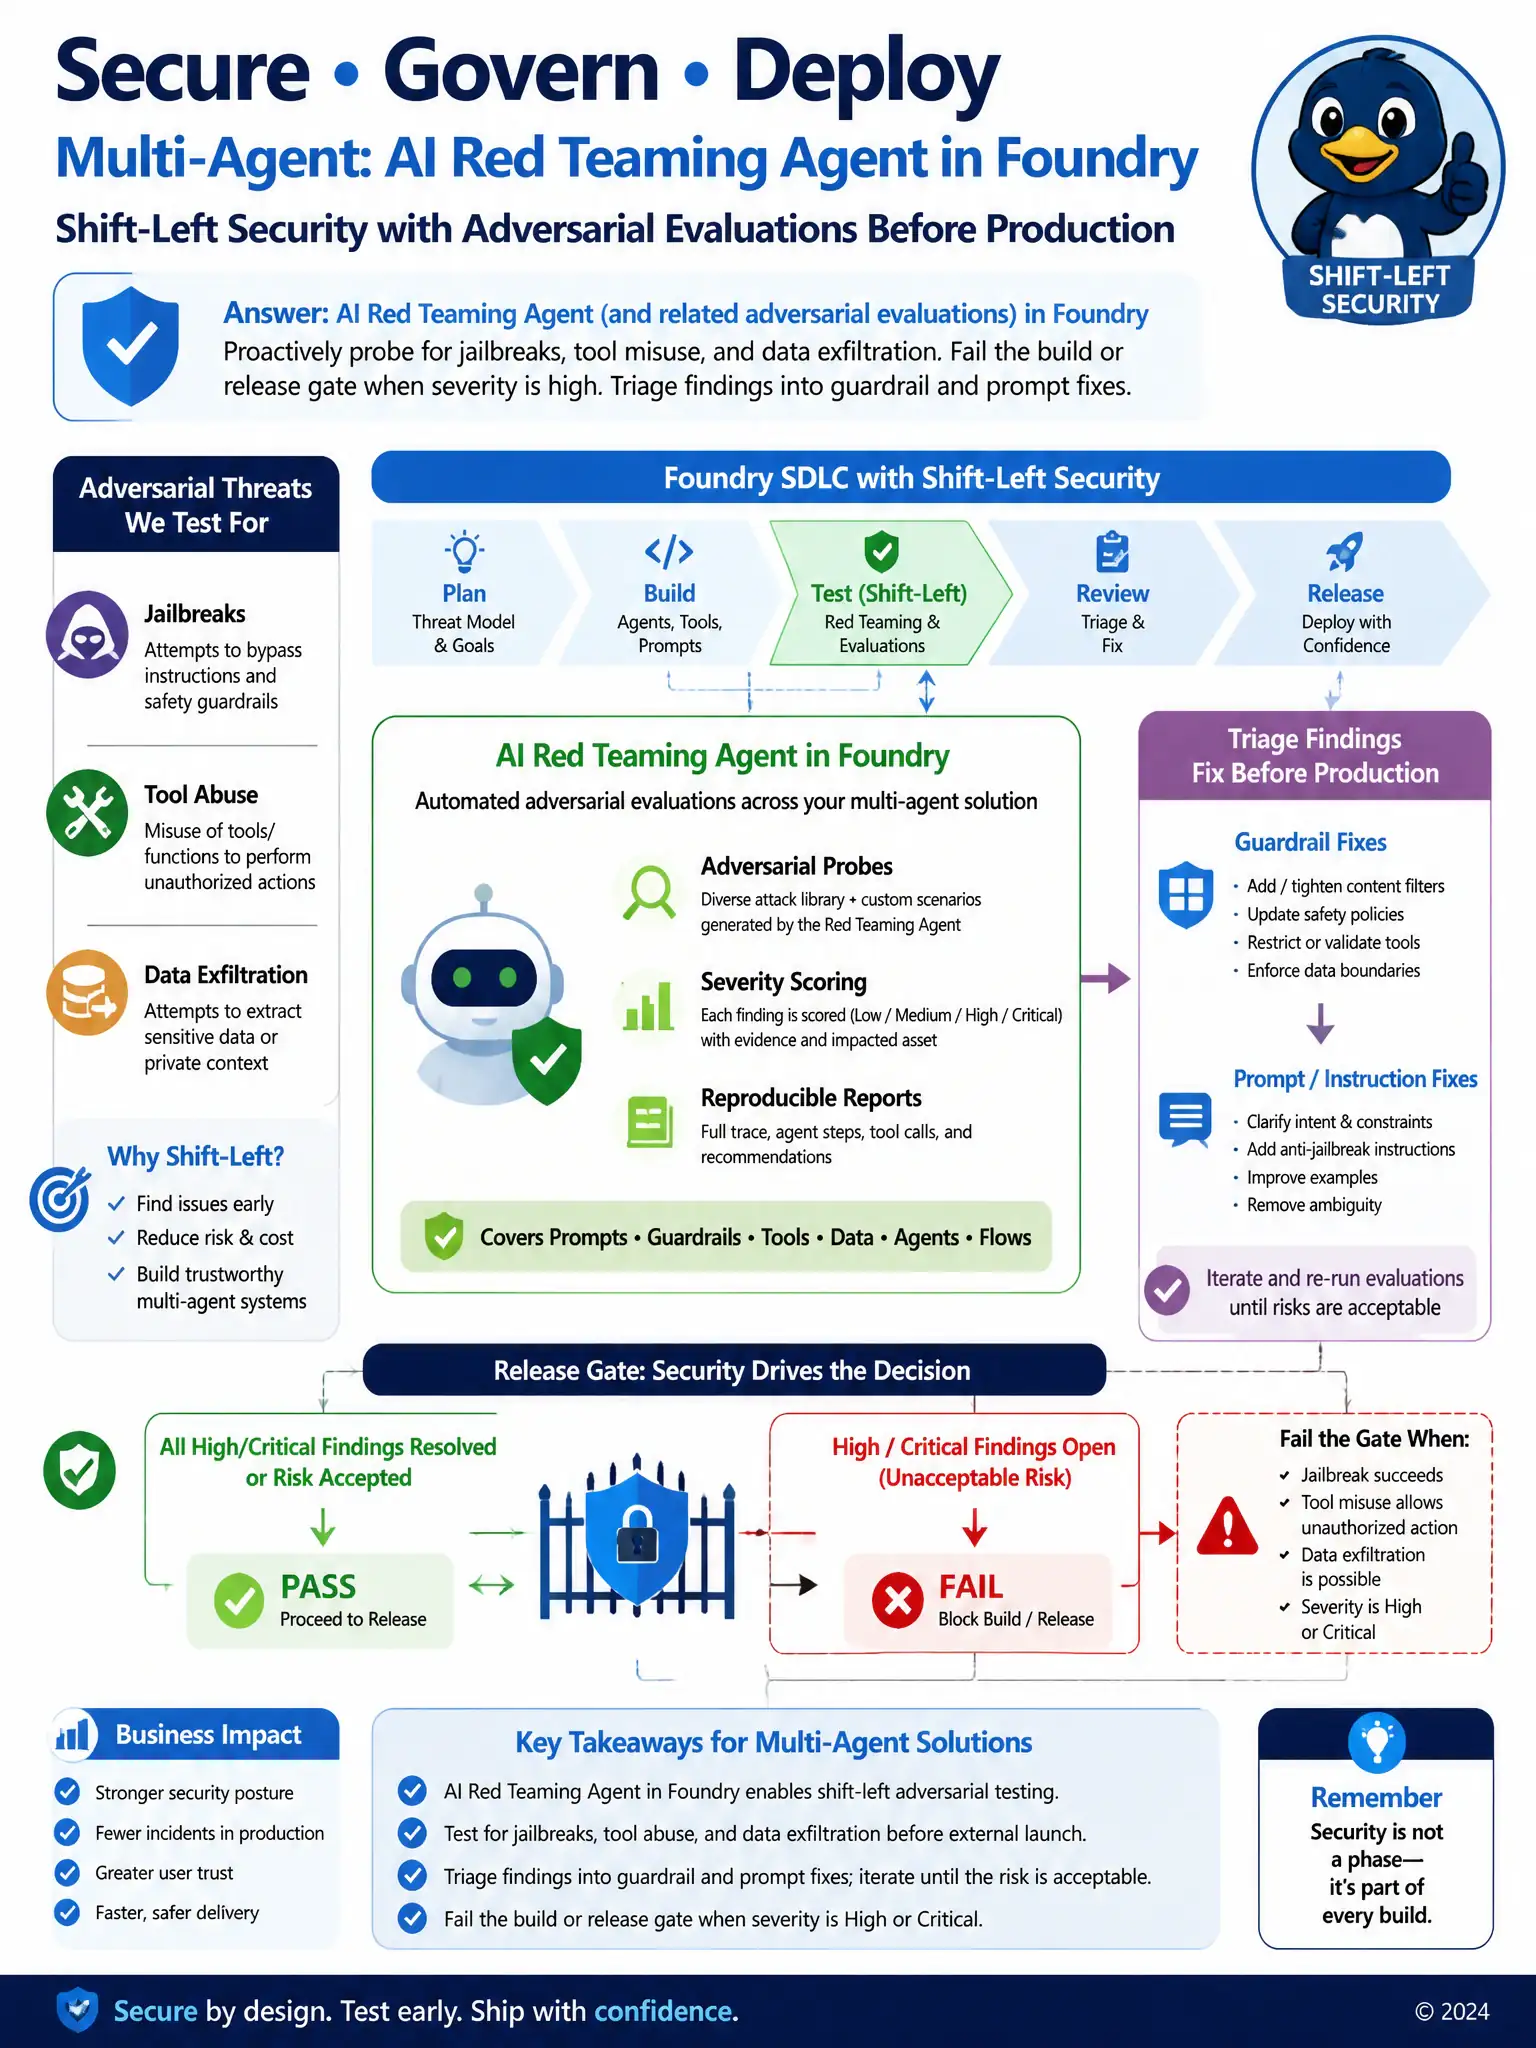
You need shift-left security, so put the AI Red Teaming Agent and related adversarial evaluations into Foundry before launch. Use jailbreak, tool-abuse, and data-exfiltration probes to fail high-severity builds or release gates. Waiting for a breach, load-only tests, or disabling safety won't meet the requirement.
Full Explanation
Use the AI Red Teaming Agent and related adversarial evaluations in Foundry as shift-left security, triaging findings into guardrail and prompt fixes before production. Integrate adversarial scenarios into CI/pre-prod, track findings, and remediate via guardrails, tool permission tightening, and prompt defensive guidelines. Feed red-team cases into the same evaluation suites used for quality regression. Skipping security testing until after a public breach is the opposite of shift-left. Load tests that ignore adversarial content do not substitute for adversarial AI security testing. Disabling all content safety increases risk and still needs validation.