
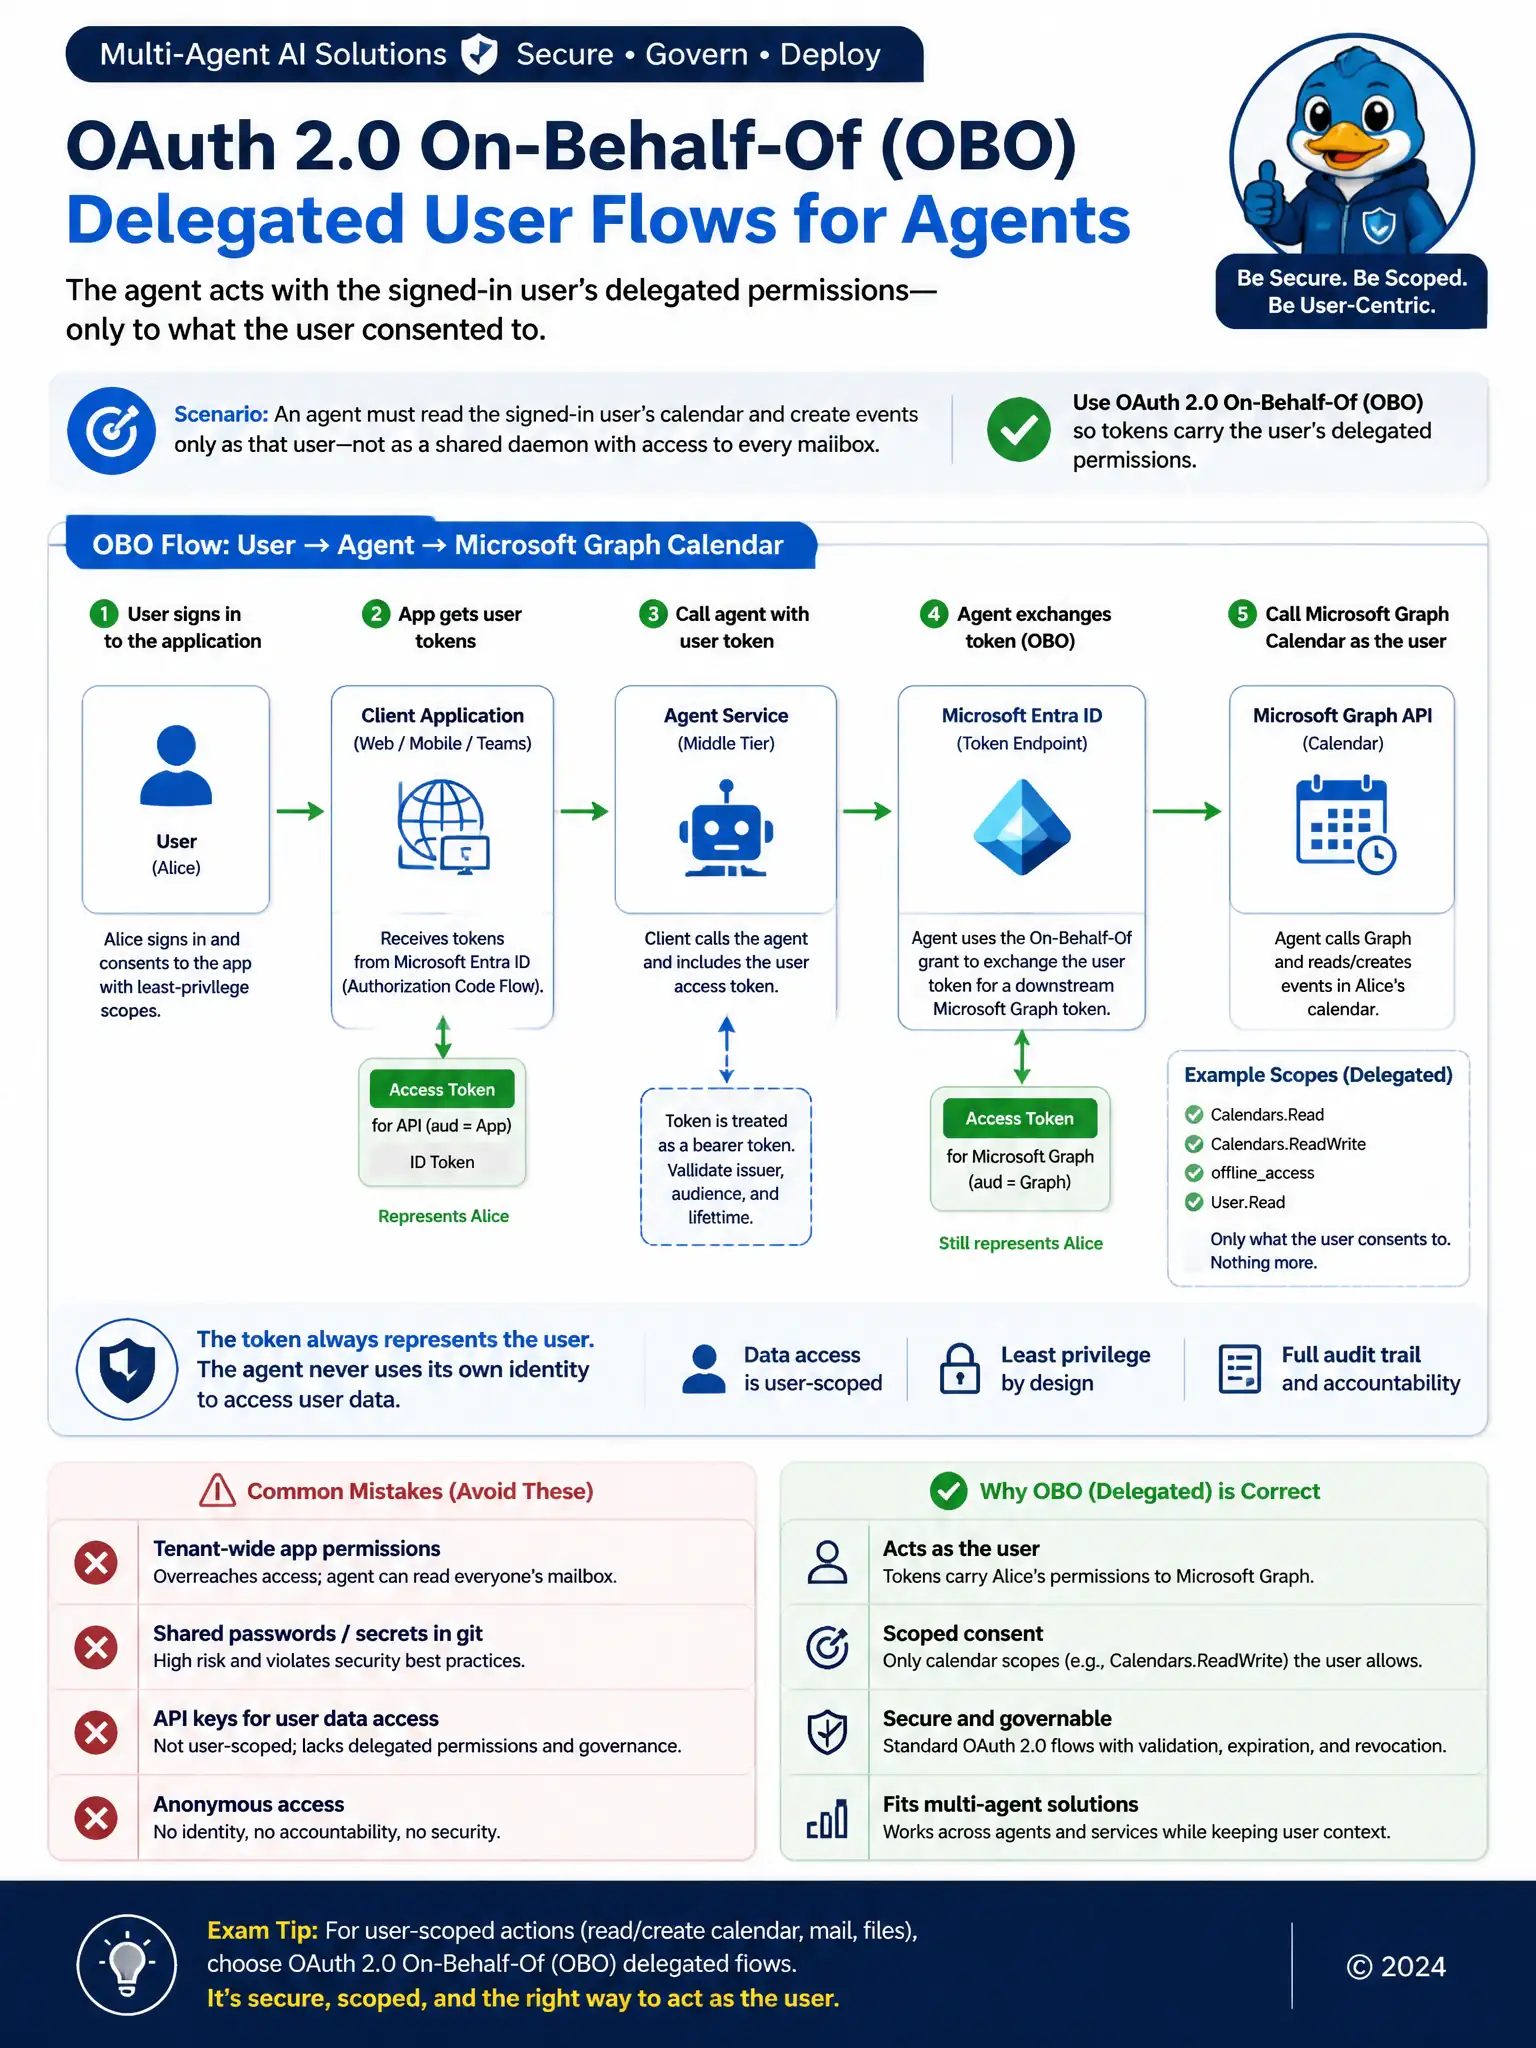
An agent must read the signed-in user’s calendar and create events only as that user—not as a shared daemon with access to every mailbox. Which authentication approach is appropriate?
Select an answer to reveal the explanation.
Short Explanation
You need OAuth 2.0 delegated on-behalf-of flows so the agent acts with the signed-in user's scoped permissions, not as a daemon. Tenant-wide app permissions, hard-coded shared passwords, and anonymous access don't meet least privilege or secret-handling basics.
Full Explanation
The appropriate approach is OAuth 2.0 delegated on-behalf-of flows with scoped consent and token handling appropriate to the multi-agent solution, so Microsoft Graph or other APIs authorize the agent as the signed-in user rather than as a shared daemon with access to every mailbox. Manage token acquisition in secure middleware, not in free-form prompts.
The tenant-wide application permission approach is incorrect for this requirement: application permissions to all mailboxes violate least privilege and the requirement that the agent act only as that user.
The hard-coded shared-mailbox username and password approach is incorrect: committing credentials to git is a critical secret-management failure.
The anonymous HTTP calendar access approach is incorrect: anonymous access is not acceptable for personal calendar data.
Document which agents use delegated versus application permissions and why.