
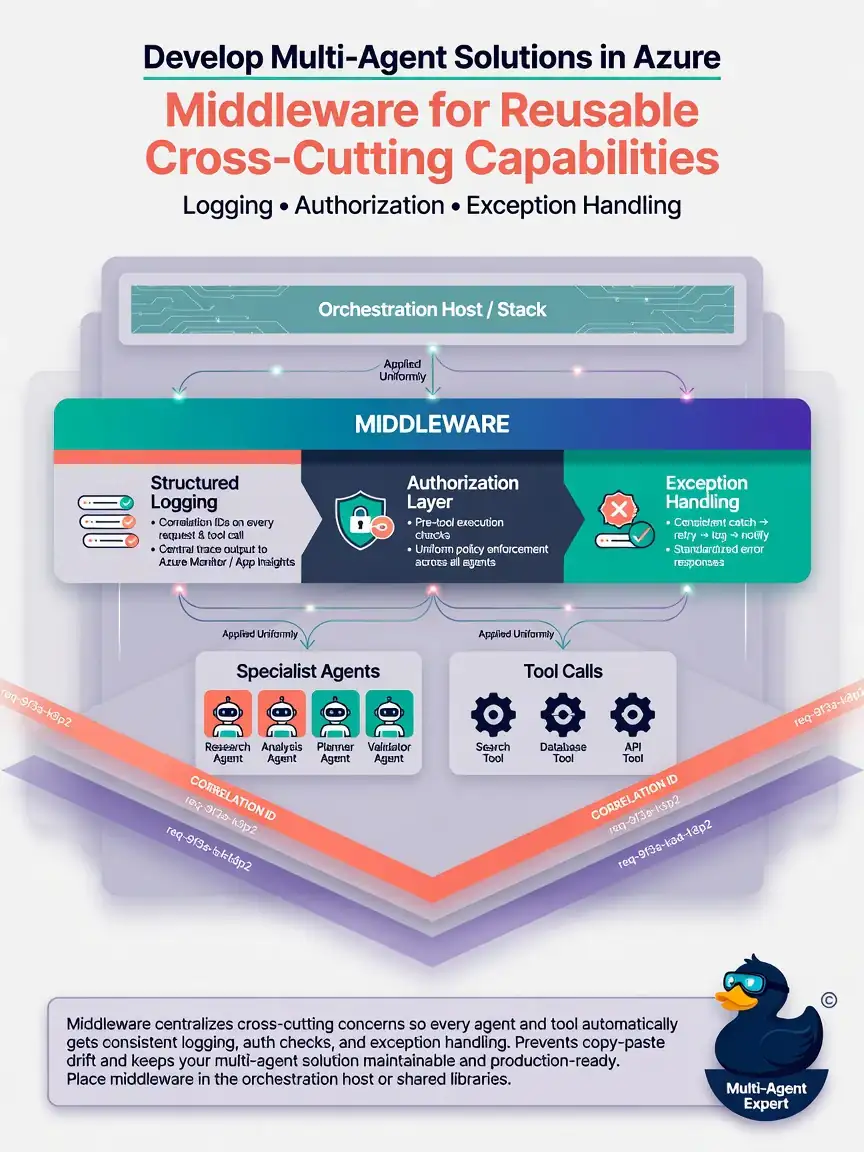
Multiple specialist agents and tools in your Azure multi-agent solution need the same cross-cutting behaviors: structured logging with correlation IDs, authorization checks before tool execution, and consistent exception handling. Duplicating this logic in every agent is causing drift. What should you implement?
Select an answer to reveal the explanation.
Short Explanation
You need middleware that centralizes logging, authorization, and exception handling so every agent and tool call follows the same rules. That keeps your multi-agent solution consistent, secure, and easier to maintain.
Full Explanation
AI-500 development skills include designing middleware for reusable capabilities across the solution, including logging, authorization, and exception handling. In multi-agent systems, every tool invocation is a security and observability event; middleware can enforce allowlists, inject correlation IDs, redact secrets, translate exceptions into control-flow decisions, and emit metrics. The copy-paste approach with skipped authorization guarantees inconsistent security. Disabling production logging blinds operations. Restarting the entire Kubernetes cluster is indiscriminate and slow. Implement middleware once, unit-test it, and ensure new agents inherit the same pipeline when registered.