
A regulated enterprise deploys multi-agent workloads that call Azure OpenAI-compatible model endpoints, Azure AI Search, and internal APIs. Policy forbids public ingress to data-plane services where private connectivity is available. Agents run on Azure Container Apps. Which network design best aligns with resource access and network boundary controls?
Select an answer to reveal the explanation.
Short Explanation
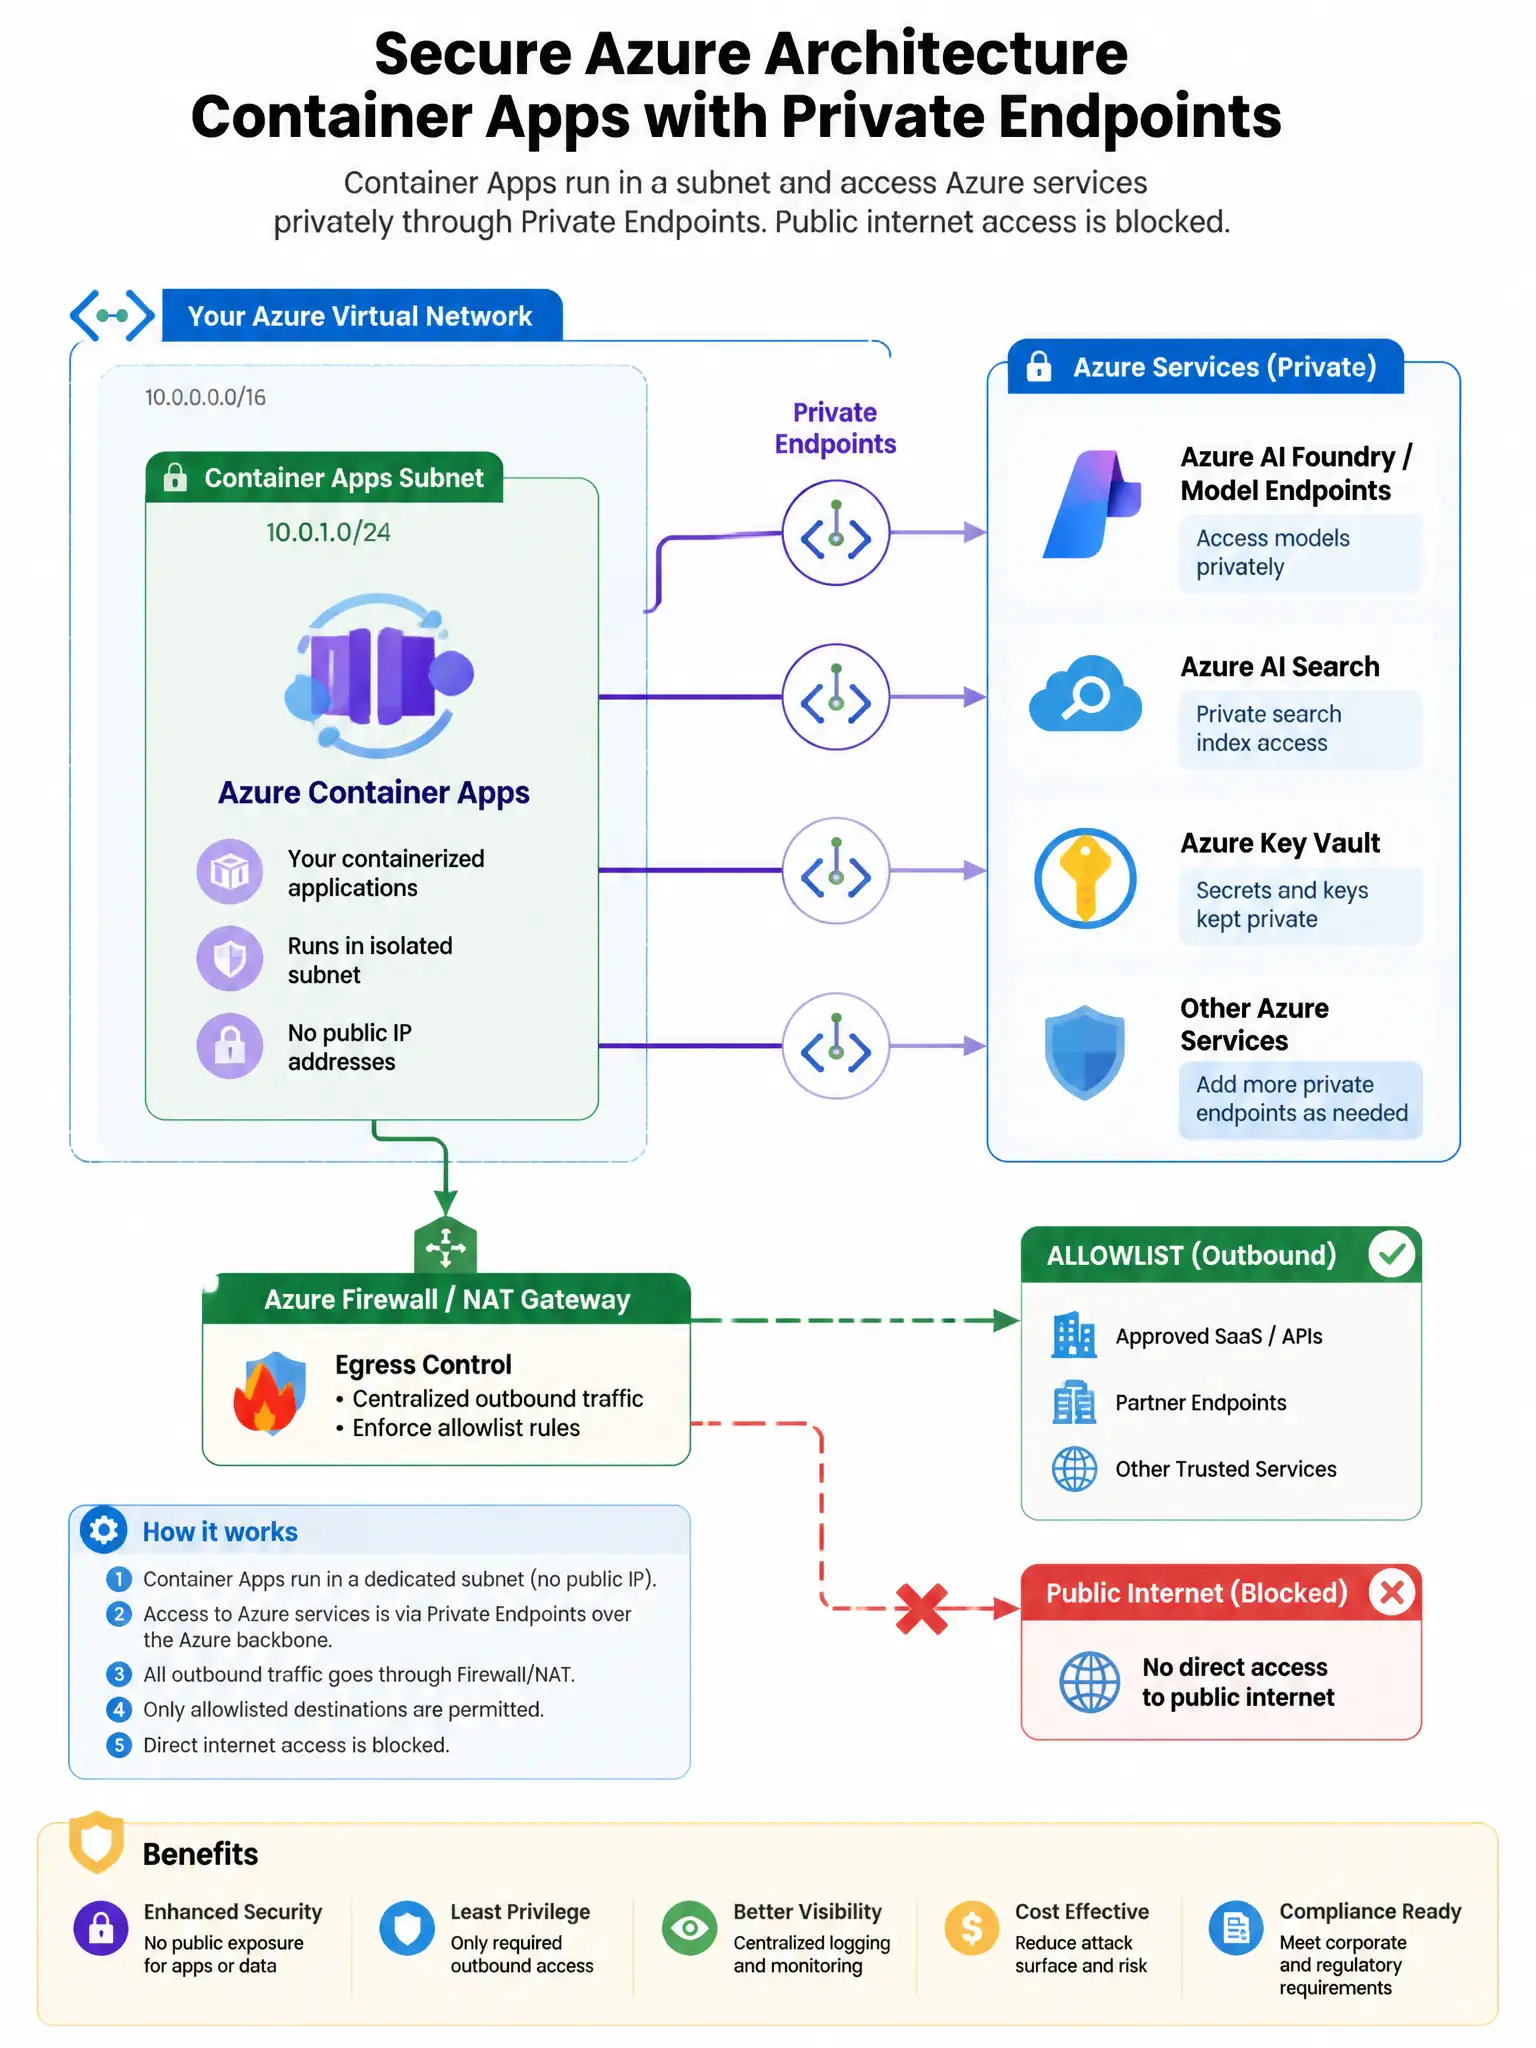
You want agent compute inside VNet-integrated environments, private endpoints for Azure AI and data services, and egress locked down to approved destinations. That keeps identity and network boundaries together, so agents can't phone home to arbitrary hosts. Public-only keys, disabled TLS, and open outbound access all weaken defense in depth.
Full Explanation
The correct design places agent compute in VNet-integrated environments, uses private endpoints for Azure AI and data services, and restricts egress so tools only reach approved destinations. AI-500 security objectives include network boundaries alongside identity-based access and RBAC. Multi-agent systems are especially sensitive to egress abuse because tool-calling models may attempt unexpected URLs. Integrating Container Apps, or AKS/App Service, with virtual networks, using private endpoints for PaaS models, search, storage, and Key Vault, and applying NSGs/firewall policies reduces exposure. The public-internet design that relies on API keys alone lacks defense-in-depth. The TLS-disabled design violates encryption expectations. The unrestricted-outbound design matches common agent incident patterns, enabling SSRF or exfiltration through tool calls. Combine private networking with RBAC and guardrails on tool URLs. Also scope DNS, use allowlisted MCP/tool hosts, and monitor denied connection attempts as security signals. Network design should map to compliance control frameworks for regulated deployments.