
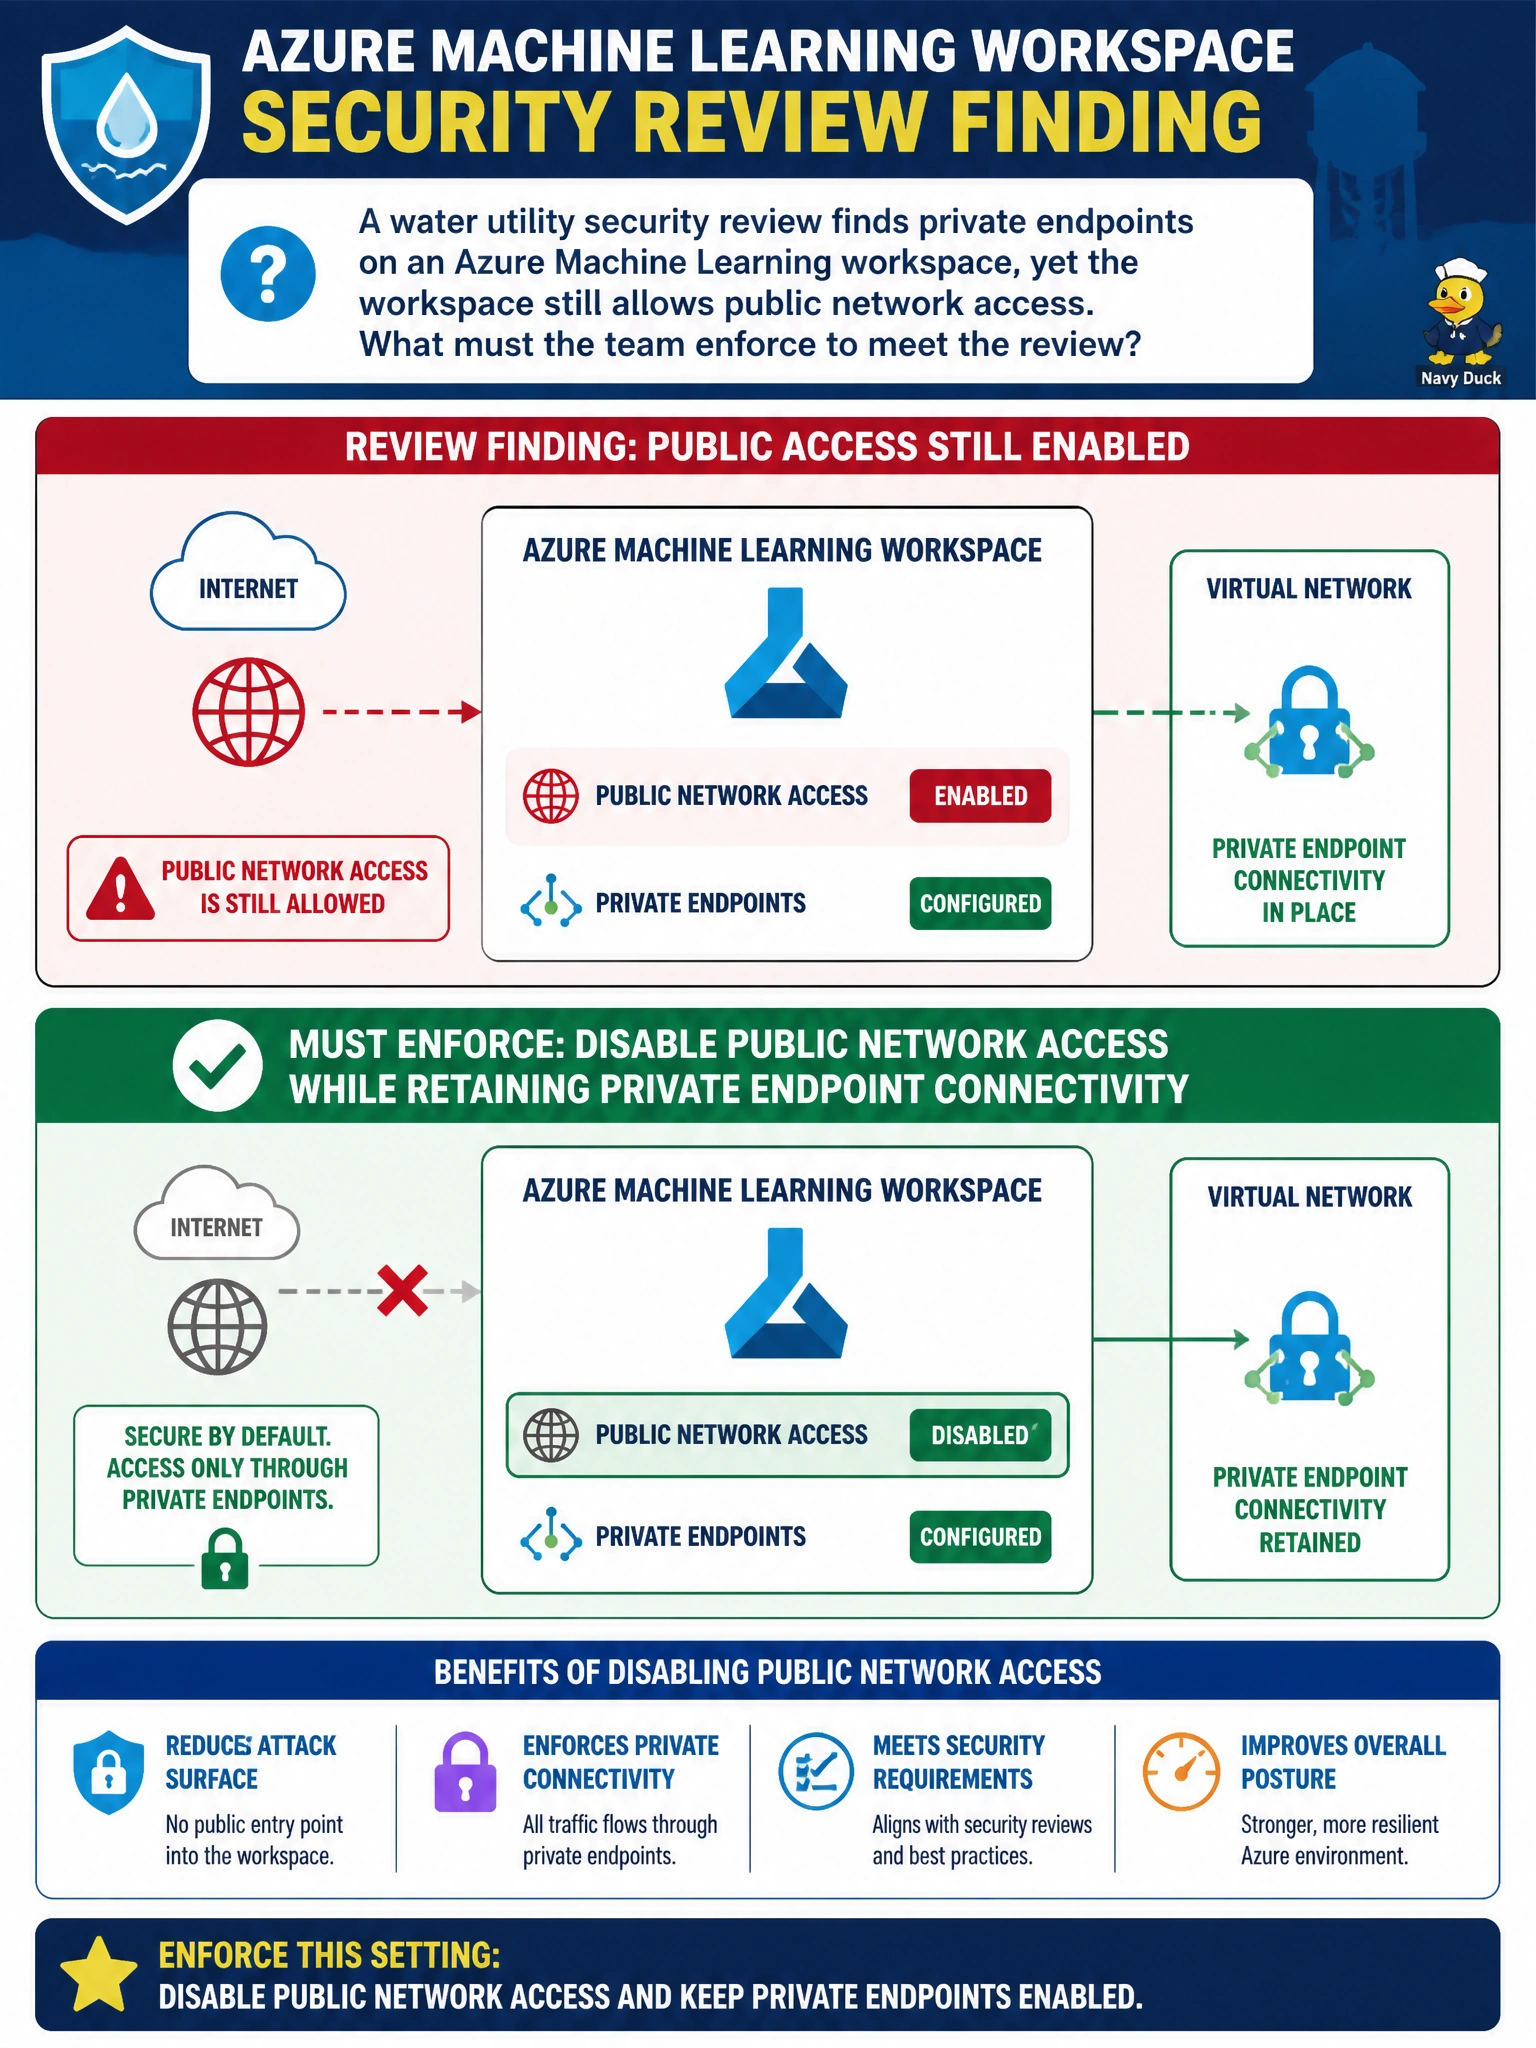
A water utility security review finds private endpoints on an Azure Machine Learning workspace, yet the workspace still allows public network access. What must the team enforce to meet the review?
Select an answer to reveal the explanation.
Short Explanation
Private endpoints plus open public access is a locked side door with the front door wide open. Turn public network access off so civic traffic must use the private path. Reviewers look for both controls together.
Full Explanation
Disabling public network access on the Azure Machine Learning workspace while retaining private endpoint connectivity closes the bypass the water utility review found. Private endpoints alone are insufficient if the workspace still accepts public traffic: attackers or misconfigured clients can reach the public surface even though a private path exists. Enforcing publicNetworkAccess Disabled (and approved private endpoint connections with private DNS) makes the municipal network path mandatory.
Disable public network access on the linked storage account while preserving workspace connectivity fails by scope—it hardens the storage dependency but leaves the workspace's own public endpoint open, so the bypass the reviewers flagged remains available and does not make the private path mandatory. Enable managed virtual network isolation for training environments with outbound control fails the review's actual finding: managed virtual network isolation controls training egress but does not close the workspace's public-facing endpoint, so the bypass the reviewers flagged remains open. Enforce private endpoint connectivity on the container registry for workspace image builds fails the review's actual finding: securing the registry for image builds does not remove the workspace's public network path, so the bypass the reviewers flagged remains open.
Exam caveat: AI-300-style networking items often test that private endpoints plus disabled public access are both required; distractors either disable public access on linked storage, enable managed virtual network isolation for training environments, or enforce private endpoints on the container registry without disabling workspace public access.
Operational check: set public network access to Disabled, verify private endpoint connection state is Approved, resolve workspace FQDNs via private DNS from a utility VNet jump host, and confirm internet clients without VPN receive connection failure.
Prefer to study offline? Printable PDF study book + test engine ($7.50, unofficial). These questions stay free here.