
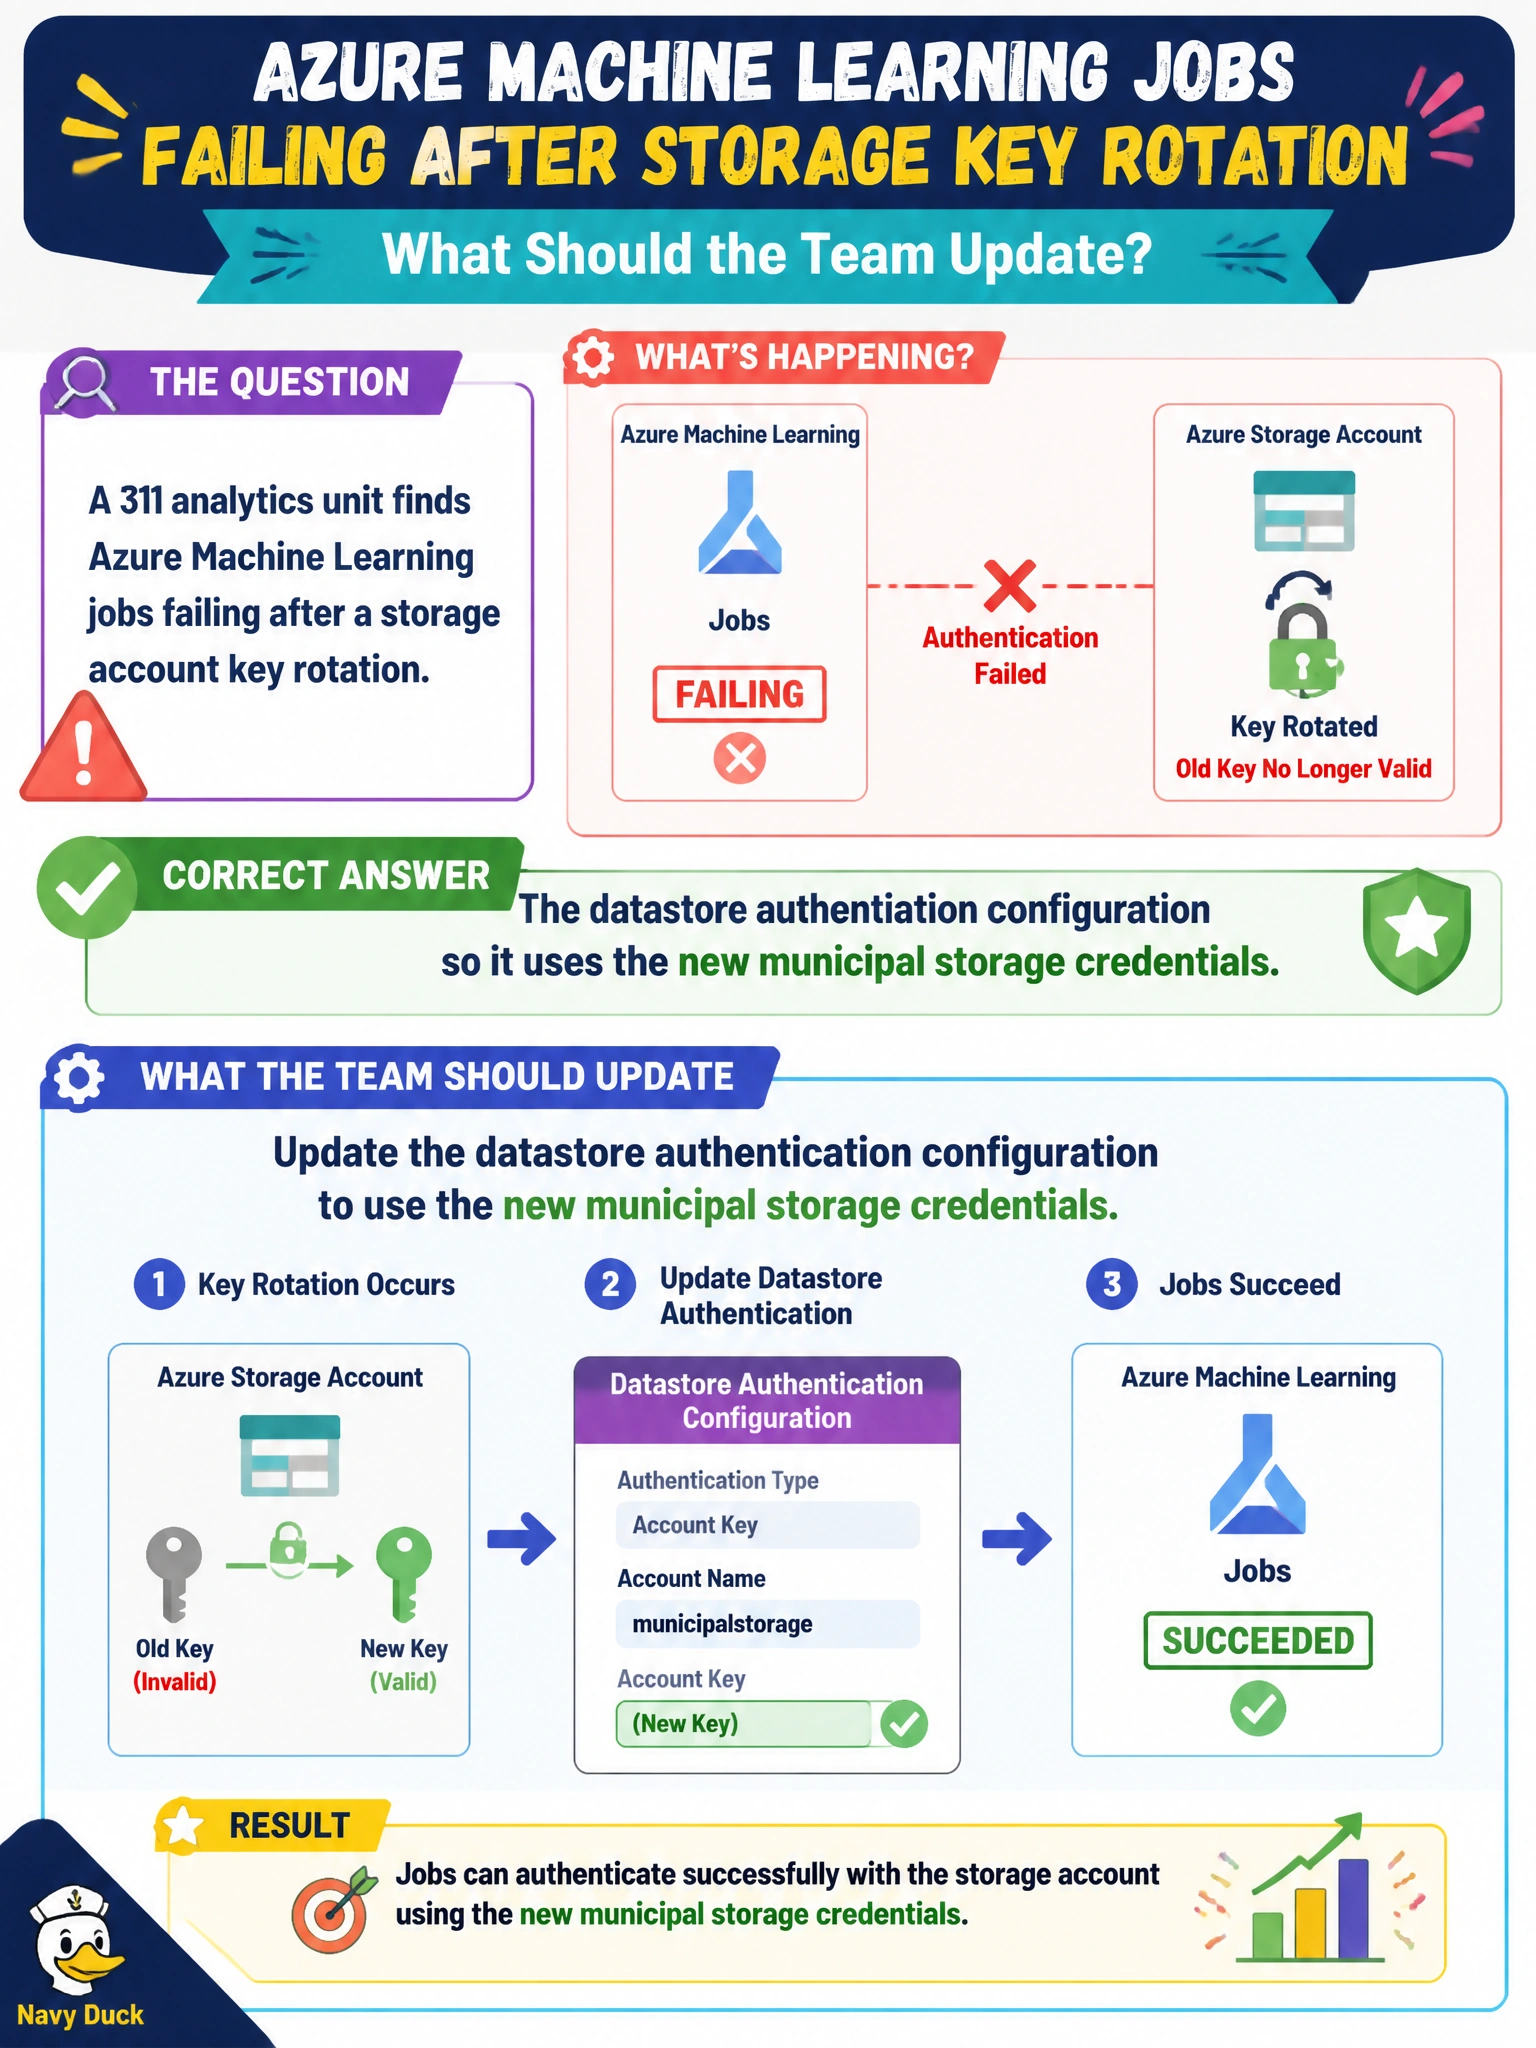
A 311 analytics unit finds Azure Machine Learning jobs failing after a storage account key rotation. What should the team update?
Select an answer to reveal the explanation.
Short Explanation
When the storage lock changes, the datastore key ring has to change too. Update Azure ML datastore authentication to the new storage credentials after rotation. You won't unblock the 311 training jobs by changing the compute cluster identity configuration, the training environment variable definition, or the dataset registration credential property, because none of those update the datastore credentials the jobs need.
Full Explanation
Updating the datastore authentication configuration so it uses the new municipal storage credentials is correct because Azure ML jobs authenticate to storage through the datastore's configured secret, key, SAS, or identity binding. After a storage account key rotation, jobs fail until that binding reflects the new credentials (or until identity-based access is confirmed still valid). The 311 analytics unit must treat datastore auth as part of the rotation runbook—not as an unrelated portal setting.
Updating only the compute cluster identity configuration so it uses the new municipal storage credentials leaves the datastore authentication unchanged, so jobs that access storage through the datastore still cannot authenticate to storage. Setting the training environment variable definition so it uses the new municipal storage credentials puts the new secret in the job environment and will not restore the datastore's broken storage-key binding. Updating the dataset registration credential property so it uses the new municipal storage credentials is likewise orthogonal: the dataset still resolves storage through the underlying datastore, so that change does not refresh the storage credential Azure ML uses to read from the 311 unit's storage account.
Exam caveat: key rotation breaks clients that still hold the old key. Prefer managed identity for datastores where possible to reduce key-rotation blast radius; when keys are used, update every dependent datastore configuration as part of the same change window.
Operational check: after rotation, update datastore auth, re-test a job that reads a known path, confirm failures clear, and document which municipal storage accounts and Azure ML datastores are coupled for future rotations.
Prefer to study offline? Printable PDF study book + test engine ($7.50, unofficial). These questions stay free here.