
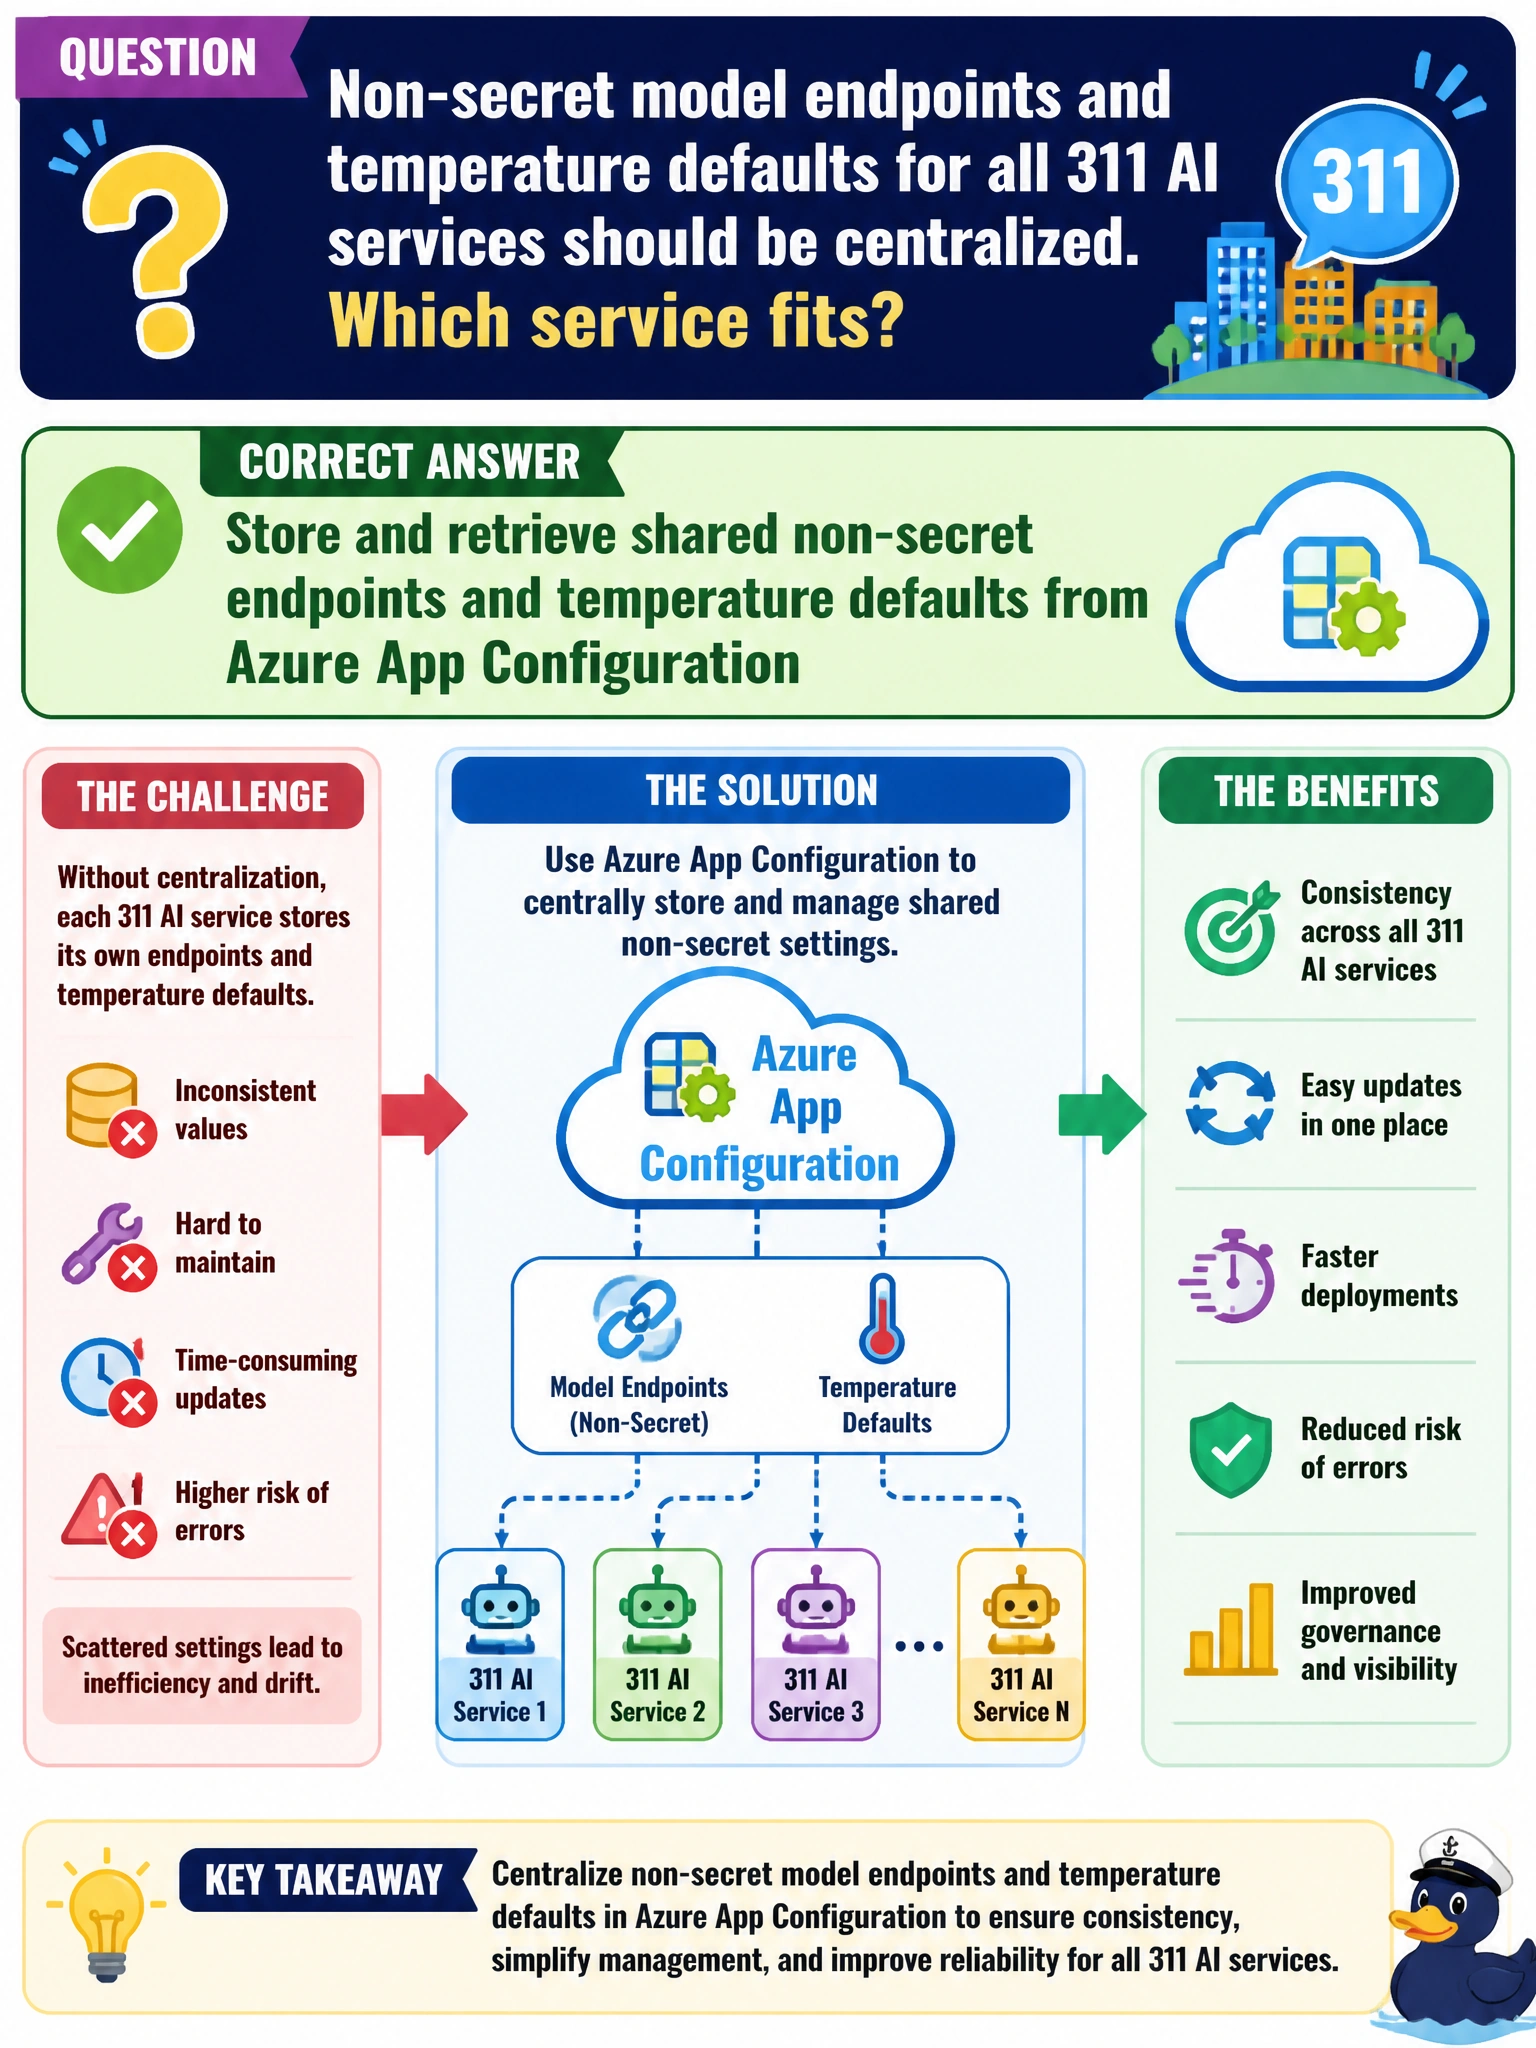
Non-secret model endpoints and temperature defaults for all 311 AI services should be centralized. Which service fits?
Select an answer to reveal the explanation.
Short Explanation
App Configuration is the shared city policy binder—endpoints and temperature defaults live once, and every 311 service checks the same page.
Full Explanation
Non-secret model endpoints and temperature defaults shared by all 311 AI services belong in Azure App Configuration. App Configuration is built for centralized, hierarchical, label-scoped application settings that many services retrieve consistently. Endpoints, temperature defaults, max-token caps, and similar non-secret generative parameters can be updated once and consumed citywide, with optional dynamic refresh so workers adopt changes without redeploy. That separation keeps Key Vault focused on credentials while App Configuration remains the shared policy binder for 311 AI runtime behavior.
Storing non-secret endpoints only as Key Vault secrets mixed with passwords fails separation of concerns: Key Vault is for secrets, adds unnecessary secret-operation cost and permission complexity, and makes routine endpoint edits look like credential changes. Duplicating different endpoint strings in each service’s source code with no shared store fails consistency—one team updates a model hostname and others keep calling the retired endpoint during peak 311 hours. Publishing endpoints solely as handwritten whiteboard notes in the network operations center fails durability and automation: whiteboards are not versioned configuration APIs and cannot drive Functions or Container Apps at scale.
Exam caveat: if a value is sensitive (API keys, connection strings), it must not be treated as ‘just another App Configuration setting’ in plaintext—use Key Vault, optionally referenced from App Config. Conversely, stuffing every non-secret into Key Vault is a distractor that appears on exams. Labels and keys must be designed so staging and production 311 fleets do not overwrite each other.
Operational check: place endpoint and temperature keys in App Configuration, point multiple 311 services at the store, change a temperature default once, confirm each service observes the same value (after refresh), and verify Key Vault is not being used as a generic config dumping ground for those non-secrets.