
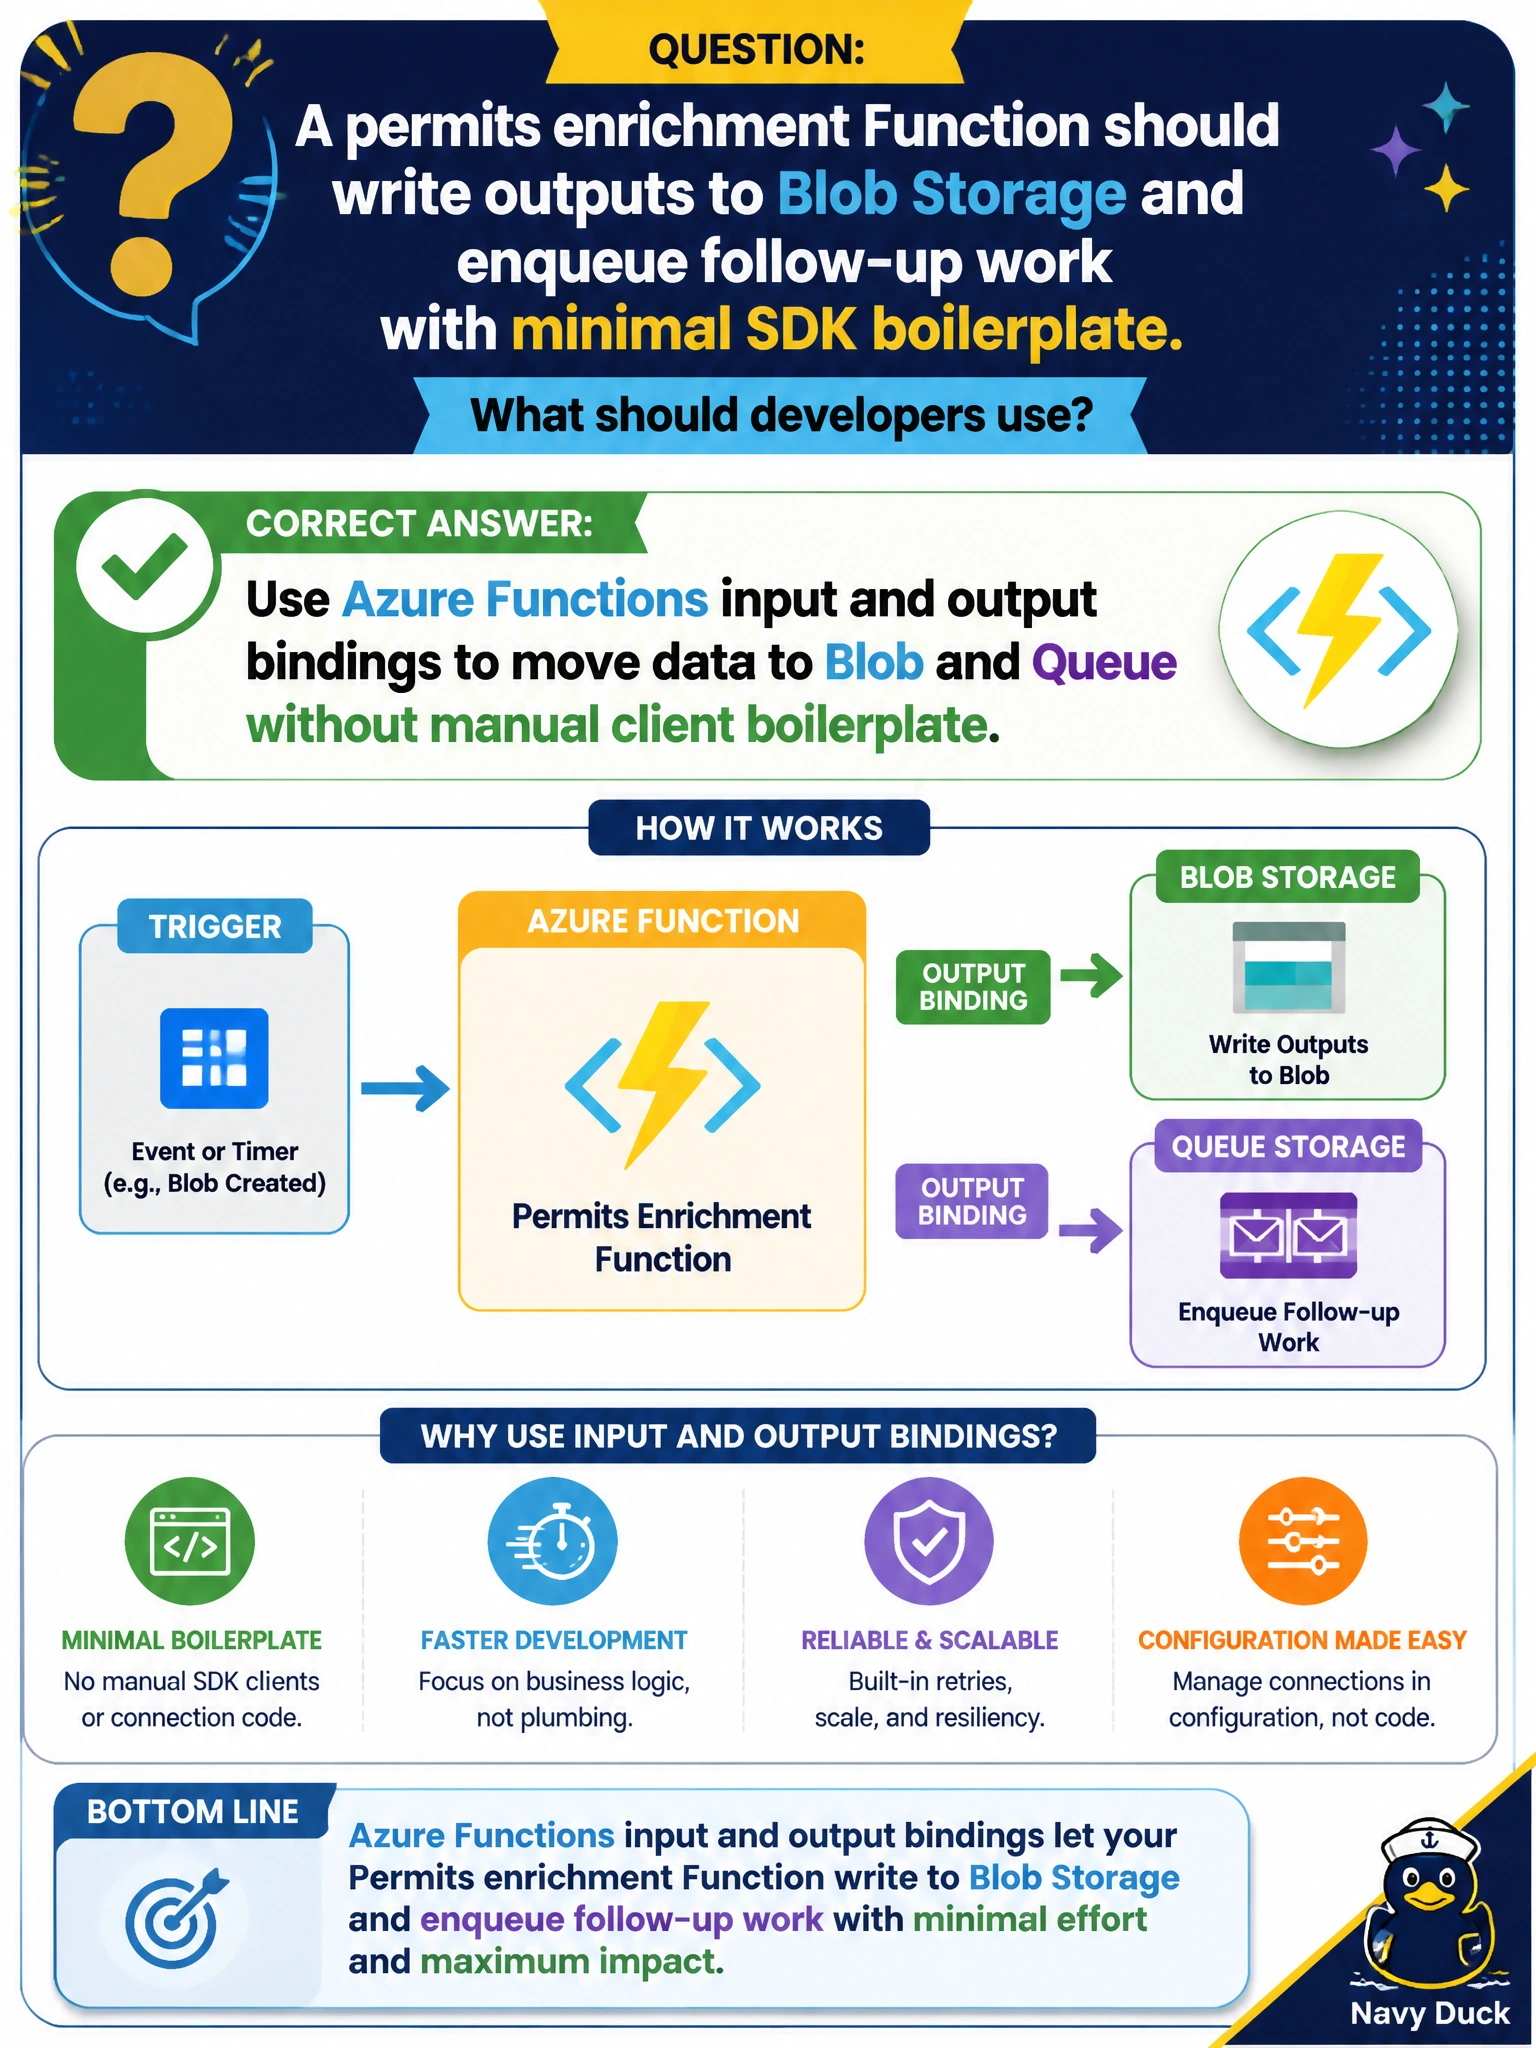
A permits enrichment Function should write outputs to Blob Storage and enqueue follow-up work with minimal SDK boilerplate. What should developers use?
Select an answer to reveal the explanation.
Short Explanation
Think of bindings as pre-labeled outboxes on the permits desk: point your Function at Blob Storage and Queue, and the runtime handles the handoff. Bindings spare you from rebuilding the postage meter for routine output work.
Full Explanation
Permits enrichment Functions that need to write outputs to Blob Storage and enqueue follow-up work can use Azure Functions input and output bindings. Bindings declaratively map blob paths and queue messages, so you avoid hand-writing Storage and Queue SDK clients for routine I/O. The runtime moves bytes and messages using configured connections, reducing duplicated boilerplate across municipal Function apps and keeping enrichment code focused on AI logic. Hand-coding Blob and Queue clients in every Function duplicates connection setup and request handling, increasing drift, secret-handling mistakes, and review surface rather than avoiding boilerplate. Avoiding bindings and shelling out to az CLI inside every invocation adds a CLI dependency, process-spawn cost, and brittle parsing to the execution path. Storing outputs only in Function log text provides no durable Blob or Queue write; logs are not a system of record for downstream civic AI steps. Exam caveat: bindings are ideal for straightforward I/O, while complex multi-step transactions may still use SDKs deliberately; prefer connection names and managed identity–compatible bindings over raw secrets when possible. Practical check: run an enrichment with bindings configured, confirm the output blob exists at the bound path and a follow-up queue message is enqueued, and ensure no az CLI process appears in the execution path.