
A public 311 chat API on AKS must be exposed with TLS termination at the ingress controller. What should the municipal team implement?
Select an answer to reveal the explanation.
Short Explanation
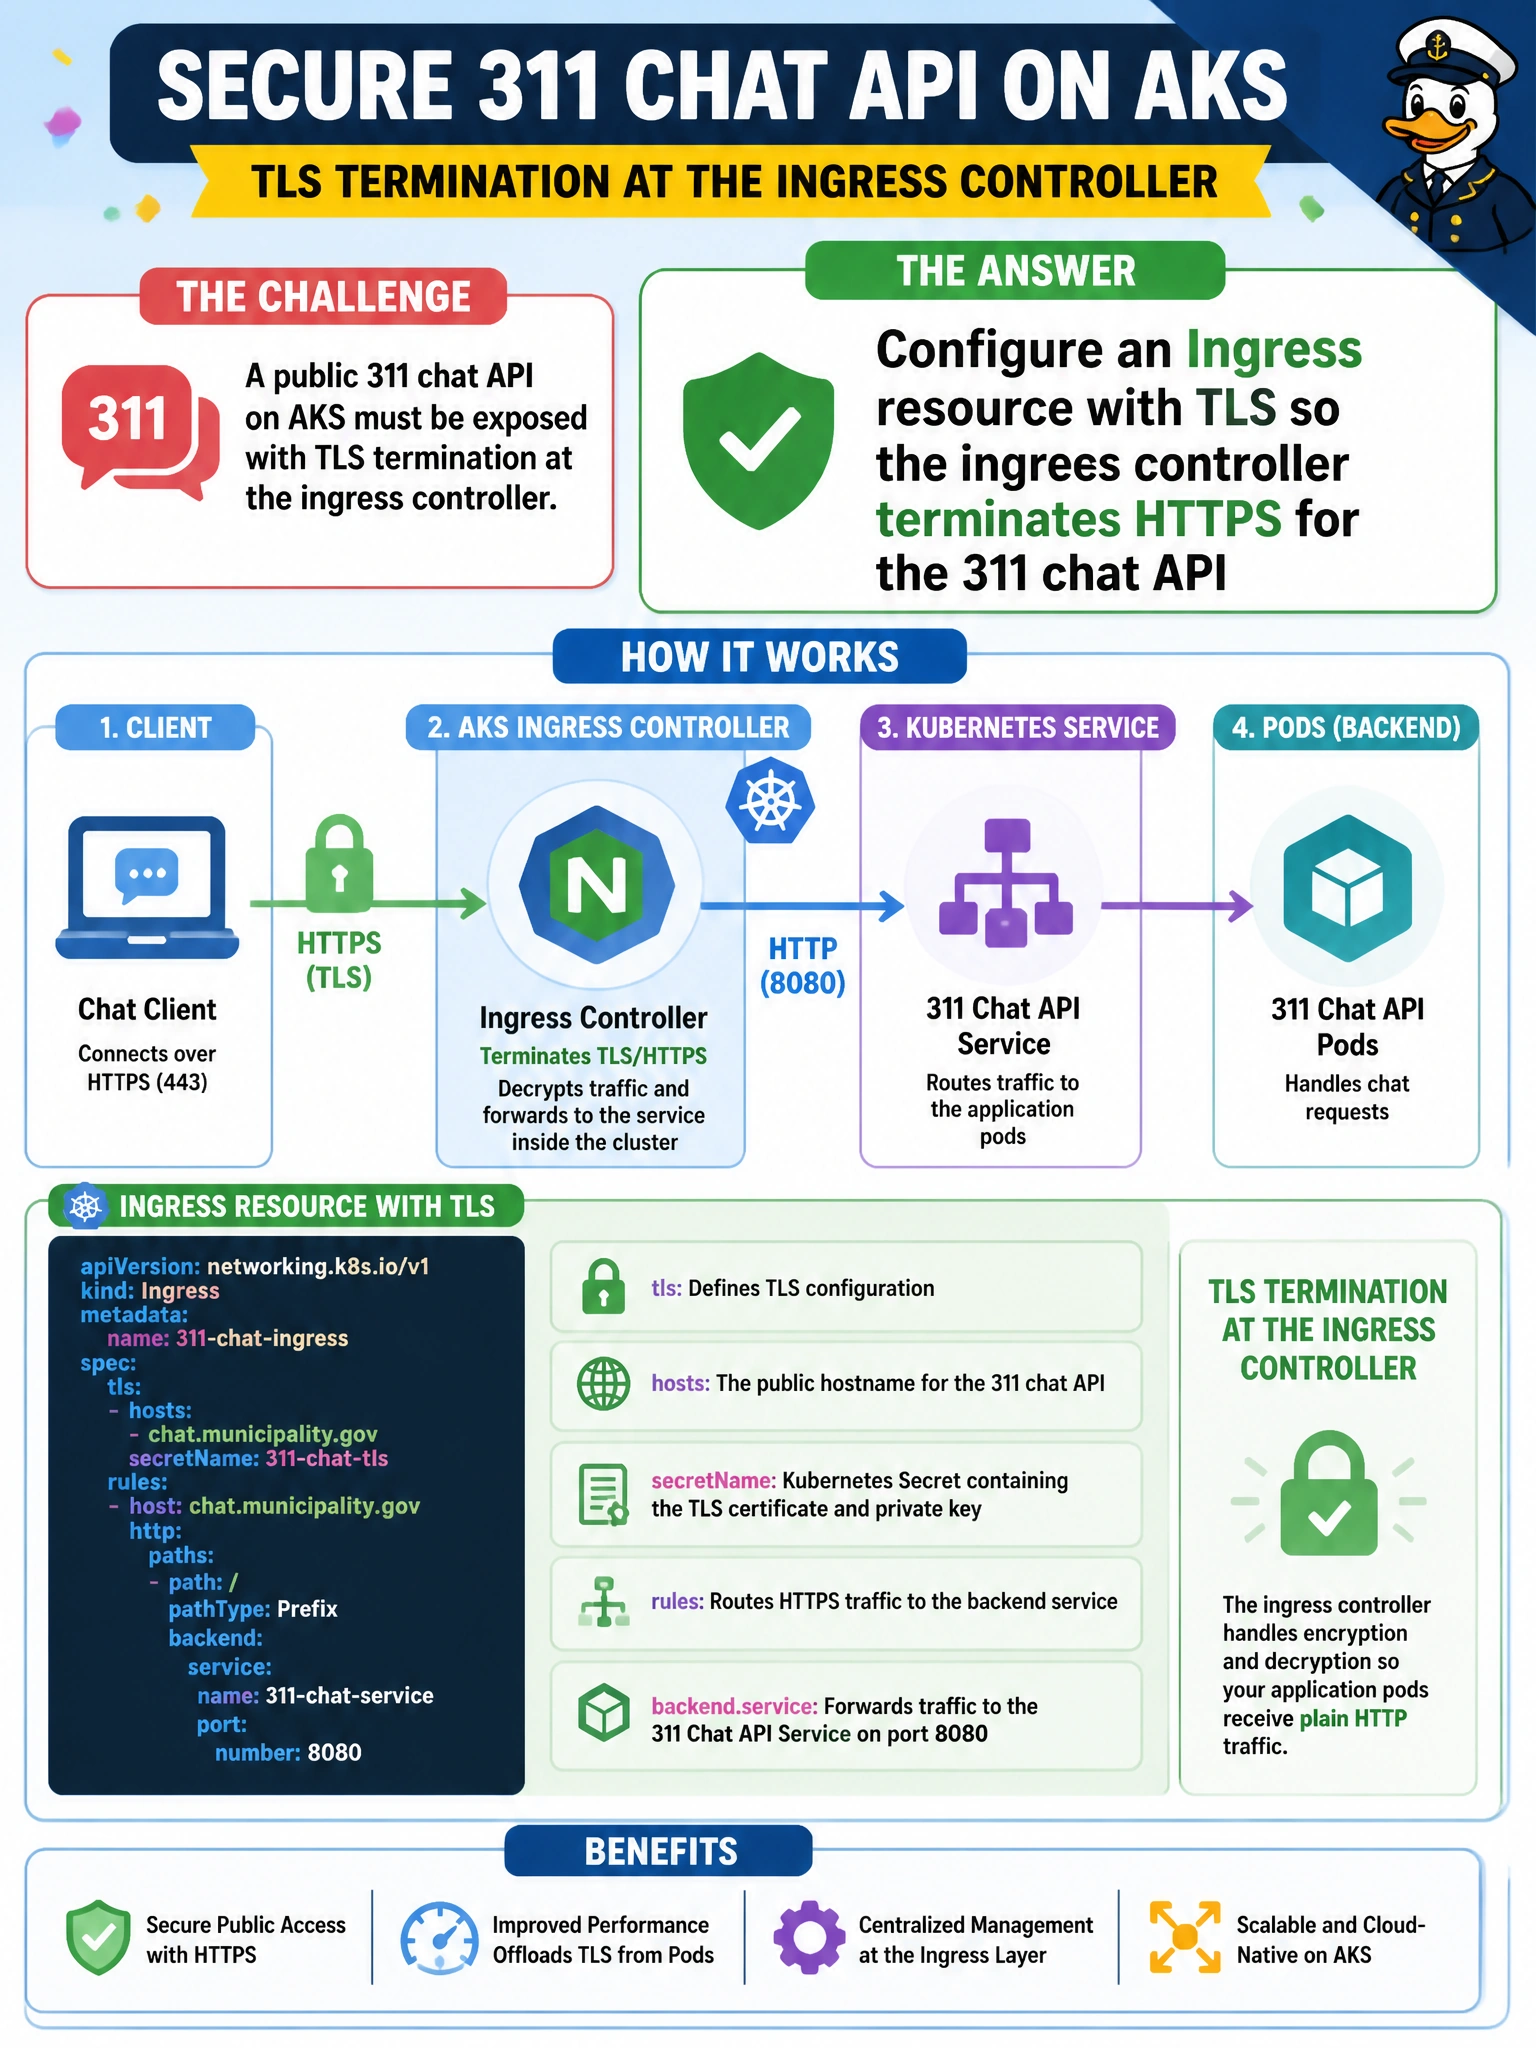
Ingress with TLS is the city's front door with a proper lock—HTTPS ends at the ingress controller for the 311 chat API, not raw pod IPs or a shrug that says 'just use a VPN.'
Full Explanation
An Ingress resource with TLS on AKS lets the ingress controller terminate HTTPS for a public 311 chat API: certificates are attached to the Ingress, the controller presents TLS to residents, and HTTP is routed to backend Services and pods on the cluster network. That centralizes certificate management, host-based routing, and encryption at the edge of the cluster rather than inventing per-pod Internet exposure. For municipal public APIs, TLS at ingress is the expected pattern for confidentiality and integrity in transit.
Exposing each pod IP directly with self-signed certificates fails by concept because pod IPs are ephemeral, not a stable public entry, and ad-hoc node-taped certs do not provide managed ingress routing or trustworthy PKI. Serving only unencrypted HTTP on a NodePort while trusting the city firewall fails because traffic can still be intercepted on paths the firewall does not encrypt, and NodePort is a poor substitute for Ingress TLS termination. Disabling TLS and requiring a VPN for every chat session fails for a public 311 API: residents should reach the service over HTTPS without a municipal VPN client, and VPN does not replace Ingress TLS design for a public endpoint.
Exam caveat: TLS termination at ingress means the controller decrypts at the edge; backends may speak HTTP inside the cluster unless you also configure backend TLS or mesh mTLS. Certificate sources (Kubernetes secrets, cert-manager, Key Vault integration) vary, but the exam focus is Ingress + TLS versus raw pod or plaintext NodePort exposure.
Operational check: Deploy the 311 chat Service, create an Ingress with TLS secret and host rules, verify HTTPS succeeds with a trusted cert, confirm HTTP redirects or rejections match policy, and ensure pod IPs are not published on the Internet. Monitor ingress controller logs for TLS handshake and backend errors during civic peak hours.